
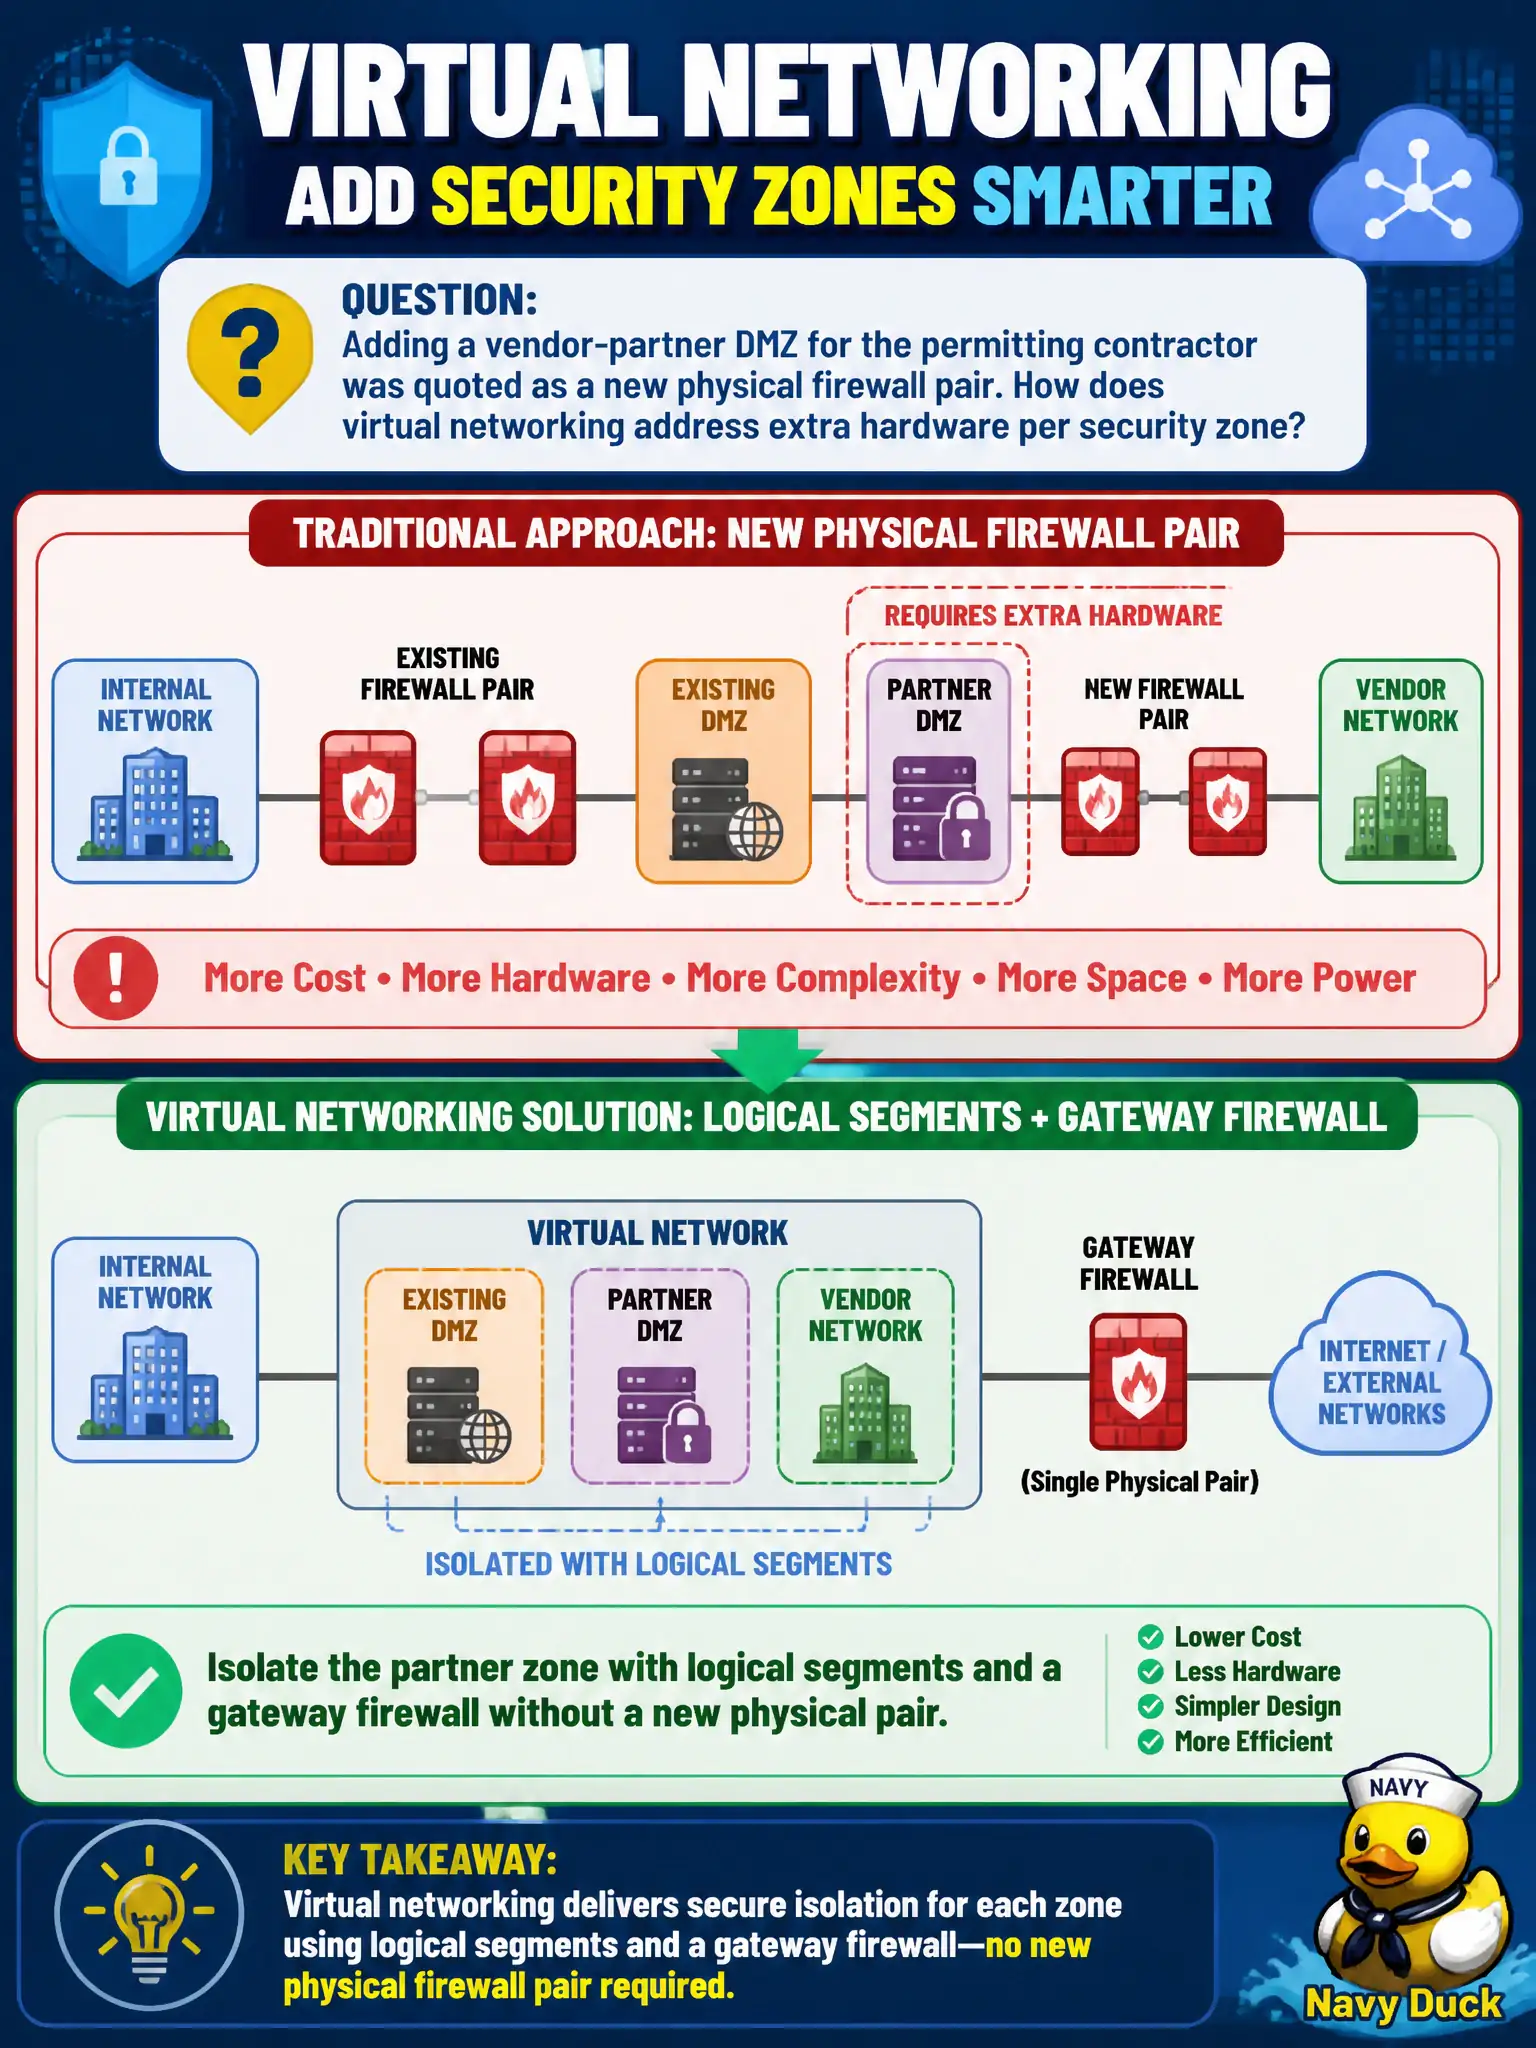
Adding a vendor-partner DMZ for the permitting contractor was quoted as a new physical firewall pair. How does virtual networking address extra hardware per security zone?
Select an answer to reveal the explanation.
Short Explanation
A new hardware pair for every partner is like buying a new gatehouse for each visiting contractor. Logical segments and a gateway firewall draw that DMZ on the existing fabric. Guest Wi-Fi and Horizon UAG are not the civic server-zone isolation the seed is after.
Full Explanation
Isolating a vendor-partner DMZ with logical segments and a gateway firewall avoids quoting a new physical firewall pair for every permitting contractor zone. Virtual networking creates security zones as software on shared Edges and hosts. Buying a smaller dedicated firewall pair because "overlay cannot isolate partners" contradicts the model. Placing vendor VMs on guest Wi-Fi is insecure and inappropriate for server DMZs. Using Horizon Unified Access Gateway as the only partner DMZ for server workloads misapplies a VDI access component. Exam caveat: partner zones still need strong default-deny, logging, and possibly physical separation for highest-risk cases; software isolation is the default agility answer on the exam. Operational check: stand up a contractor segment with gateway firewall policy allowing only required permitting API flows and deny all else. Keep municipal naming and change tickets aligned with the software objects so civic audits can trace intent. Prefer verifying with a non-production agency workload before promoting the same pattern to life-safety systems. Record realization state and underlay health in the runbook used by on-call city operators. Keep municipal naming and change tickets aligned with the software objects so civic audits can trace intent.