
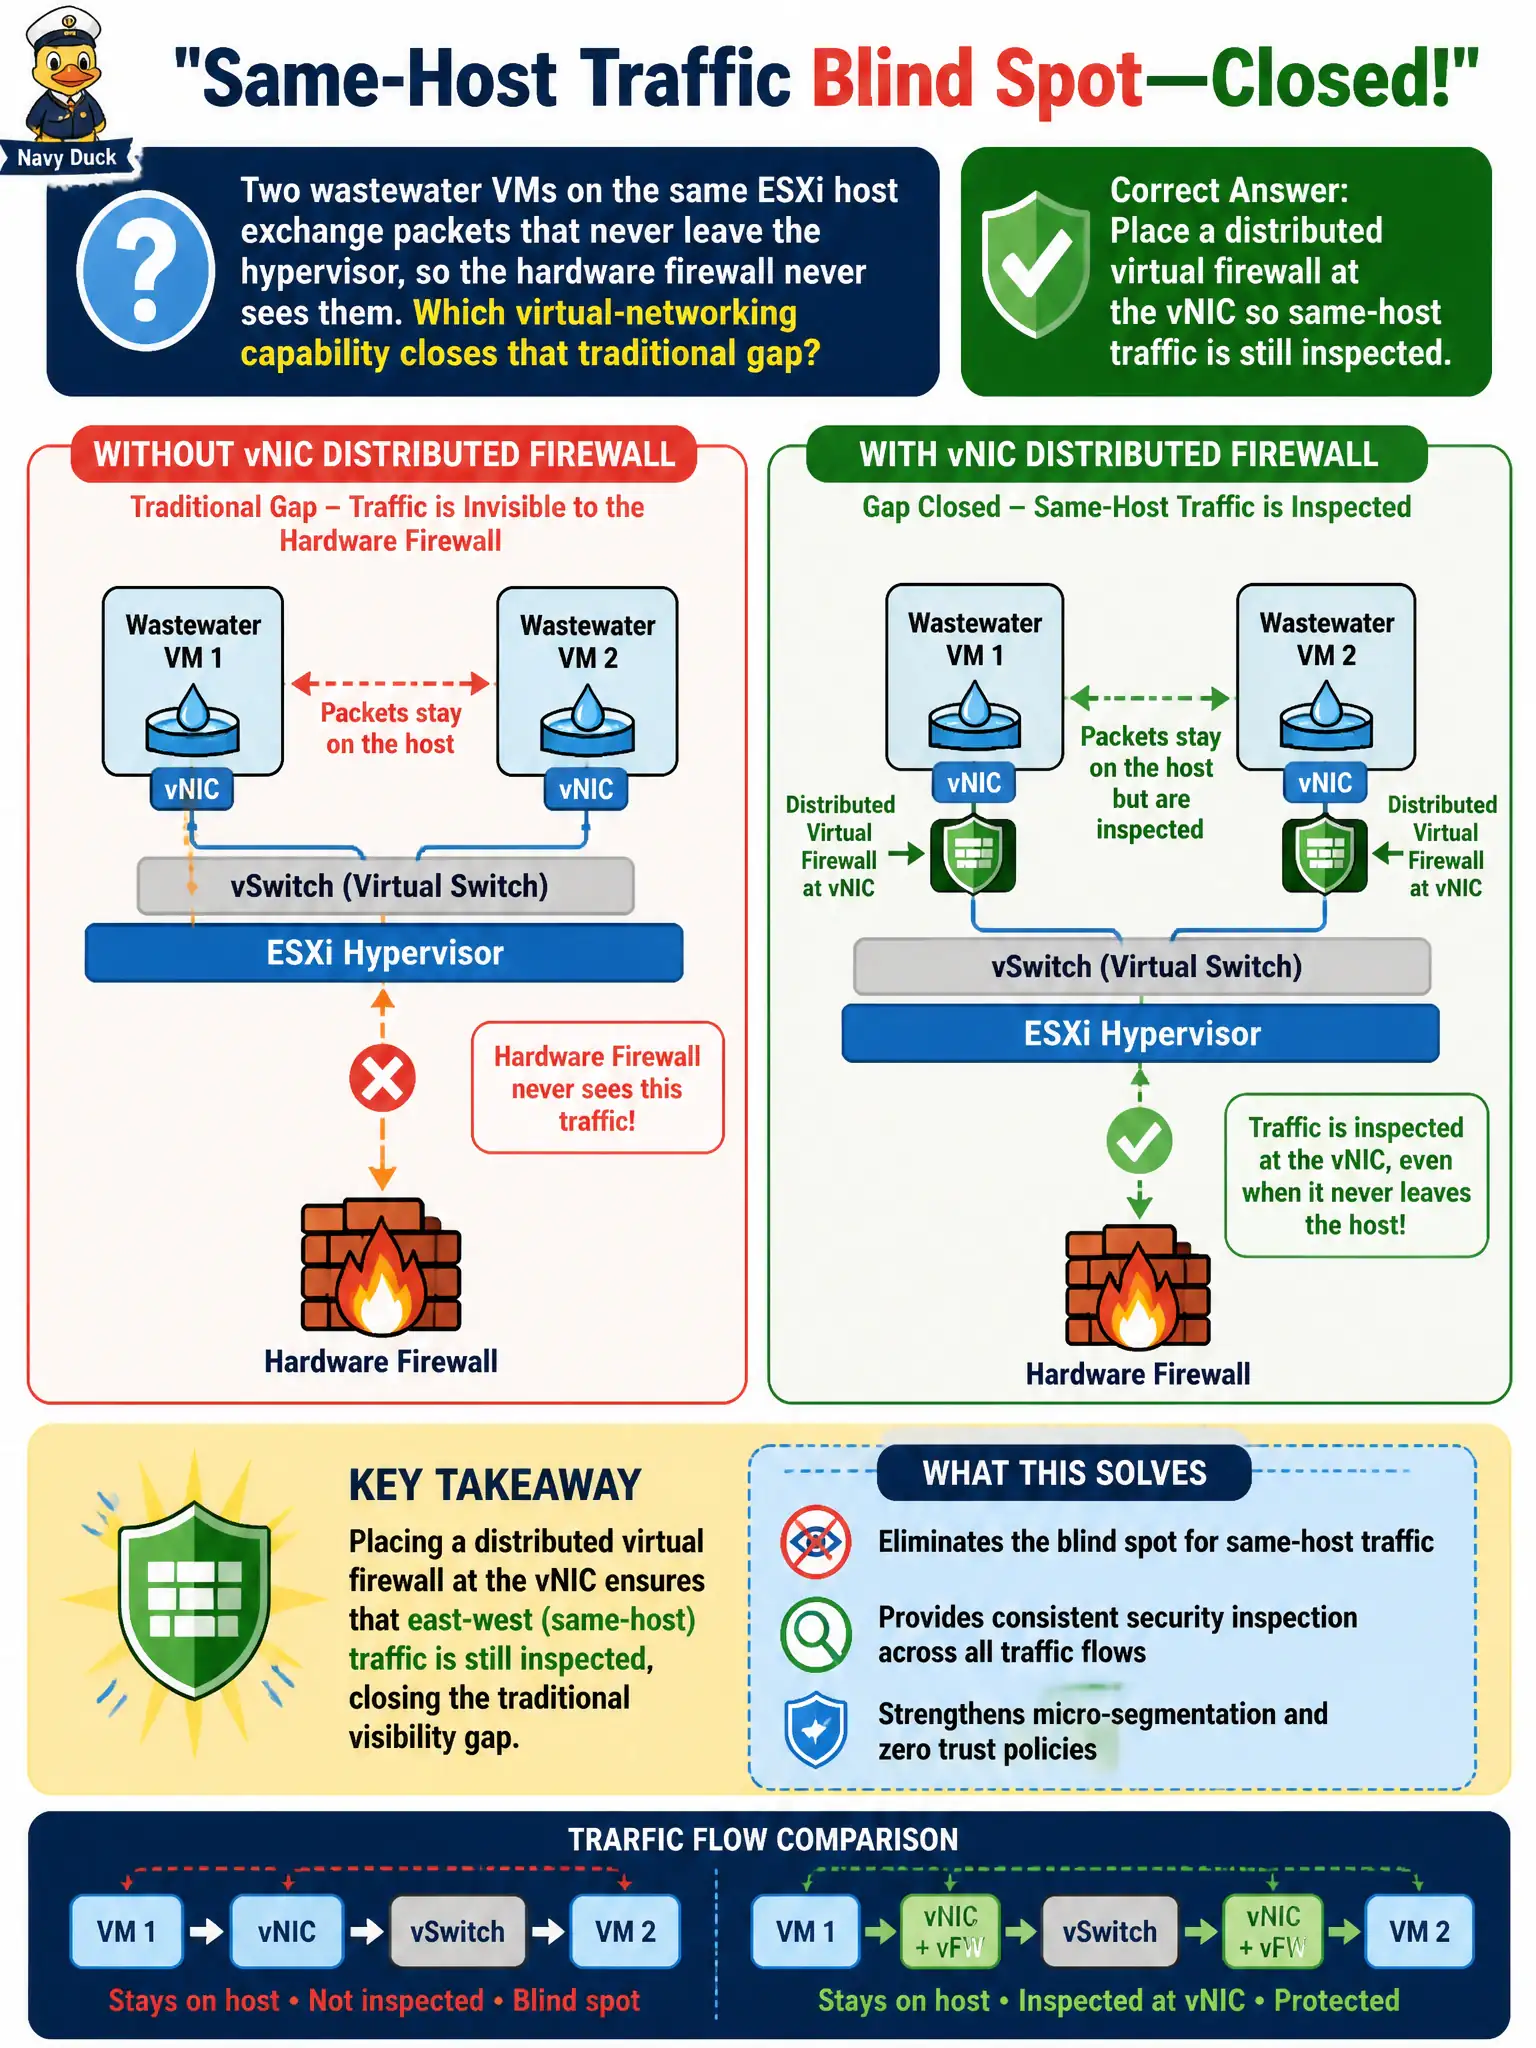
Two wastewater VMs on the same ESXi host exchange packets that never leave the hypervisor, so the hardware firewall never sees them. Which virtual-networking capability closes that traditional gap?
Select an answer to reveal the explanation.
Short Explanation
Same-host VM talk is like two offices passing notes under the door—the street cop at the hardware firewall never sees it. A distributed firewall sits at each vNIC and reads those notes before they hop. vMotion or Workspace ONE Intelligence does not become that in-host checkpoint.
Full Explanation
A distributed virtual firewall at the vNIC inspects same-host traffic that never leaves the hypervisor, closing the traditional gap where a hardware firewall never sees those wastewater VM packets. Forcing vMotion solely so packets hit a physical firewall is operationally wasteful. Mirroring to Workspace ONE Intelligence for MDM inspection is not the network firewall control. Disabling the virtual switch to fail closed is not a workable design. Exam caveat: DFW rules must be realized on the host; policy that exists only in the UI without successful realization still leaves a gap. Operational check: place two wastewater test VMs on one ESXi host and verify DFW logs/counters show enforcement for a denied east-west probe that never reaches the ToR. Keep municipal naming and change tickets aligned with the software objects so civic audits can trace intent. Prefer verifying with a non-production agency workload before promoting the same pattern to life-safety systems. Record realization state and underlay health in the runbook used by on-call city operators. Keep municipal naming and change tickets aligned with the software objects so civic audits can trace intent. Prefer verifying with a non-production agency workload before promoting the same pattern to life-safety systems.