
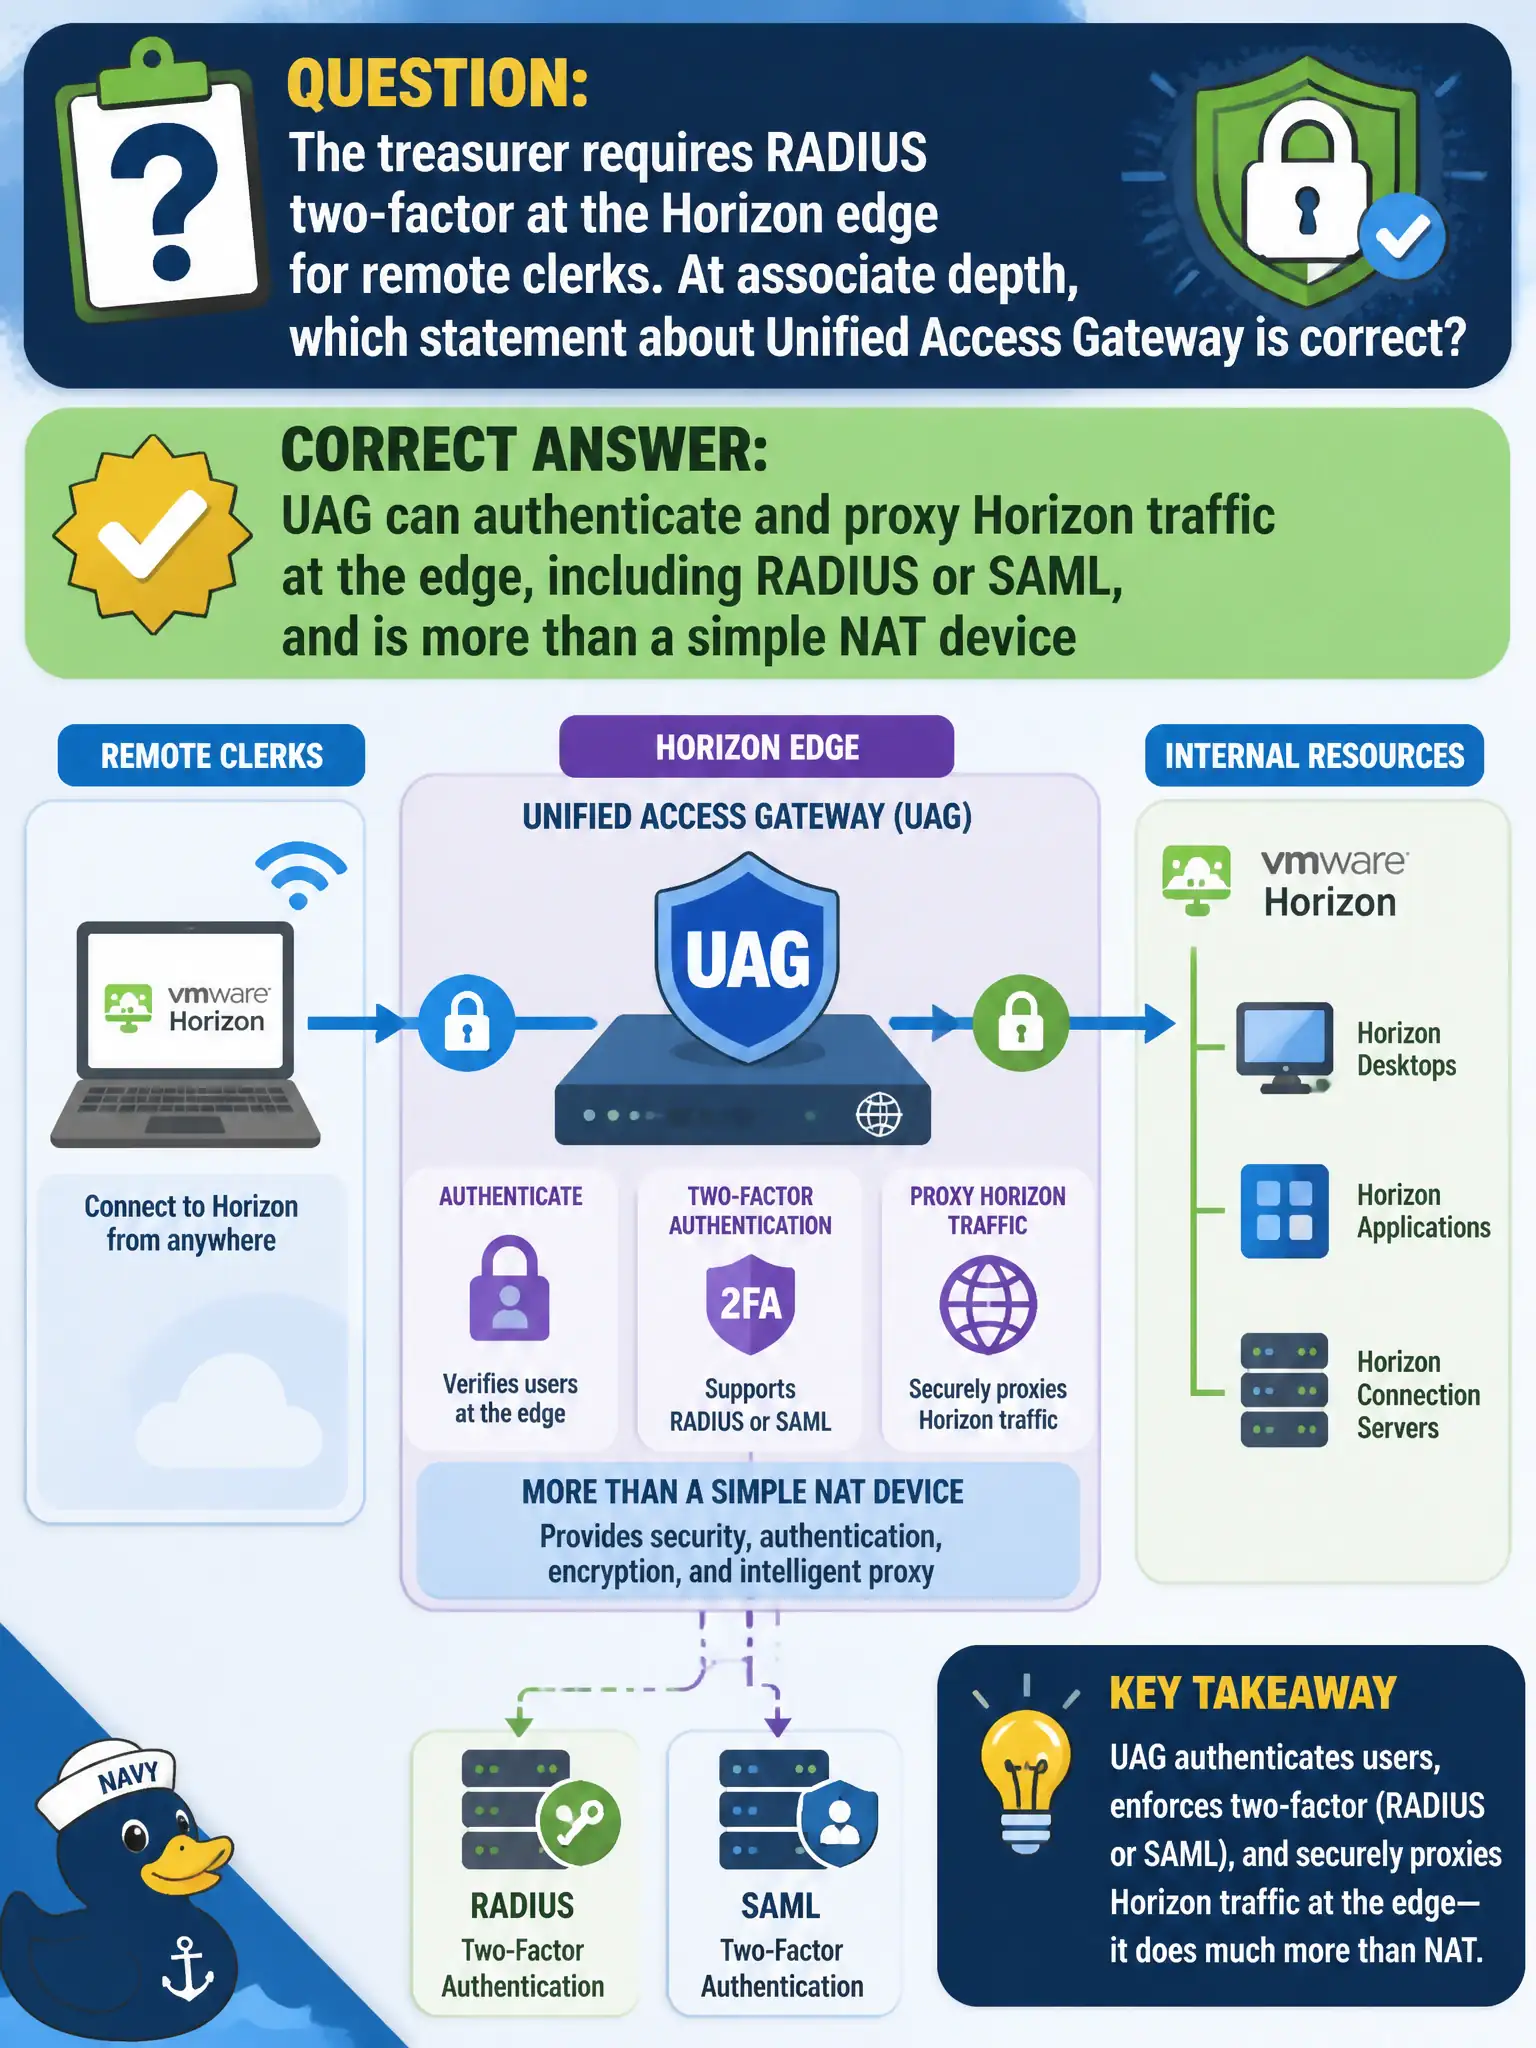
The treasurer requires RADIUS two-factor at the Horizon edge for remote clerks. At associate depth, which statement about Unified Access Gateway is correct?
Select an answer to reveal the explanation.
Short Explanation
UAG is not a cheap NAT sticker on the firewall. It is the certified Horizon edge box that can proxy the session and handle RADIUS or SAML at the door. NSX DFW and Assist do not take that job.
Full Explanation
When the treasurer requires RADIUS two-factor at the Horizon edge for remote clerks, Unified Access Gateway can authenticate and proxy Horizon traffic at the edge, including RADIUS or SAML integrations, and is more than a simple NAT device. At associate depth, treat UAG as an intelligent secure gateway that can participate in authentication for municipal remote access, not as a dumb port forwarder on the civic firewall. UAG is not only a NAT rule and can participate in authentication workflows. NSX Distributed Firewall does not replace UAG whenever RADIUS is required for Horizon remote access. Workspace ONE Assist remote control is not the certified Horizon edge appliance for Blast and broker XML-API. Exam caveat: exact auth method screens vary by version, but the exam idea is that UAG is where such edge controls apply for remote Horizon—DFW micro-segmentation and Assist support do not become the Horizon gateway. Operational check: enable the required RADIUS or SAML edge authentication on UAG for remote clerks, test a treasurer-approved login path end to end, confirm NAT-only firewall rules without UAG are insufficient for the requirement, and keep Assist off the Horizon edge diagram.