
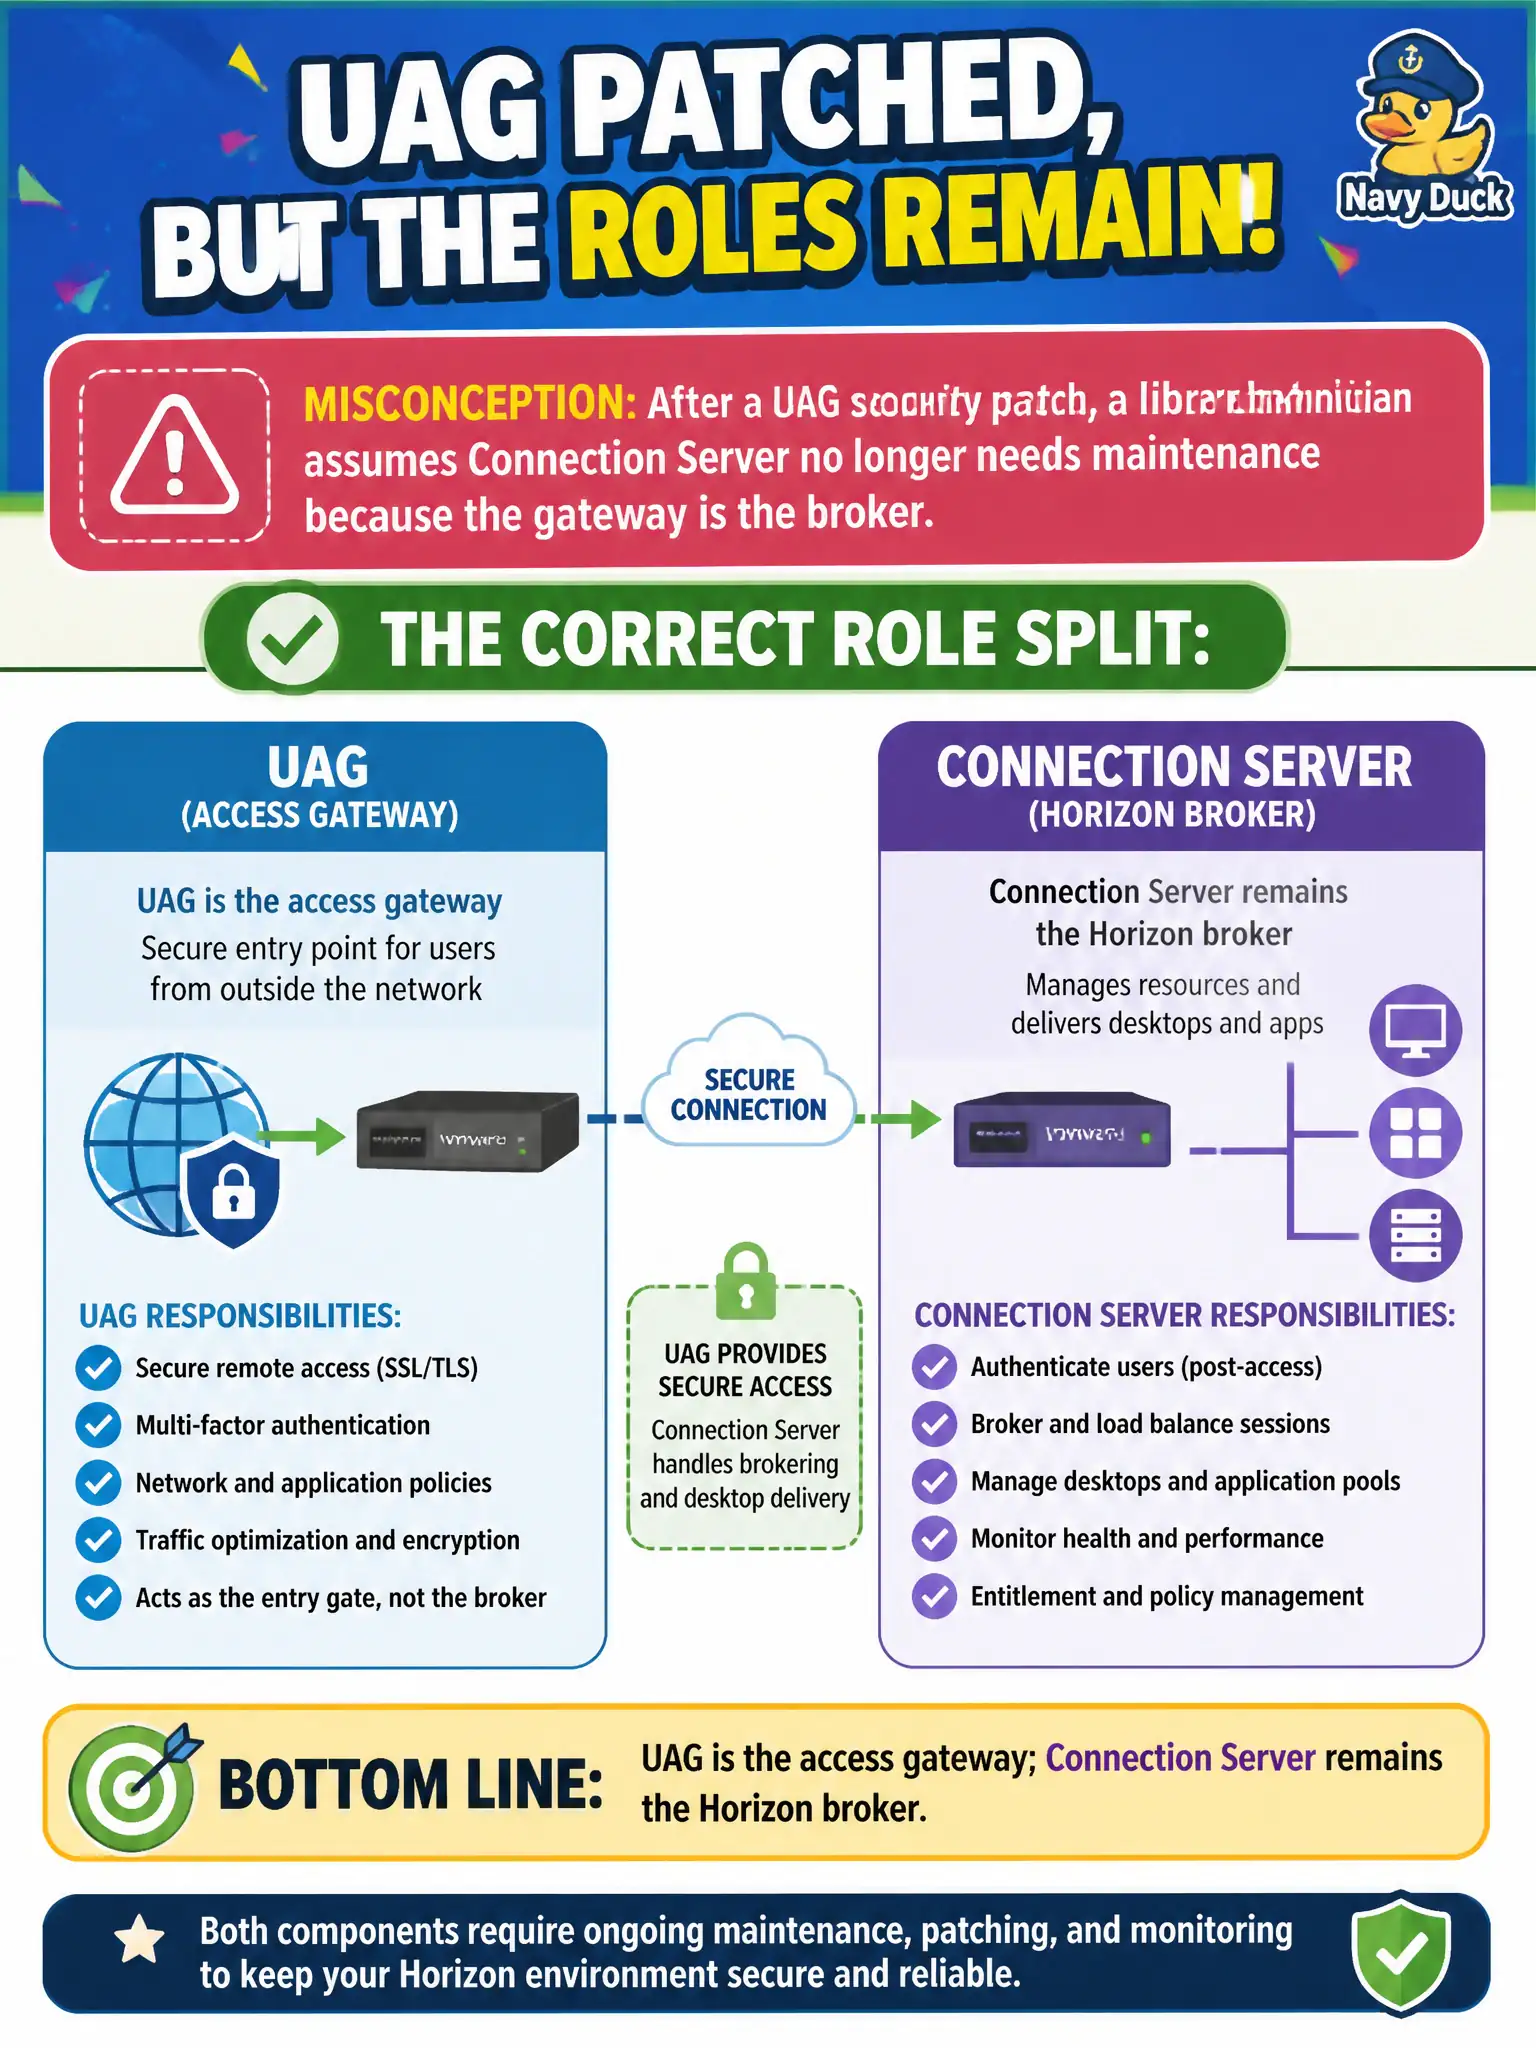
After a UAG security patch, a library technician assumes Connection Server no longer needs maintenance because the gateway is the broker. What is the correct role split?
Select an answer to reveal the explanation.
Short Explanation
UAG is the doorman; Connection Server is the front desk that actually assigns rooms. Patching the doorman does not fire the front desk. Two boxes, two jobs—keep both healthy.
Full Explanation
After a UAG security patch, assuming Connection Server no longer needs maintenance because the gateway is the broker is incorrect. Unified Access Gateway is the access gateway; Connection Server remains the Horizon broker that entitles users and connects them to desktop and application pools. Both components stay in the civic maintenance and compatibility plan. UAG does not broker desktop pools while Connection Server only terminates Blast. Patching UAG does not automatically upgrade Connection Server through vMotion. App Volumes Manager does not become both the edge and the broker after a UAG patch. Exam caveat: version compatibility between UAG and Connection Server still matters; patching one tier does not retire lifecycle work on the other, and vMotion is unrelated to product upgrades. Operational check: after UAG patching, verify Connection Server services and pool brokering still function for a test library user, confirm UAG still only gateways, schedule Connection Server patches on their own cadence with a compatibility matrix check, and update the municipal patch calendar. Keep civic diagrams labeled so help-desk and network teams do not swap these products during incidents.