
How should the associate identify Unified Access Gateway in the UEM access design?
Select an answer to reveal the explanation.
Short Explanation
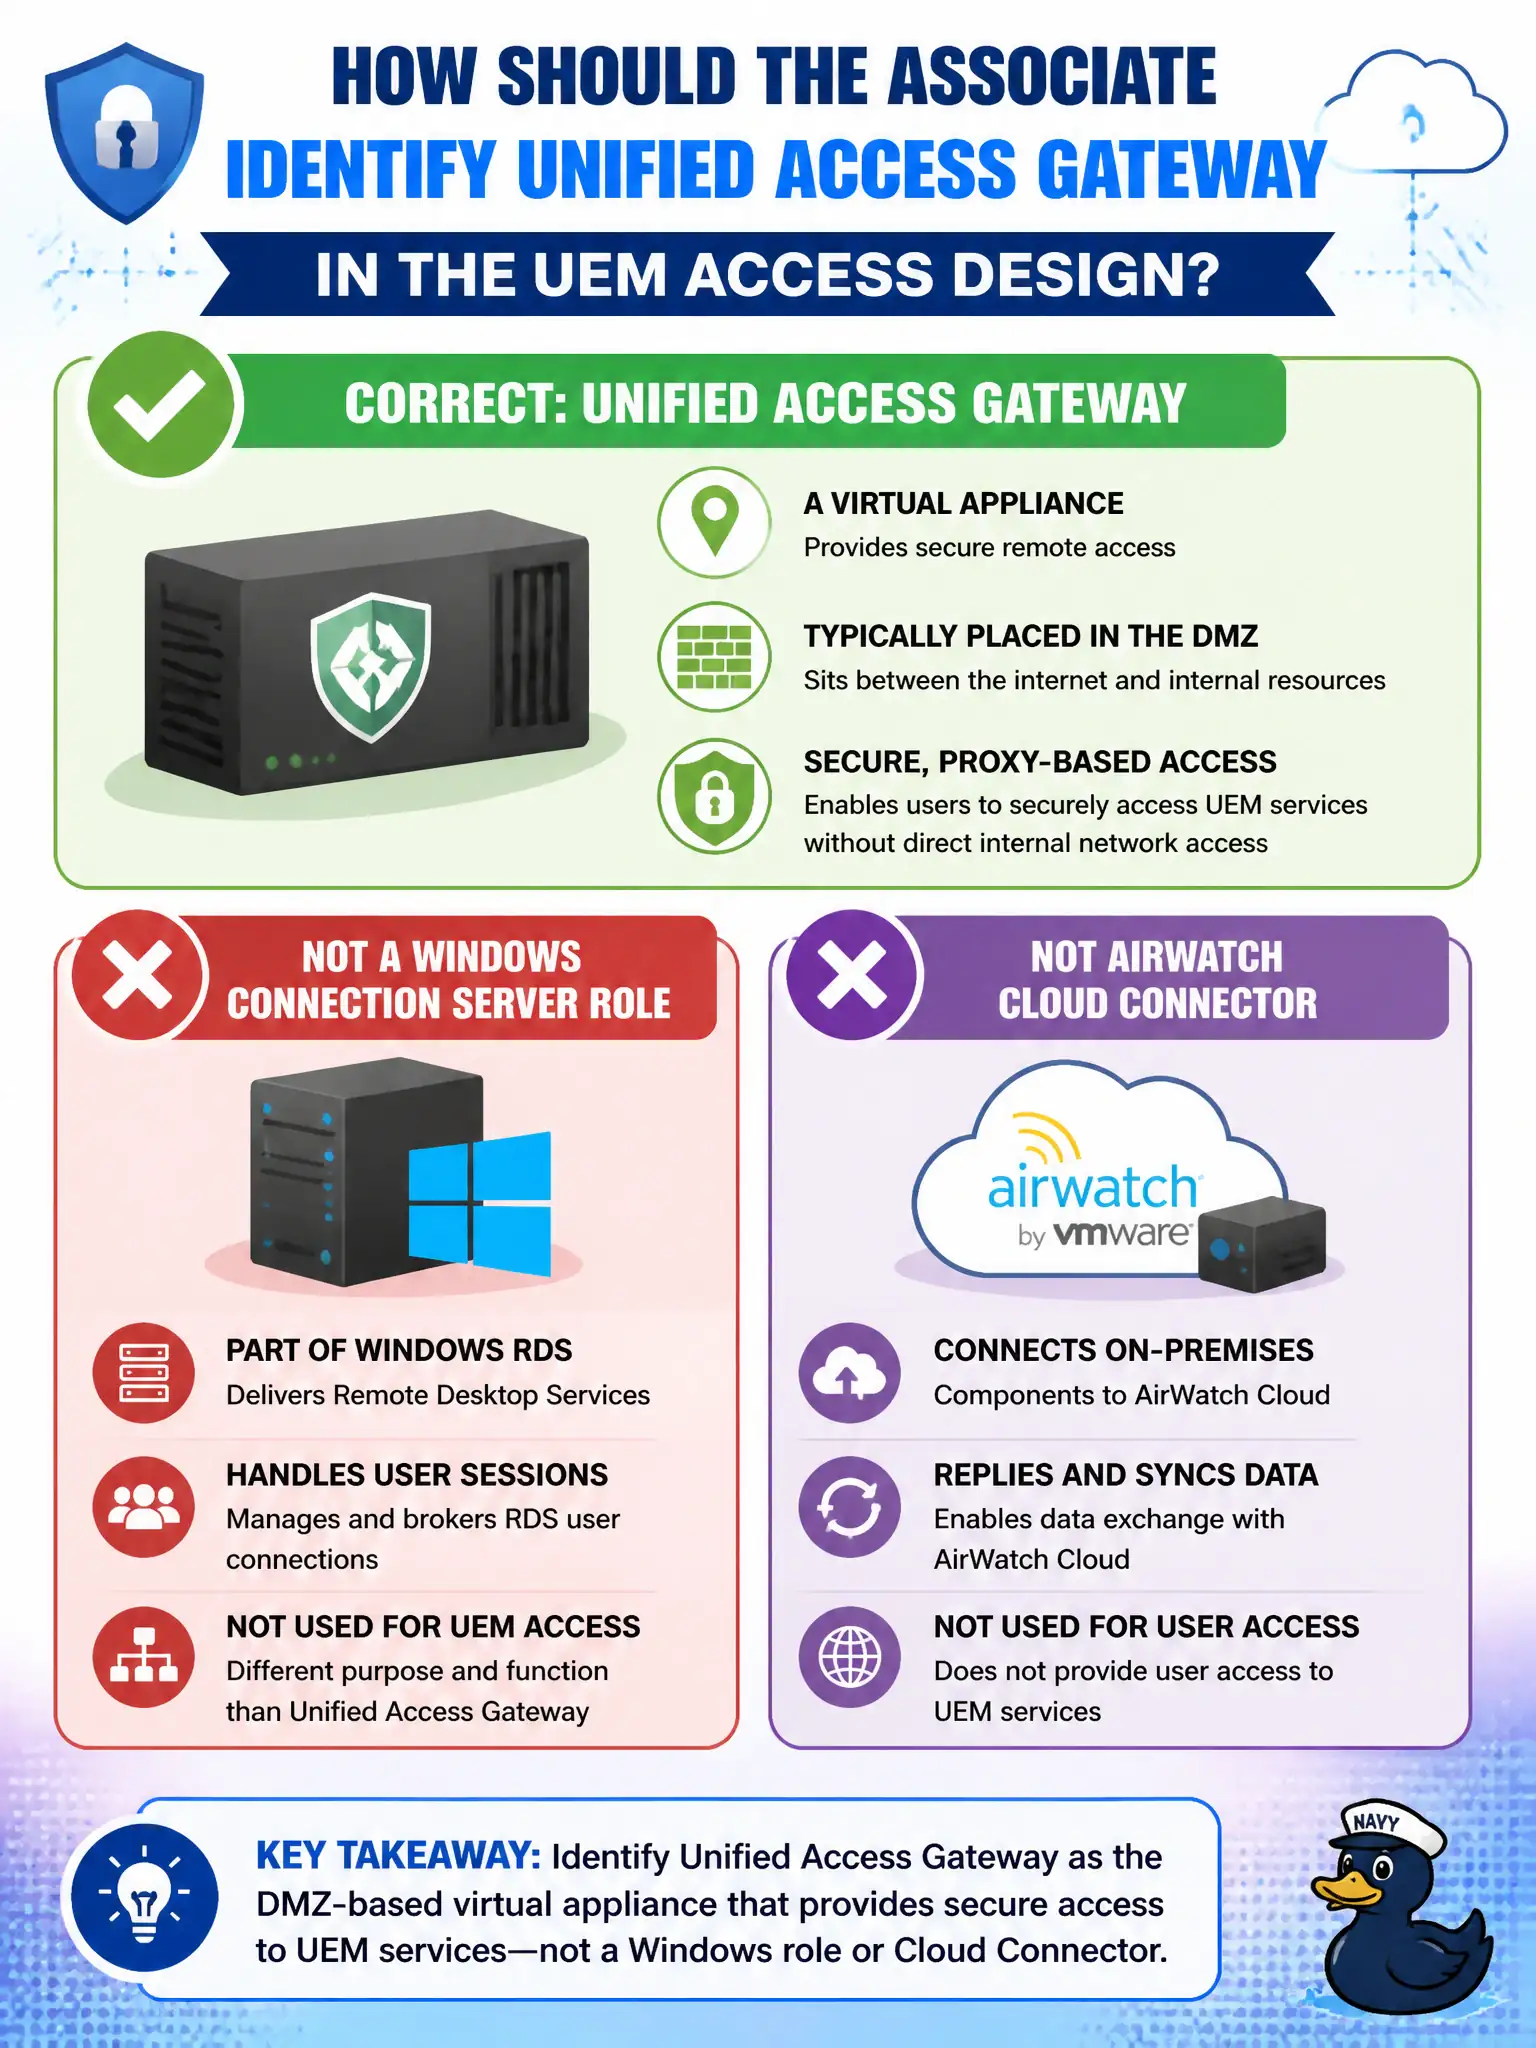
UAG is a DMZ appliance, like a guard shack in the parking lot, not a Windows role bolted onto Connection Server and not the directory courier. Cloud Connector talks to AD; App Volumes talks to packages.
Full Explanation
At associate depth, Unified Access Gateway in the UEM access design is identified as a virtual appliance typically placed in the DMZ—not a Windows Connection Server role and not AirWatch Cloud Connector. UAG is the edge guard shack for Horizon and for UEM edge services such as Tunnel, separate from directory connectors and separate from the Horizon broker operating system role inside the trusted network. UAG is not a Windows service that is installed on every Connection Server. UAG is not the on-premises directory connector that binds SaaS UEM to Active Directory—that is AirWatch Cloud Connector. UAG is not the vCenter Server plugin that layers applications onto instant clones; application layering is an App Volumes concern on vSphere-hosted desktops, not a UAG identity. Exam caveat: do not merge UAG, Cloud Connector, and Connection Server into one edge blob on civic diagrams; place UAG in the DMZ and keep connectors and brokers in appropriate internal zones. Operational check: on the city’s network diagram, place UAG in the DMZ, place Cloud Connector internal for AD and CA integrations, place Connection Server internal as the Horizon broker, and confirm no design document calls UAG a Windows Connection Server service or a directory connector.