
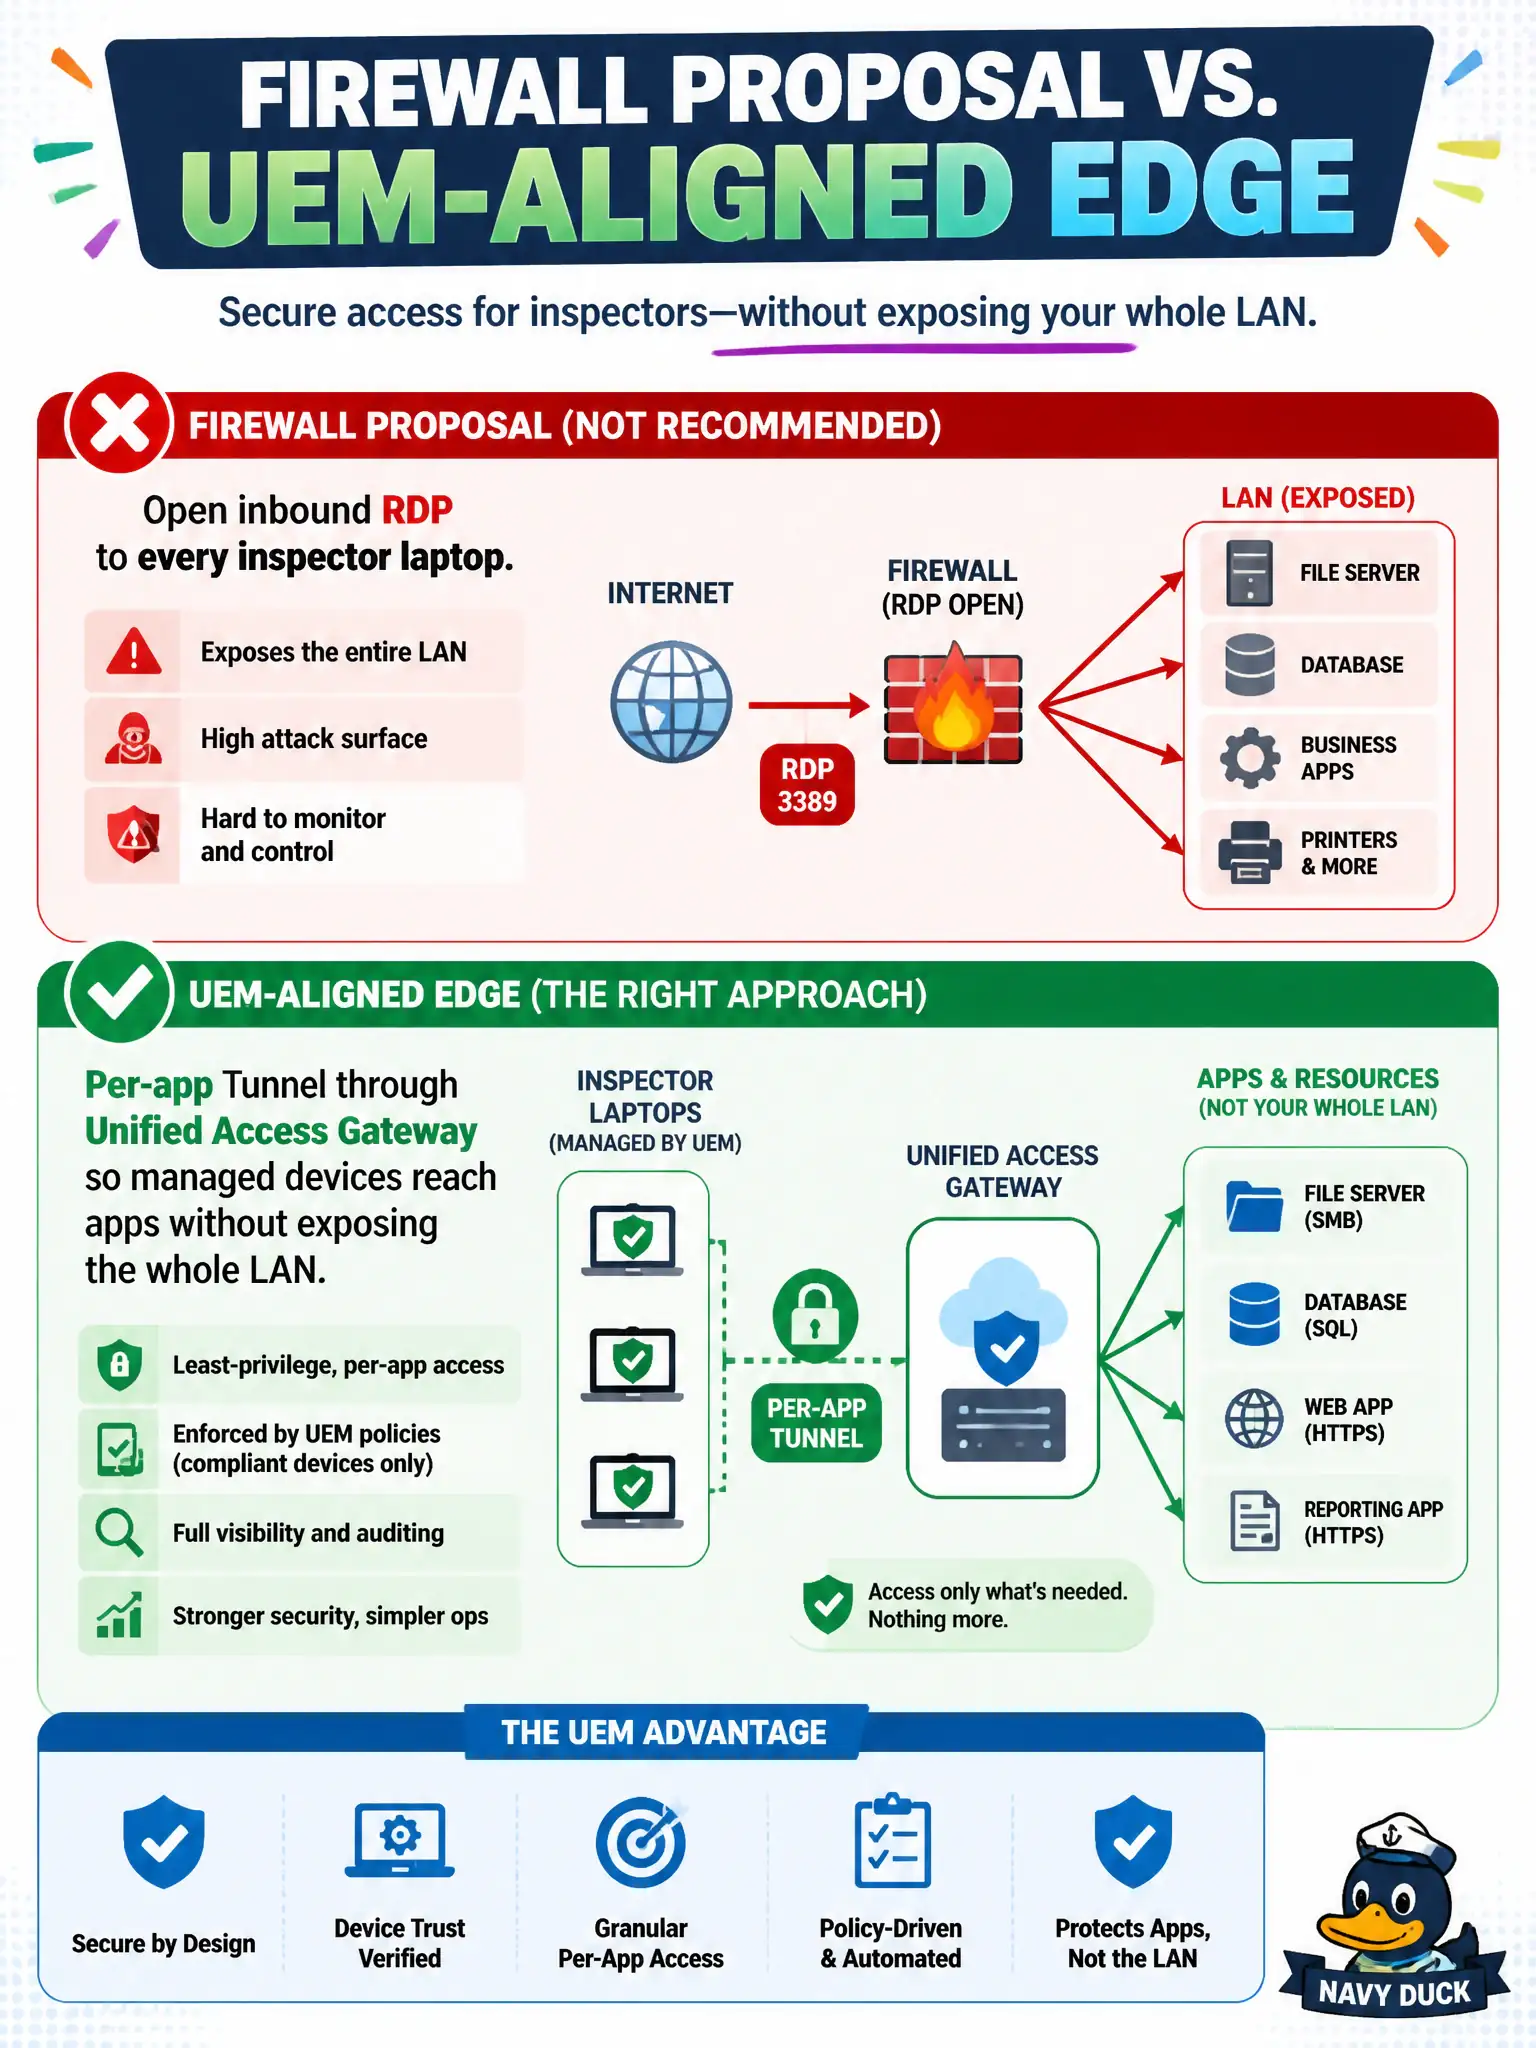
A firewall proposal would open inbound RDP to every inspector laptop. What is the UEM-aligned edge instead?
Select an answer to reveal the explanation.
Short Explanation
Do not leave a front door on every inspector laptop. Per-app Tunnel through UAG is a single locked hatch for the app, not the whole LAN. NSX overlays, a public Connection Server, and App Volumes do not replace that hatch.
Full Explanation
A firewall proposal that would open inbound RDP to every inspector laptop is the wrong municipal edge design. The UEM-aligned approach is per-app Tunnel through Unified Access Gateway so managed devices reach needed applications without exposing the whole LAN or publishing every laptop’s RDP listener to untrusted networks. That single locked application path is what associate-depth Workspace ONE access design expects. Publishing every laptop’s RDP port through an NSX overlay still exposes remote desktop broadly and is not the Workspace ONE Tunnel answer. Putting Horizon Connection Server on the internet as a laptop jump host confuses VDI brokering with endpoint RDP exposure and places the broker on the wrong trust boundary. Installing App Volumes Agent does not convert RDP into a safe package-attach model for remote inspector laptops. Exam caveat: Tunnel protects application paths on managed devices; it is not a blanket replacement for every remote-support use case—Workspace ONE Assist may still be used for screen share under civic policy. Operational check: block inbound RDP to inspector endpoints from the internet, enable Tunnel via UAG for the required civic apps, confirm those apps work over Tunnel from the field, and verify RDP ports remain closed from untrusted sources in a scan or firewall review.