
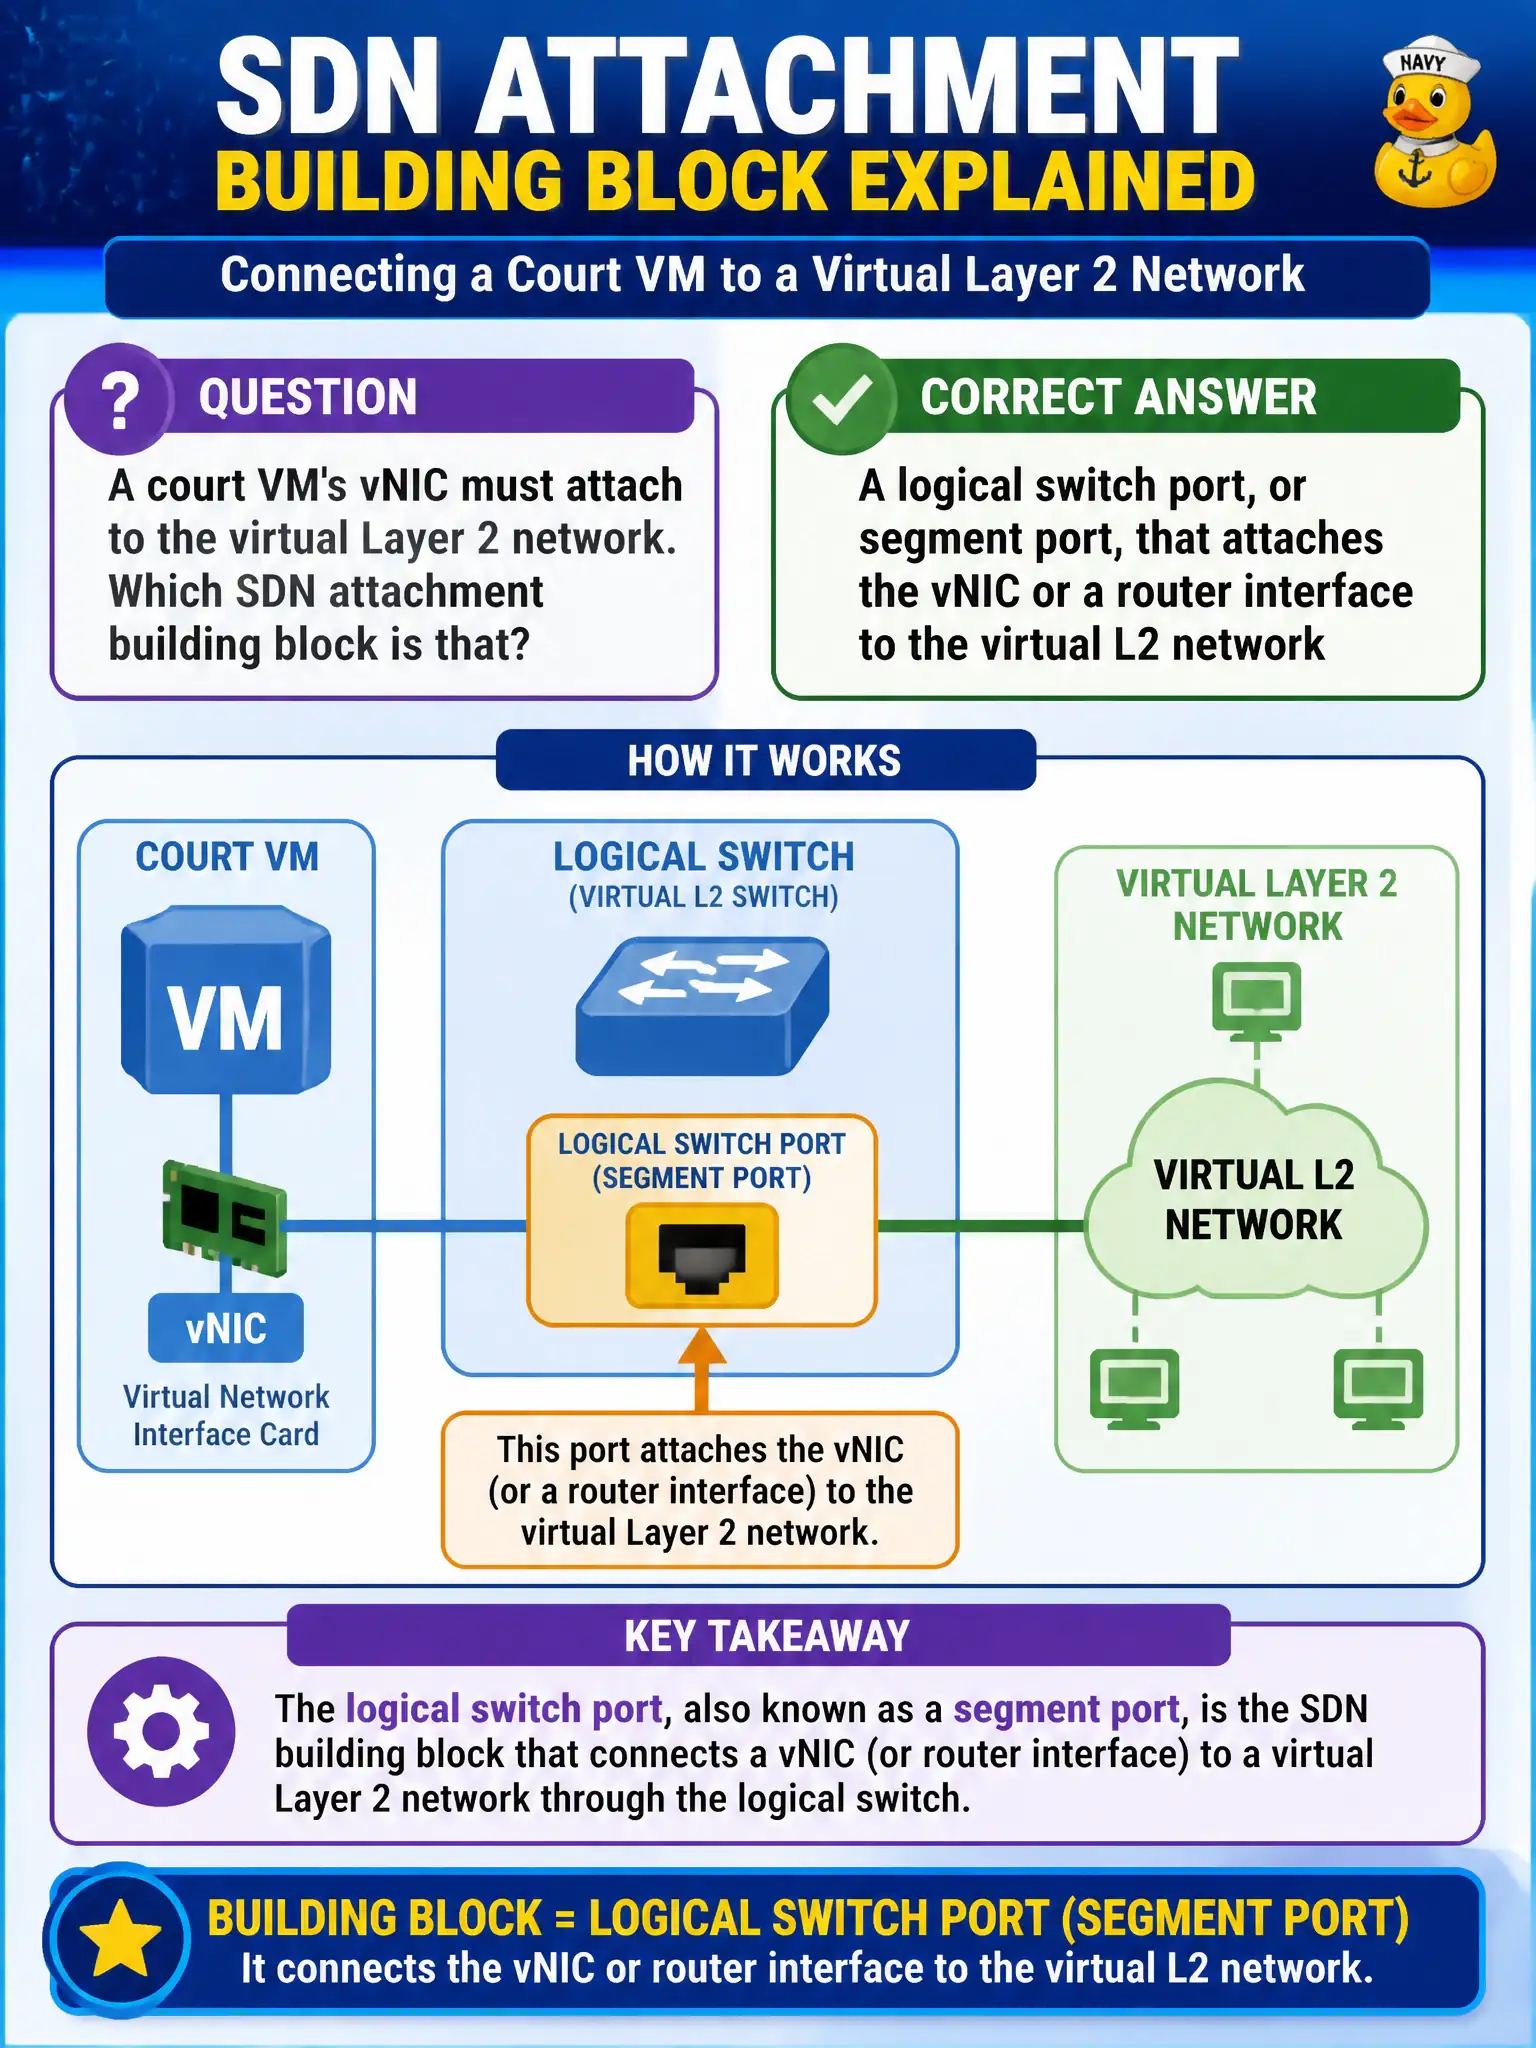
A court VM's vNIC must attach to the virtual Layer 2 network. Which SDN attachment building block is that?
Select an answer to reveal the explanation.
Short Explanation
The segment is the hallway; the segment port is the door the court vNIC actually uses. A datastore mount, a Horizon session, or a sensor ID is not that door.
Full Explanation
A court VM’s vNIC joins the virtual Layer-2 network through a logical switch port—called a segment port in Policy mode. That attachment building block is the door on the segment hallway: it connects a VM vNIC, or a logical-router interface, to the virtual L2 network so the guest can participate in the civic segment’s broadcast domain and related security controls. A vSphere datastore mount presents capacity for virtual disks and never turns storage into a network attachment for the vNIC. A Horizon session associates a user with a desktop remoting path; it does not bind a vNIC to an NSX segment. A Carbon Black sensor ID identifies an endpoint agent and is not the VM’s MAC address or segment port object. Exam caveat: Distributed Firewall and other port-based controls evaluate traffic in the context of that logical or segment port. If the vNIC is attached to the wrong segment, firewall troubleshooting will look mysterious until attachment is corrected. Operational check: connect the court VM’s vNIC to the intended segment, locate the realized segment port in NSX, generate a ping or application probe, and confirm counters move on that port while datastore mounts, Horizon sessions, and sensor IDs remain unrelated to the attachment.