
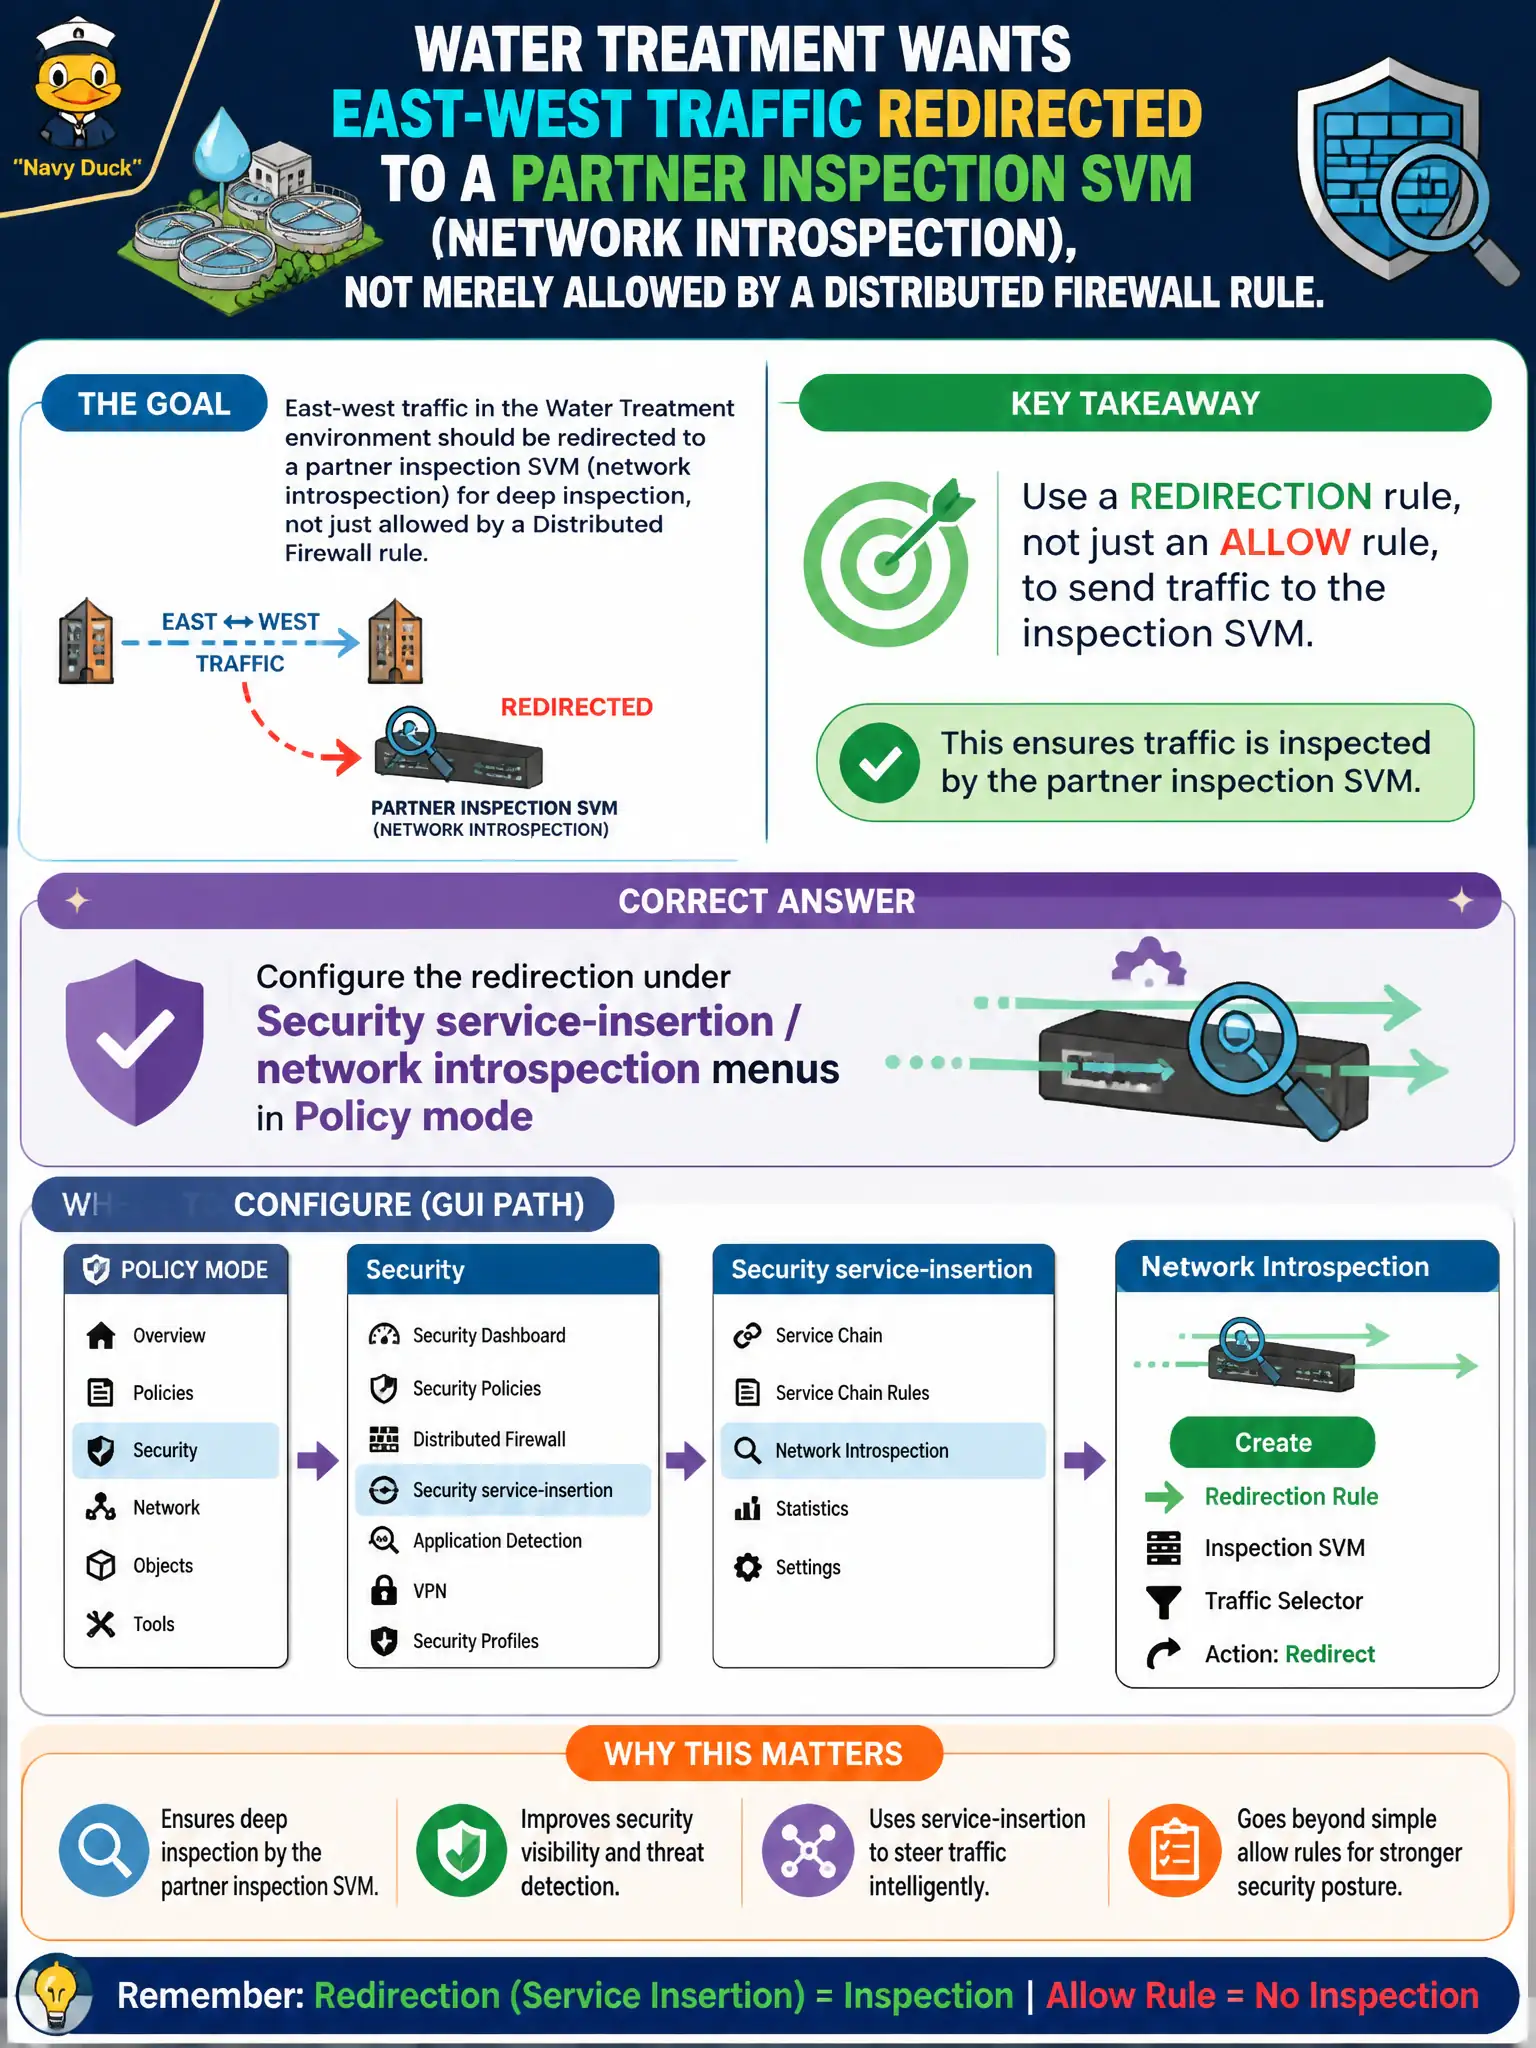
Water treatment wants east-west traffic redirected to a partner inspection SVM (network introspection), not merely allowed by a Distributed Firewall rule. Which GUI family hosts that redirection rule?
Select an answer to reveal the explanation.
Short Explanation
Allowing a packet is not the same as steering it through the city’s inspection booth. East-west redirection lives under Security service insertion / network introspection in Policy—DFW allow, DNS, and HA do not chain that SVM.
Full Explanation
Water treatment’s need to redirect east-west traffic to a partner inspection SVM is network introspection / service insertion, configured under Security service-insertion / network introspection menus in Policy mode. Redirection steers packets to the partner SVM for inspection rather than merely allowing them with a Distributed Firewall rule. Publishing a DFW allow-any rule permits traffic; it does not redirect packets to a partner SVM. Adding a DNS forwarder on the Tier-1 is DNS services, not service insertion redirection. Raising vSphere HA admission control affects cluster failover capacity; it does not redirect overlay flows to an introspection SVM. Exam caveat: service insertion requires the partner service deployment and correct redirection policy; a healthy DFW allow is not evidence that introspection redirection is active. Operational check: confirm the partner SVM is registered/healthy, create the redirection policy for the water-treatment east-west path, verify traffic hits the SVM in partner logs, and record the service chain in the OT/IT change package. In municipal operations, record the chosen control and the rejected alternatives in the change ticket so future on-call staff understand which failure modes would affect city services. Re-validate after the next maintenance window that the same GUI path and realized state still hold under the current NSX build used by the civic platform team.