
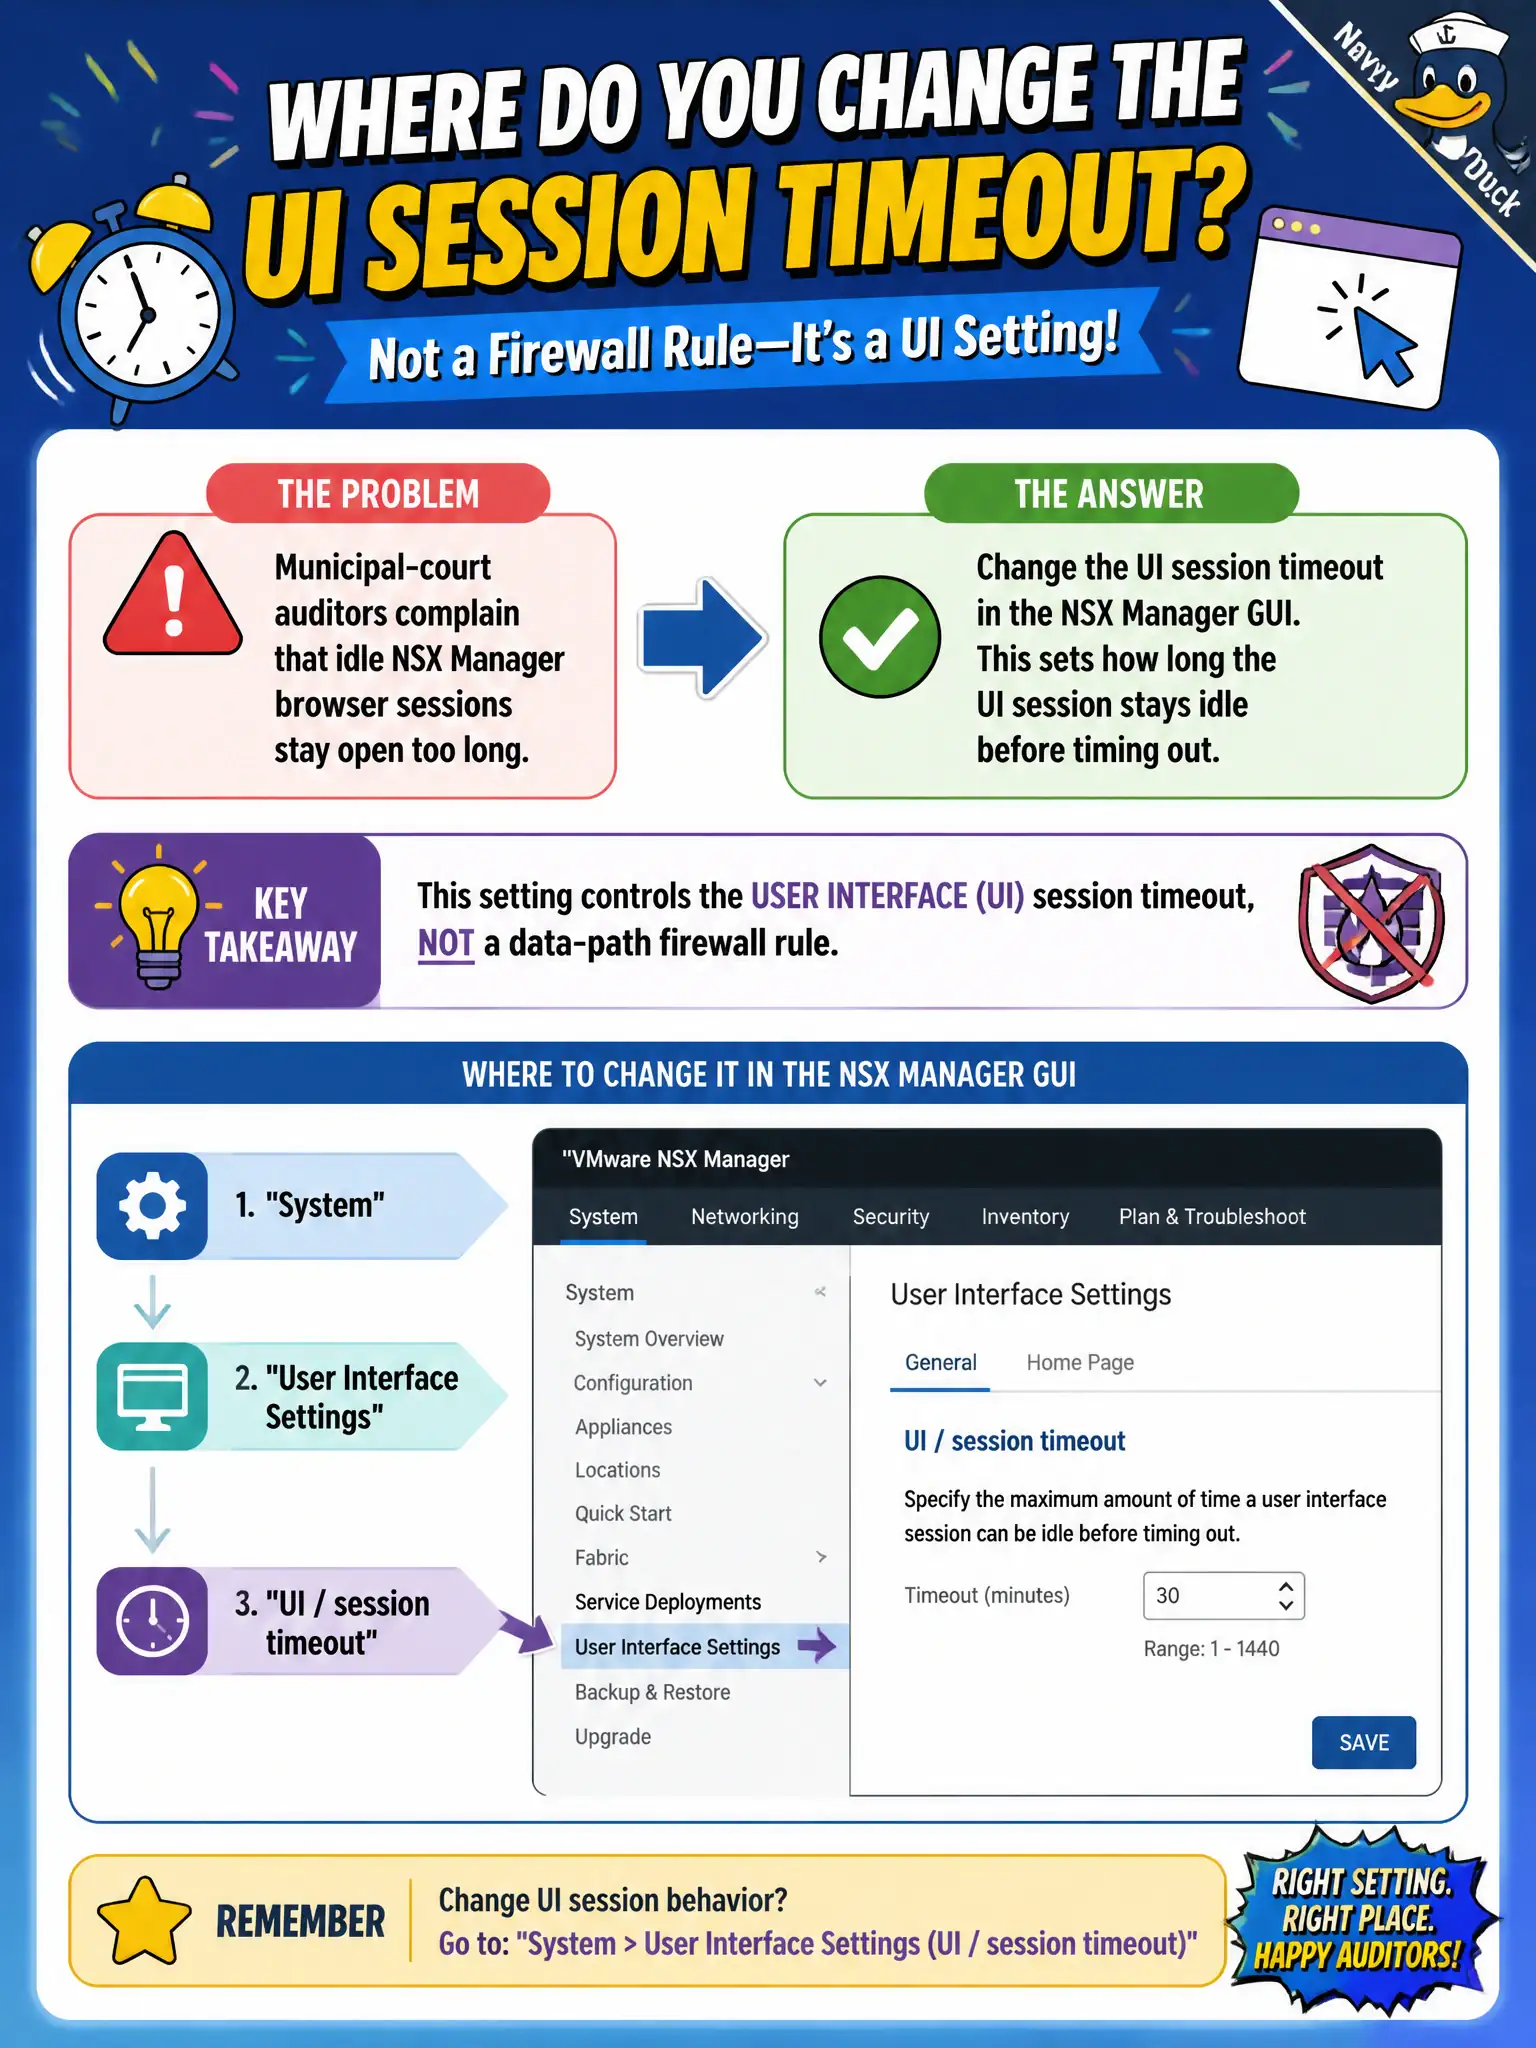
Municipal-court auditors complain that idle NSX Manager browser sessions stay open too long. Which GUI location changes the UI session timeout rather than a data-path firewall rule?
Select an answer to reveal the explanation.
Short Explanation
How long a clerk's browser stays signed into city hall is a front-desk policy, not a street-firewall rule. Session timeout lives under System > User Interface Settings, not Distributed Firewall.
Full Explanation
Idle NSX Manager browser session lifetime is a System UI control, not a data-path firewall rule. Municipal-court auditors who need shorter idle timeouts change System > User Interface Settings (UI / session timeout) so clerk and auditor sessions expire according to city-hall front-desk policy without touching overlay forwarding. Adding a Distributed Firewall deny for HTTPS to NSX Manager is the wrong concept: that would block management access rather than timing out idle authenticated UI sessions, and DFW exclusion practices often keep Managers off DFW enforcement. Shortening DHCP lease on a management overlay segment affects address renewal, not authenticated UI session idle timers. Inventory > Groups tagging auditor accounts does not implement UI session expiry; tags feed grouping for security policy, not Manager session length. Exam caveat: UI session timeout is distinct from API token lifetime and from IdP session policy—align all three when the city uses federated login. Operational check: set the UI timeout to the auditor-approved value, sign in with a test auditor account, idle past the threshold, confirm forced re-authentication, and record the setting in the court security baseline.