
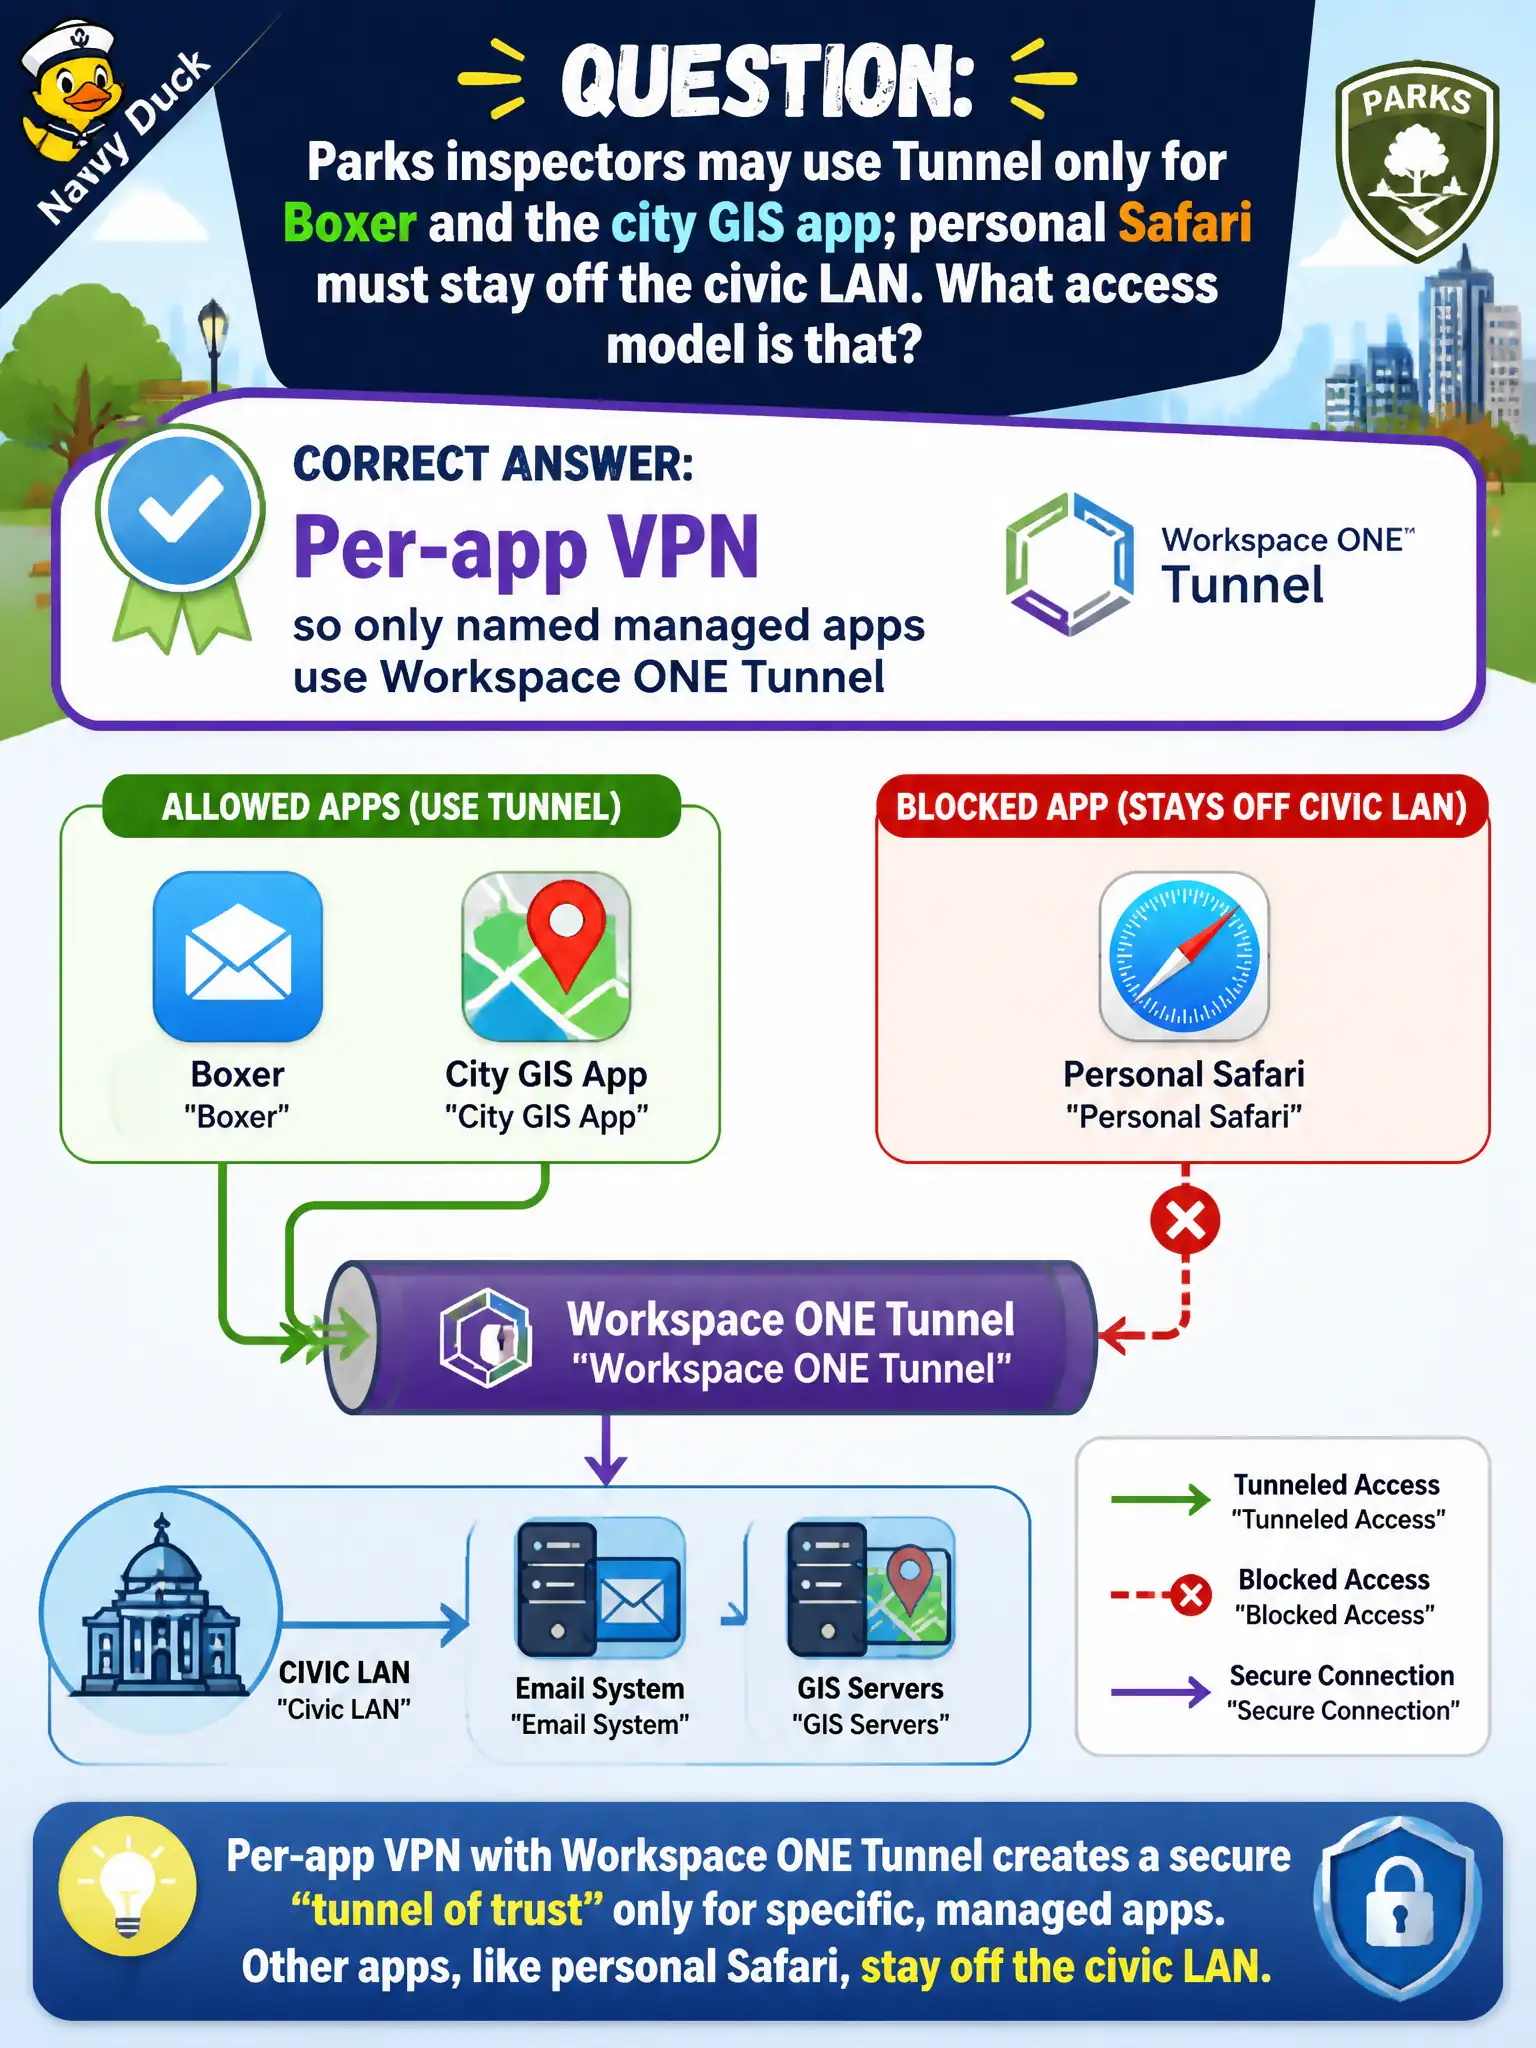
Parks inspectors may use Tunnel only for Boxer and the city GIS app; personal Safari must stay off the civic LAN. What access model is that?
Select an answer to reveal the explanation.
Short Explanation
Think of Tunnel as a staff-only side door for named apps, not a loading dock that swallows Safari too. Device-wide IPsec would haul personal browsing onto the LAN, and Horizon HTML Access or NSX would be the wrong door entirely. Only Boxer and GIS using Tunnel is the per-app VPN model.
Full Explanation
Per-app VPN with Workspace ONE Tunnel means administrators nominate managed apps—such as Boxer and a city GIS client—so only those processes use the Tunnel path while personal Safari stays off the civic LAN. That access model matches parks-inspector requirements that separate work apps from personal browsing. Parks IT uses that model so inspectors can map assets and read mail without exposing the entire personal browser session to internal GIS servers. A device-wide always-on IPsec tunnel that includes every process is a different access model and would haul personal Safari onto the civic LAN. Horizon HTML Access turns a browser into a VDI client to a broker; it does not redefine Safari as a civic LAN VPN client for arbitrary sites. NSX Distributed Firewall enforces data-center east-west and perimeter rules; it is not the phone's VPN client. Exam caveat: Items that contrast Tunnel with full-device VPN are testing scope—named managed apps versus the entire device—not whether encryption exists. Operational check: Enable Tunnel for Boxer and GIS only, open a civic-only URL from each managed app, then confirm Safari cannot reach the same internal host. Keeping personal browsing off the civic LAN is a deliberate parks security outcome of per-app Tunnel, not an accidental side effect of HTML Access or NSX.