
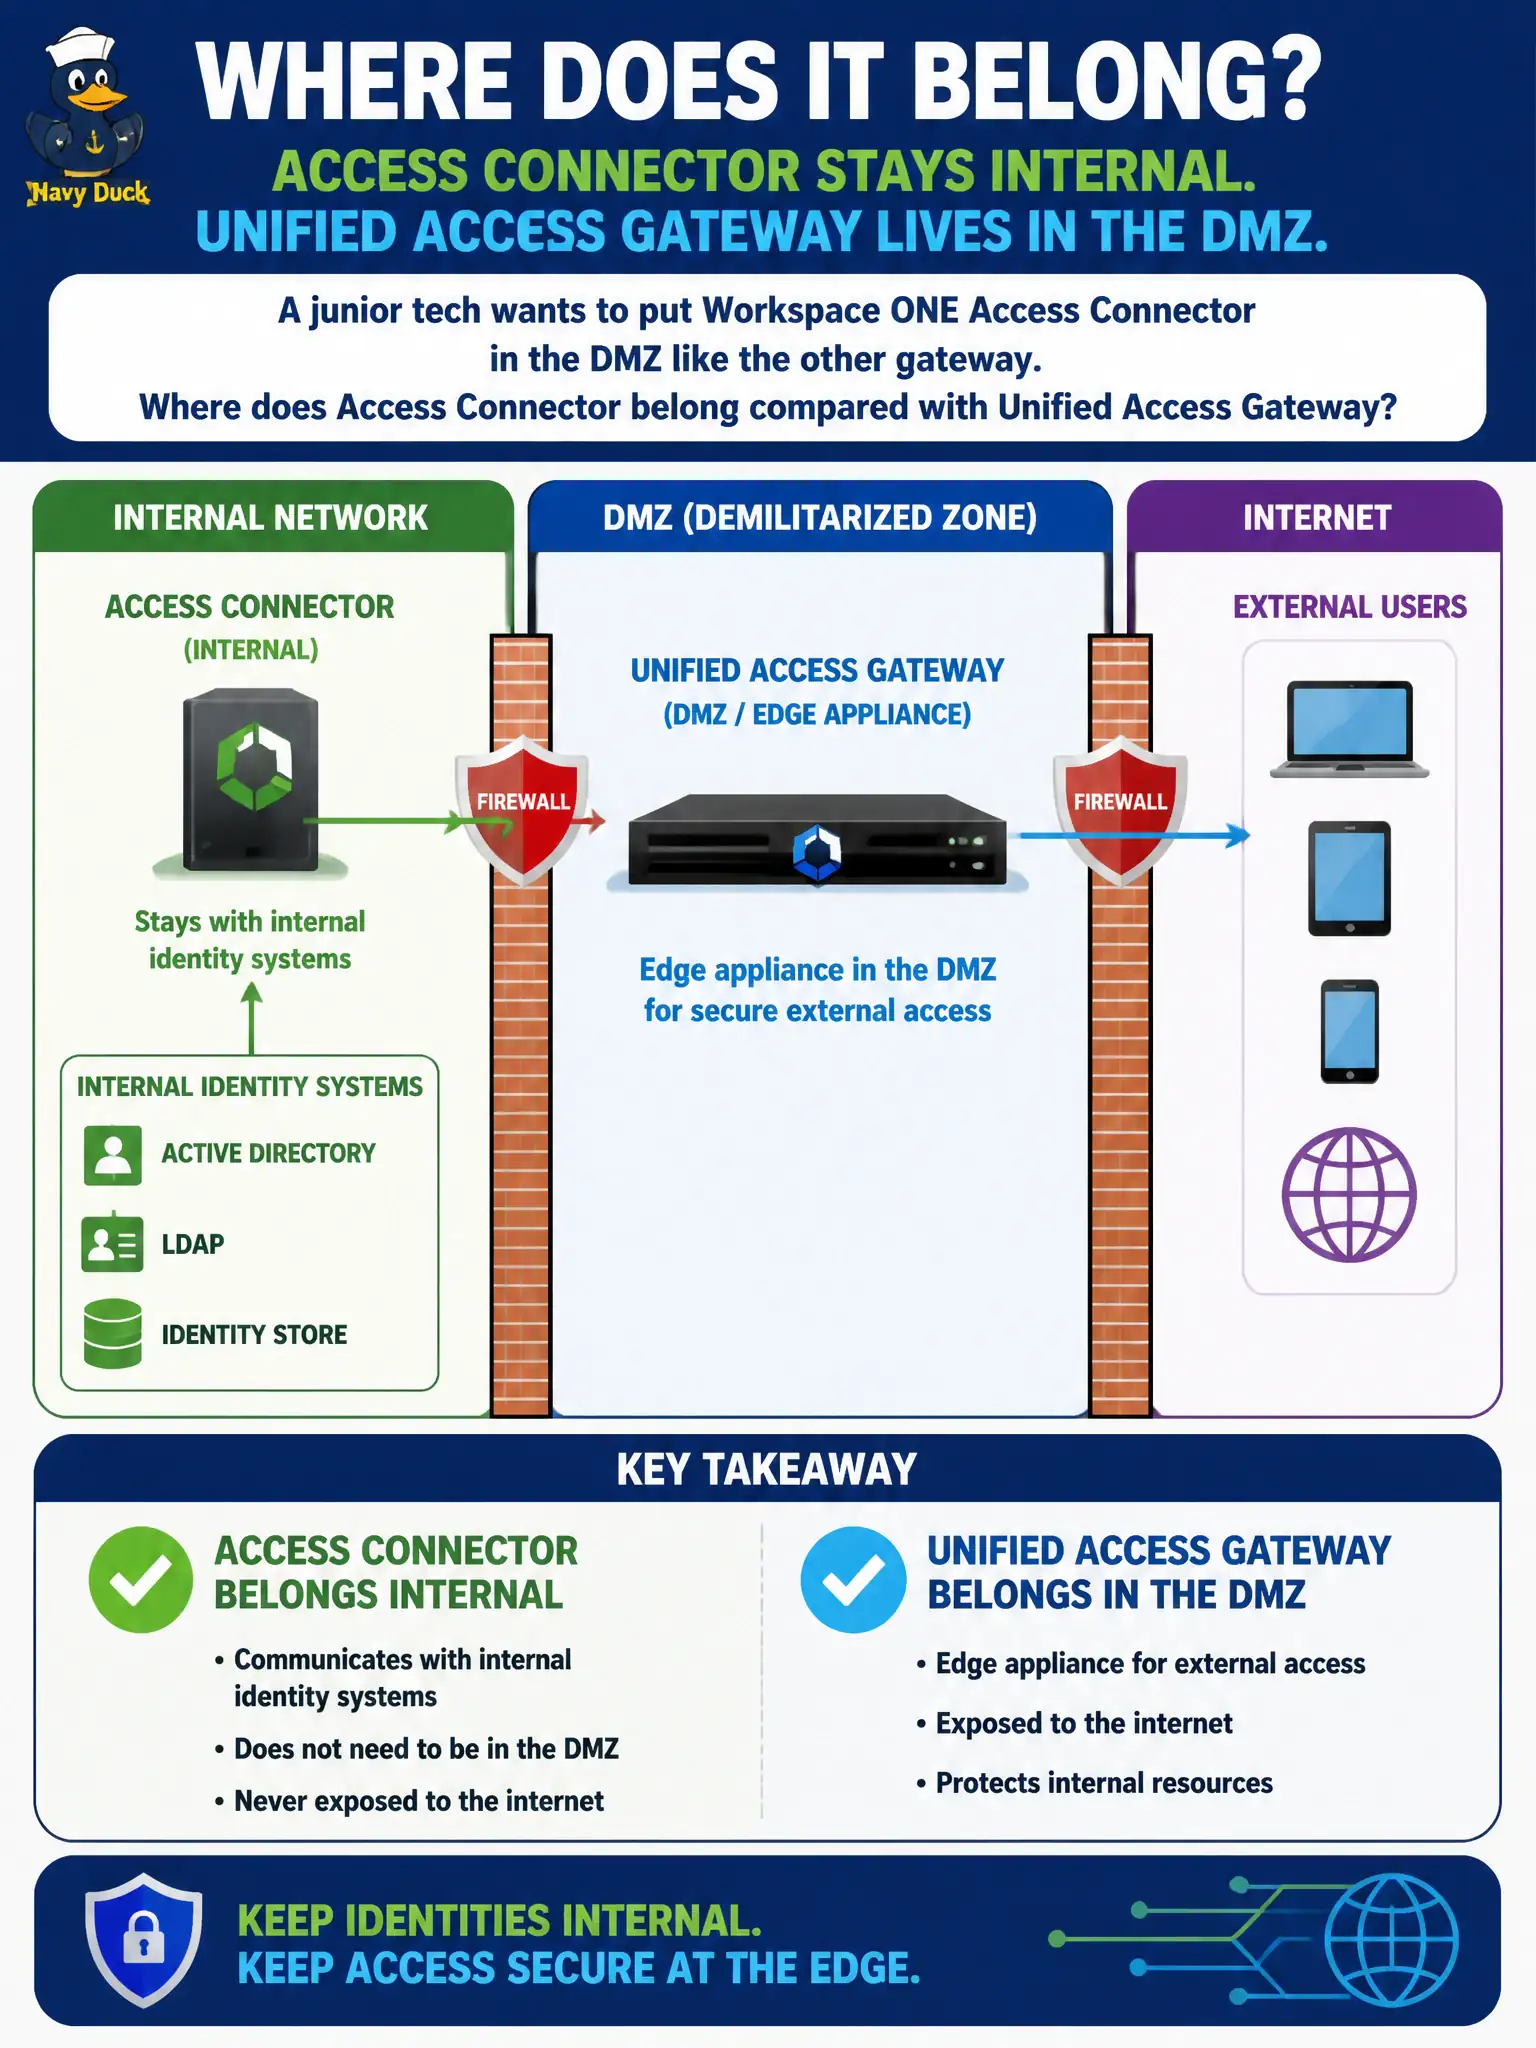
A junior tech wants to put Workspace ONE Access Connector in the DMZ like the other gateway. Where does Access Connector belong compared with Unified Access Gateway?
Select an answer to reveal the explanation.
Short Explanation
The connector lives with the badge office inside the building; UAG is the gated driveway. Do not park Access Connector in the DMZ just because both boxes have 'access' in the name.
Full Explanation
A junior tech who wants to put Workspace ONE Access Connector in the DMZ like the other gateway needs the placement rule: Access Connector stays with internal identity systems, while Unified Access Gateway is the edge appliance in the DMZ. The connector lives with the badge office inside the building; UAG is the gated driveway. Do not park Access Connector in the DMZ just because both products have “access” in the name. The claim that both appliances belong in the DMZ because any connector is an internet-facing reverse proxy fails by concept: Access Connector is not a reverse proxy and is not designed as the internet-facing edge. The claim that Access Connector replaces UAG for Horizon Blast so the DMZ host should run both roles fails because Blast/edge external access remains a UAG (and Horizon) concern; Access Connector does not assume the Blast edge role. The claim that UAG must sit next to domain controllers while Access Connector sits on guest Wi-Fi reverses intended trust boundaries: UAG belongs at the edge/DMZ, and Access Connector belongs near internal directories—not on untrusted guest wireless. Exam caveat: hybrid designs still allow outbound Connector connectivity to cloud services, but logical placement remains internal; network allow-lists and least privilege around AD matter as much as the VLAN label. Operational check: document Access Connector on an internal identity VLAN with directory reachability, place UAG in the DMZ for external Horizon/Tunnel paths, and reject a design that co-locates Access Connector on guest Wi-Fi or treats it as a Blast reverse proxy.