
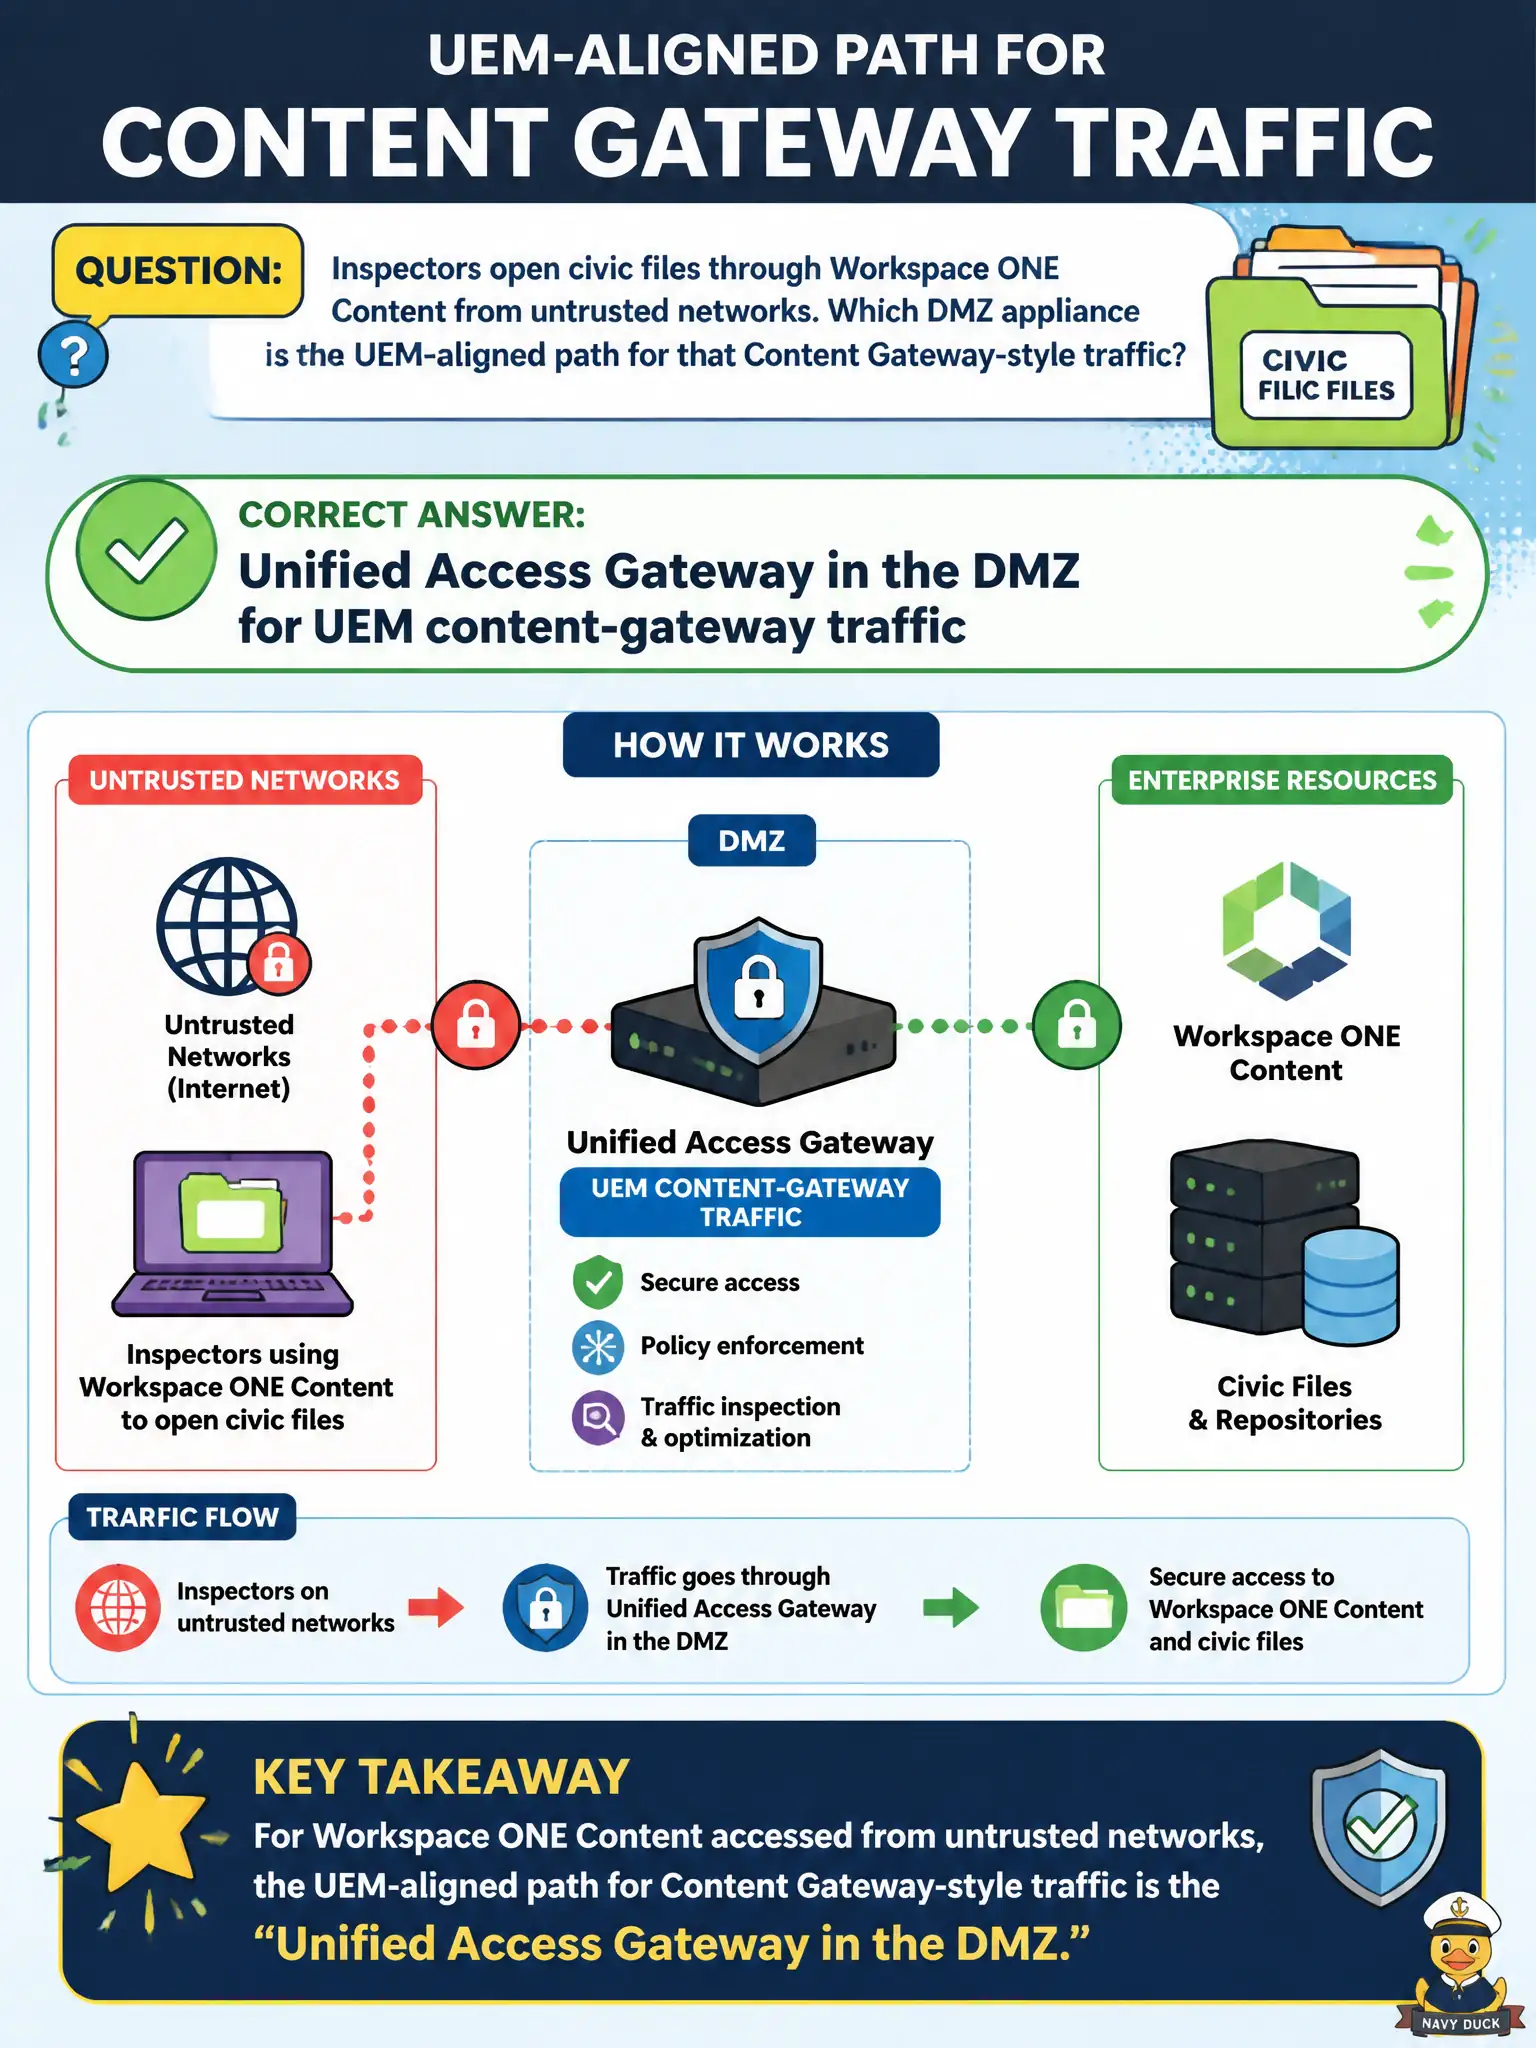
Inspectors open civic files through Workspace ONE Content from untrusted networks. Which DMZ appliance is the UEM-aligned path for that Content Gateway-style traffic?
Select an answer to reveal the explanation.
Short Explanation
Content from a coffee-shop network should knock on UAG in the DMZ, not on Connection Server hanging on the internet. vCenter and DEM are not that file door.
Full Explanation
Inspectors who open civic files through Workspace ONE Content from untrusted networks should use the UEM-aligned DMZ path: Unified Access Gateway for UEM content-gateway–style traffic. At associate depth, content access from coffee-shop, home, or other untrusted networks terminates on UAG rather than publishing internal content repositories or Connection Server directly to the internet for file access. Horizon Connection Server published on the internet is the wrong edge for UEM Content and bypasses the UAG model for that mobile content traffic. vCenter Server on the management VLAN manages compute and VM inventory and is not the content gateway for inspector documents. Dynamic Environment Manager console on a file share personalizes Windows Horizon sessions and does not terminate Content Gateway traffic from phones. Exam caveat: Content Gateway or UEM content edge configuration on UAG is distinct from the Horizon Blast edge even when both services run on UAG appliances in the same civic DMZ. Operational check: from an untrusted network, open a test document via Workspace ONE Content through UAG, confirm the session hits the DMZ content edge in logs, and verify Connection Server and vCenter remain unreachable from that same untrusted path.