
The permitting app on phones uses per-app VPN into civic systems. Which appliance terminates that UEM Tunnel edge in the DMZ?
Select an answer to reveal the explanation.
Short Explanation
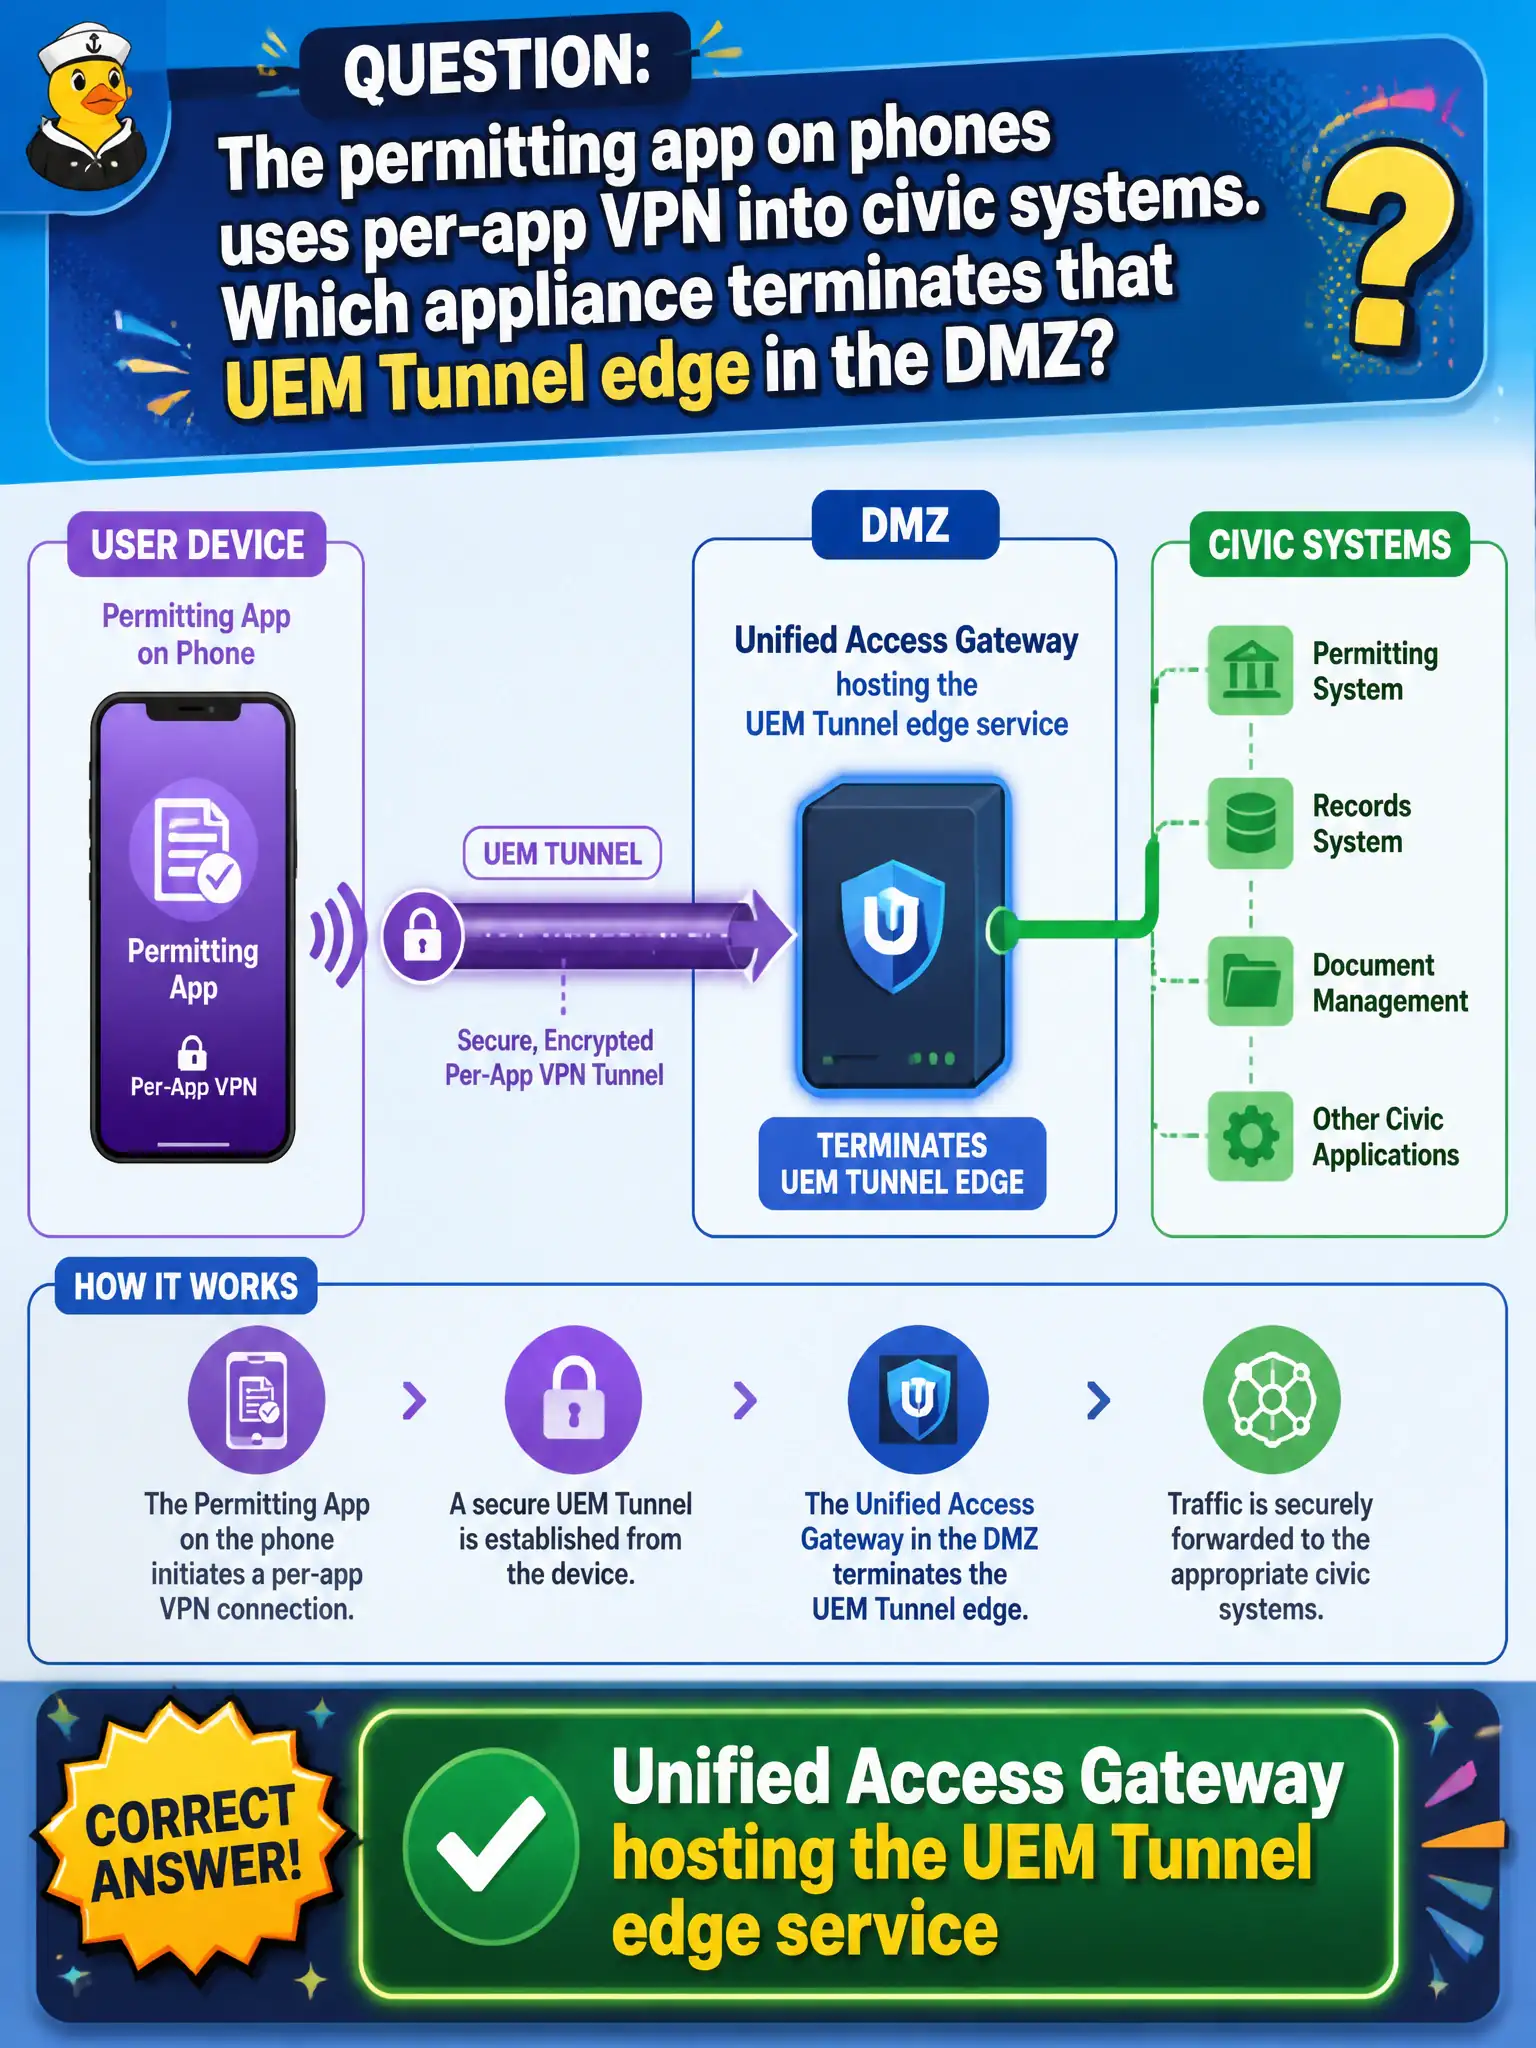
UAG wears two hats. This hat is the UEM Tunnel door in the DMZ for the permitting app, not the Horizon Blast door. Cloud Connector and App Volumes are not VPN concentrators.
Full Explanation
When the permitting app on phones uses per-app VPN into civic systems, the appliance that terminates that UEM Tunnel edge in the DMZ is Unified Access Gateway hosting the UEM Tunnel edge service. UAG is the associate-depth DMZ platform for Tunnel so managed mobile apps reach internal permitting APIs without exposing the whole municipal LAN or publishing every backend on the internet. Horizon Connection Server is the broker for desktop and application sessions; it is not the BLAST broker acting as a VPN concentrator for Android per-app Tunnel. AirWatch Cloud Connector integrates SaaS UEM with on-premises directory and enterprise systems such as Active Directory and certificate authorities; it is not the per-app VPN concentrator. App Volumes Manager assigns Windows packages to desktops and is not a mobile VPN terminator. Exam caveat: the same UAG platform can also host Horizon edge services; role selection on the appliance matters—configure Tunnel for UEM per-app VPN versus Blast and XML-API for Horizon remote desktops. Operational check: point the permitting app’s Tunnel profile at the UAG Tunnel edge, confirm traffic lands on UAG in the DMZ from field tablets, verify Connection Server and Cloud Connector are not in that VPN data path, and test API reachability only while Tunnel is up.