
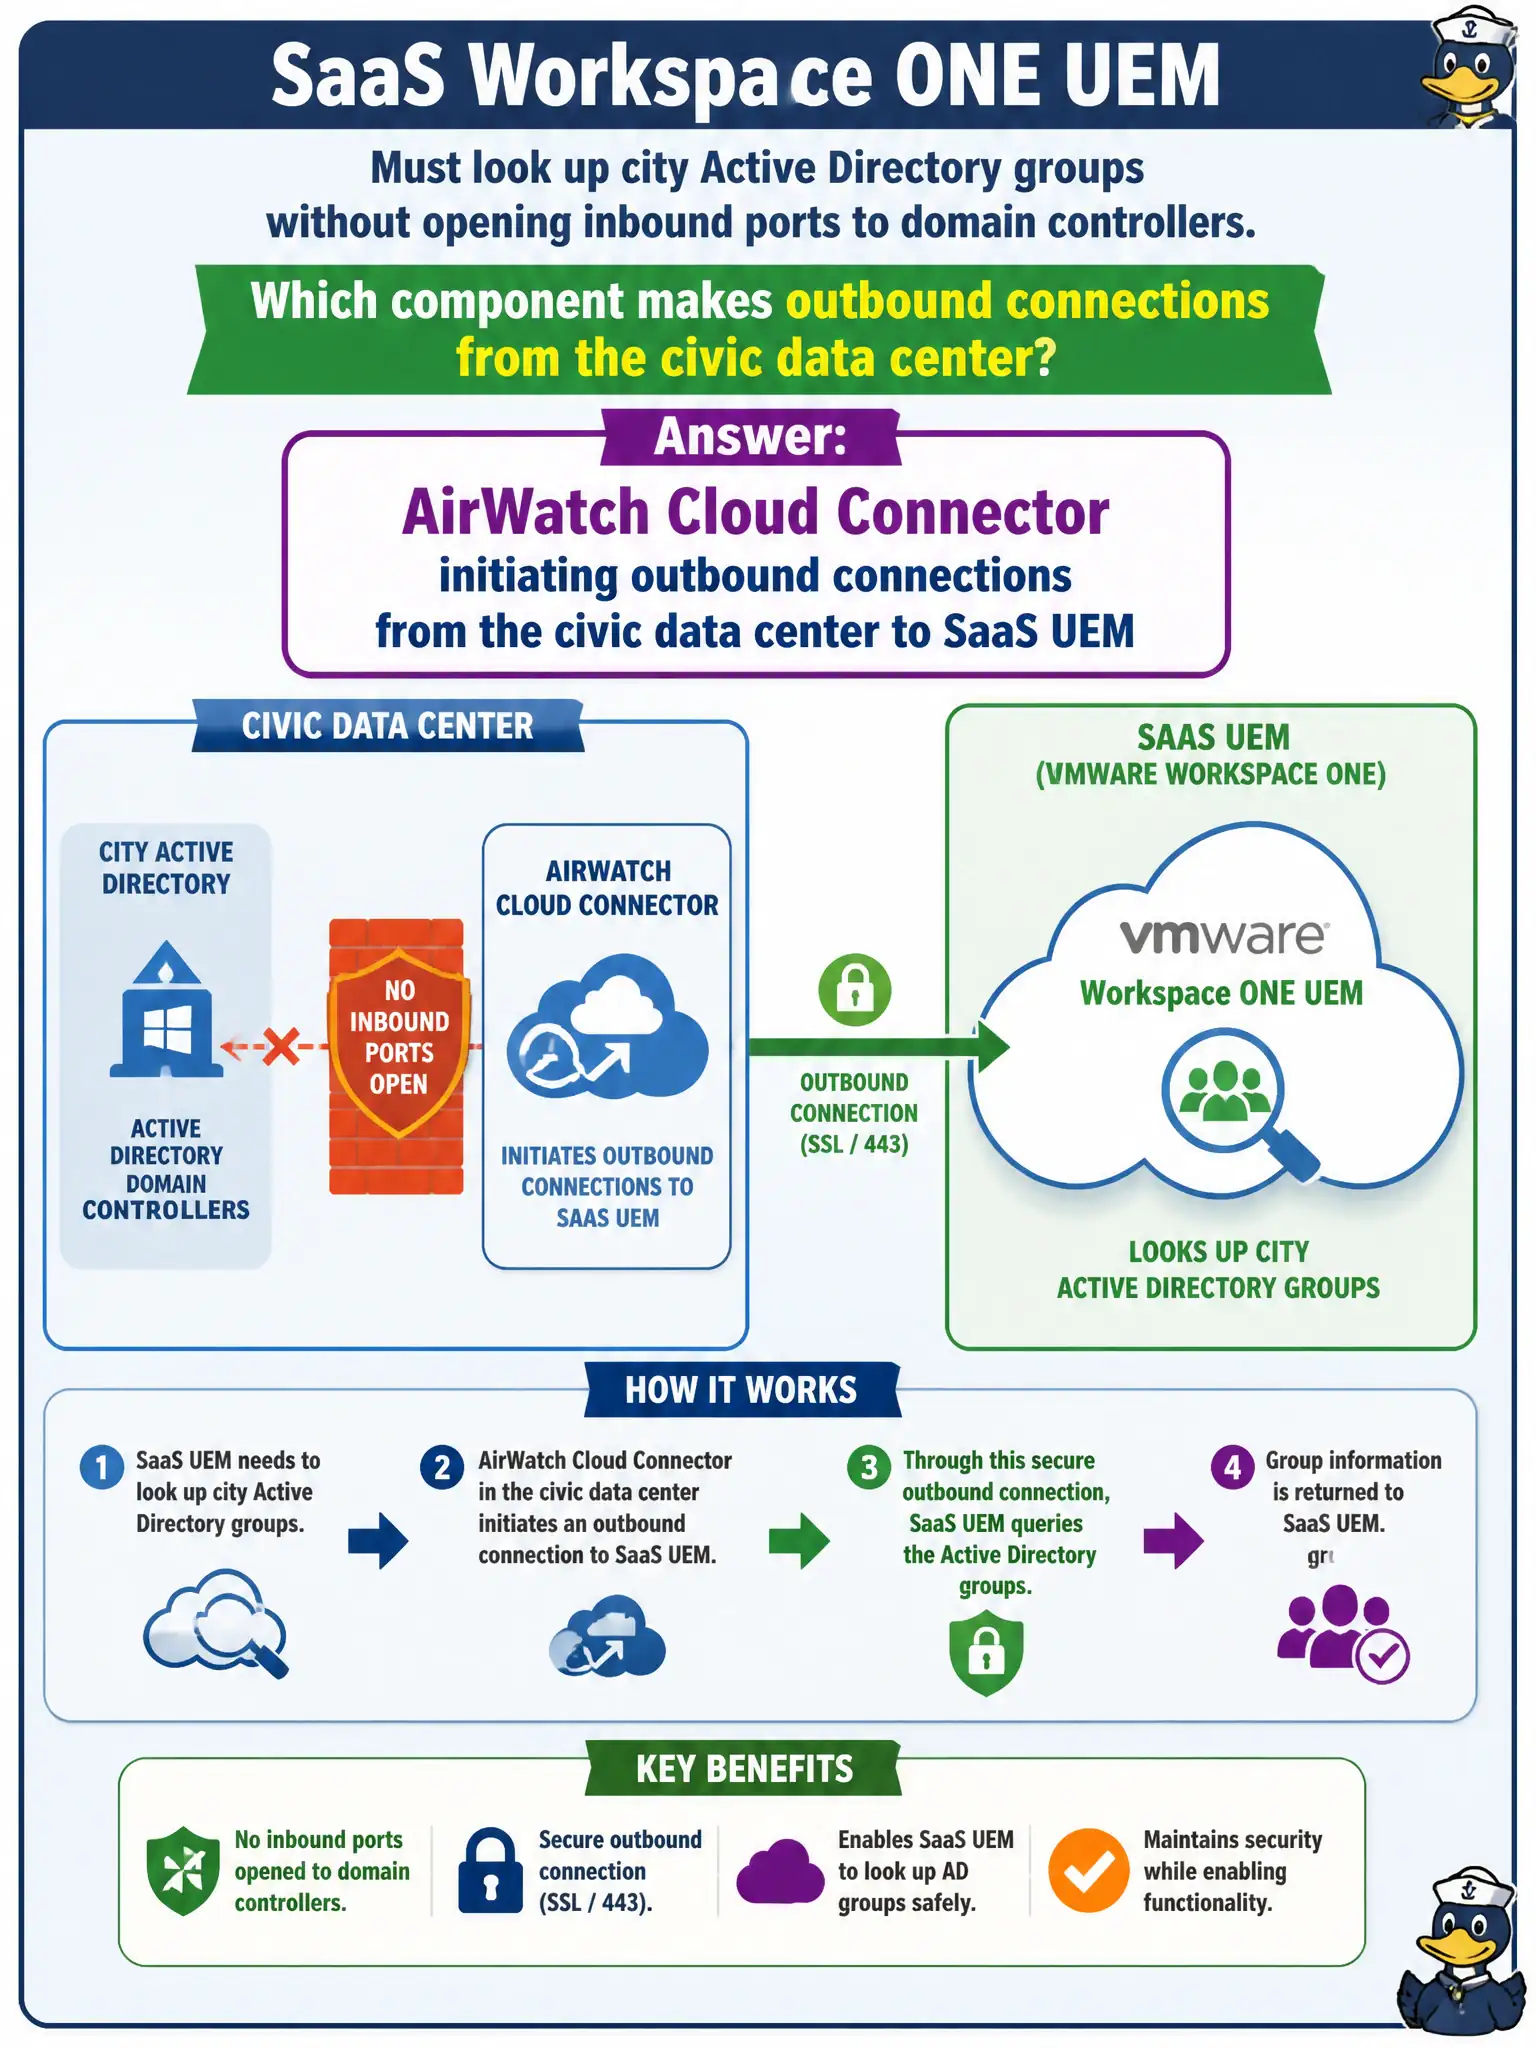
SaaS Workspace ONE UEM must look up city Active Directory groups without opening inbound ports to domain controllers. Which component makes outbound connections from the civic data center?
Select an answer to reveal the explanation.
Short Explanation
Think of AirWatch Cloud Connector as a city courier who walks out to the SaaS lobby; nobody punches a hole into the records vault. UAG BLAST, Horizon Cloud Connector, and NSX T0 are other couriers with other packages.
Full Explanation
SaaS Workspace ONE UEM that must look up city Active Directory groups without opening inbound ports to domain controllers relies on AirWatch Cloud Connector (Workspace ONE UEM Cloud Connector) initiating outbound connections from the civic data center to the SaaS tenant. The connector sits on premises, reaches out to the cloud, and brokers directory and related enterprise integrations so Active Directory remains internal while municipal groups still appear for enrollment and assignment. Unified Access Gateway as a BLAST proxy in the DMZ terminates Horizon remote display and related Horizon edge traffic; it is not the outbound directory bridge for SaaS UEM. Horizon Cloud Connector registers Horizon Cloud pods or related control-plane links and is not the AirWatch directory courier. NSX Edge T0 advertising LDAP as an overlay service confuses network virtualization with the UEM connector model and is not how civic AD stays off the internet for Workspace ONE. Exam caveat: Cloud Connector health affects directory sync and some on-prem integrations; it is not required for every already-enrolled device’s basic SaaS check-in path. Operational check: confirm Cloud Connector shows healthy outbound connectivity, look up a new civic AD group in SaaS UEM without any inbound 443 rule to domain controllers, and verify firewall logs show outbound connector traffic rather than internet-sourced LDAP to AD.