
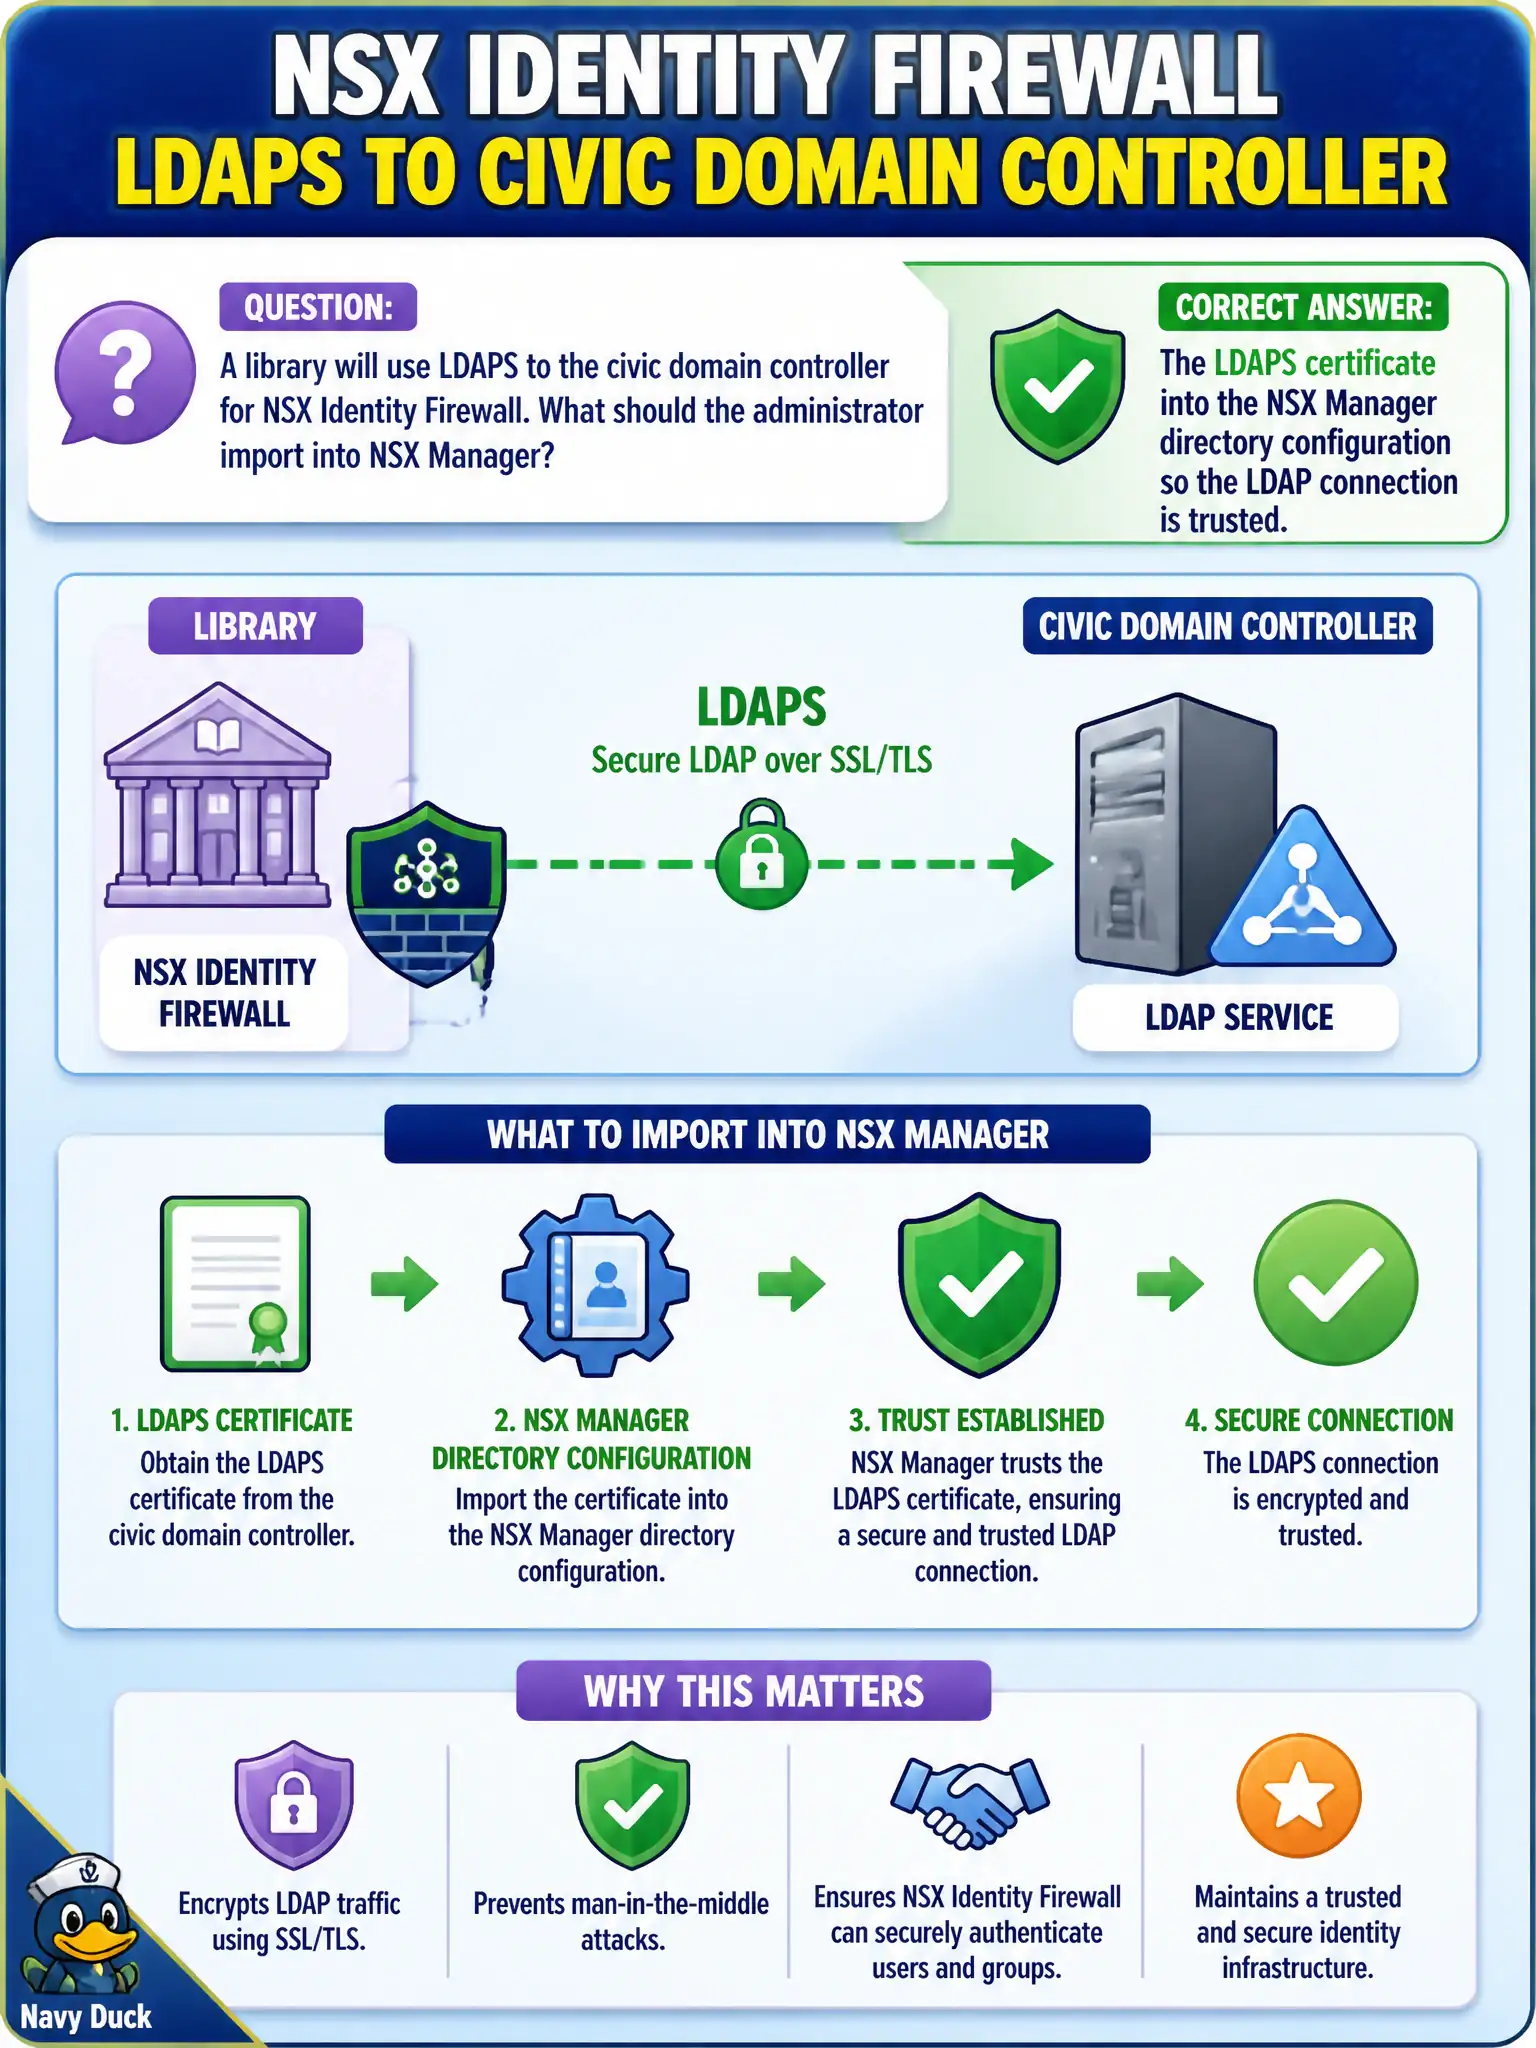
A library will use LDAPS to the civic domain controller for NSX Identity Firewall. What should the administrator import into NSX Manager?
Select an answer to reveal the explanation.
Short Explanation
LDAPS is a locked tunnel to the civic DC, and NSX Manager needs the DC's certificate on its key ring. Import that cert in the directory config. Carbon Black sensor certs and UEM profiles are not that trust store.
Full Explanation
A library using LDAPS to the civic domain controller for NSX Identity Firewall must import the LDAPS certificate into the NSX Manager directory configuration so the LDAP connection is trusted. Without certificate trust, secure directory bind fails and IDFW groups will not sync reliably.
A Carbon Black Cloud sensor certificate does not establish NSX Manager directory trust. A Workspace ONE UEM profile that trusts LDAPS only inside the Manager guest OS is not the NSX directory configuration import. Claiming NSX-T 3.x directory connections are plaintext LDAP only is false when LDAPS is in use and expected.
Exam caveat: LDAPS requires certificate trust in the NSX directory config—do not confuse with unrelated product certs.
Operational check: import the LDAPS certificate on NSX Manager, test directory connection, sync library IDFW groups, and document certificate renewal in the identity runbook.
LDAPS certificate import is library PKI hygiene for IDFW. Track certificate expiry beside other civic IdP certs, test reconnect after renewal, and forbid plaintext LDAP “temporary” exceptions on Managers that hold security policy for patron-facing systems. Keep the imported LDAPS certificate thumbprint and a successful directory test with the identity change record so the next on-call engineer can renew trust without rediscovering Manager directory settings under pressure.