
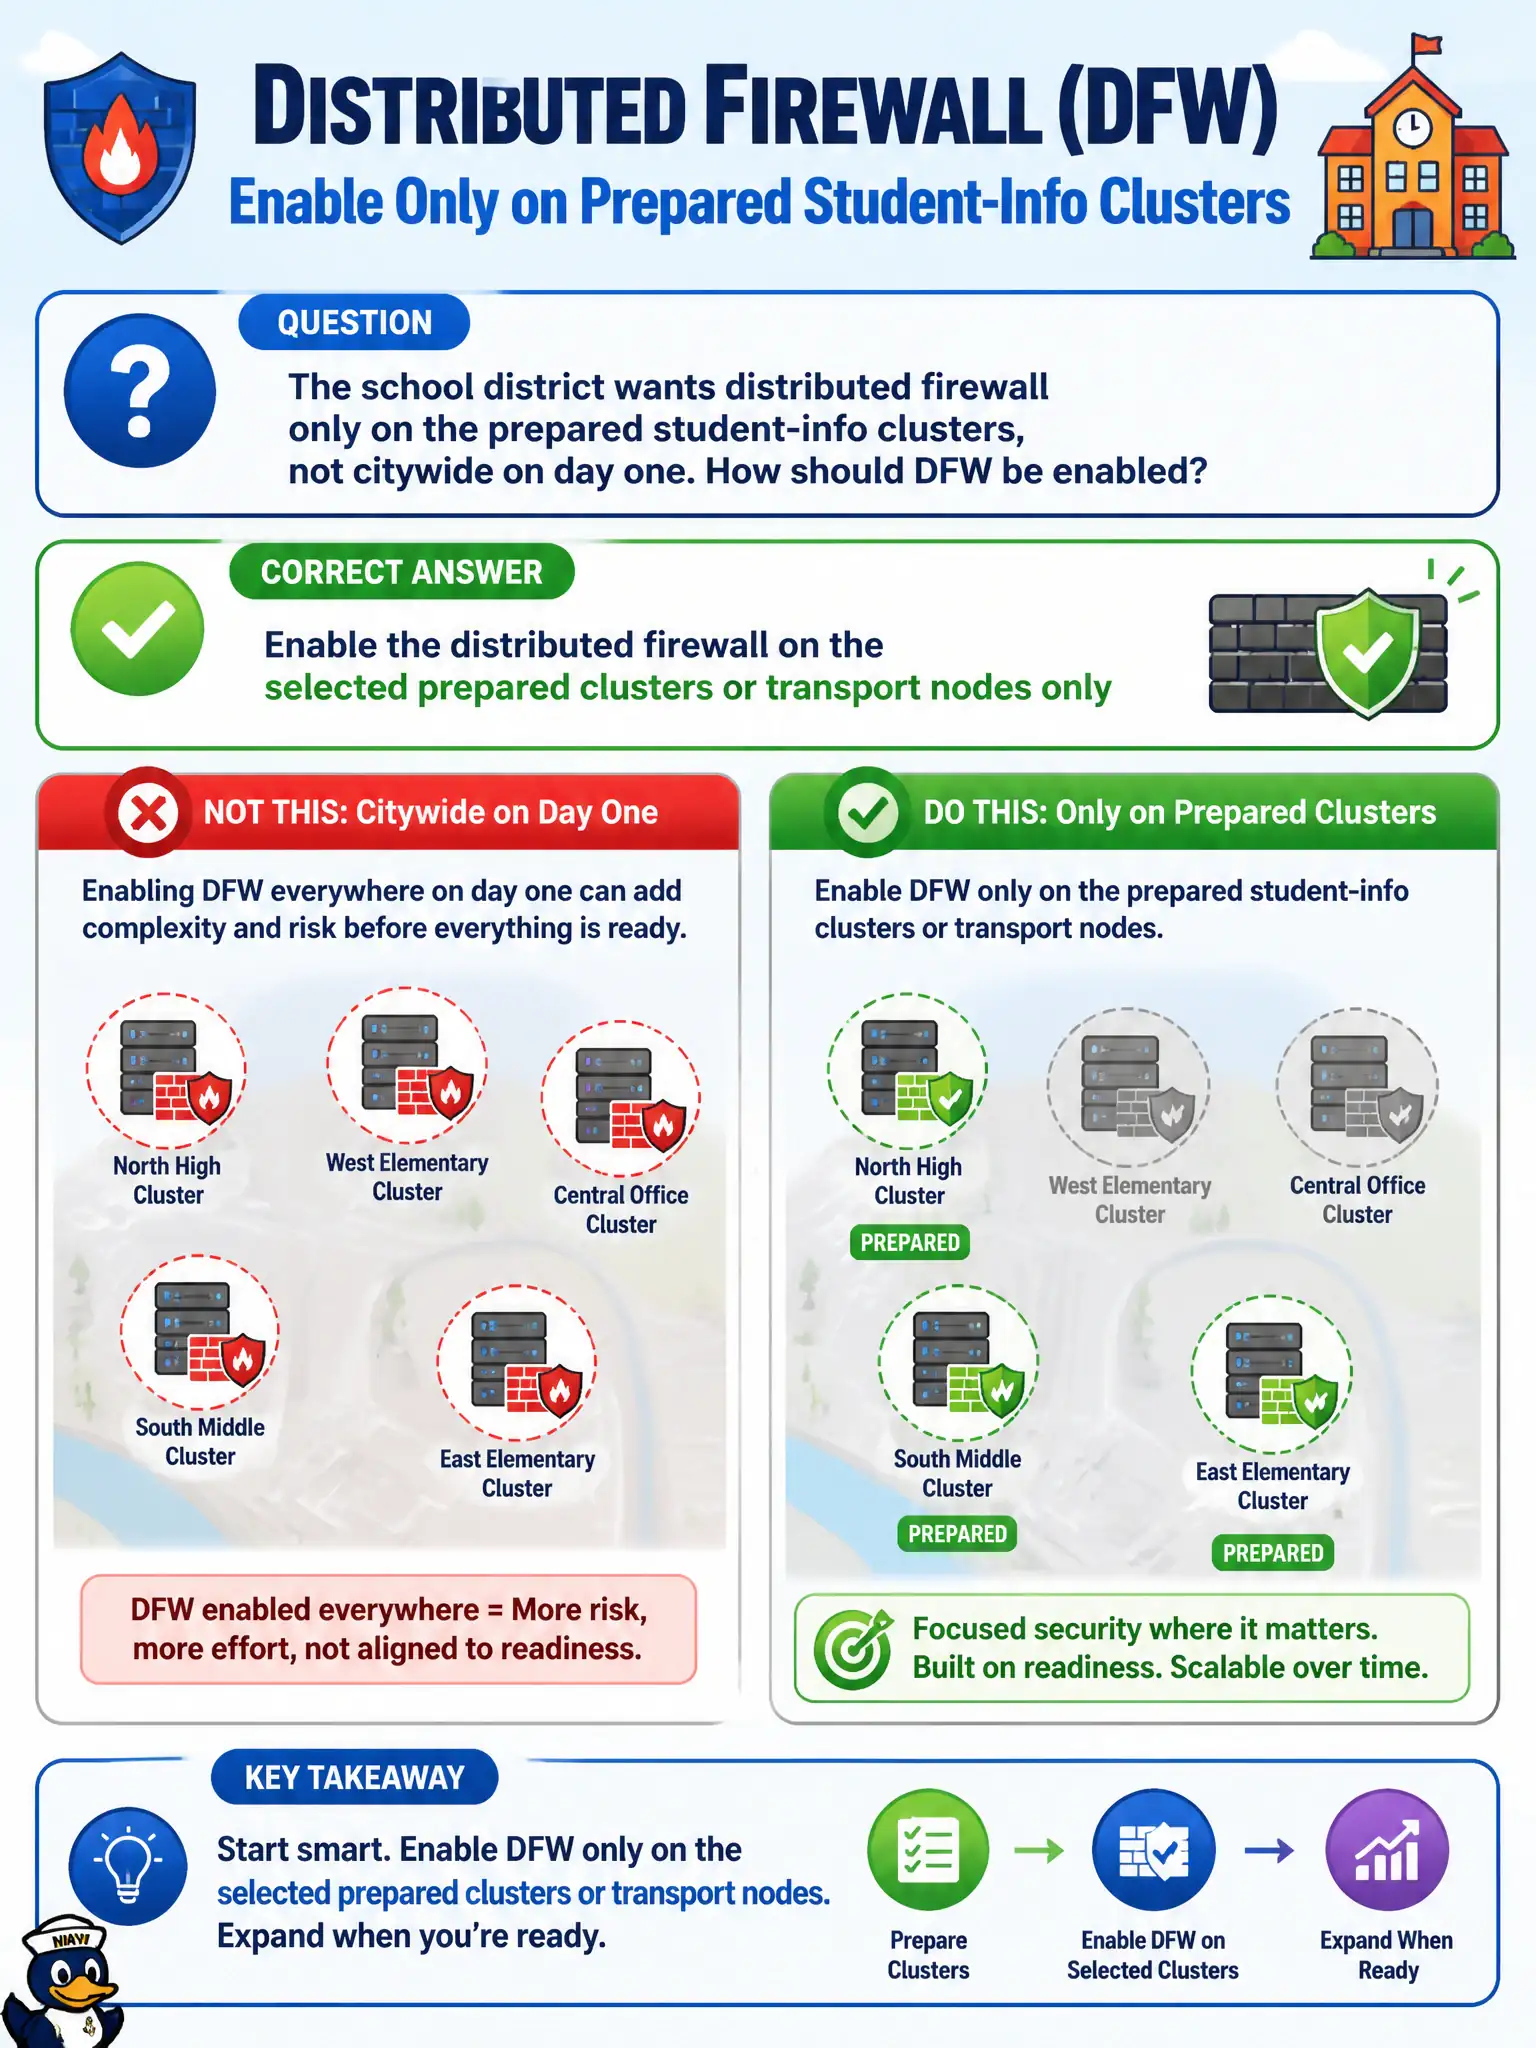
The school district wants distributed firewall only on the prepared student-info clusters, not citywide on day one. How should DFW be enabled?
Select an answer to reveal the explanation.
Short Explanation
You do not flip every breaker in city hall to light one classroom. Turn DFW on only for the prepared student-info clusters so the rest of the civic estate stays out of the first cutover.
Full Explanation
School-district Distributed Firewall should be enabled only on the selected prepared student-info clusters or transport nodes when the first cutover must not go citywide. Scoped enablement keeps unfinished civic clusters out of the blast radius while student-info hosts that are actually prepared begin enforcing policy.
Enabling DFW on every cluster in every civic vCenter at once overscopes day-one risk. Enabling DFW in Carbon Black Cloud skips NSX host preparation and is not NSX distributed firewall. Publishing a Workspace ONE Access policy to the clusters does not enable NSX DFW on transport nodes.
Exam caveat: preparation plus scoped enablement beats a citywide flip when only one application domain is ready.
Operational check: confirm student-info transport nodes are Up, enable DFW only on those nodes or clusters, validate pilot allow/deny, and keep other civic clusters disabled until their preparation checklist is green.
Scoped DFW enablement is a classroom lighting circuit, not the whole municipal grid. After enabling only student-info prepared nodes, deliberately confirm neighboring civic clusters still show DFW disabled, run allow/deny tests on student-info only, and gate any expansion on a written preparation checklist signed by school and city platform owners.