
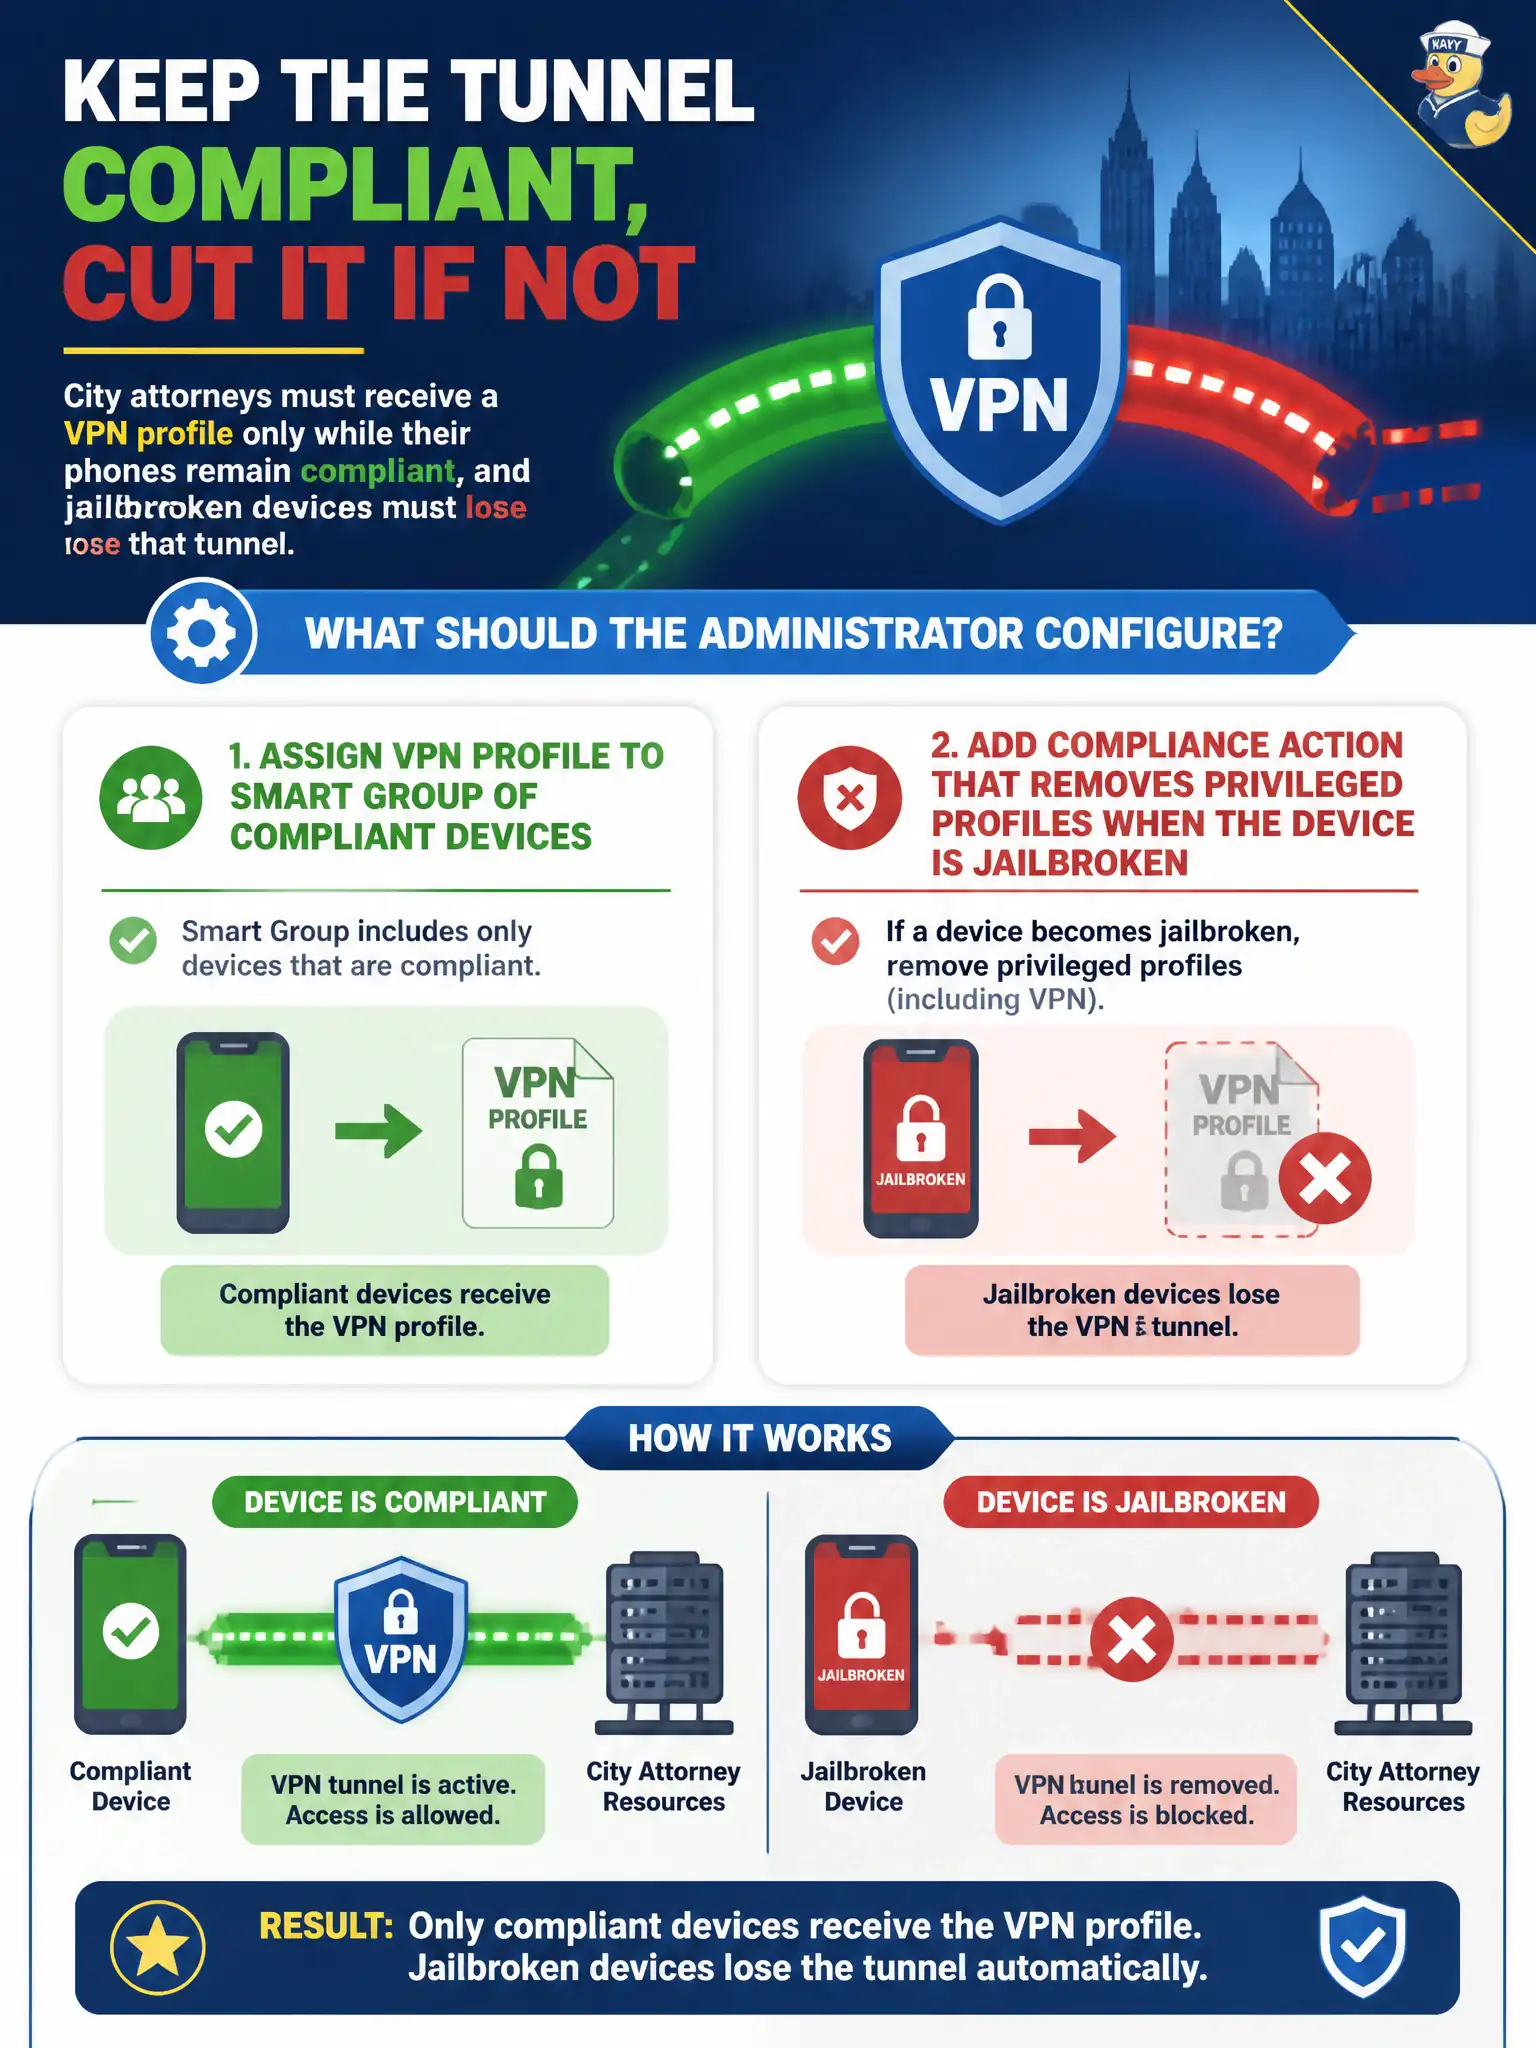
City attorneys must receive a VPN profile only while their phones remain compliant, and jailbroken devices must lose that tunnel. What should the administrator configure?
Select an answer to reveal the explanation.
Short Explanation
A privileged VPN is a badge that should snap off the moment the phone is jailbroken, not a sticker you leave on forever. Tie the VPN profile to compliant devices, then let compliance yank it when posture fails. A forever-on profile keeps the tunnel up on the exact phones you wanted to cut off.
Full Explanation
City attorneys must receive a VPN profile only while phones remain compliant, and jailbroken devices must lose that tunnel. Assign the VPN profile to a smart group of compliant devices and add a compliance action that removes privileged profiles when the device is jailbroken—a privileged VPN is a badge that should snap off when posture fails. Publishing a forever-on VPN profile to All Devices and ignoring compliance fails by concept because the tunnel stays available on the exact phones you intended to cut off when jailbroken. Adding the VPN FQDN to a Carbon Black Cloud permission allow list fails because CBC permissions govern process execution, not UEM profile entitlement tied to compliance. Creating an NSX-T distributed firewall rule that permits UDP 500 from every attorney phone regardless of MDM state fails because DFW cannot evaluate UEM jailbreak compliance or remove MDM VPN profiles. Exam caveat: privileged VPN delivery is compliance-scoped UEM profile assignment plus remediation actions—not forever-on All Devices, not CBC allows, not NSX regardless of MDM state. Operational check: confirm compliant attorney phones receive the VPN profile, mark a test device non-compliant or jailbroken in lab, confirm the privileged profile is removed, and verify All Devices forever-on was not used. Document the compliance action chain in the city attorney mobile standard so legal hold scenarios still honor jailbreak revocation.