
A county assessor line-of-business tax application is terminated by Carbon Black Cloud. What is the correct policy change?
Select an answer to reveal the explanation.
Short Explanation
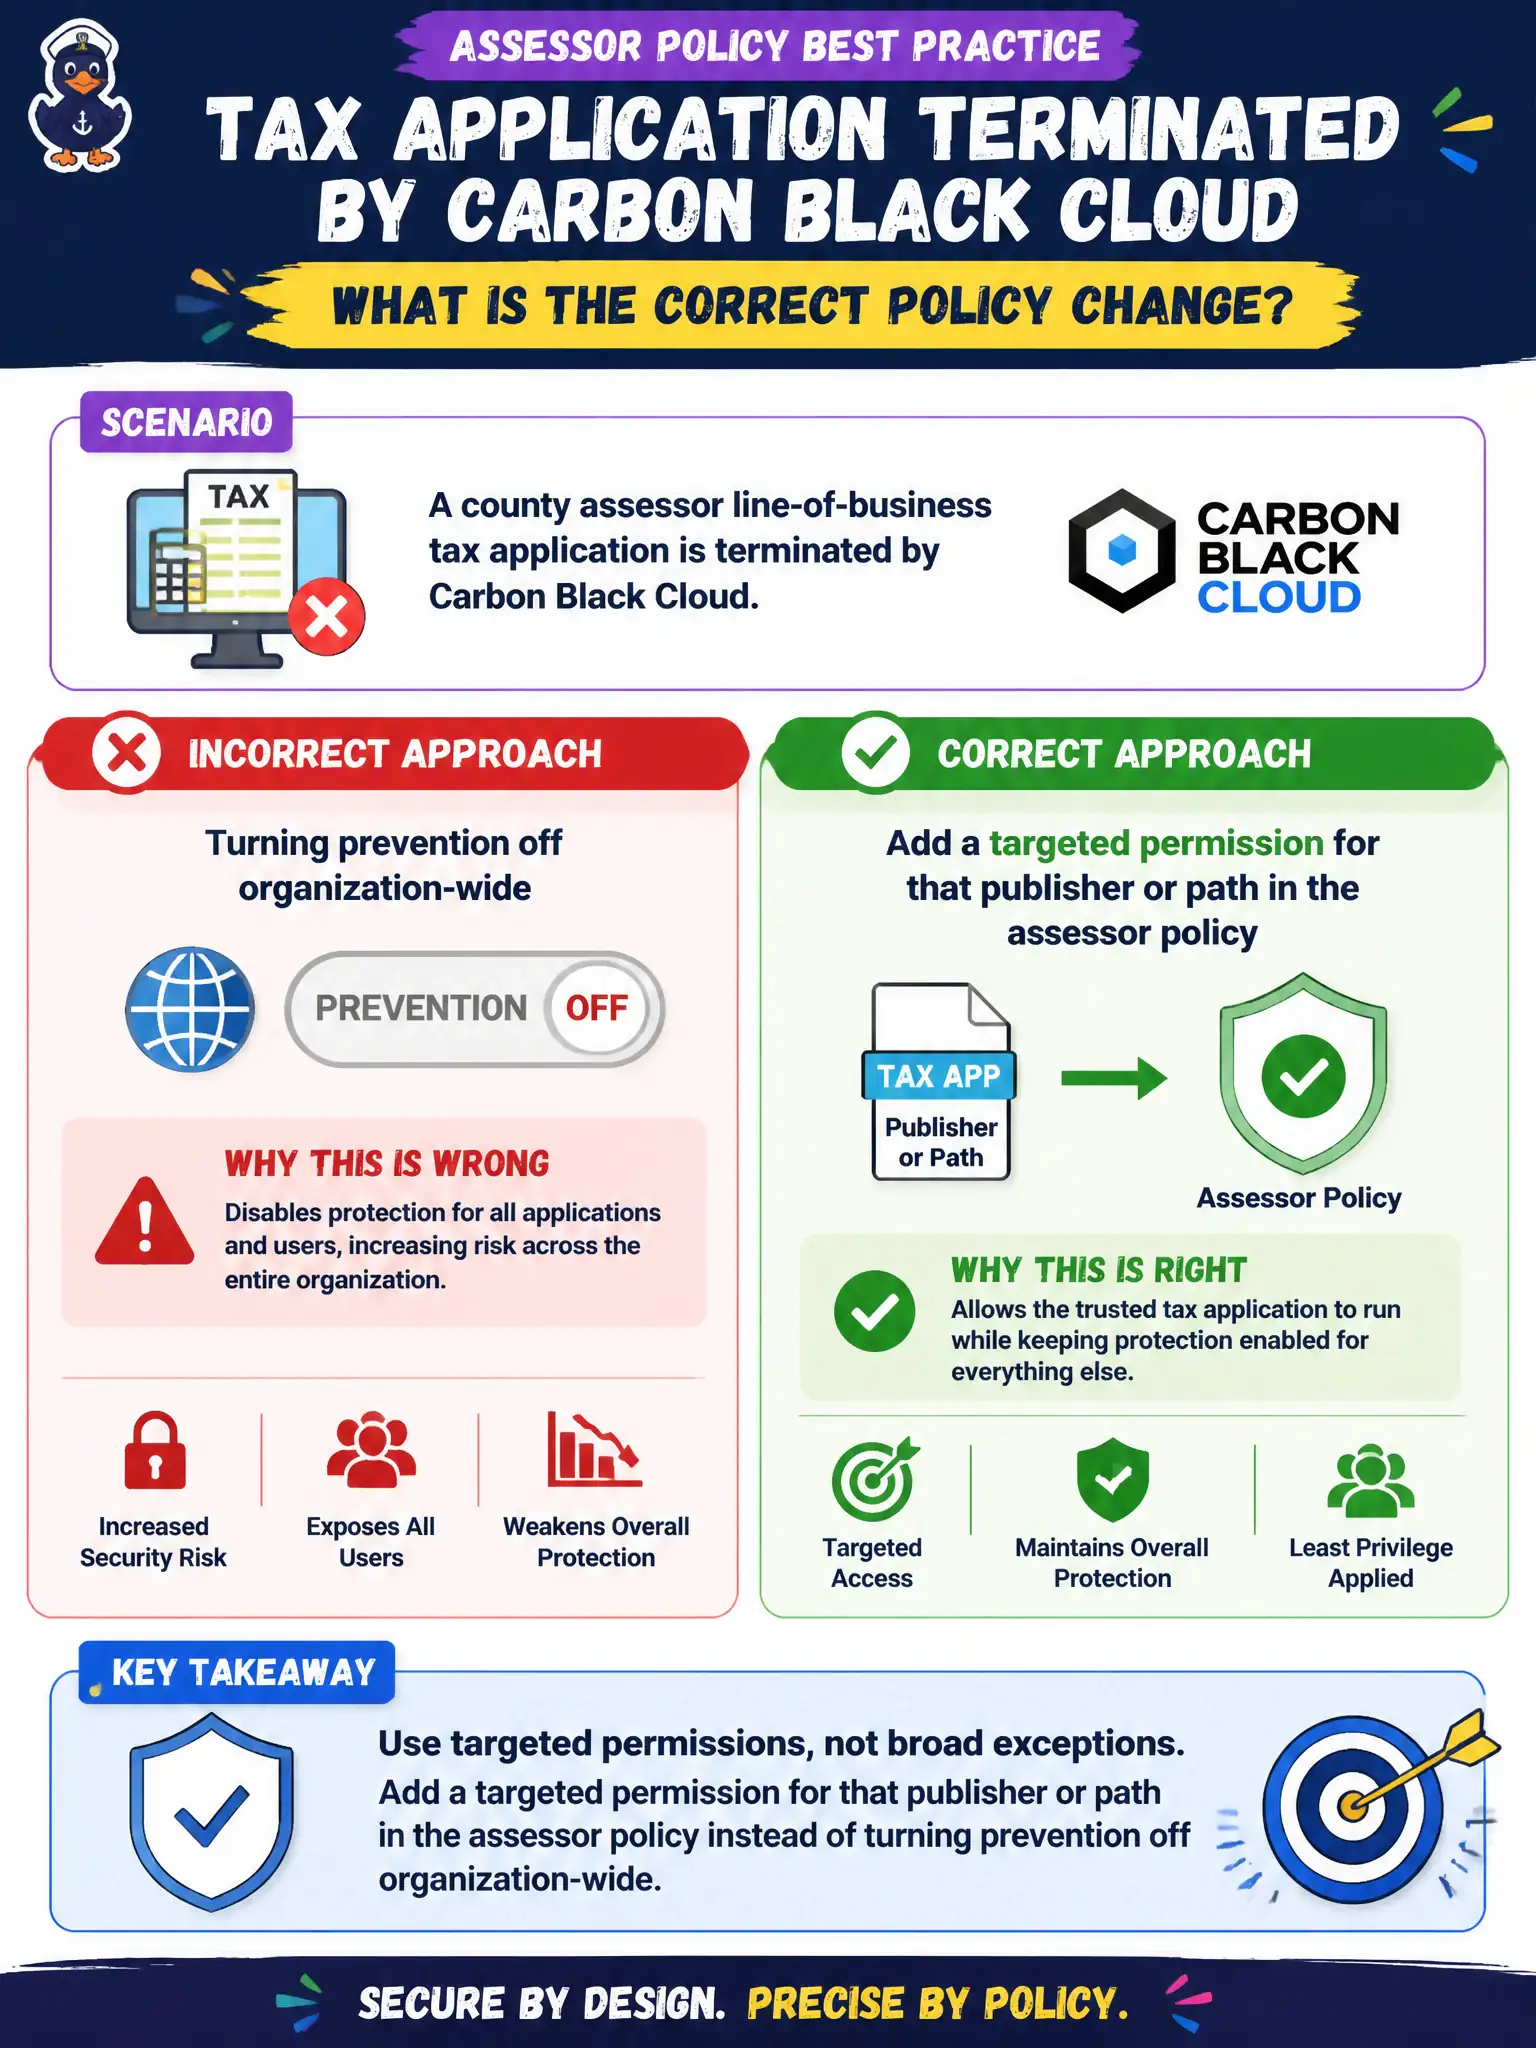
One cranky tax app is not a reason to disarm the whole city. Put a scoped permission in the assessor policy and leave prevention on for everyone else.
Full Explanation
When a county assessor line-of-business tax application is terminated by Carbon Black Cloud, add a targeted permission for that publisher or path in the assessor policy instead of turning prevention off organization-wide. One cranky tax app is not a reason to disarm the whole city. Turning prevention off for every sensor in the city tenant fails by concept because a local application conflict does not justify tenant-wide disarmament. Uninstalling the sensor from assessor PCs until tax season ends fails because removing the sensor abandons endpoint protection rather than scoping an allow. Deleting the Standard policy so no endpoint can terminate processes fails because destroying Standard is not a scoped permission and harms default coverage for unmatched sensors. Exam caveat: remediate false blocks with targeted policy permissions or allows—not org-wide prevention off, sensor removal, or deleting Standard. Operational check: add the publisher or path permission to the assessor policy, confirm the tax app launches, verify other city groups still enforce prevention, and review recent terminations for scope creep. Record the permission rationale in the assessor change ticket so the next CBC policy merge does not drop the exception silently.