
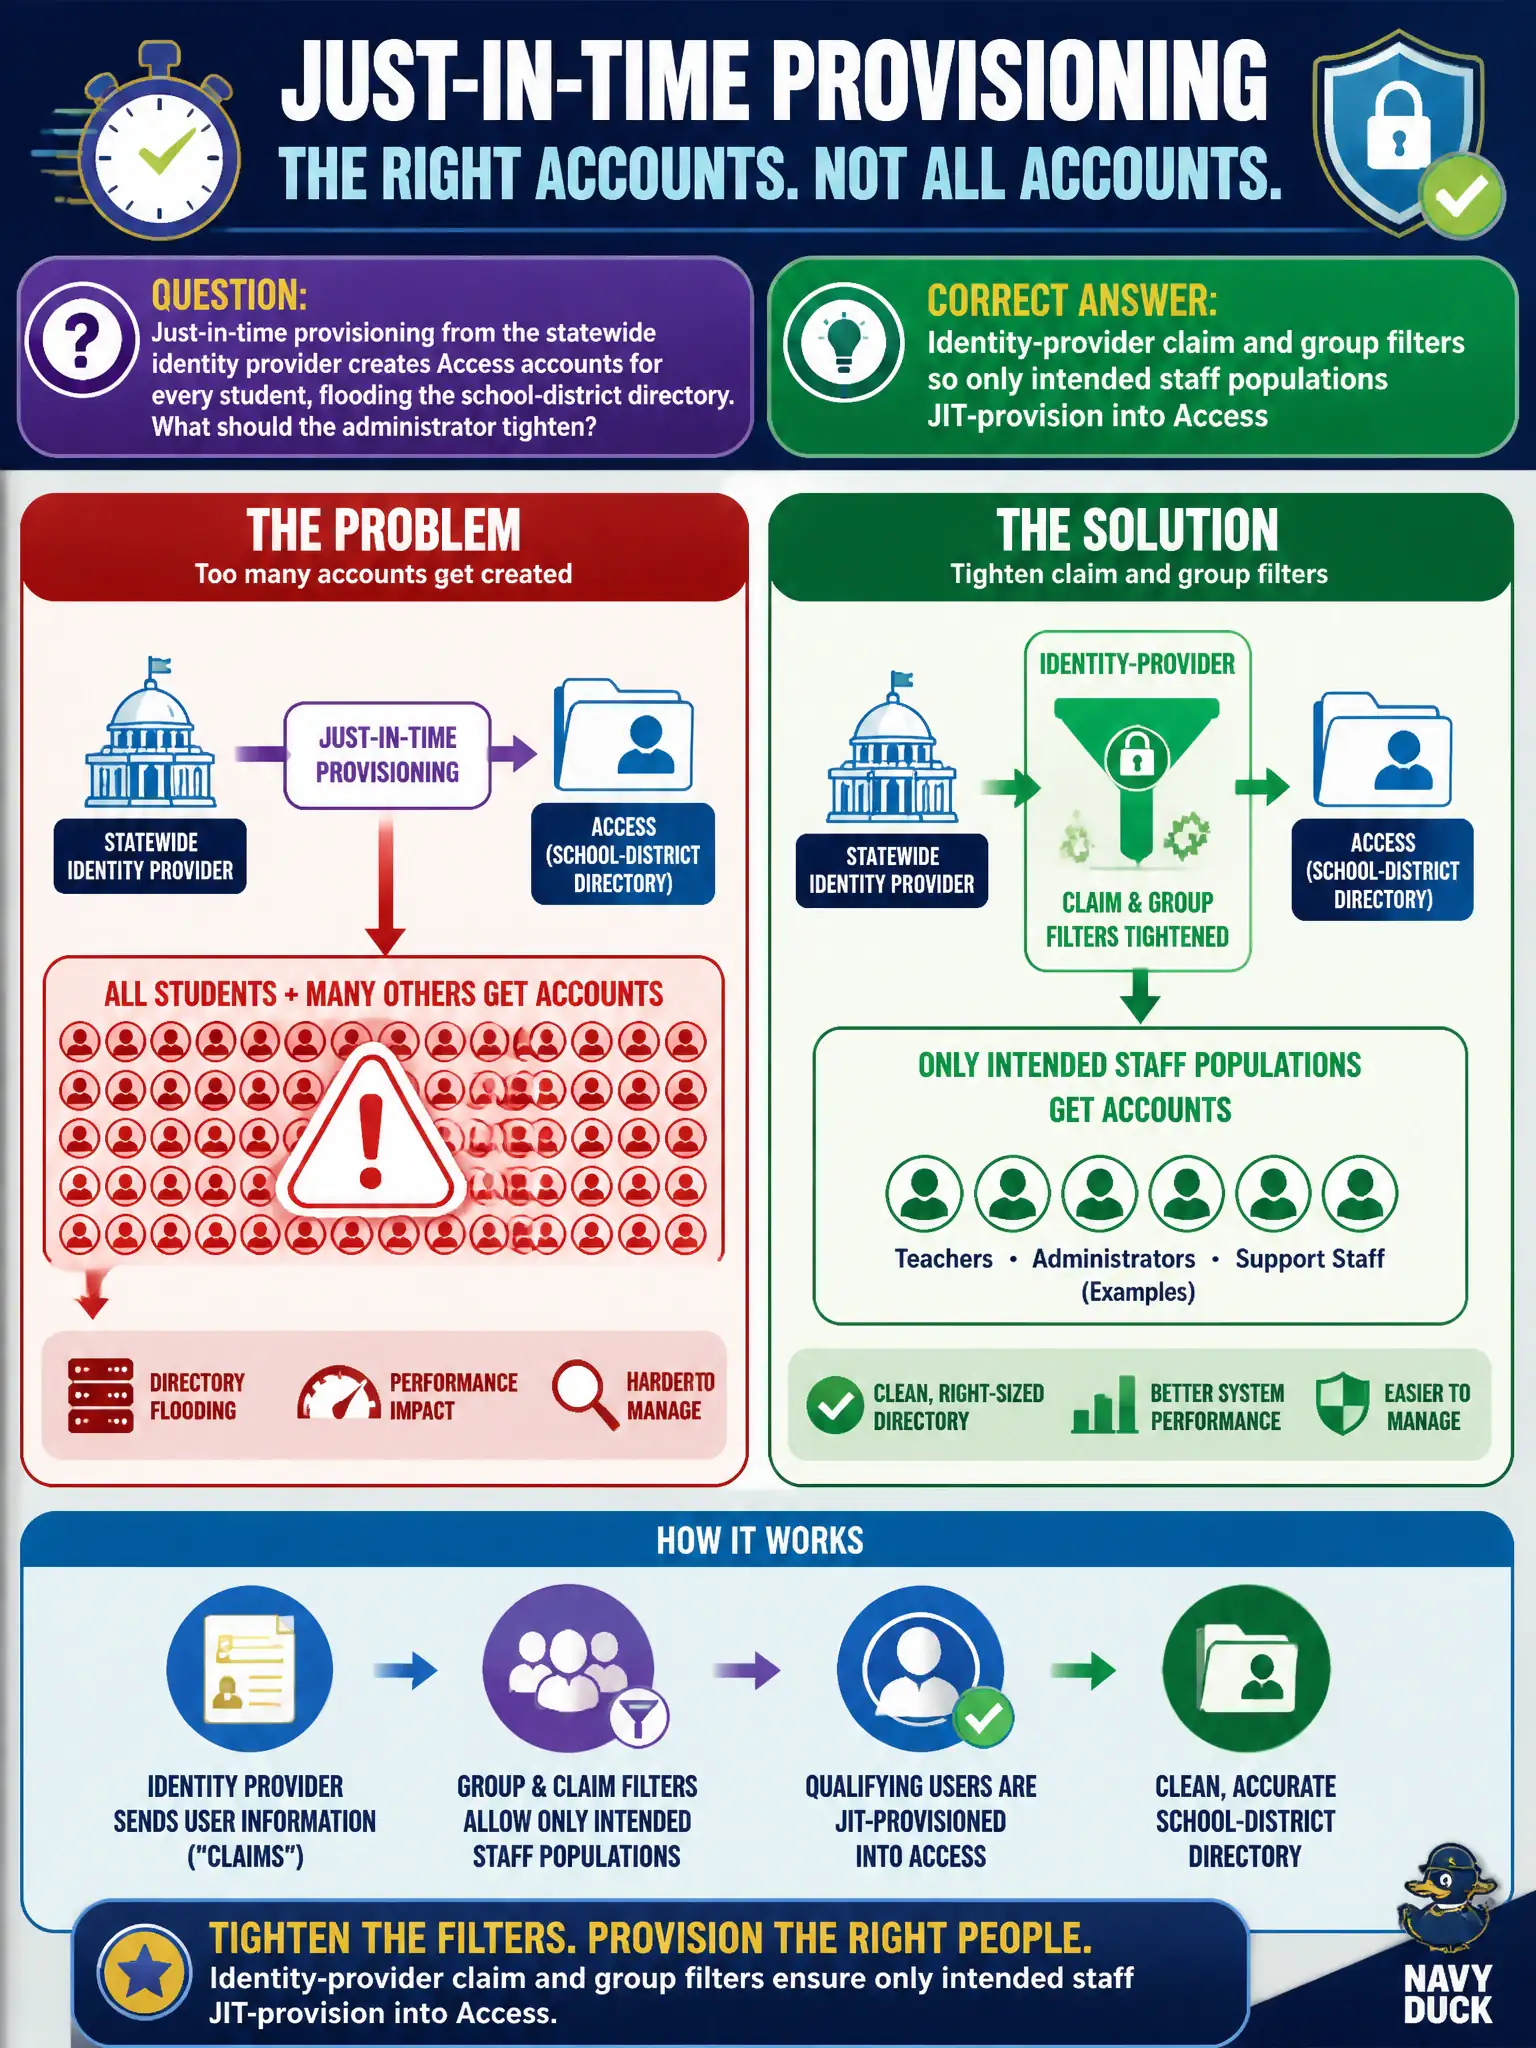
Just-in-time provisioning from the statewide identity provider creates Access accounts for every student, flooding the school-district directory. What should the administrator tighten?
Select an answer to reveal the explanation.
Short Explanation
JIT should not photocopy the entire student roster into Access. Filter claims and groups at the IdP so only the intended staff land.
Full Explanation
When just-in-time provisioning from the statewide identity provider creates Access accounts for every student and floods the school-district directory, the administrator should tighten identity-provider claim and group filters so only intended staff populations JIT-provision into Access. Treat JIT filters as the school enrollment clerk who only creates badges for staff groups, not for every student assertion that arrives. Changing the NSX-T identity firewall sync interval so extra users age out of groups faster fails by concept because IDFW sync timing does not scope which users JIT-provision into Access. Changing Carbon Black Cloud sensor-group membership to hide student accounts fails because CBC groups do not control Access JIT provisioning. Setting a Distributed Firewall default-allow so extra accounts cannot be noticed fails because network default-allow neither scopes JIT nor is an acceptable cover-up. Exam caveat: claim and group filters on the federated IdP limit which identities JIT-provision into Workspace ONE Access. Operational check: apply claim and group filters for intended staff populations, remove erroneously provisioned student accounts, retest JIT with a staff and a student assertion, and document filter criteria in the district Access provisioning standard.