
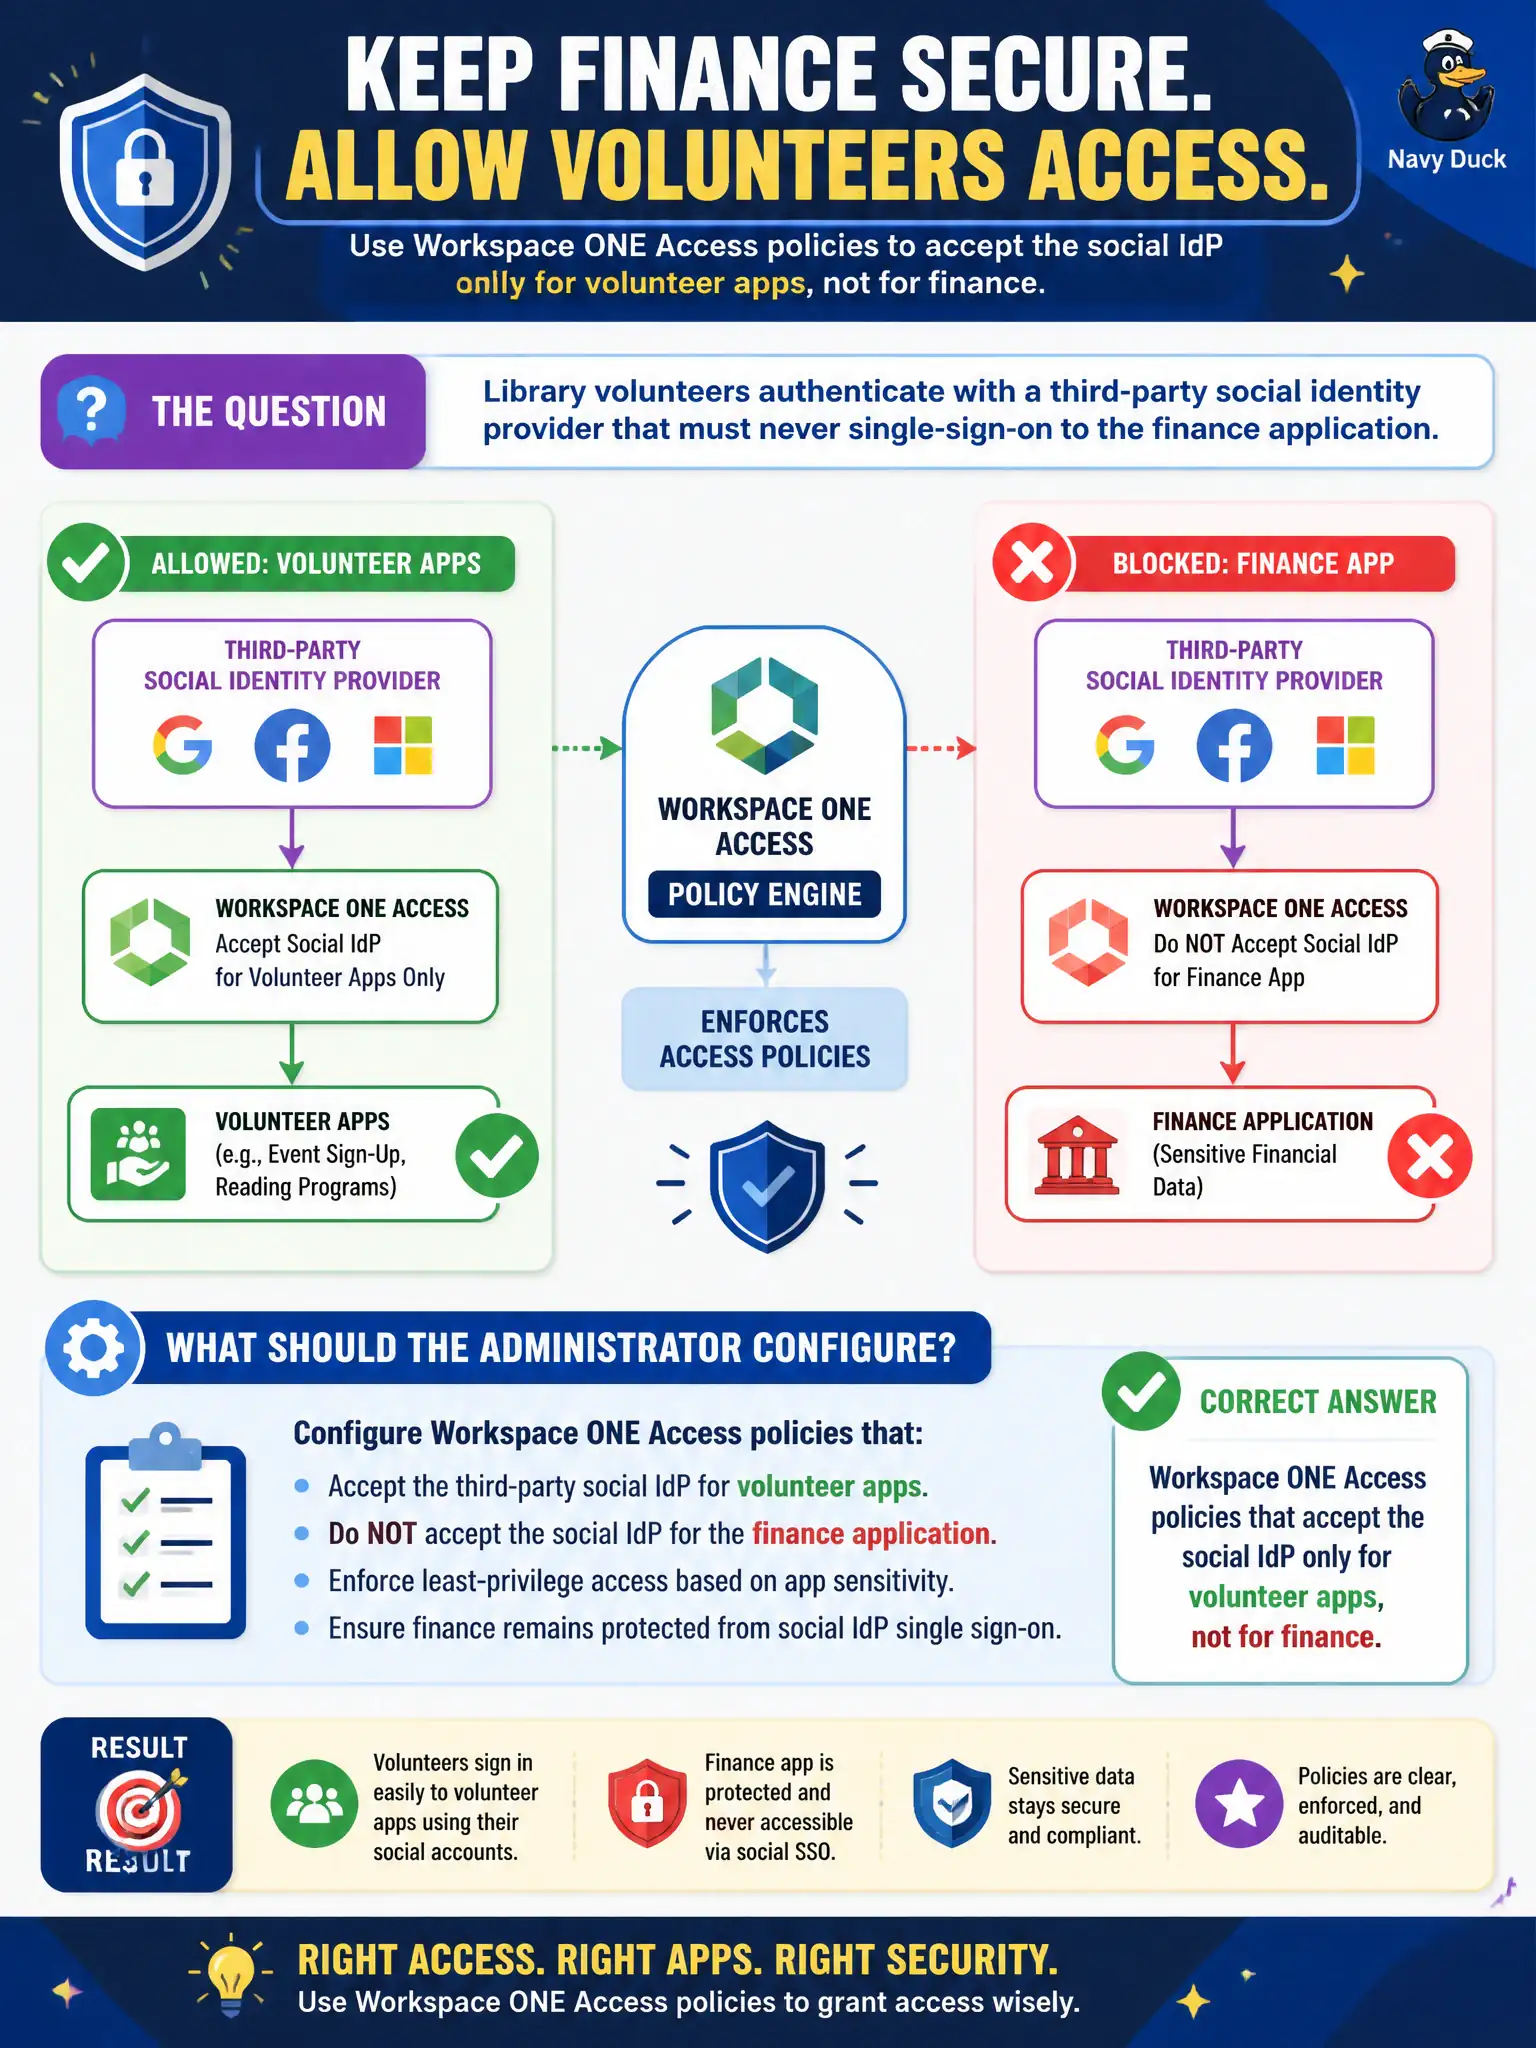
Library volunteers authenticate with a third-party social identity provider that must never single-sign-on to the finance application. What should the administrator configure?
Select an answer to reveal the explanation.
Short Explanation
Volunteer badges open the stacks, not the treasurer's vault. Scope Access so the social IdP is valid only for volunteer apps.
Full Explanation
When library volunteers authenticate with a third-party social identity provider that must never single-sign-on to the finance application, the administrator should configure Workspace ONE Access policies that accept the social IdP only for volunteer apps, not for finance. Treat the social IdP as a volunteer library card that opens maker-space apps but must not open the finance vault. An NSX-T Distributed Firewall rule that drops HTTPS from volunteer VLANs to finance fails by concept because network deny is not IdP-scoped SSO control and volunteers may not even use those VLANs for SaaS. A Carbon Black Cloud device-control block on the finance executable for volunteer PCs fails because device control is not Access IdP acceptance policy for federation. A shared volunteer password on the finance app instead of federation fails because shared passwords are an anti-pattern and do not implement IdP-scoped SSO. Exam caveat: which IdP is accepted for an application is a Workspace ONE Access policy setting—scope the social IdP to volunteer apps and exclude finance. Operational check: bind the social IdP only to volunteer app policies, attempt finance SSO with a social identity and expect deny, confirm staff IdP still reaches finance, and document IdP-to-app mappings in the library Access design.