
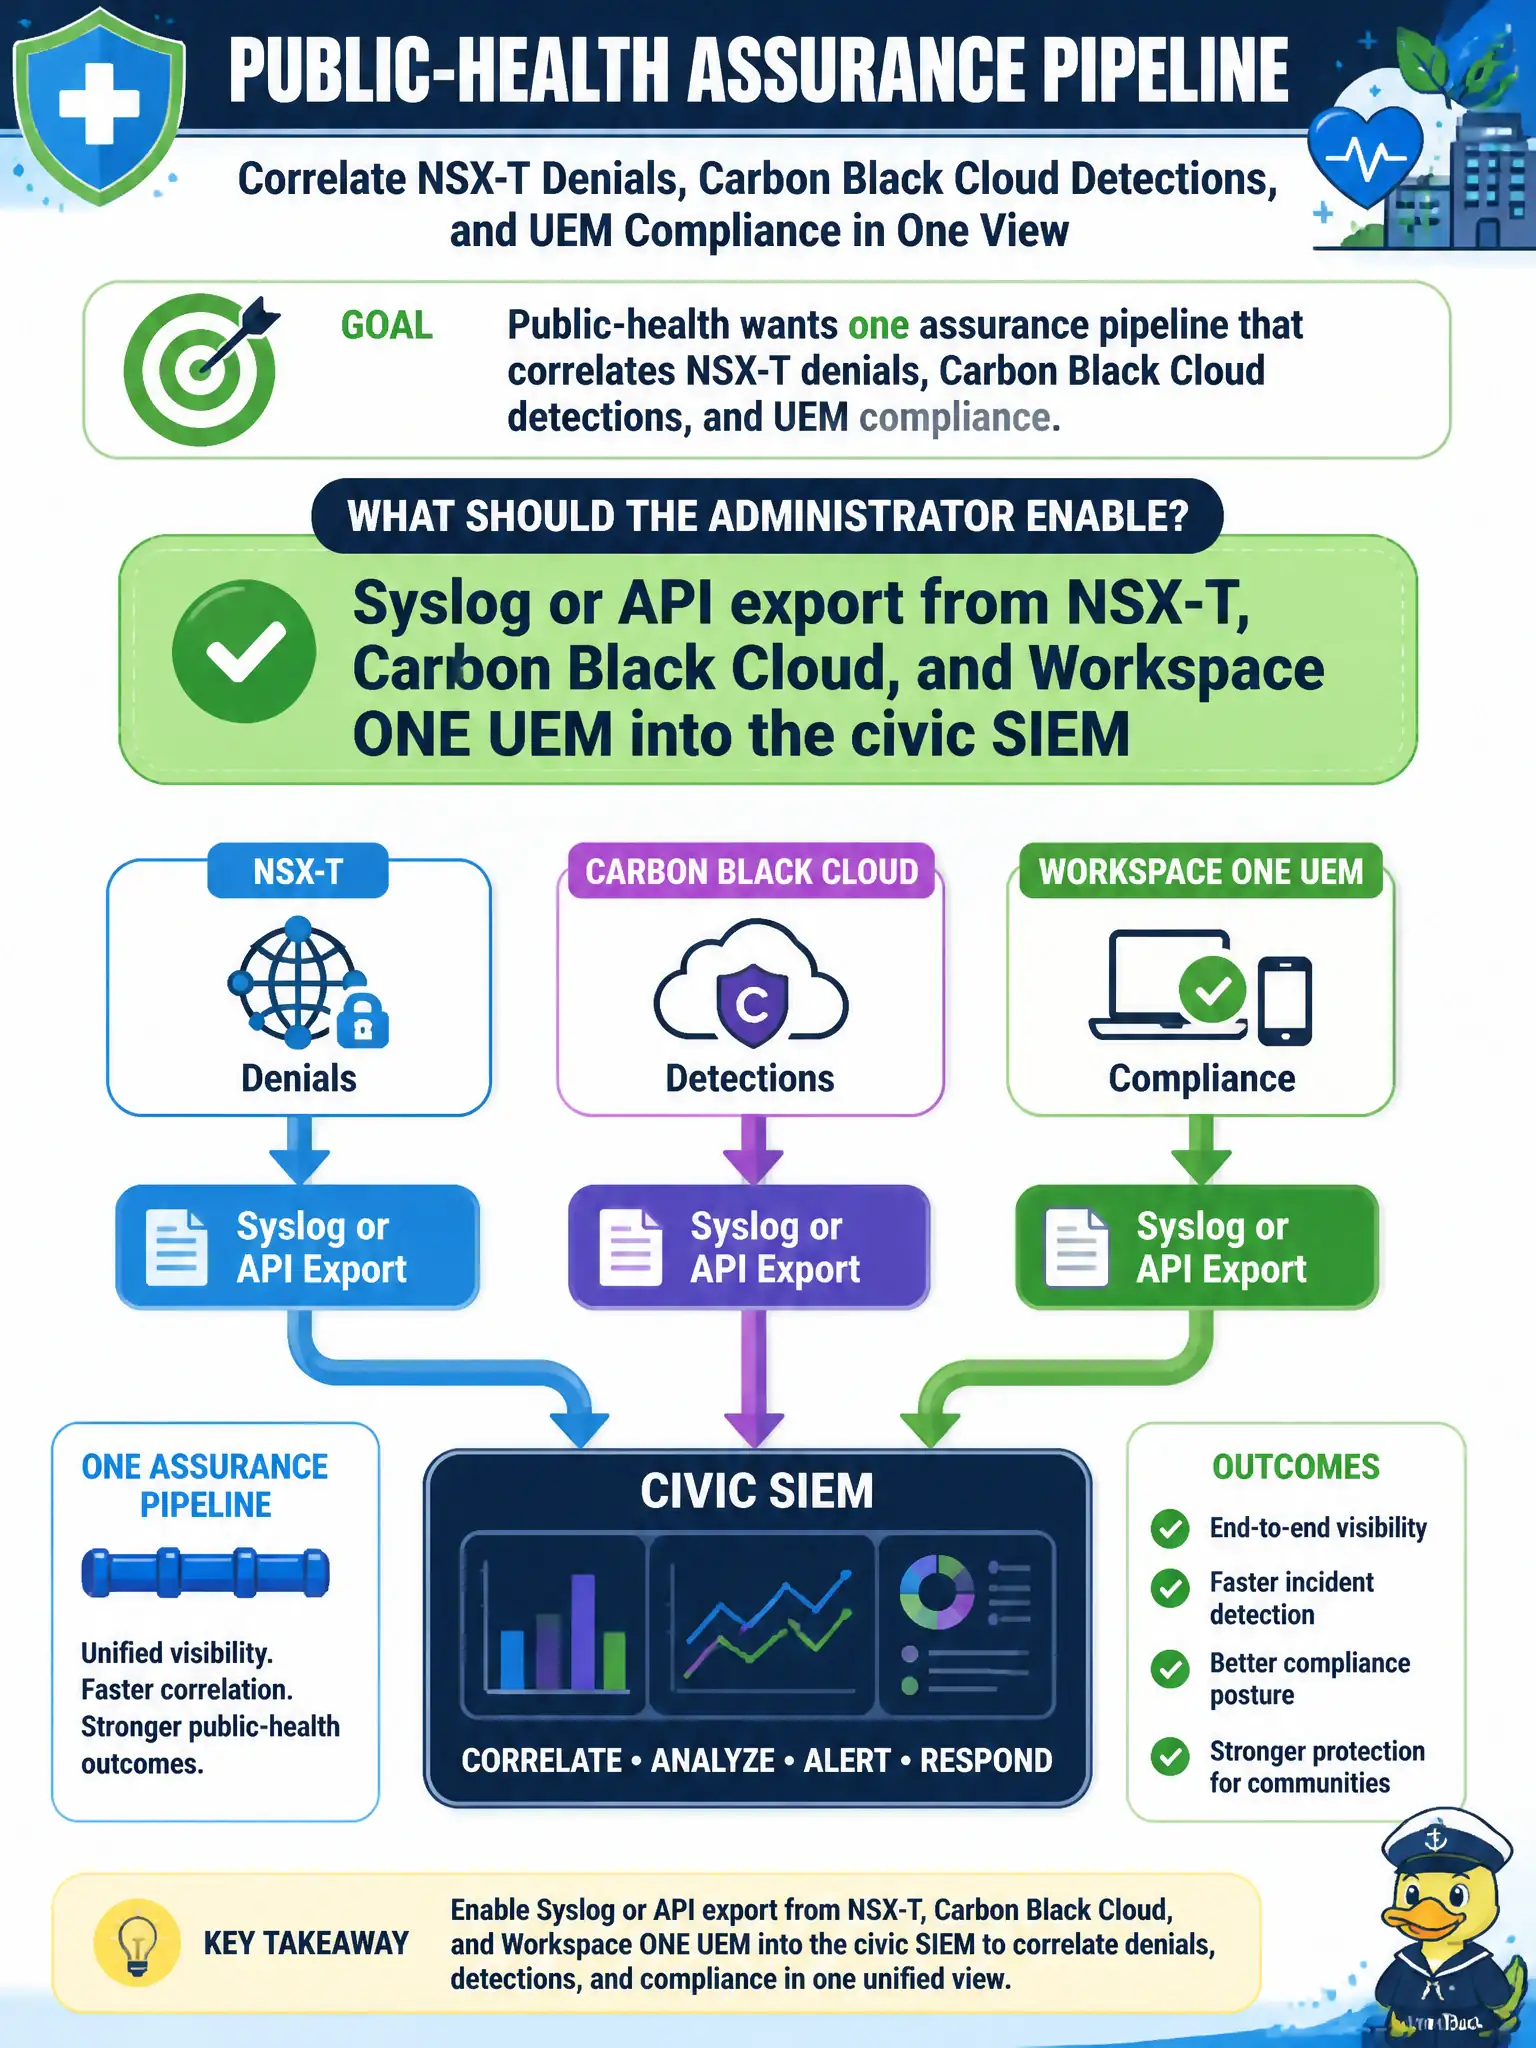
Public-health wants one assurance pipeline that correlates NSX-T denials, Carbon Black Cloud detections, and UEM compliance. What should the administrator enable?
Select an answer to reveal the explanation.
Short Explanation
Three clinic radios only help if they feed the same dispatcher. Ship NSX-T, Carbon Black Cloud, and UEM into the civic SIEM over syslog or API so regulation monitoring can correlate them.
Full Explanation
Public-health wanting one assurance pipeline that correlates NSX-T denials, Carbon Black Cloud detections, and UEM compliance should enable syslog or API export from NSX-T, Carbon Black Cloud, and Workspace ONE UEM into the civic SIEM. Treat the SIEM as the public-health operations floor where deny, detect, and device-posture signals land on one timeline. Screenshotting each console weekly instead of shipping logs fails by concept because static screenshots cannot correlate events across products or support continuous monitoring. Exporting only vCenter tasks and skipping the security products fails because vCenter task logs omit DFW denials, CBC detections, and UEM compliance. Replacing product telemetry with a statement of applicability and no log shipping fails because a paper SoA does not provide correlated operational evidence. Exam caveat: multi-product regulation assurance means exporting NSX-T, Carbon Black Cloud, and Workspace ONE UEM telemetry to a SIEM via syslog or API. Operational check: enable exports from all three products, verify events arrive in the civic SIEM, build correlation views for denials versus detections versus non-compliance, and document the pipeline in the public-health assurance architecture.