
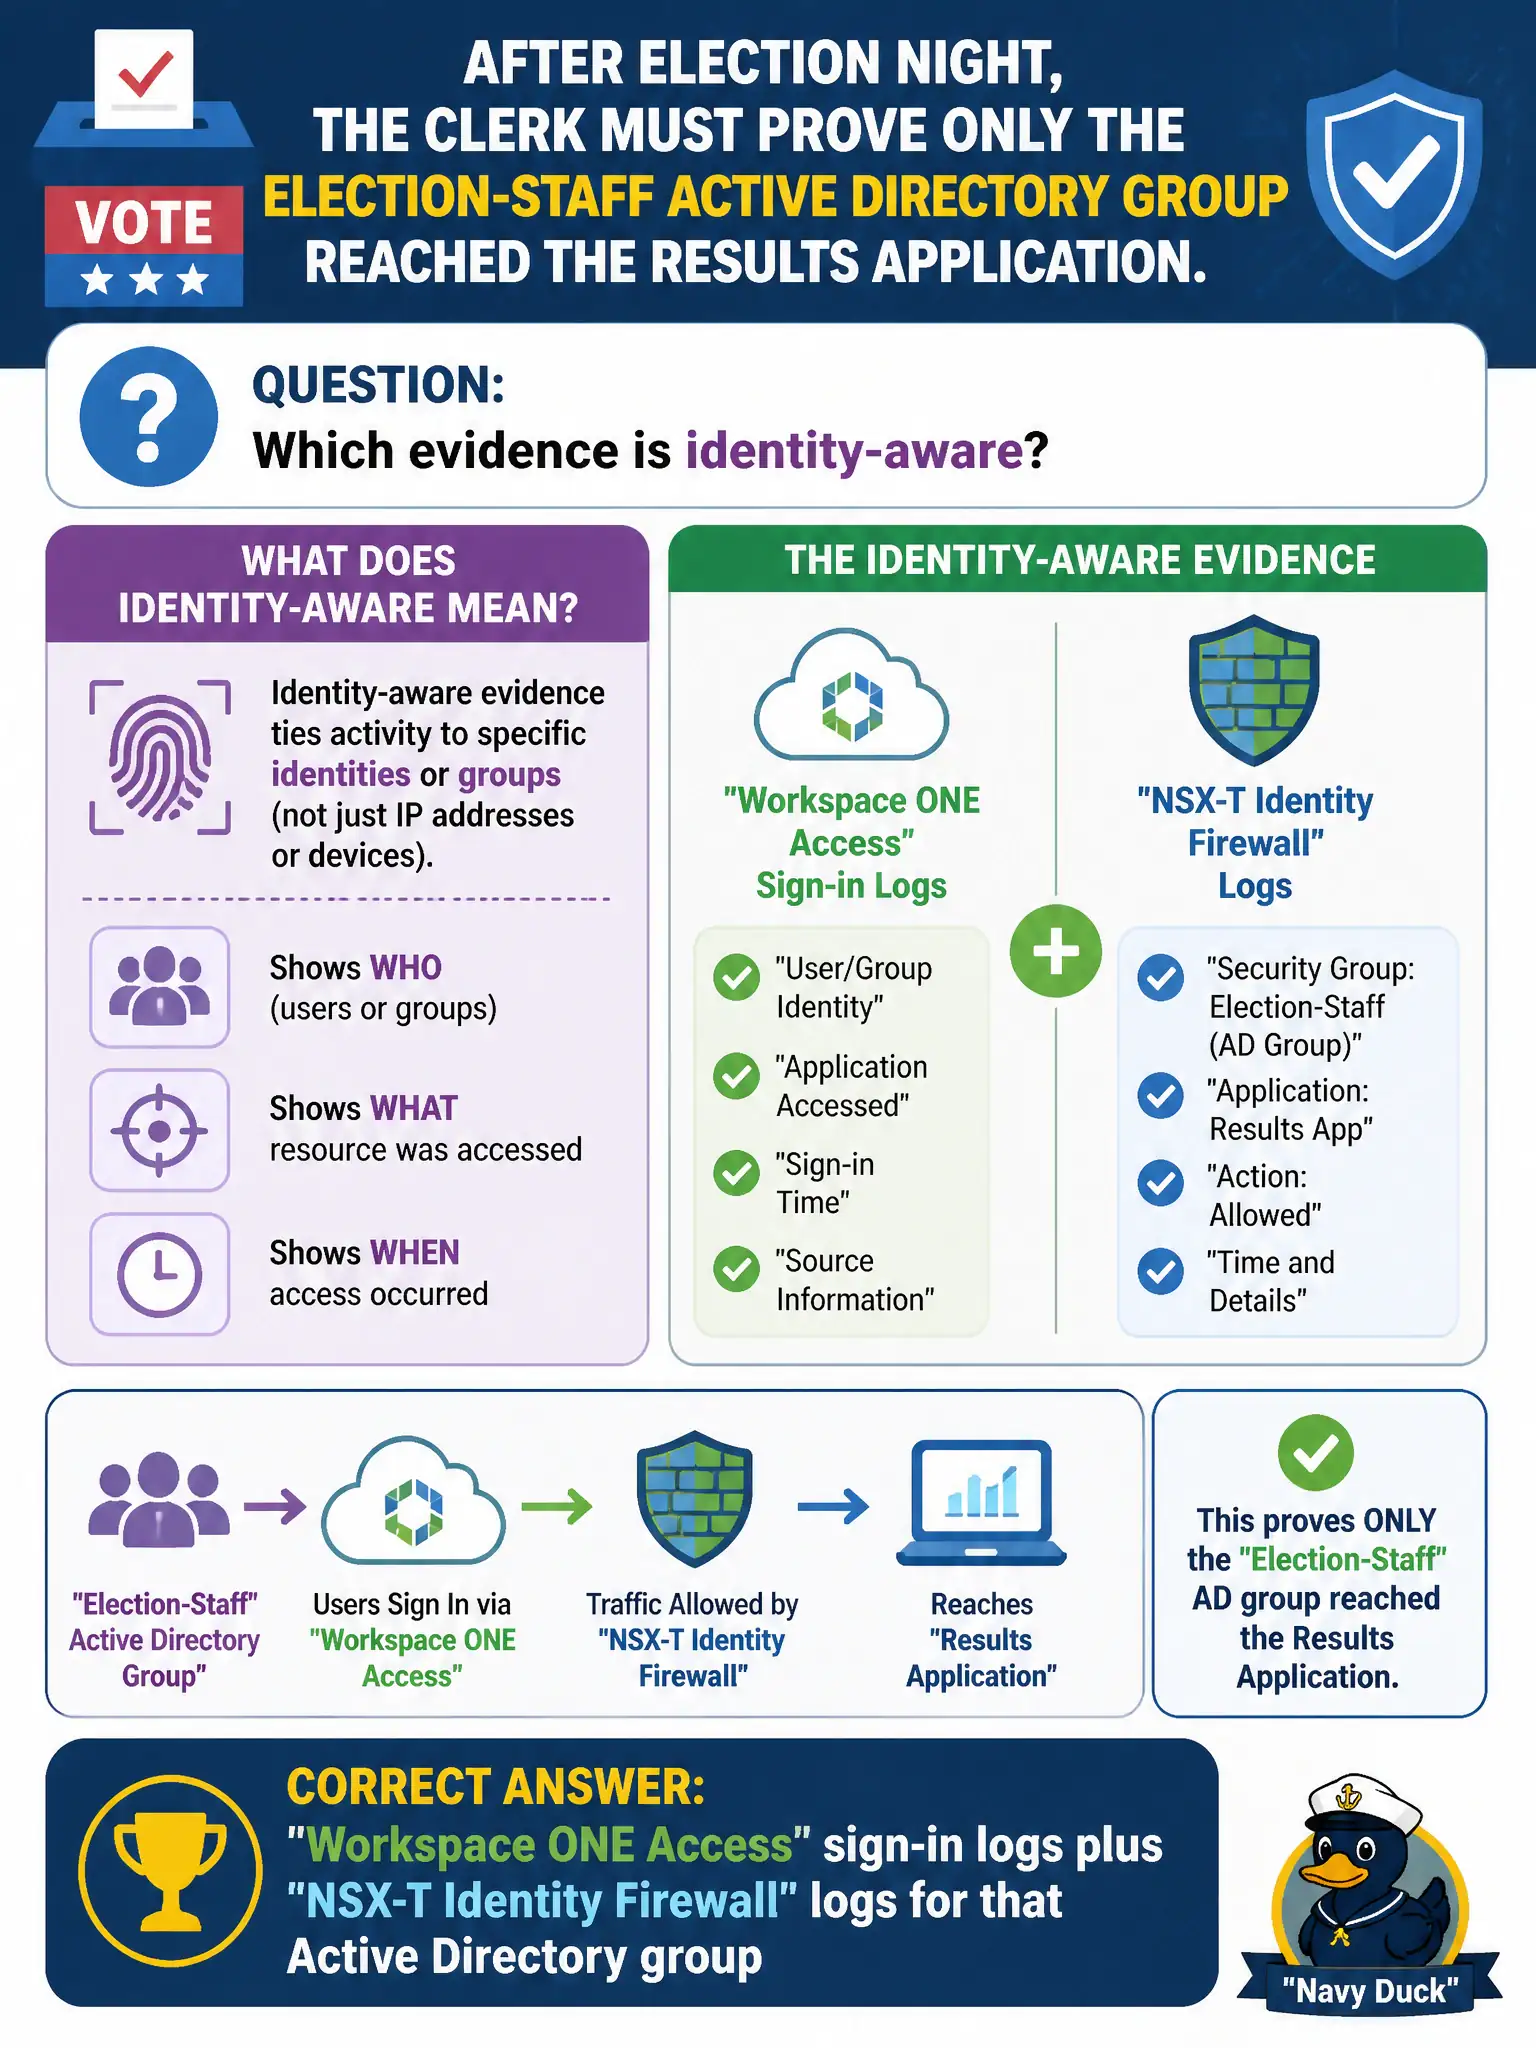
After election night, the clerk must prove only the election-staff Active Directory group reached the results application. Which evidence is identity-aware?
Select an answer to reveal the explanation.
Short Explanation
The clerk does not want to know which printer talked—the clerk wants to know which people walked in. Access sign-ins plus Identity Firewall logs for the election-staff group are that guest list.
Full Explanation
After election night, when the clerk must prove only the election-staff Active Directory group reached the results application, the identity-aware evidence is Workspace ONE Access sign-in logs plus NSX-T Identity Firewall logs for that Active Directory group. Treat those user logs as the poll-book signatures showing which election staff actually opened the results door. Distributed Firewall IP-only hit counts with no user mapping fail by concept because IP hits show addresses, not AD group membership on the path. Tier-0 interface counters on the results VLAN fail because interface counters are volume metrics, not identity-aware access evidence. Carbon Black Cloud device inventory without Access or Identity Firewall user fields fails because device inventory alone does not prove which AD group reached the results app. Exam caveat: user-based controls require user-based evidence—Access sign-in logs and Identity Firewall logs tied to the election-staff group. Operational check: export Access sign-ins for the results app filtered to election-staff, correlate Identity Firewall hits for that AD group, confirm no unexpected users, and archive the identity evidence with the election canvass package.