
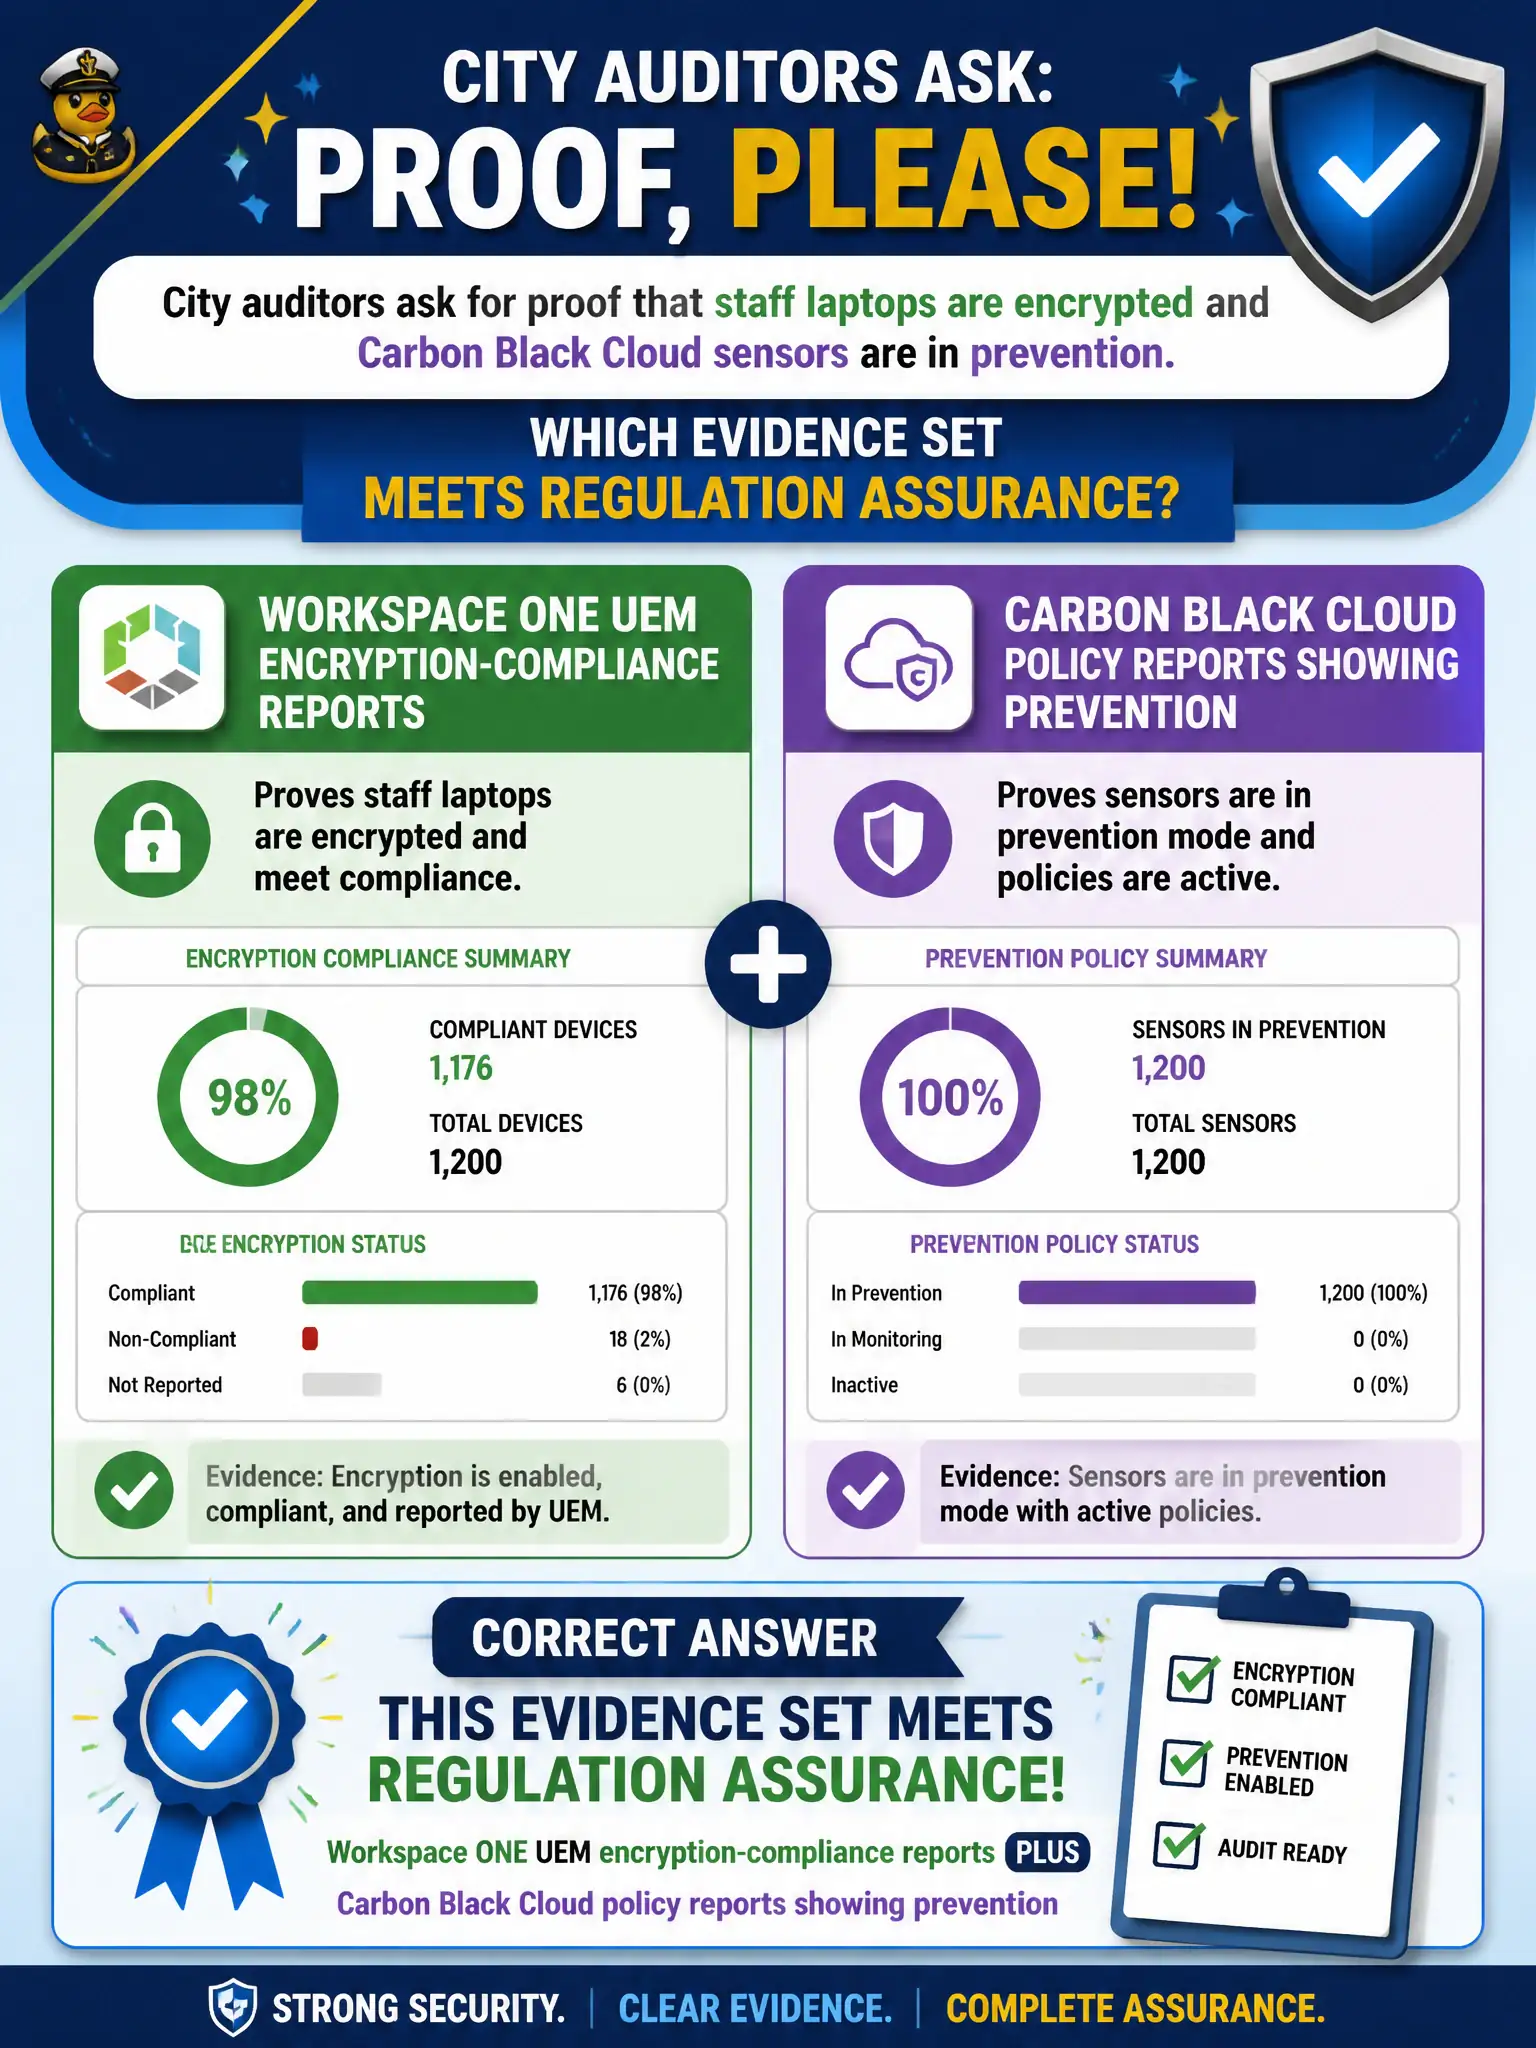
City auditors ask for proof that staff laptops are encrypted and Carbon Black Cloud sensors are in prevention. Which evidence set meets regulation assurance?
Select an answer to reveal the explanation.
Short Explanation
Auditors want to see the locks and the cameras, not a nicely written essay about locks. Pull UEM encryption compliance and Carbon Black Cloud prevention reports from the actual city laptops.
Full Explanation
When city auditors ask for proof that staff laptops are encrypted and Carbon Black Cloud sensors are in prevention, the evidence set that meets regulation assurance is Workspace ONE UEM encryption-compliance reports plus Carbon Black Cloud policy reports showing prevention. Treat those product reports as the civic meters that show doors locked and alarms armed—not as a memo describing how locks ought to work. A control-family memo with no Workspace ONE or Carbon Black Cloud telemetry fails by concept because managerial language without product posture is not assurance evidence. NSX-T Tier-0 routing tables as proof of disk encryption fail because routing tables show underlay or Edge routing, not laptop encryption state. Horizon pod design diagrams as the encryption and prevention control fail because architecture diagrams do not report live UEM encryption or Carbon Black prevention posture. Exam caveat: regulation assurance on the VMware security stack is product telemetry from UEM and Carbon Black Cloud for those controls; memos, T0 tables, and Horizon diagrams are not substitutes. Operational check: export UEM encryption-compliance for staff laptop smart groups, export Carbon Black Cloud policy reports confirming prevention, attach both to the audit package, and schedule recurring report pulls for continuous assurance.