
Intruders quietly steal voter-roll exports from a county system and prepare them for sale, without knocking services offline. Which motivation best matches this behavior?
Select an answer to reveal the explanation.
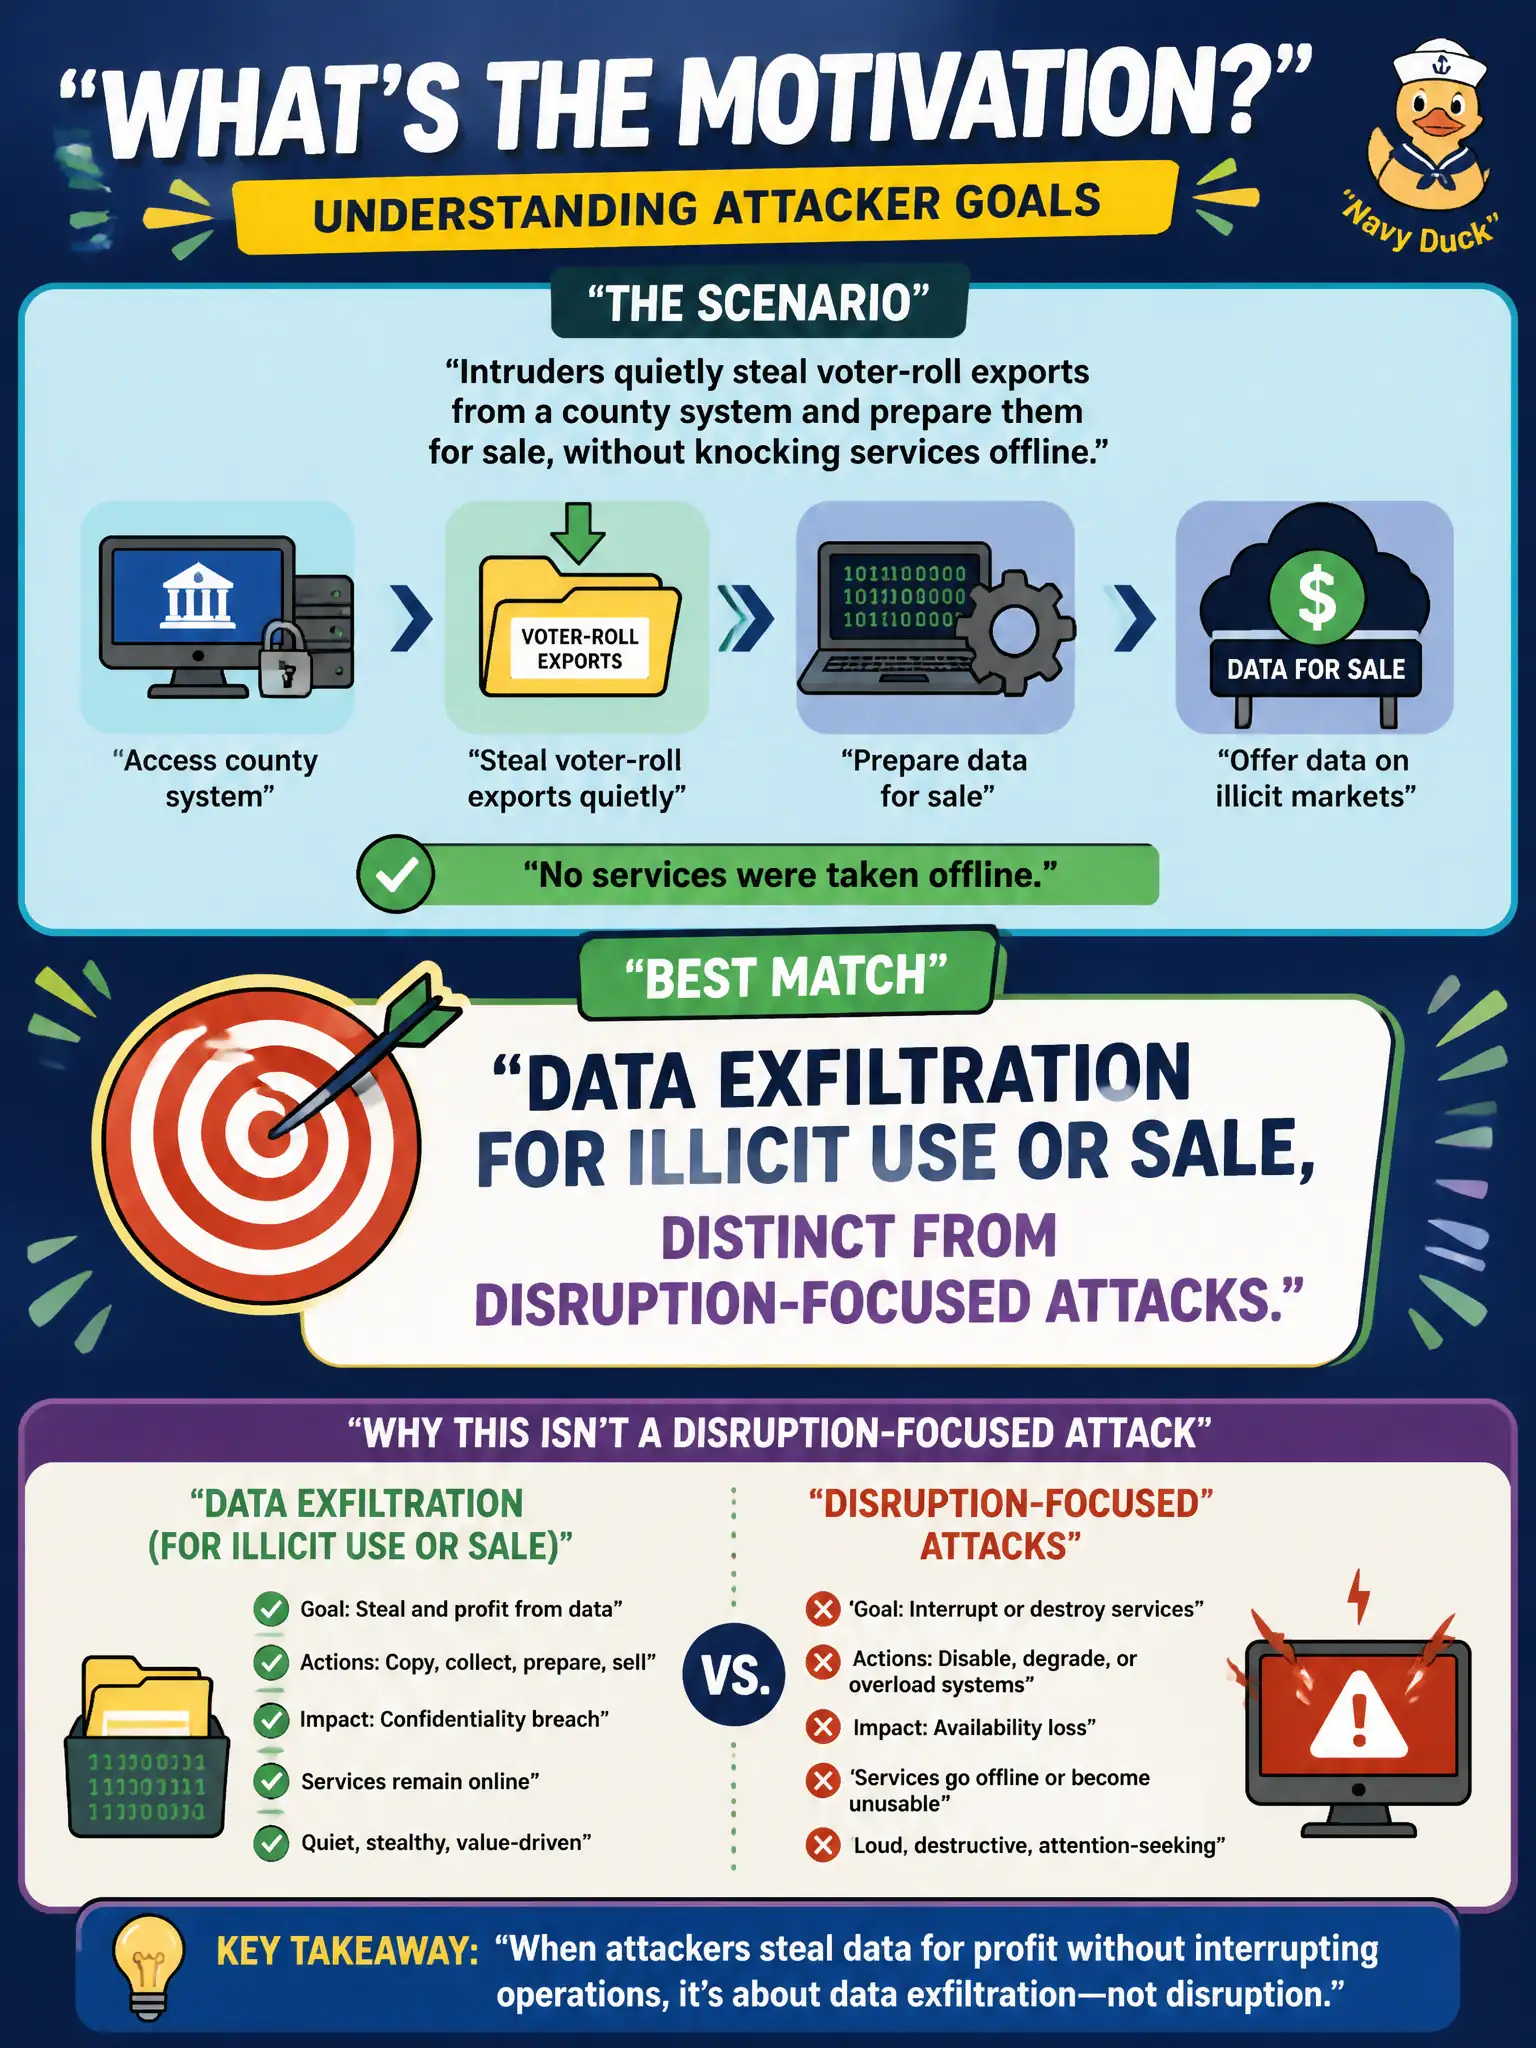
Short Explanation
If the lights stay on but the voter file walks out the door for a black-market listing, the motive is exfiltration—not DDoS chaos or spray-paint politics. Different crimes leave different footprints.
Full Explanation
Quiet theft of voter-roll exports prepared for illicit use or sale, without knocking services offline, centers on data exfiltration. The motivation is obtaining and removing sensitive information for espionage, fraud, or black-market sale. Availability remains intact by design so operators may not notice until later; confidentiality of election-related personal data is the asset under attack.
Service disruption and chaos similar to volumetric DDoS would prioritize outages and citizen-facing downtime, which the scenario explicitly avoids. Website defacement for political slogans is a visibility and messaging motive, not silent preparation of voter files for sale. Authorized archival by election officials under an approved retention ticket is legitimate records management, not intruder theft for illicit markets.
Exam caveat: separate exfiltration motives from disruption and vandalism; intact services plus stolen data points to exfiltration. Operational check: monitor bulk export and unusual query volumes on voter systems, restrict export roles, encrypt and watermark sensitive extracts, alert on transfers to personal media or odd destinations, and exercise detection that does not rely solely on availability alarms.