
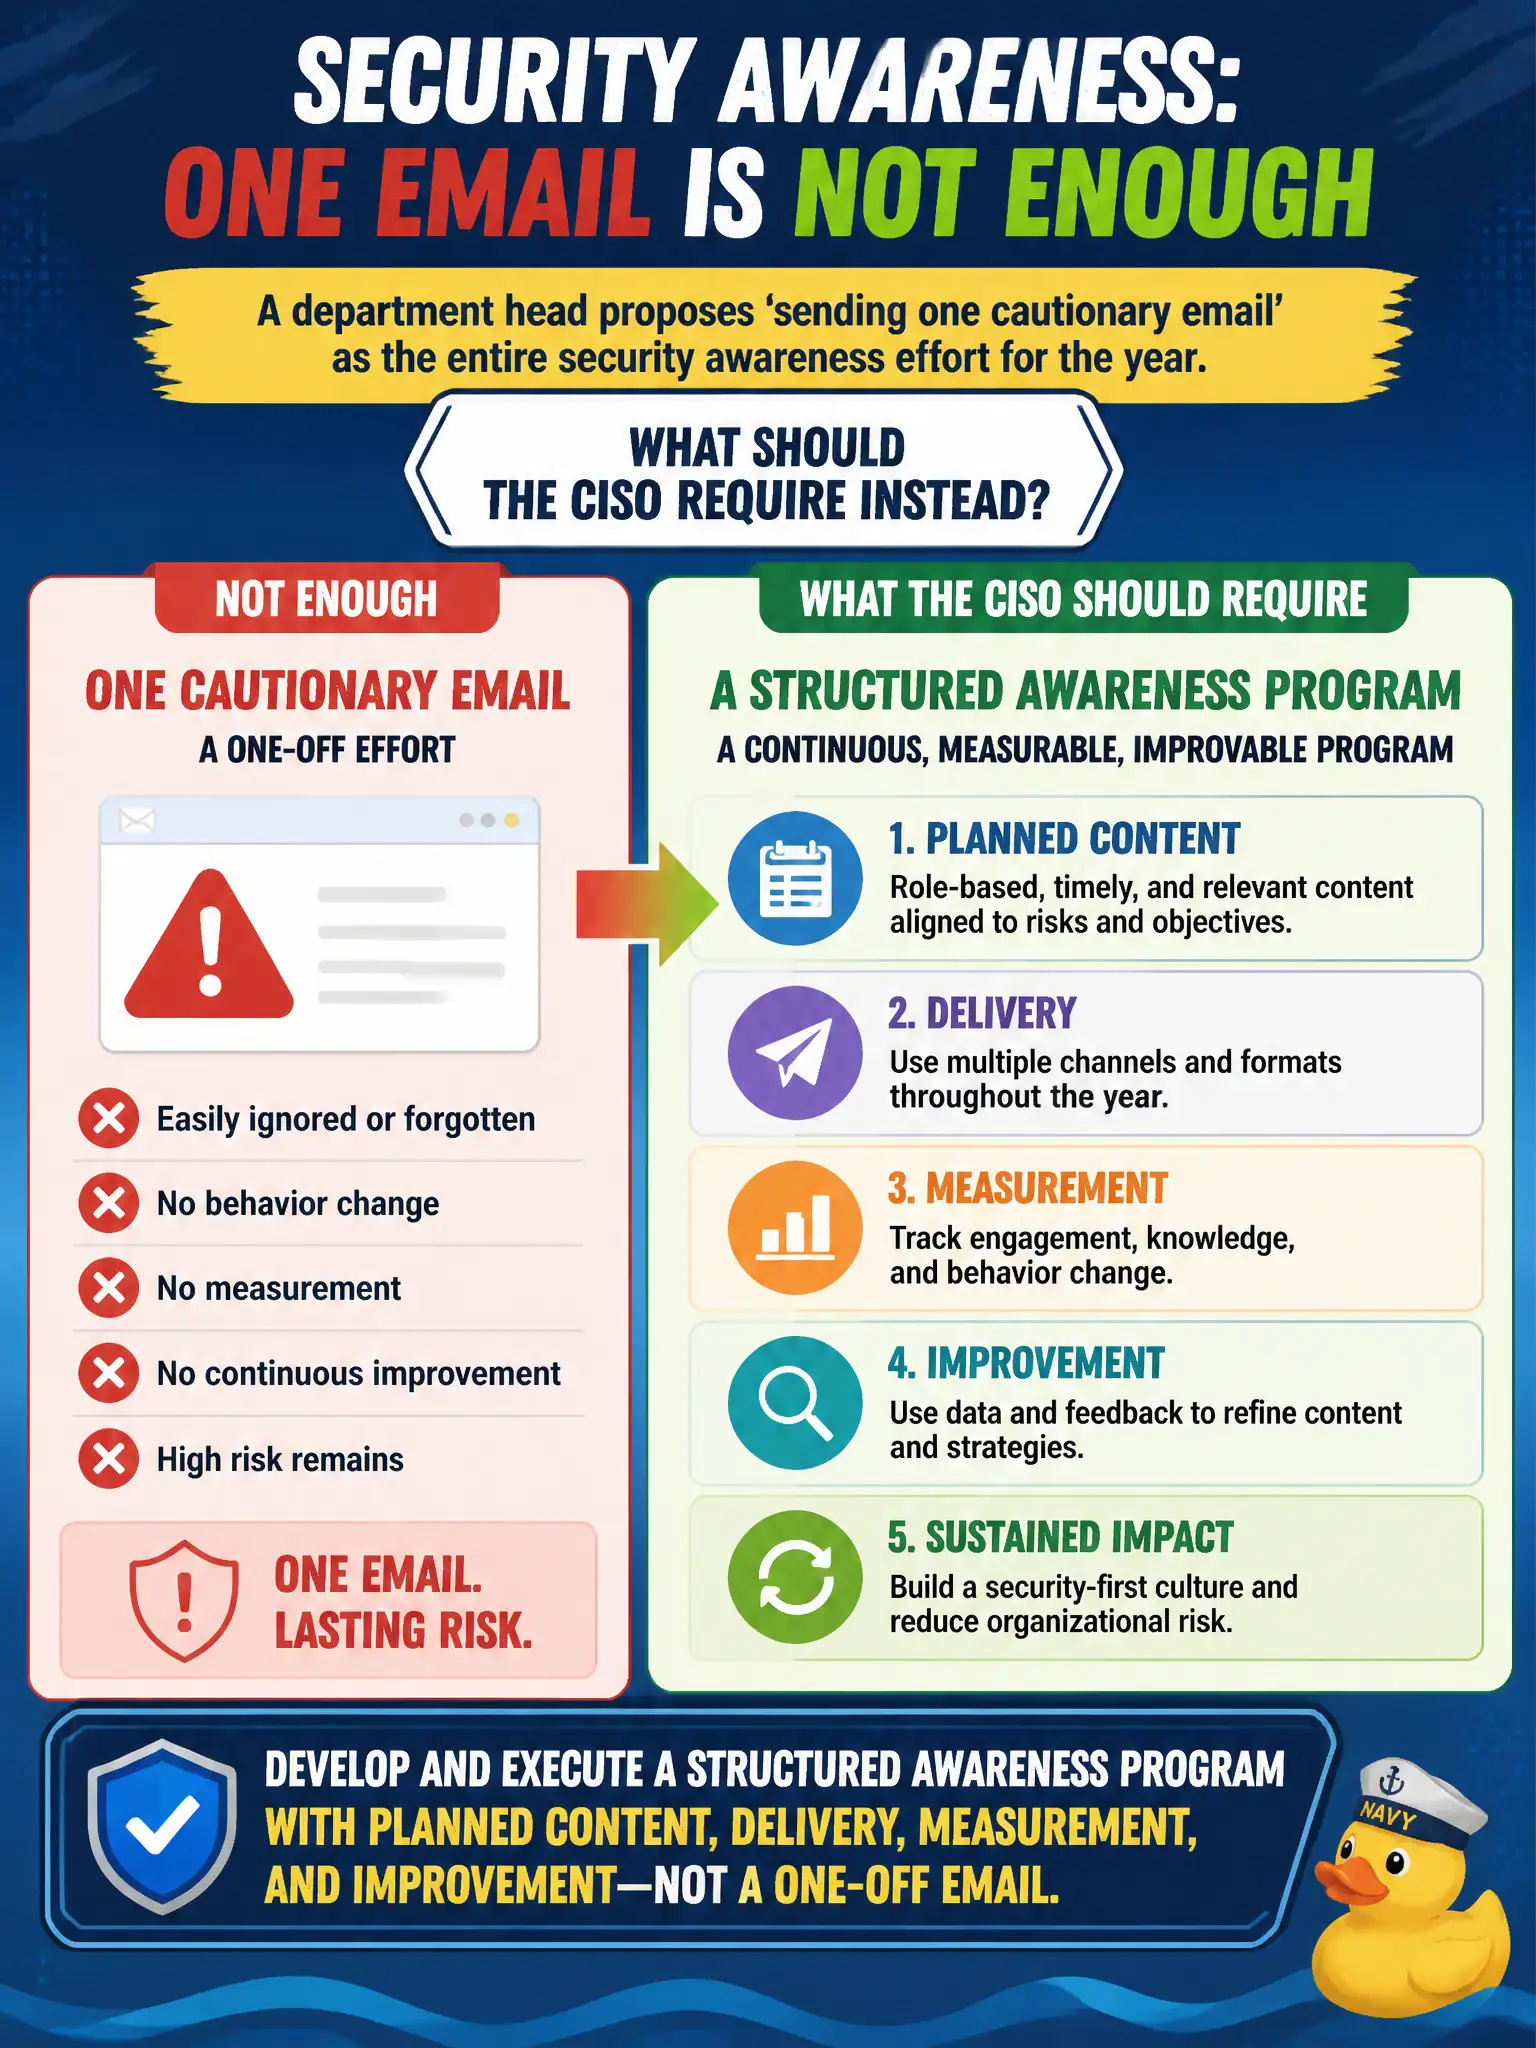
A department head proposes 'sending one cautionary email' as the entire security awareness effort for the year. What should the CISO require instead?
Select an answer to reveal the explanation.
Short Explanation
One email isn’t a program—it’s a shrug with a subject line. Build the real thing: plan it, run it, measure it, improve it.
Full Explanation
A single cautionary email is not a security awareness program. The CISO should require development and execution of a structured program with planned content, delivery methods, measurement, and continuous improvement. Municipal workforces need role-relevant modules, simulations, acknowledgements, and feedback loops—not a once-a-year message that is easy to ignore and impossible to prove effective.
Agreeing that one annual email fully satisfies awareness obligations mistakes activity for a program and will fail audit or grant scrutiny. Replacing awareness with unmonitored internet browsing as 'experiential learning' abandons curriculum and measurement. Outsourcing awareness solely to fortune-cookie lunch messages is unserious and leaves no audit trail or skill building for clerks handling resident data.
Exam caveat: Look for answers describing a managed program lifecycle—plan, deliver, measure, improve—versus one-off communications or gimmicks that cannot demonstrate coverage or behavior change.
Operational check: publish an annual awareness plan (topics by quarter, audiences, channels), budget for LMS and simulations, assign an owner, review metrics in a governance meeting, and update content after real municipal incidents or new grant requirements.