
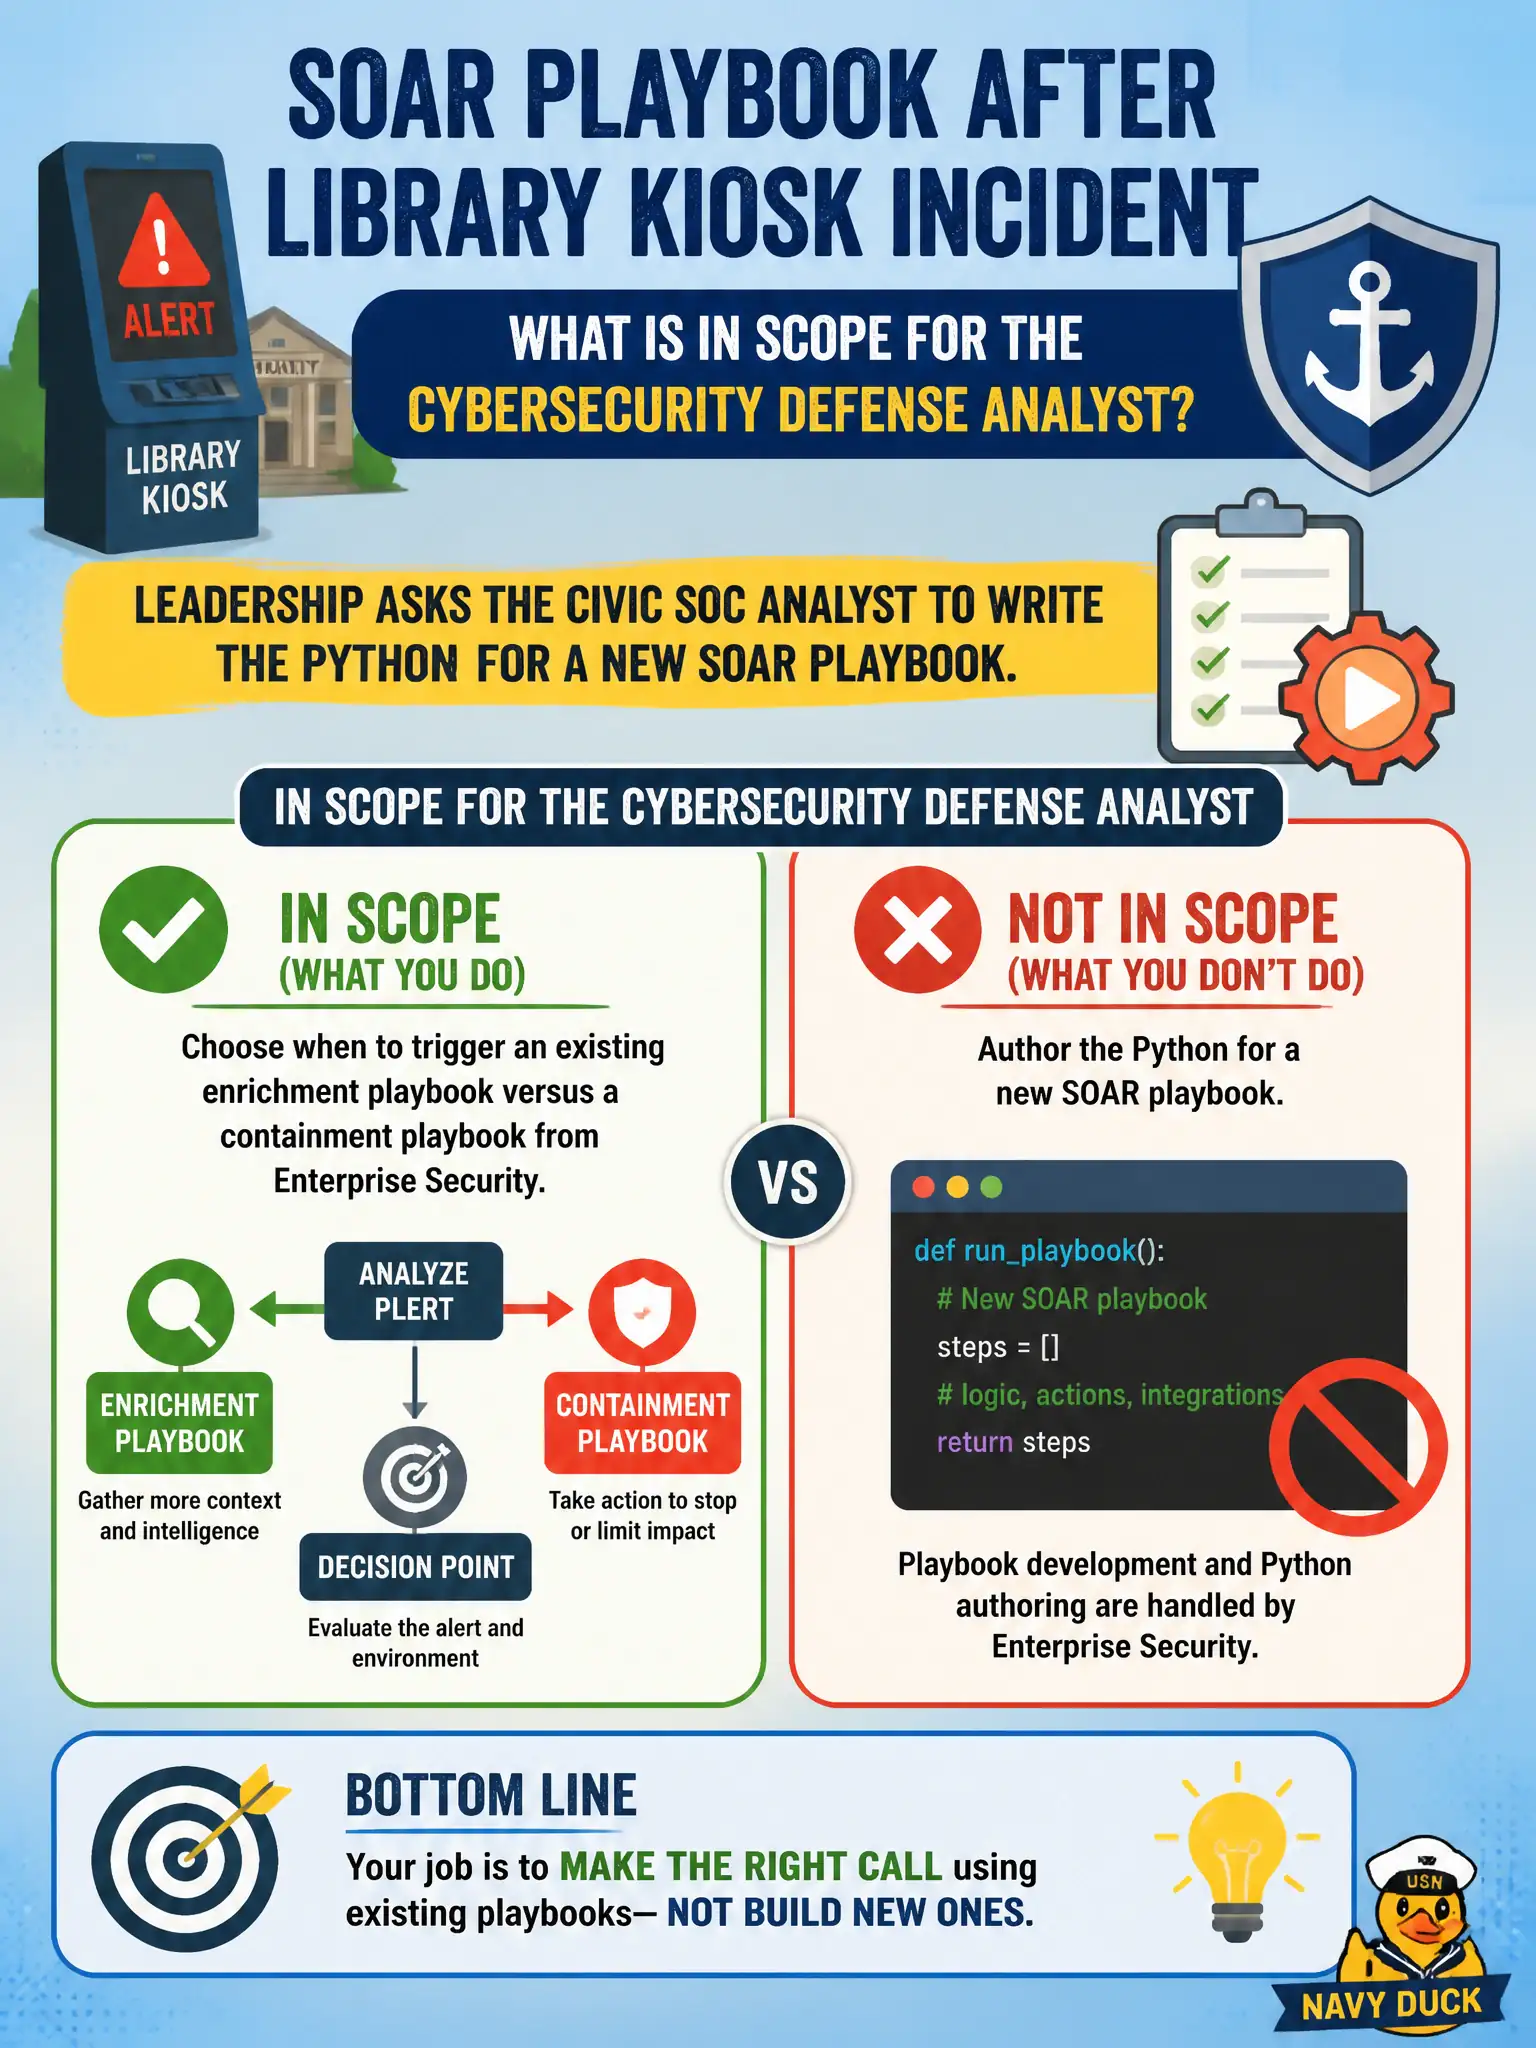
Leadership asks the civic SOC analyst to write the Python for a new SOAR playbook after a library kiosk incident. What is in scope for the Cybersecurity Defense Analyst?
Select an answer to reveal the explanation.
Short Explanation
This exam is not a SOAR developer lab. The analyst skill is picking enrichment versus containment and knowing when to pull that trigger from ES. Leave the Python to the playbook authors.
Full Explanation
SPLK-5001 for the Cybersecurity Defense Analyst covers when and how to trigger SOAR playbooks from Enterprise Security—including choosing enrichment versus containment for a library kiosk incident—not authoring or debugging the Python inside those playbooks. After a library kiosk incident, leadership may want new automation, but the analyst's in-scope contribution is selecting the right existing playbook trigger path and impact level from ES, not becoming the SOAR developer. Authoring and debugging the Python playbook in Splunk SOAR as the exam skill misstates the blueprint and sibling-cert boundaries. Installing the SOAR server and creating custom integrations are platform and engineering tasks outside analyst scope. Sizing the SOAR automation farm is Defense Architect territory, not Analyst exam skill. Exam caveat: analyst scope is trigger selection and enrichment-versus-containment judgment from ES; playbook code, SOAR install, custom integrations, and farm sizing belong elsewhere. Operational check: for the library kiosk incident, pick an existing enrichment playbook versus a containment playbook based on confidence and blast radius, trigger it via the appropriate ES path, and escalate playbook code changes to SOAR developers rather than writing Python yourself.