
While working an elections investigation in Enterprise Security, the analyst needs to launch playbook actions as part of the case workflow. Which trigger path does this describe?
Select an answer to reveal the explanation.
Short Explanation
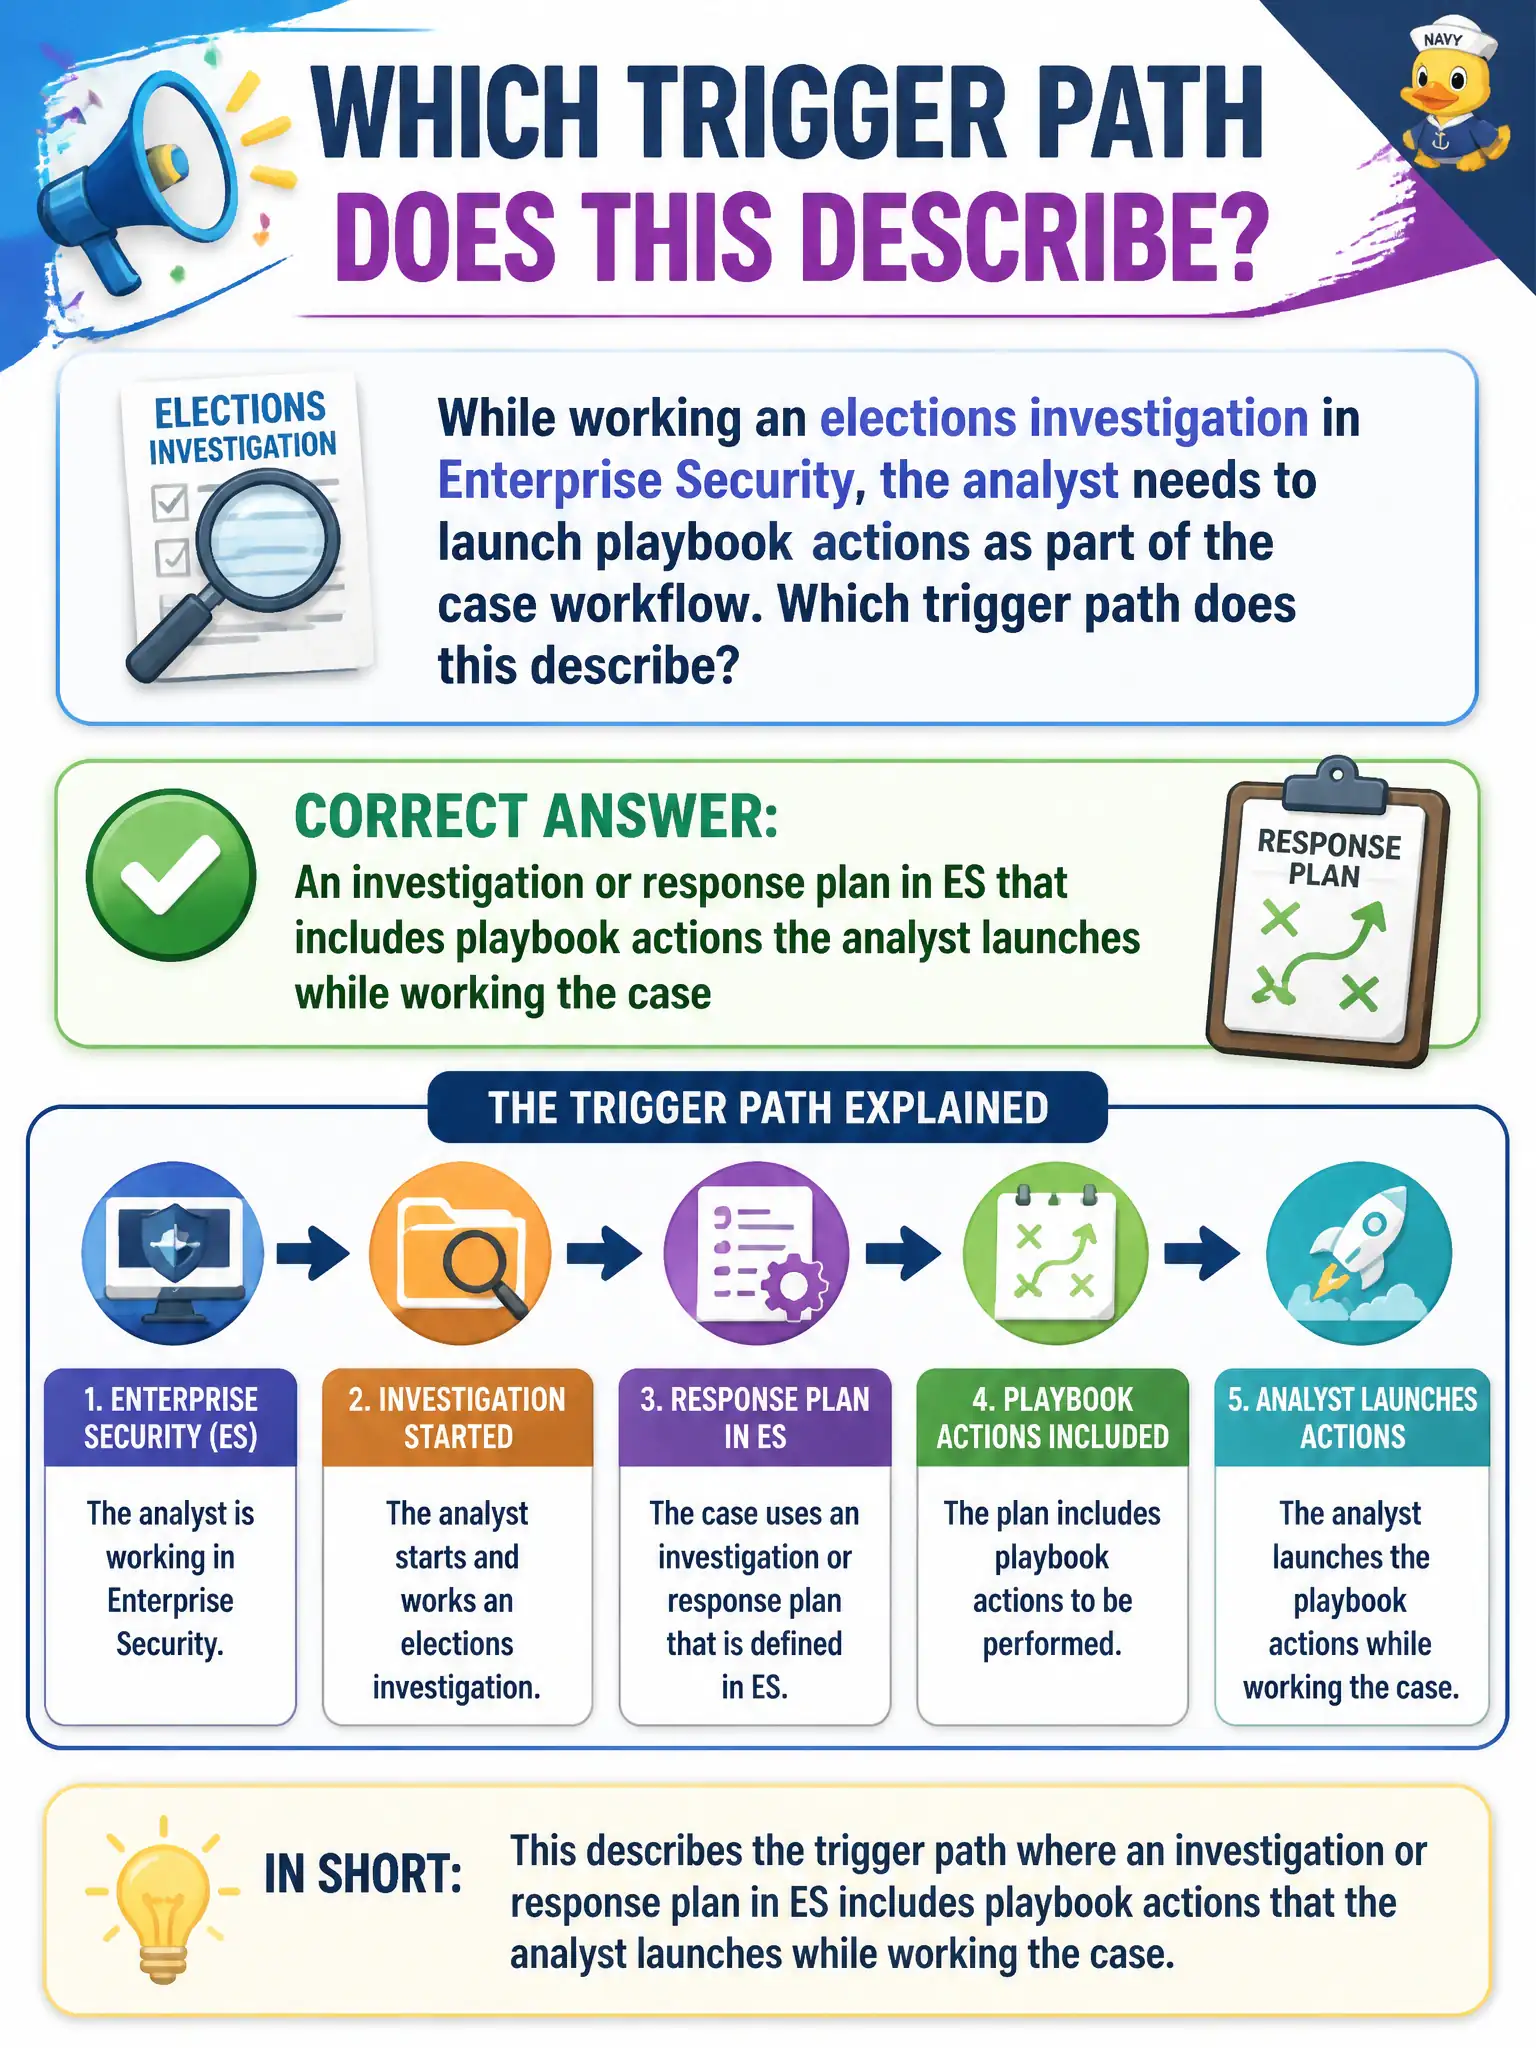
A response plan is the case folder with the next buttons already printed. While the elections investigation is open, the analyst launches those playbook actions from the plan. That is a third trigger path besides scheduled AR and a one-off queue click.
Full Explanation
Enterprise Security investigations can include a response plan with playbook actions the analyst launches while working the case; that investigation or response-plan path is a named ES-to-SOAR trigger style alongside scheduled Adaptive Response and ad-hoc Analyst Queue actions. During an elections investigation, launching those plan-embedded playbook actions as part of the case workflow is exactly what that path describes. A CIM field extraction on the Email data model is onboarding and normalization work, not a playbook trigger. A tstats search with no Adaptive Response may power detections but does not by itself invoke SOAR playbooks. An indexer-cluster rolling restart from Incident Review is platform administration and is not available—or appropriate—as an investigation playbook action. Exam caveat: response plans inside ES investigations are a third trigger path for playbook actions during case work—do not confuse them with CIM extractions, bare tstats, or indexer operations. Operational check: open the elections investigation, locate the response plan's playbook actions, launch an enrichment playbook from the plan while the case is active, and verify SOAR shows the run tied to that investigation context.