
Which SOAR trigger policy fits the city's risk tolerance?
Select an answer to reveal the explanation.
Short Explanation
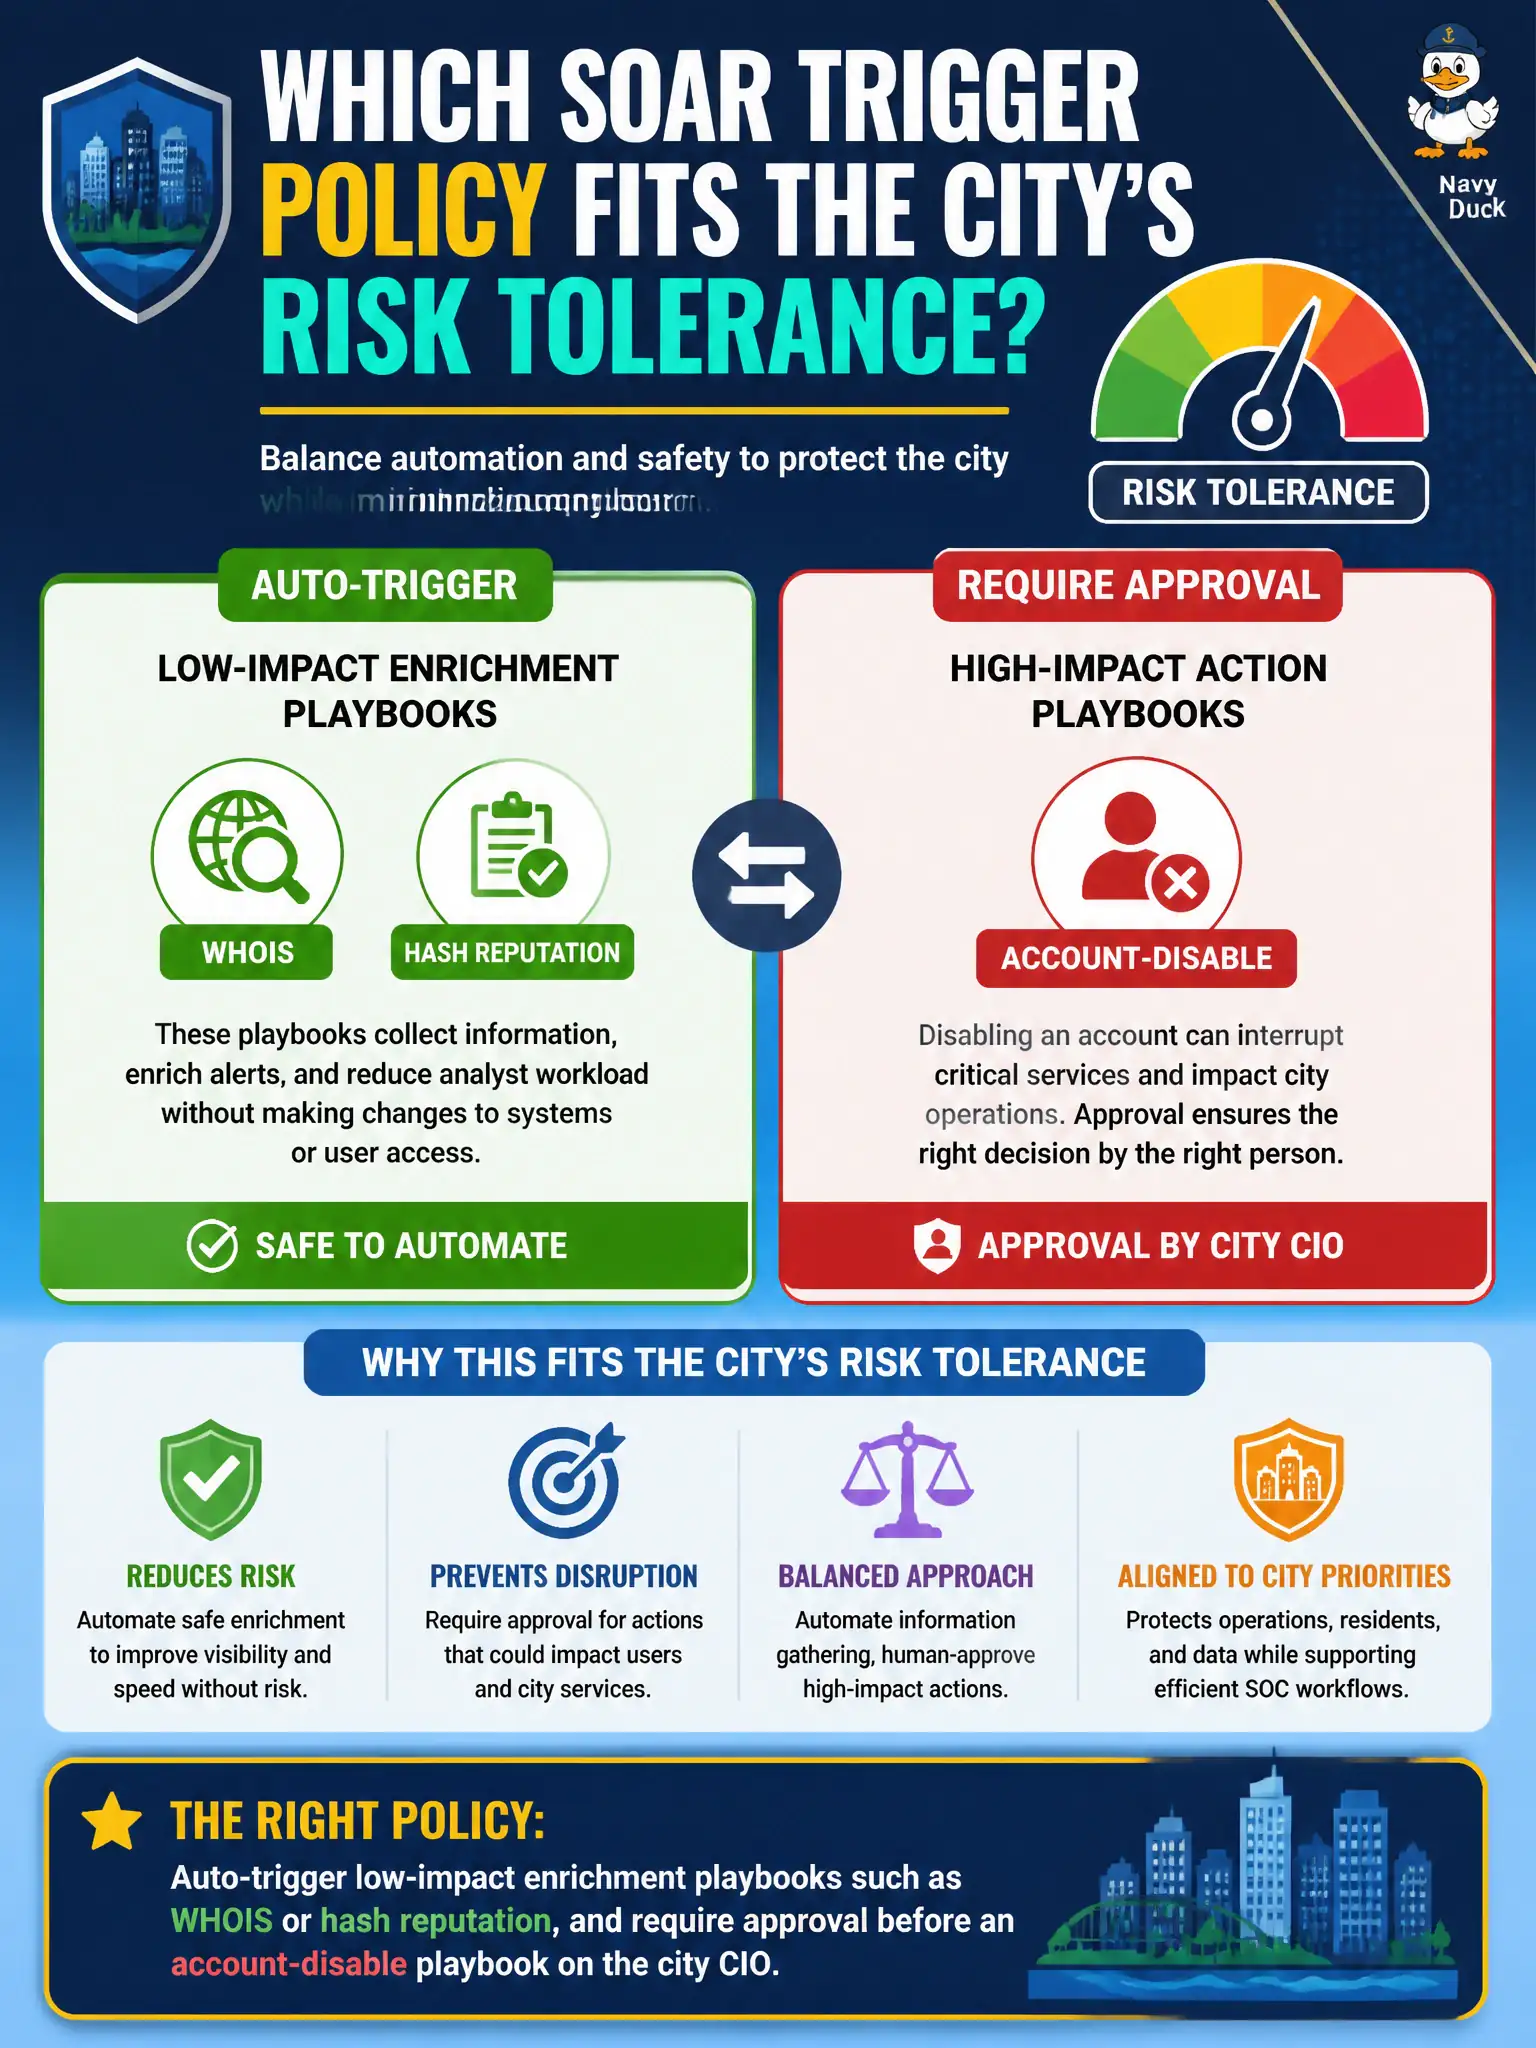
WHOIS and hash lookups are like asking the library catalog who checked out a book—safe to automate. Disabling the CIO is changing the locks on city hall. Match impact to auto versus approved.
Full Explanation
Analysts match playbook impact to trigger style so civic automation stays safe. Auto-triggering low-impact enrichment playbooks such as WHOIS or hash reputation is appropriate, while account-disable on a high-privilege identity requires approval—exactly the policy that fits a city risk tolerance when enrichment is cheap and containment is costly. Auto-triggering an account-disable playbook on the city CIO whenever any notable appears is disproportionate and can lock out critical leadership on noise. Never triggering enrichment playbooks because WHOIS is always destructive mislabels passive enrichment as containment and throws away safe automation. Auto-disabling every identity in Asset and Identity on the first risk event inverts impact modeling and can halt municipal operations. Exam caveat: enrichment auto-trigger versus containment with approval is the SPLK-5001 impact model—do not treat WHOIS as destructive or executive disable as default auto. Operational check: configure WHOIS/hash enrichment playbooks to auto-trigger from appropriate detections, require approval before any account-disable playbook (especially CIO or other privileged civic identities), and test both paths with a non-production notable to confirm enrichment runs free while disable waits for approval.