
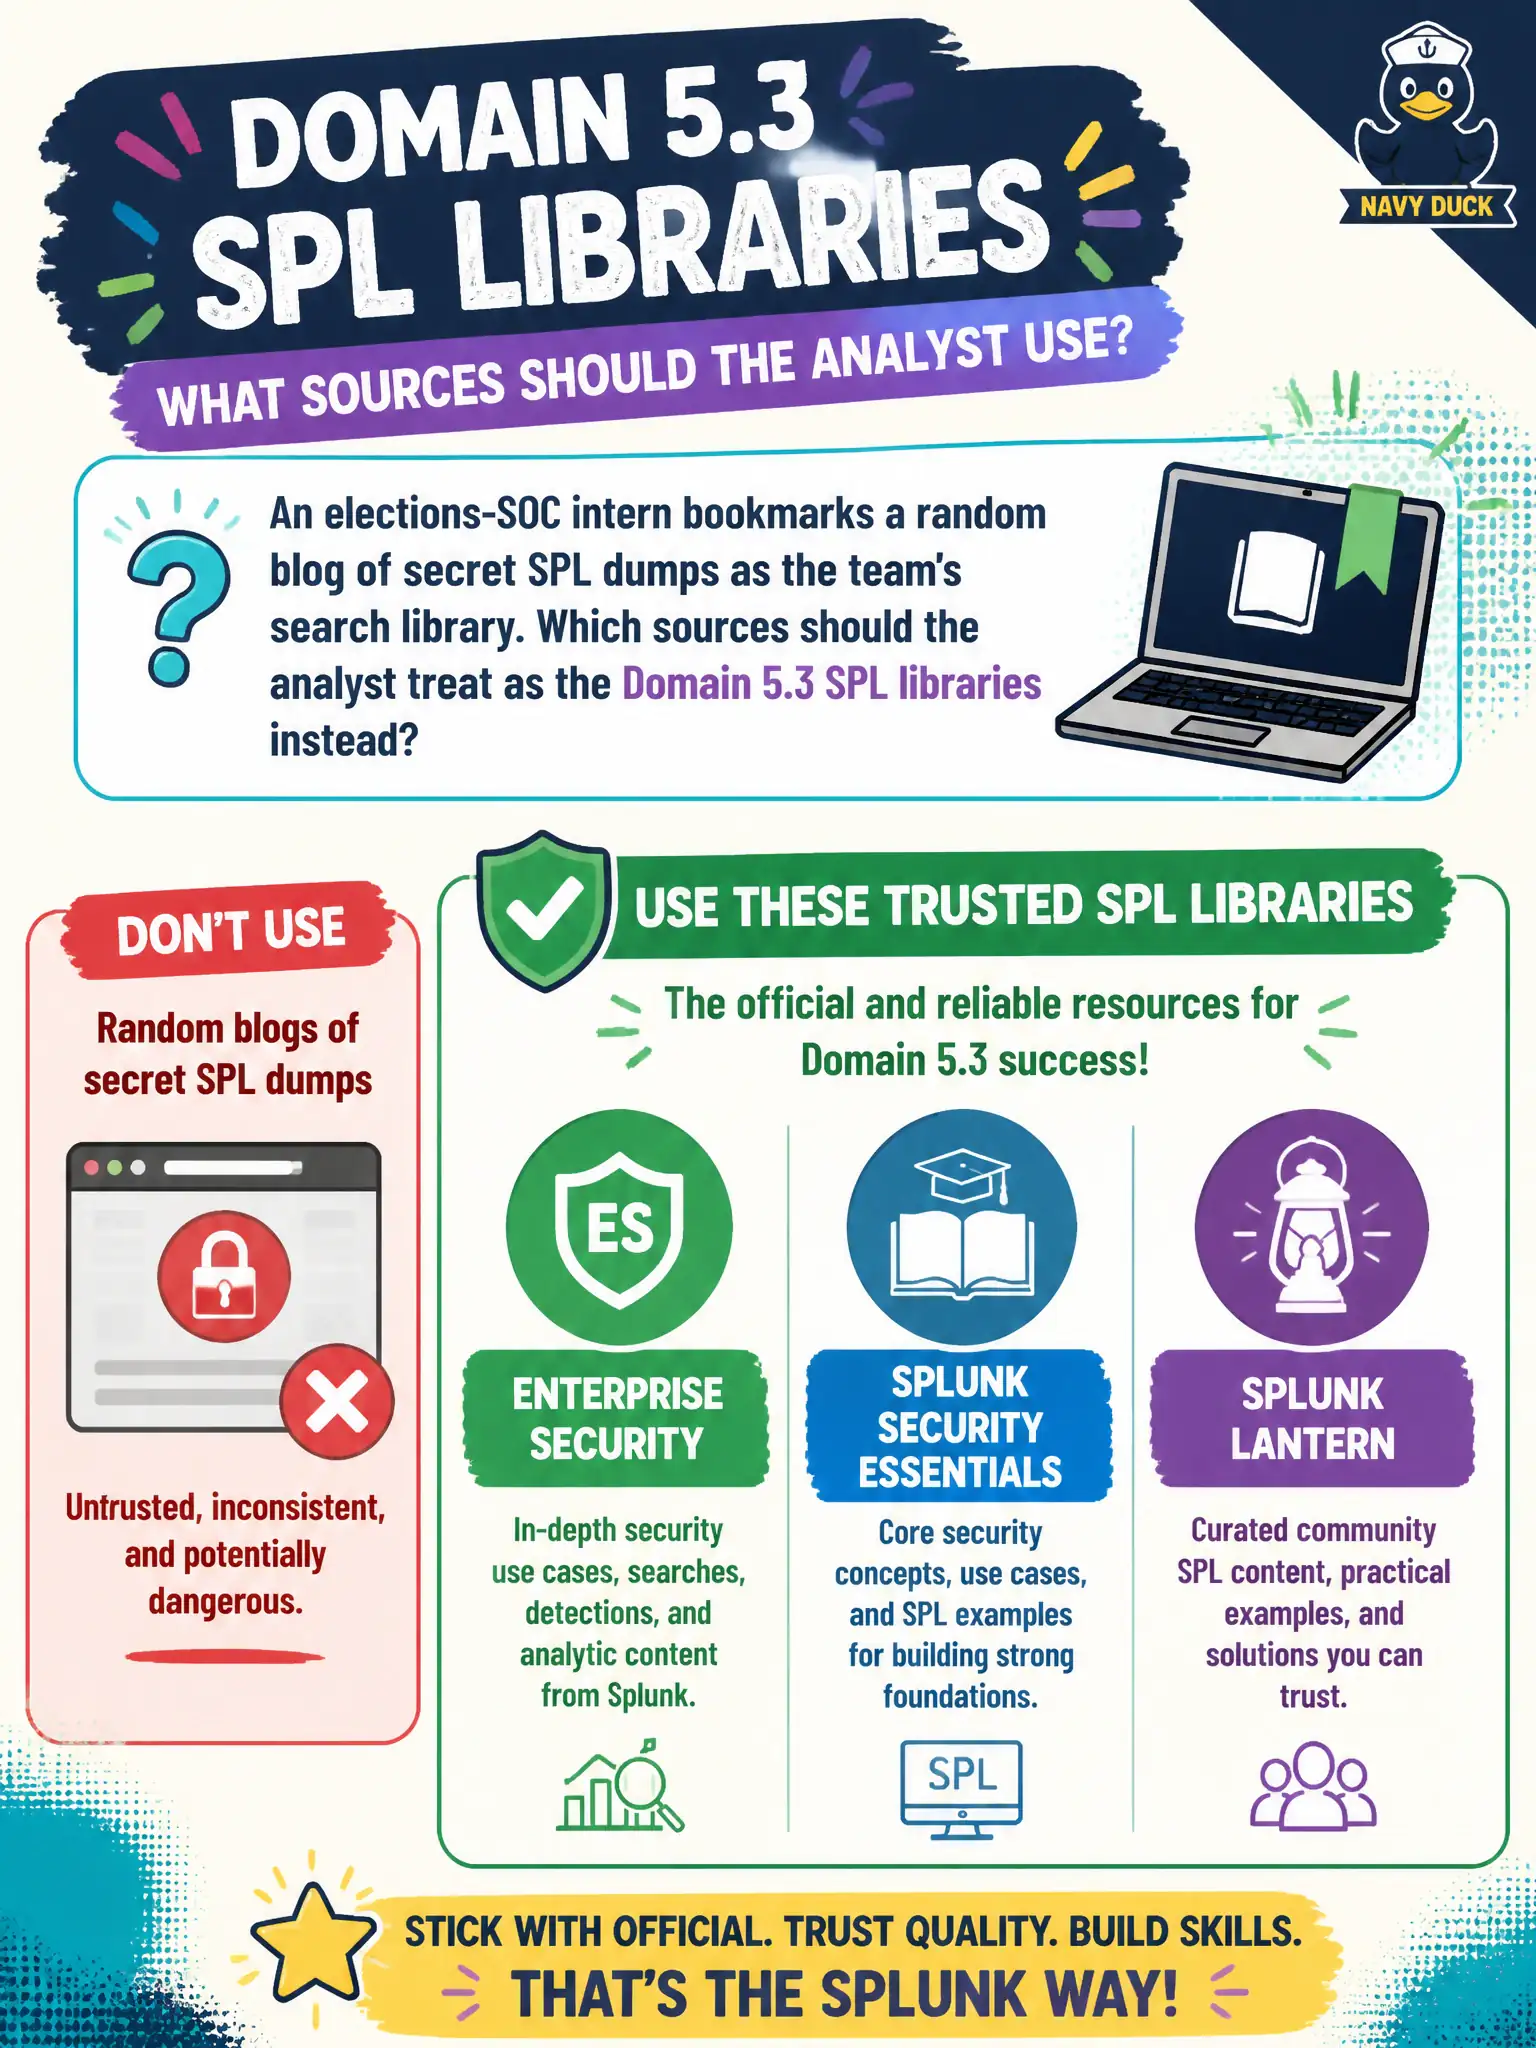
An elections-SOC intern bookmarks a random blog of secret SPL dumps as the team's search library. Which sources should the analyst treat as the Domain 5.3 SPL libraries instead?
Select an answer to reveal the explanation.
Short Explanation
Boss of the SOC videos are fine study material, but they are not the in-product SPL library. For 5.3 the named shelves are ES, Security Essentials, and Lantern. Random blogs and dumps are not canon.
Full Explanation
For Domain 5.3-style SPL libraries, the named civic sources of truth are Enterprise Security, Splunk Security Essentials, and Splunk Lantern—not random blogs of secret SPL dumps. Unofficial gist collections and exam-dump forums that claim real exam SPL are neither authoritative nor appropriate study or production sources. License-master CSV exports and deployment-server app lists describe platform inventory, not investigation search libraries. CompTIA Security+ command references with Splunk field names stapled on are sibling-cert material, not the Splunk defense-analyst content stack. Boss of the SOC videos can be useful practice, but they are not a substitute for the in-product and official libraries named above. Exam caveat: when unofficial content conflicts with ES/SSE/Lantern/Docs, follow the official stack even if the blog claims to be newer or 'real exam' material. Operational check: replace the intern's random-blog bookmark list with links to ES correlation searches, SSE, and Lantern; require new elections-SOC searches to cite which official source they were adapted from. Document the revised approach in the civic SOC runbook so the next on-call analyst inherits the correct pattern rather than the anti-pattern. Retain Job Inspector evidence with the change ticket for municipal audit readiness.