
A parks-department SOC lead needs analysts to keep Enterprise Security, Splunk Security Essentials, and Splunk Lantern straight. Which assignment is correct?
Select an answer to reveal the explanation.
Short Explanation
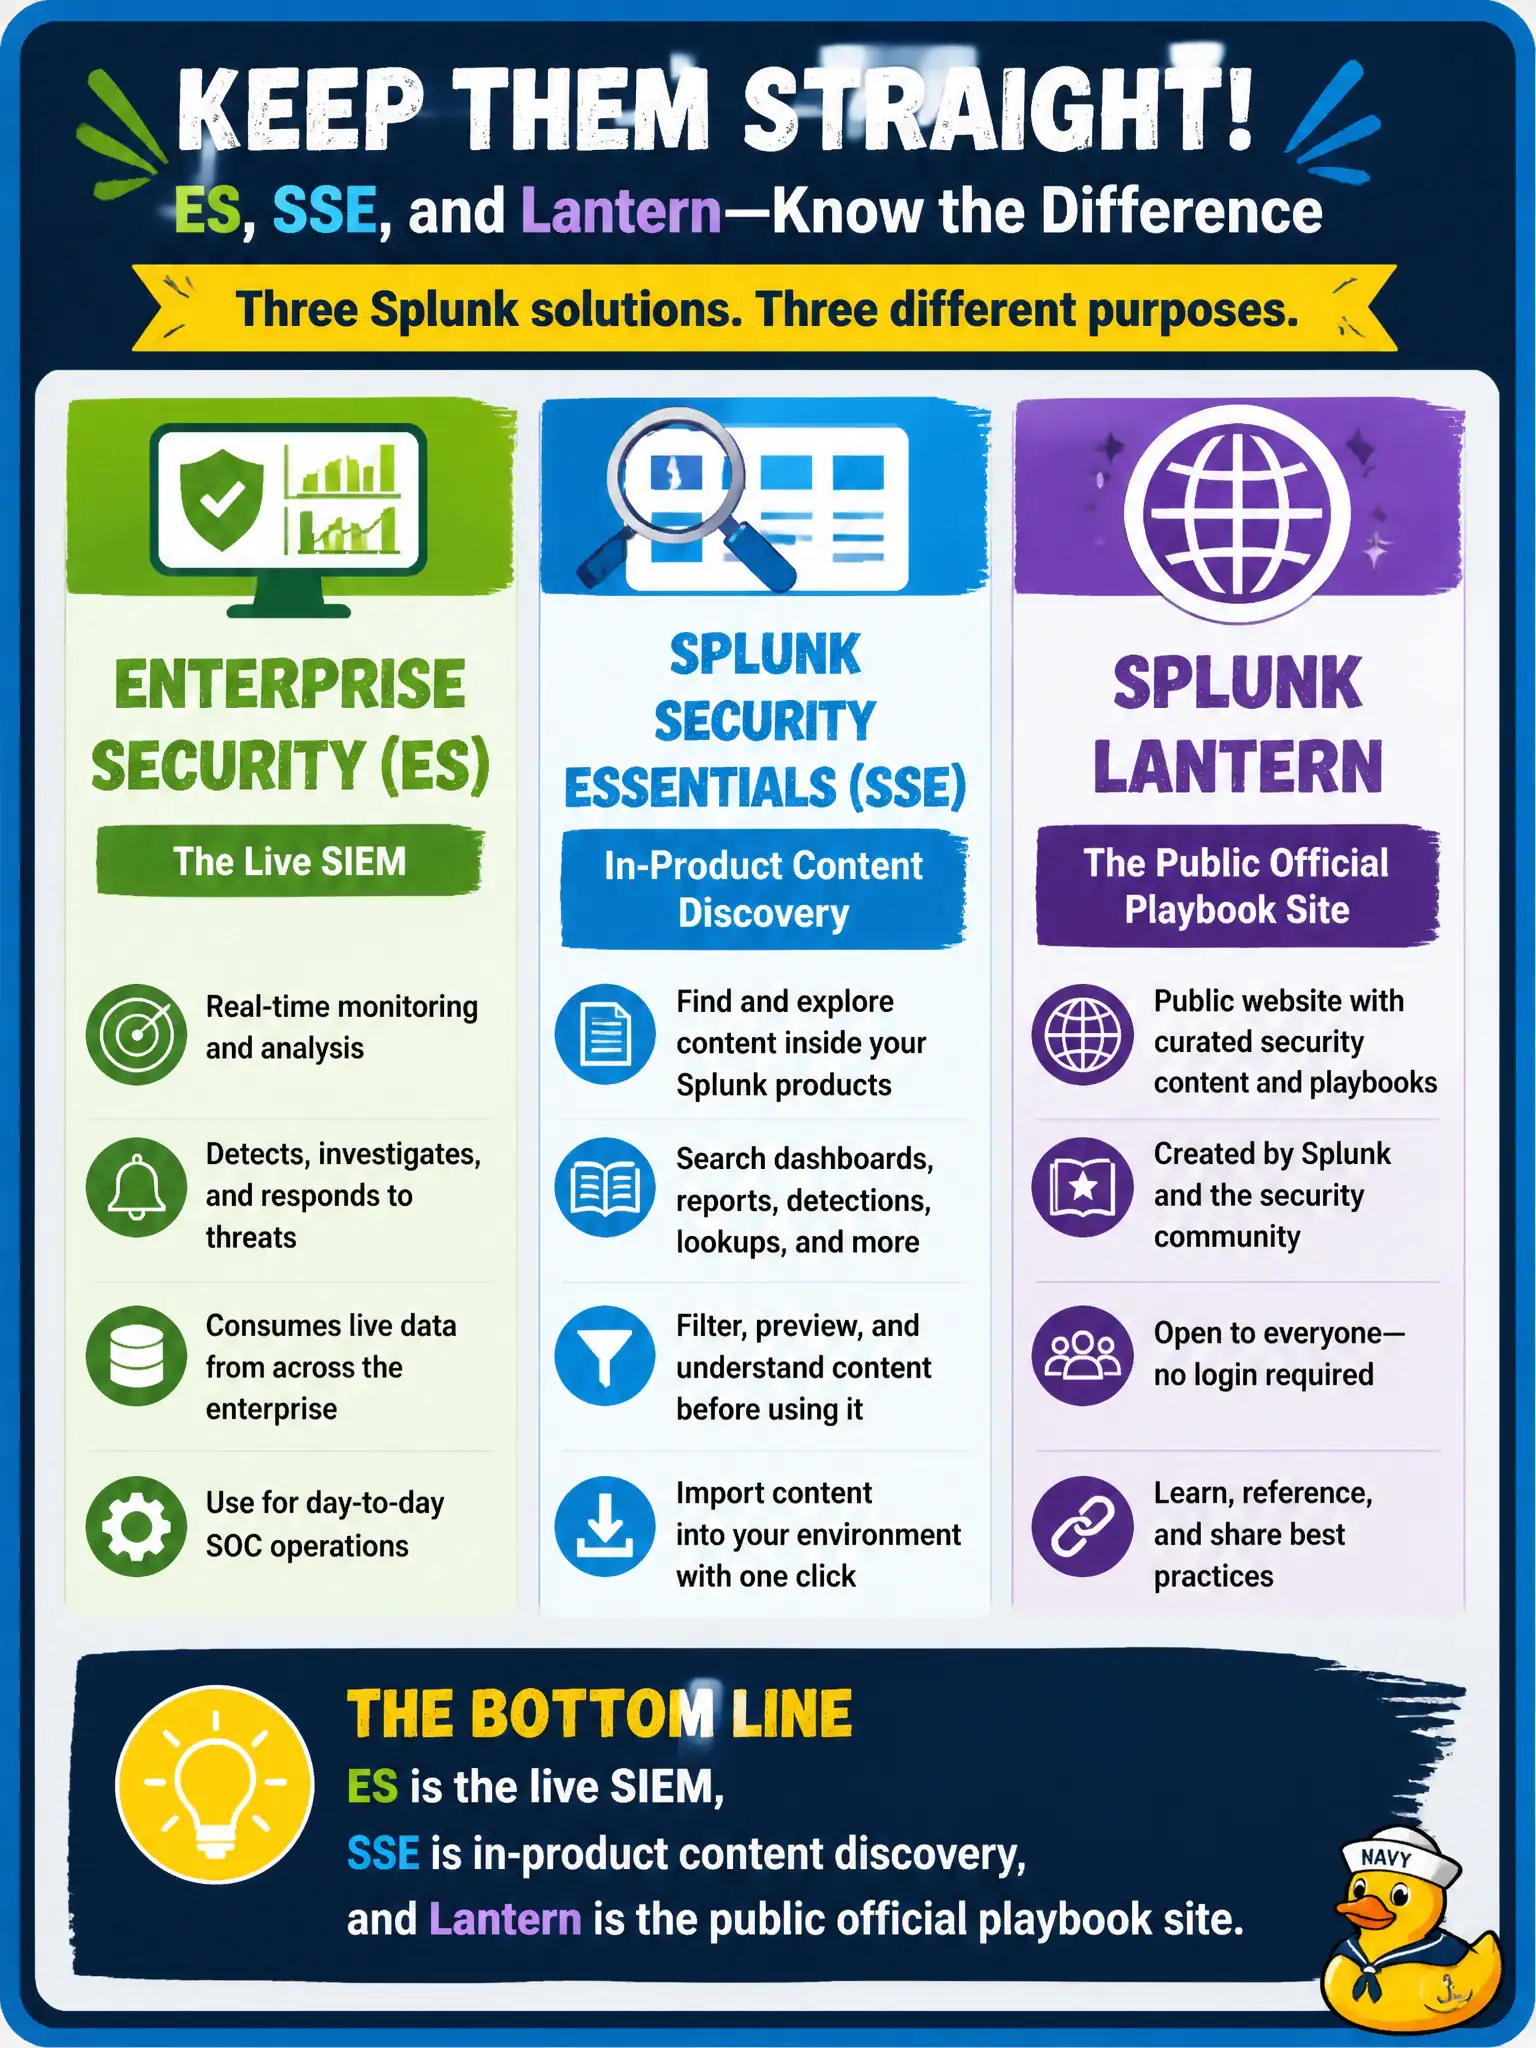
Three tools, three jobs: ES is the live SIEM where notables live, SSE is the in-product catalog of searches and data-source maps, and Lantern is the public official how-to site. Swap those labels and parks analysts look in the wrong building.
Full Explanation
Parks-department analysts must keep three Splunk surfaces distinct: Enterprise Security is the live SIEM where notables and investigations run; Splunk Security Essentials is in-product content discovery for searches and data-source mappings; Splunk Lantern is the public official how-to and playbook site with example searches. Swapping those labels sends analysts to the wrong building—treating ES as a blog, SSE as the SIEM, or Lantern as a CIM installer breaks civic workflows. ES does not primarily author Python playbooks, SSE does not size indexers, and Lantern does not assign notable dispositions. SSE is not the live SIEM, and Lantern is not a sourcetype add-on. Exam caveat: content often moves from Lantern/SSE learning into ES production detections—knowing which tool is live operations versus guidance prevents 'I enabled it in Lantern' confusion. Operational check: walk a new parks analyst through opening one live notable in ES, one bookmark in SSE, and one Lantern guide, and have them state which system is SIEM, which is content discovery, and which is the public playbook site. Document the revised approach in the civic SOC runbook so the next on-call analyst inherits the correct pattern rather than the anti-pattern. Retain Job Inspector evidence with the change ticket for municipal audit readiness.