
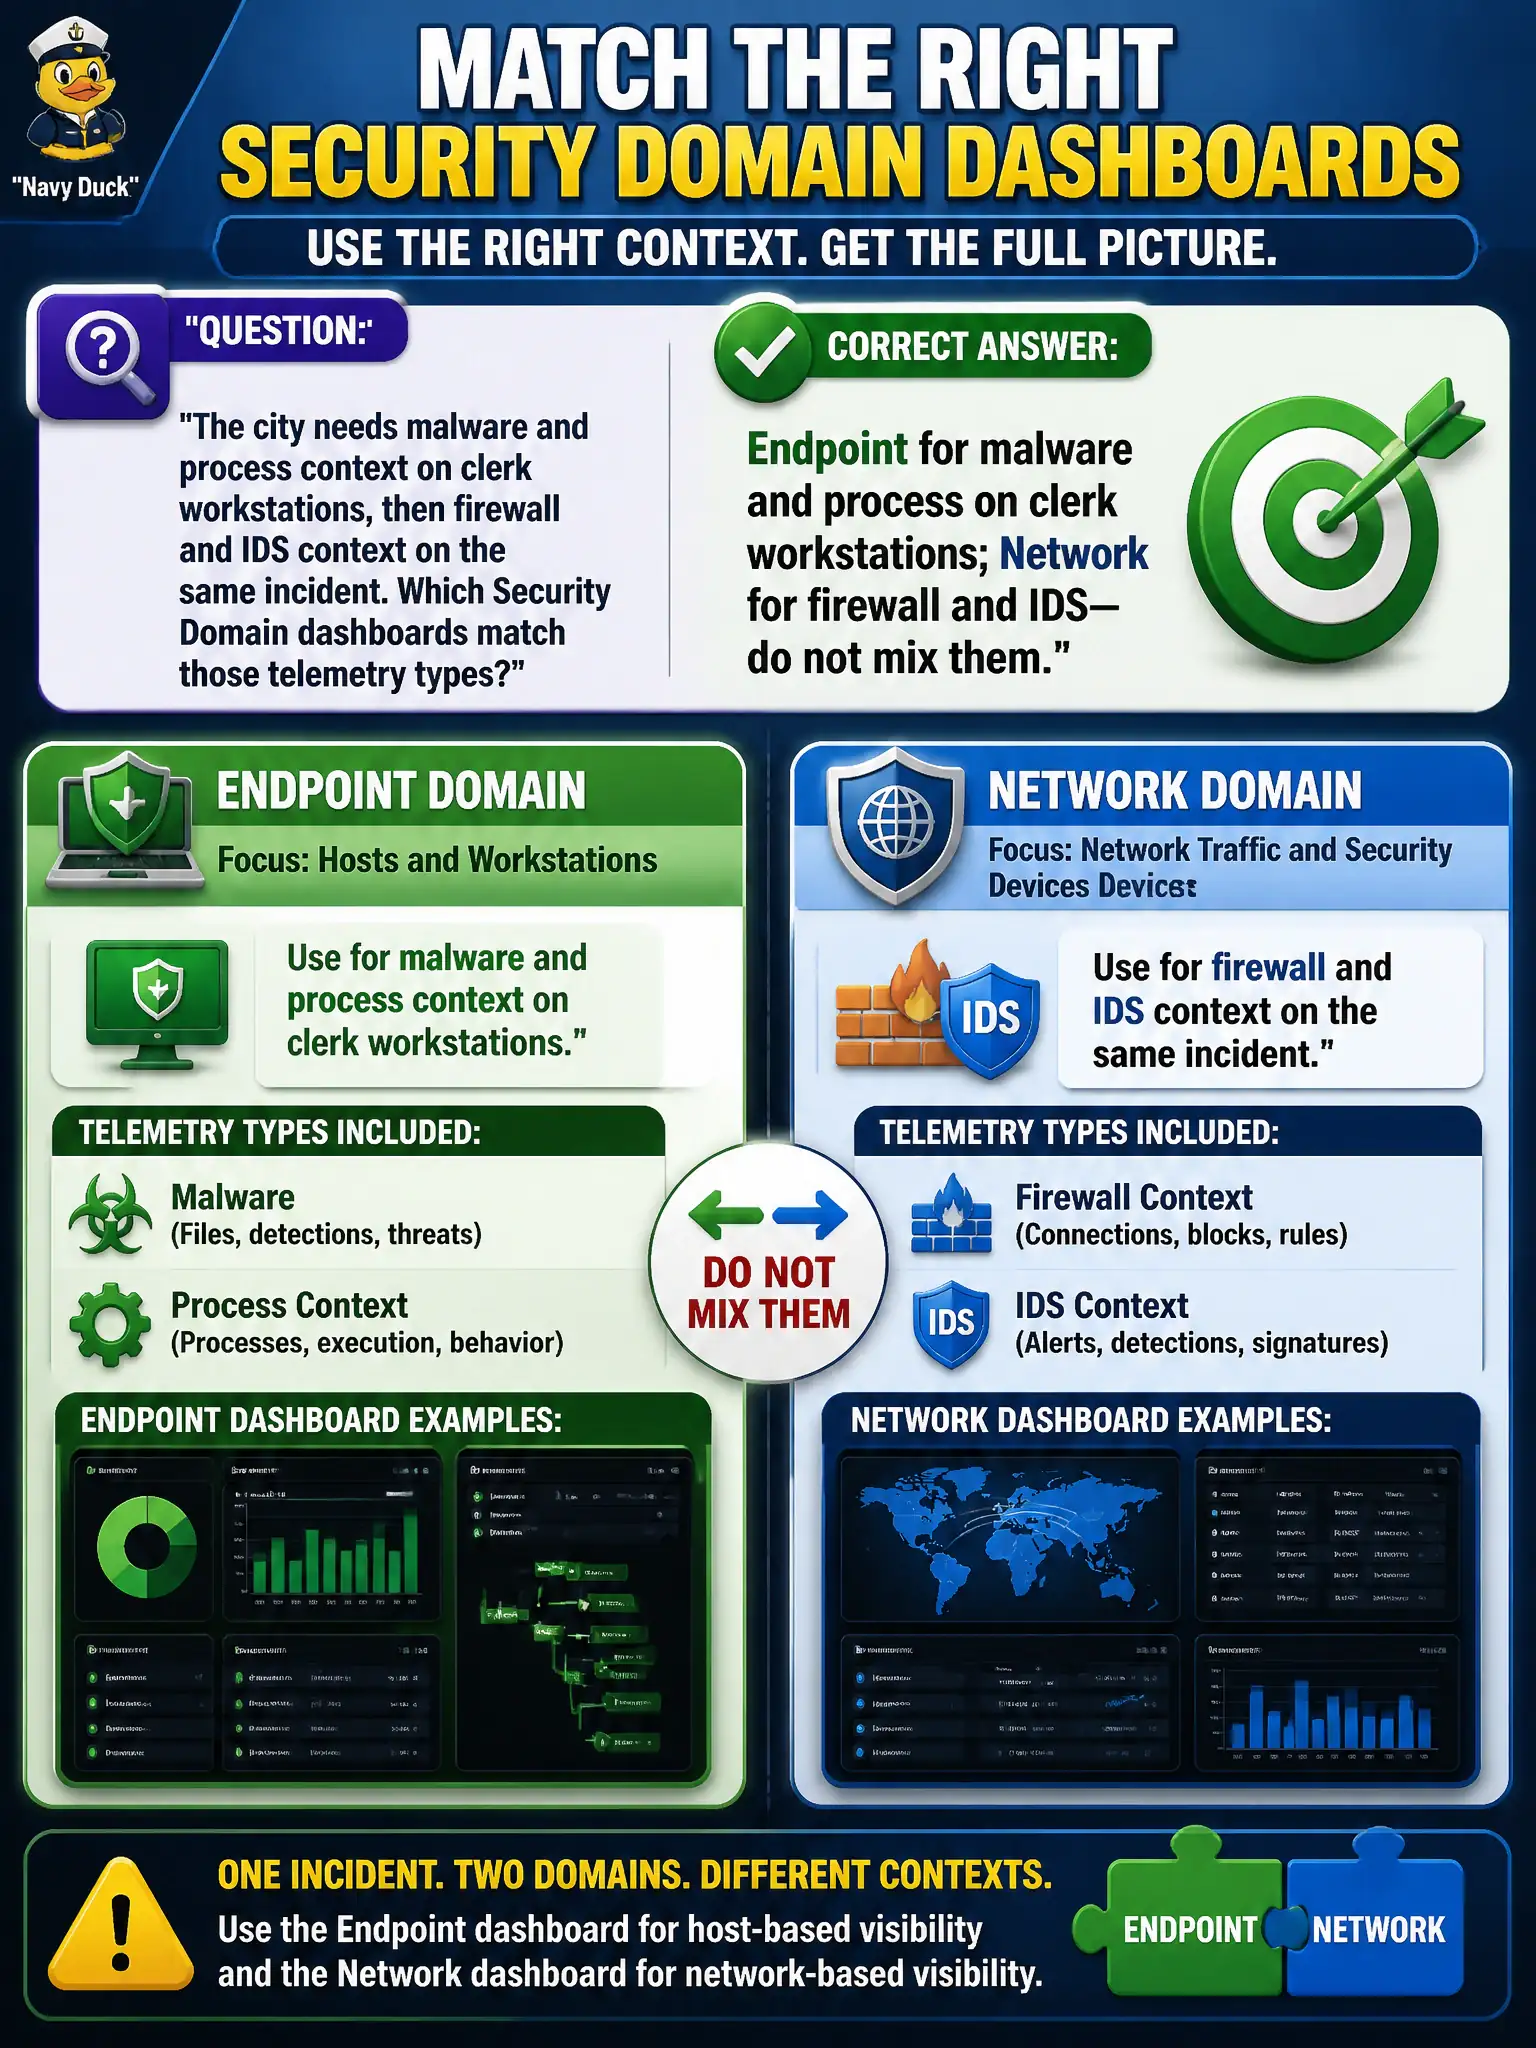
The city needs malware and process context on clerk workstations, then firewall and IDS context on the same incident. Which Security Domain dashboards match those telemetry types?
Select an answer to reveal the explanation.
Short Explanation
Process trees live on Endpoint; firewall and IDS live on Network. Swapping those dashboards is like looking for a virus on the street map. Domain dashboards follow the telemetry, not the other way around.
Full Explanation
Endpoint Security Domain dashboards provide malware and process context on clerk workstations; Network domain dashboards provide firewall and IDS context on the same civic incident. Analysts should match telemetry type to domain and not swap them when pivoting. Putting process names on Network and firewall denies on Endpoint fails by concept because that mixes schemas and yields empty or misleading panels that waste time during response. Using Security Posture for packet-level process trees fails by concept because Posture is an overview of notables by domain and urgency for briefings, not deep process trees or packet analysis. Using Incident Review Audit for both because domain dashboards are supposedly only for CIO slides fails by concept because Audit tracks analyst workflow history, while domain dashboards are operational investigation surfaces for Endpoint and Network evidence. Exam caveat: SPLK-5001 expects correct Security Domain selection by data type for municipal incidents spanning endpoint and network. Operational check: for a clerk incident, open Endpoint for process and malware, open Network for firewall and IDS, confirm each domain has mapped data, and avoid forcing the wrong domain to answer the other question.