
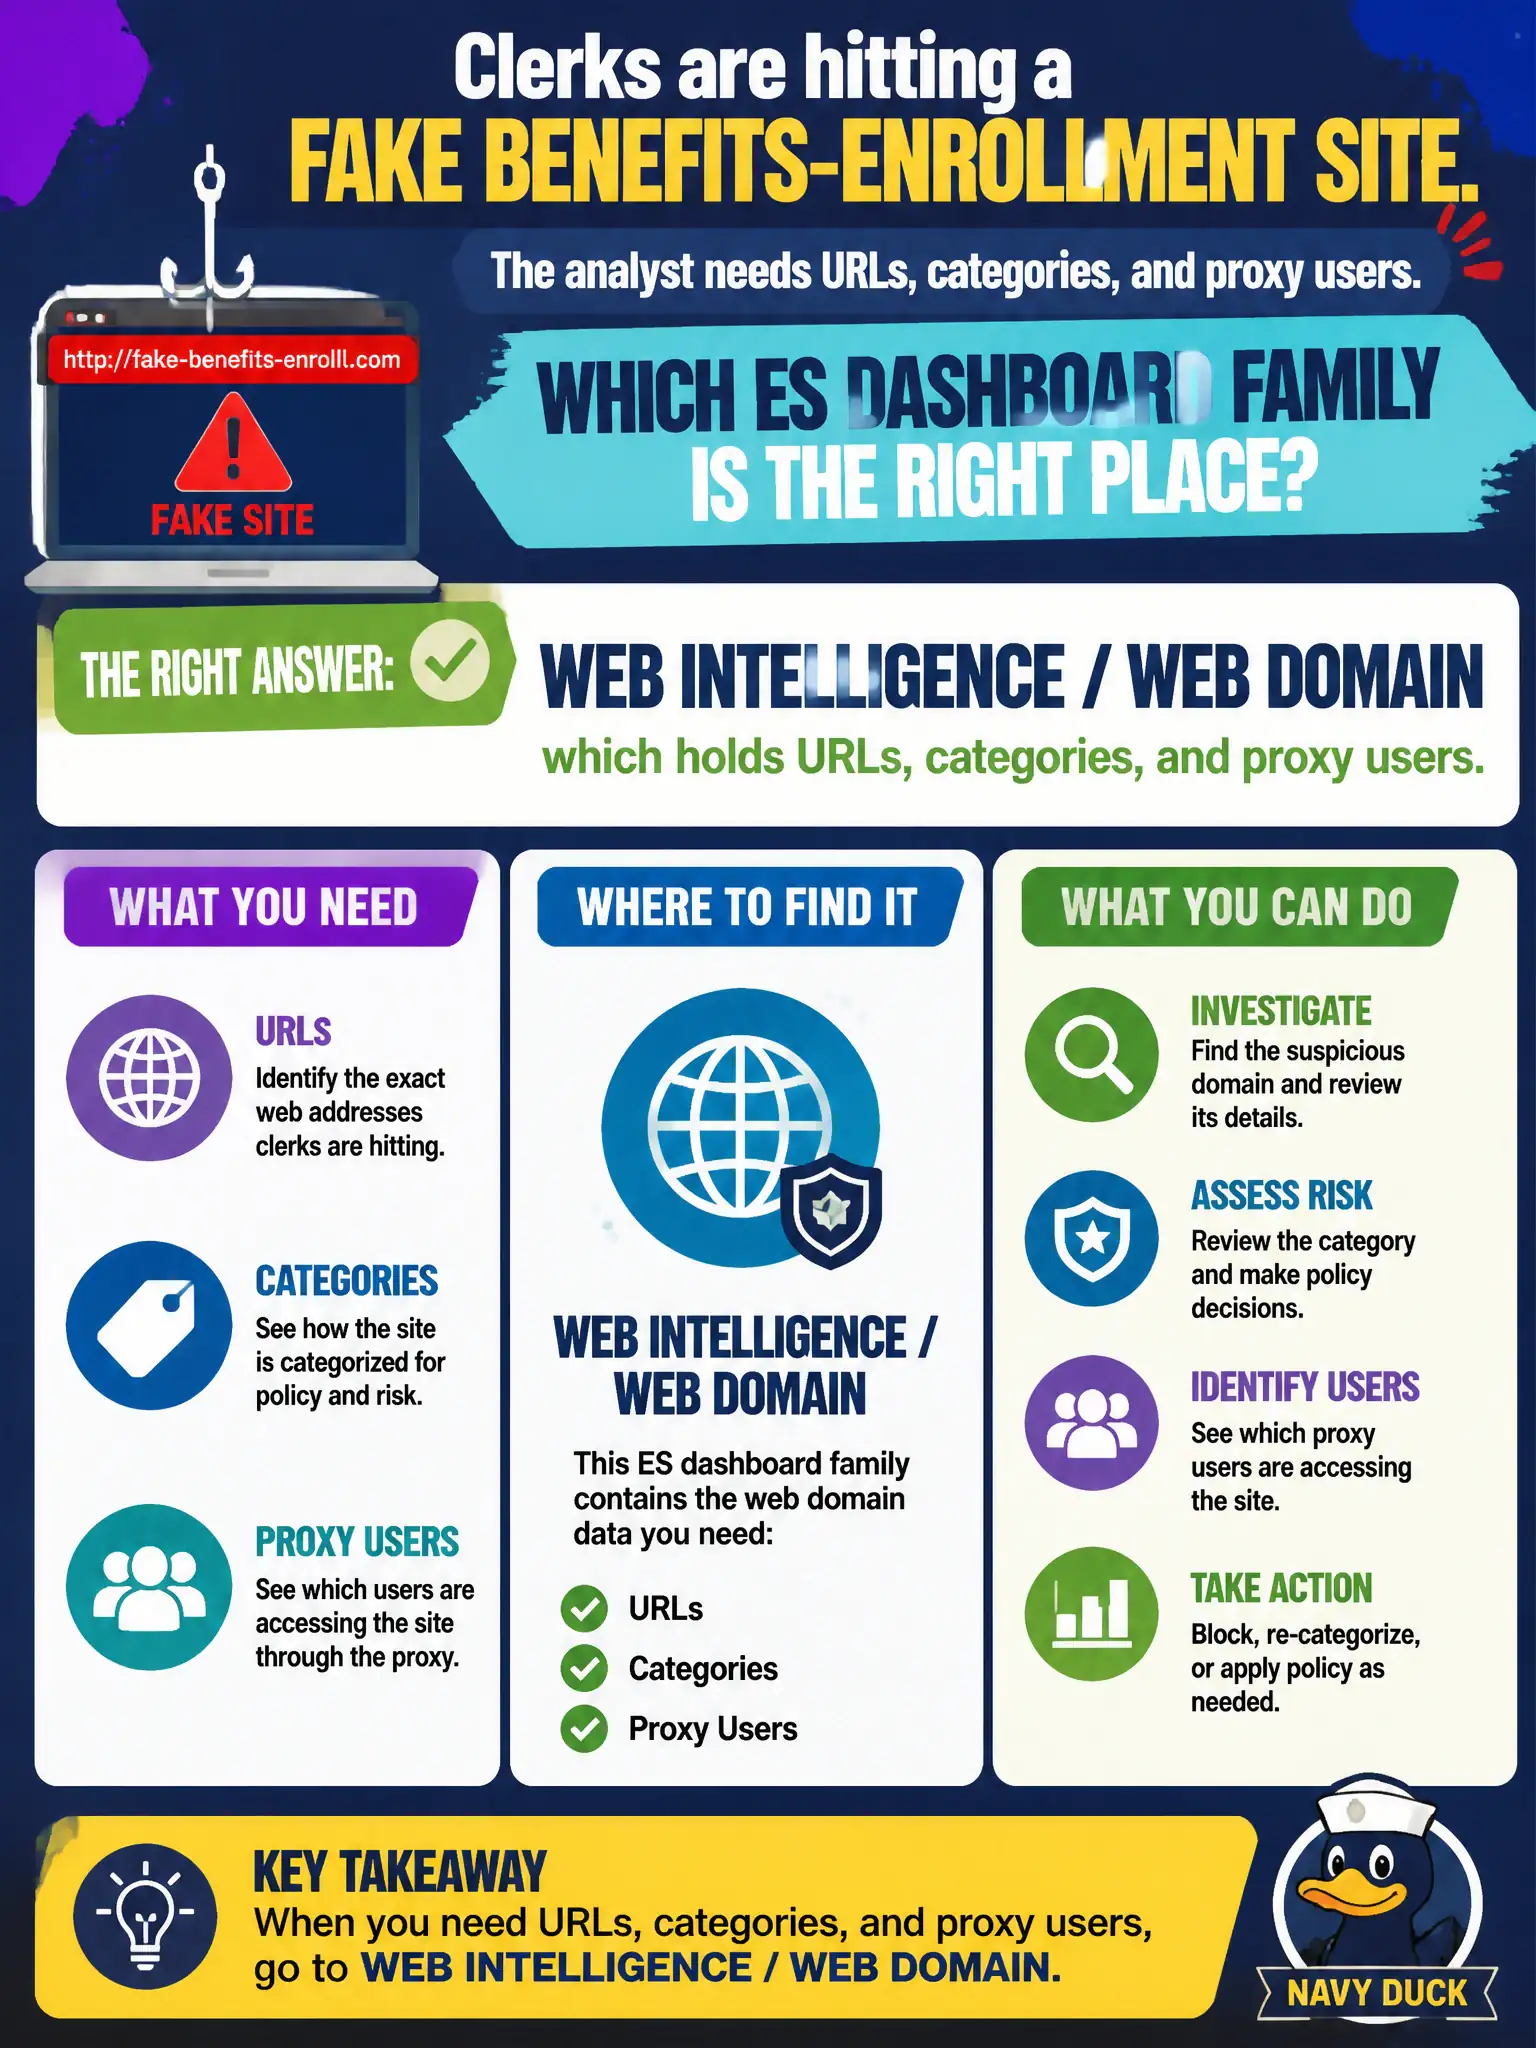
Clerks are hitting a fake benefits-enrollment site. The analyst needs URLs, categories, and proxy users. Which ES dashboard family is the right place?
Select an answer to reveal the explanation.
Short Explanation
A fake benefits site is a web question—URLs, categories, who hit the proxy. That is Web Intelligence, not the identity-anomaly or malware pane as the first stop. Don't file every URL as a risk object either.
Full Explanation
URLs, URL categories, and proxy users for clerks hitting a fake benefits-enrollment site belong in Web Intelligence / the Web security domain. Those Enterprise Security dashboards and the Web data model are built for web-gateway and proxy investigations that answer who browsed what. Access Anomalies fails by concept as the primary place because the enrollment lure analysis is a web and URL problem first, even though identity anomalies may appear as a secondary pivot. Endpoint fails by concept when treating every fake site automatically as host malware; the immediate evidence is browsing and proxy telemetry, not necessarily a process compromise yet. Risk Analysis fails by concept as the store of every URL as a risk object; risk views show scored objects and contributing risk, not the Web domain's URL and category investigation workflow. Exam caveat: SPLK-5001 maps URL and proxy questions to the Web domain for civic phishing and watering-hole style cases. Operational check: open Web Intelligence or the Web domain, filter to the fake enrollment URL or category and affected proxy users, corroborate with related searches, then add Endpoint or Access pivots only if hosts or accounts show further compromise.