
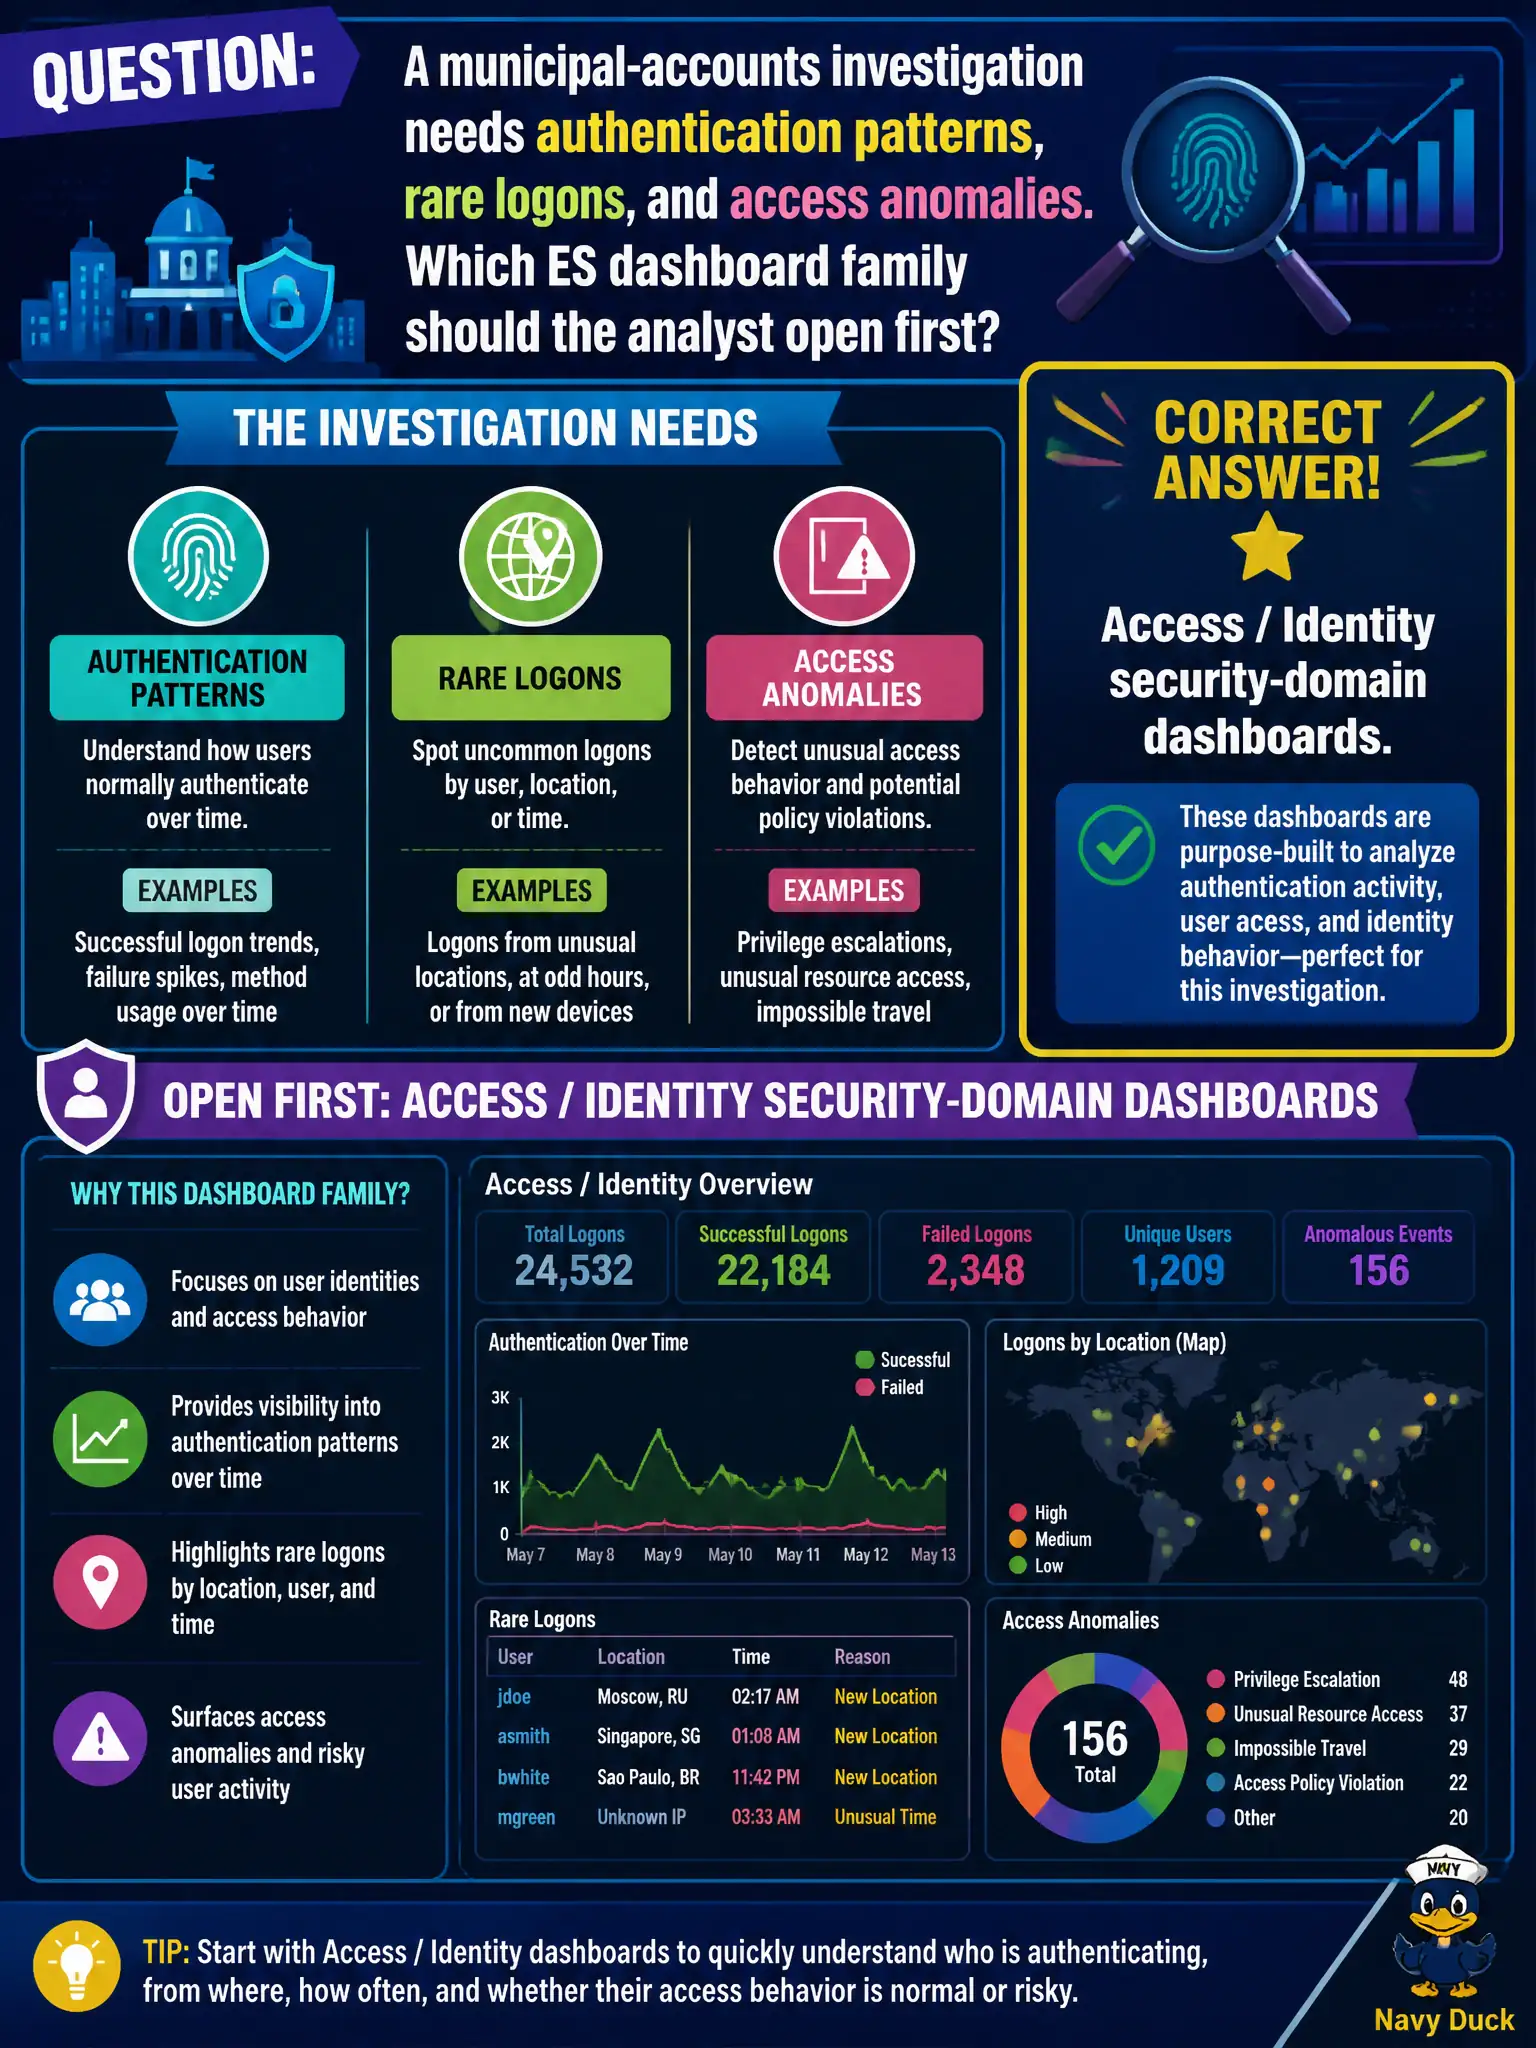
A municipal-accounts investigation needs authentication patterns, rare logons, and access anomalies. Which ES dashboard family should the analyst open first?
Select an answer to reveal the explanation.
Short Explanation
Badge-reader questions live on Access and Identity. Rare logons and municipal-account oddities are not first a malware, URL, or DNS dashboard. Match the domain to the telemetry.
Full Explanation
Authentication patterns, rare logons, and access anomalies for a municipal-accounts investigation belong first in Access / Identity security-domain dashboards. Those Enterprise Security views are built around identity and access telemetry once CIM Authentication and related sources are populated and mapped. Opening only the Endpoint malware dashboard fails by concept because malware and process context do not replace access-pattern analysis when the question is who logged on, from where, and how unusually. Using Web Intelligence URL categories only fails by concept because URL category views answer web browsing and proxy questions, not logon rarity and account access anomalies. Using Protocol Intelligence DNS only fails by concept because DNS protocol views may corroborate later but do not substitute for Access domain identity analytics. Exam caveat: SPLK-5001 expects analysts to choose Security Domain dashboards that match the investigation question—Access/Identity for municipal account patterns. Operational check: open Access/Identity domain dashboards for the municipal accounts case, verify Authentication-mapped data is present, review rare logons and anomalies there, and only then pivot to Endpoint or Web if evidence leads to malware or browsing.