
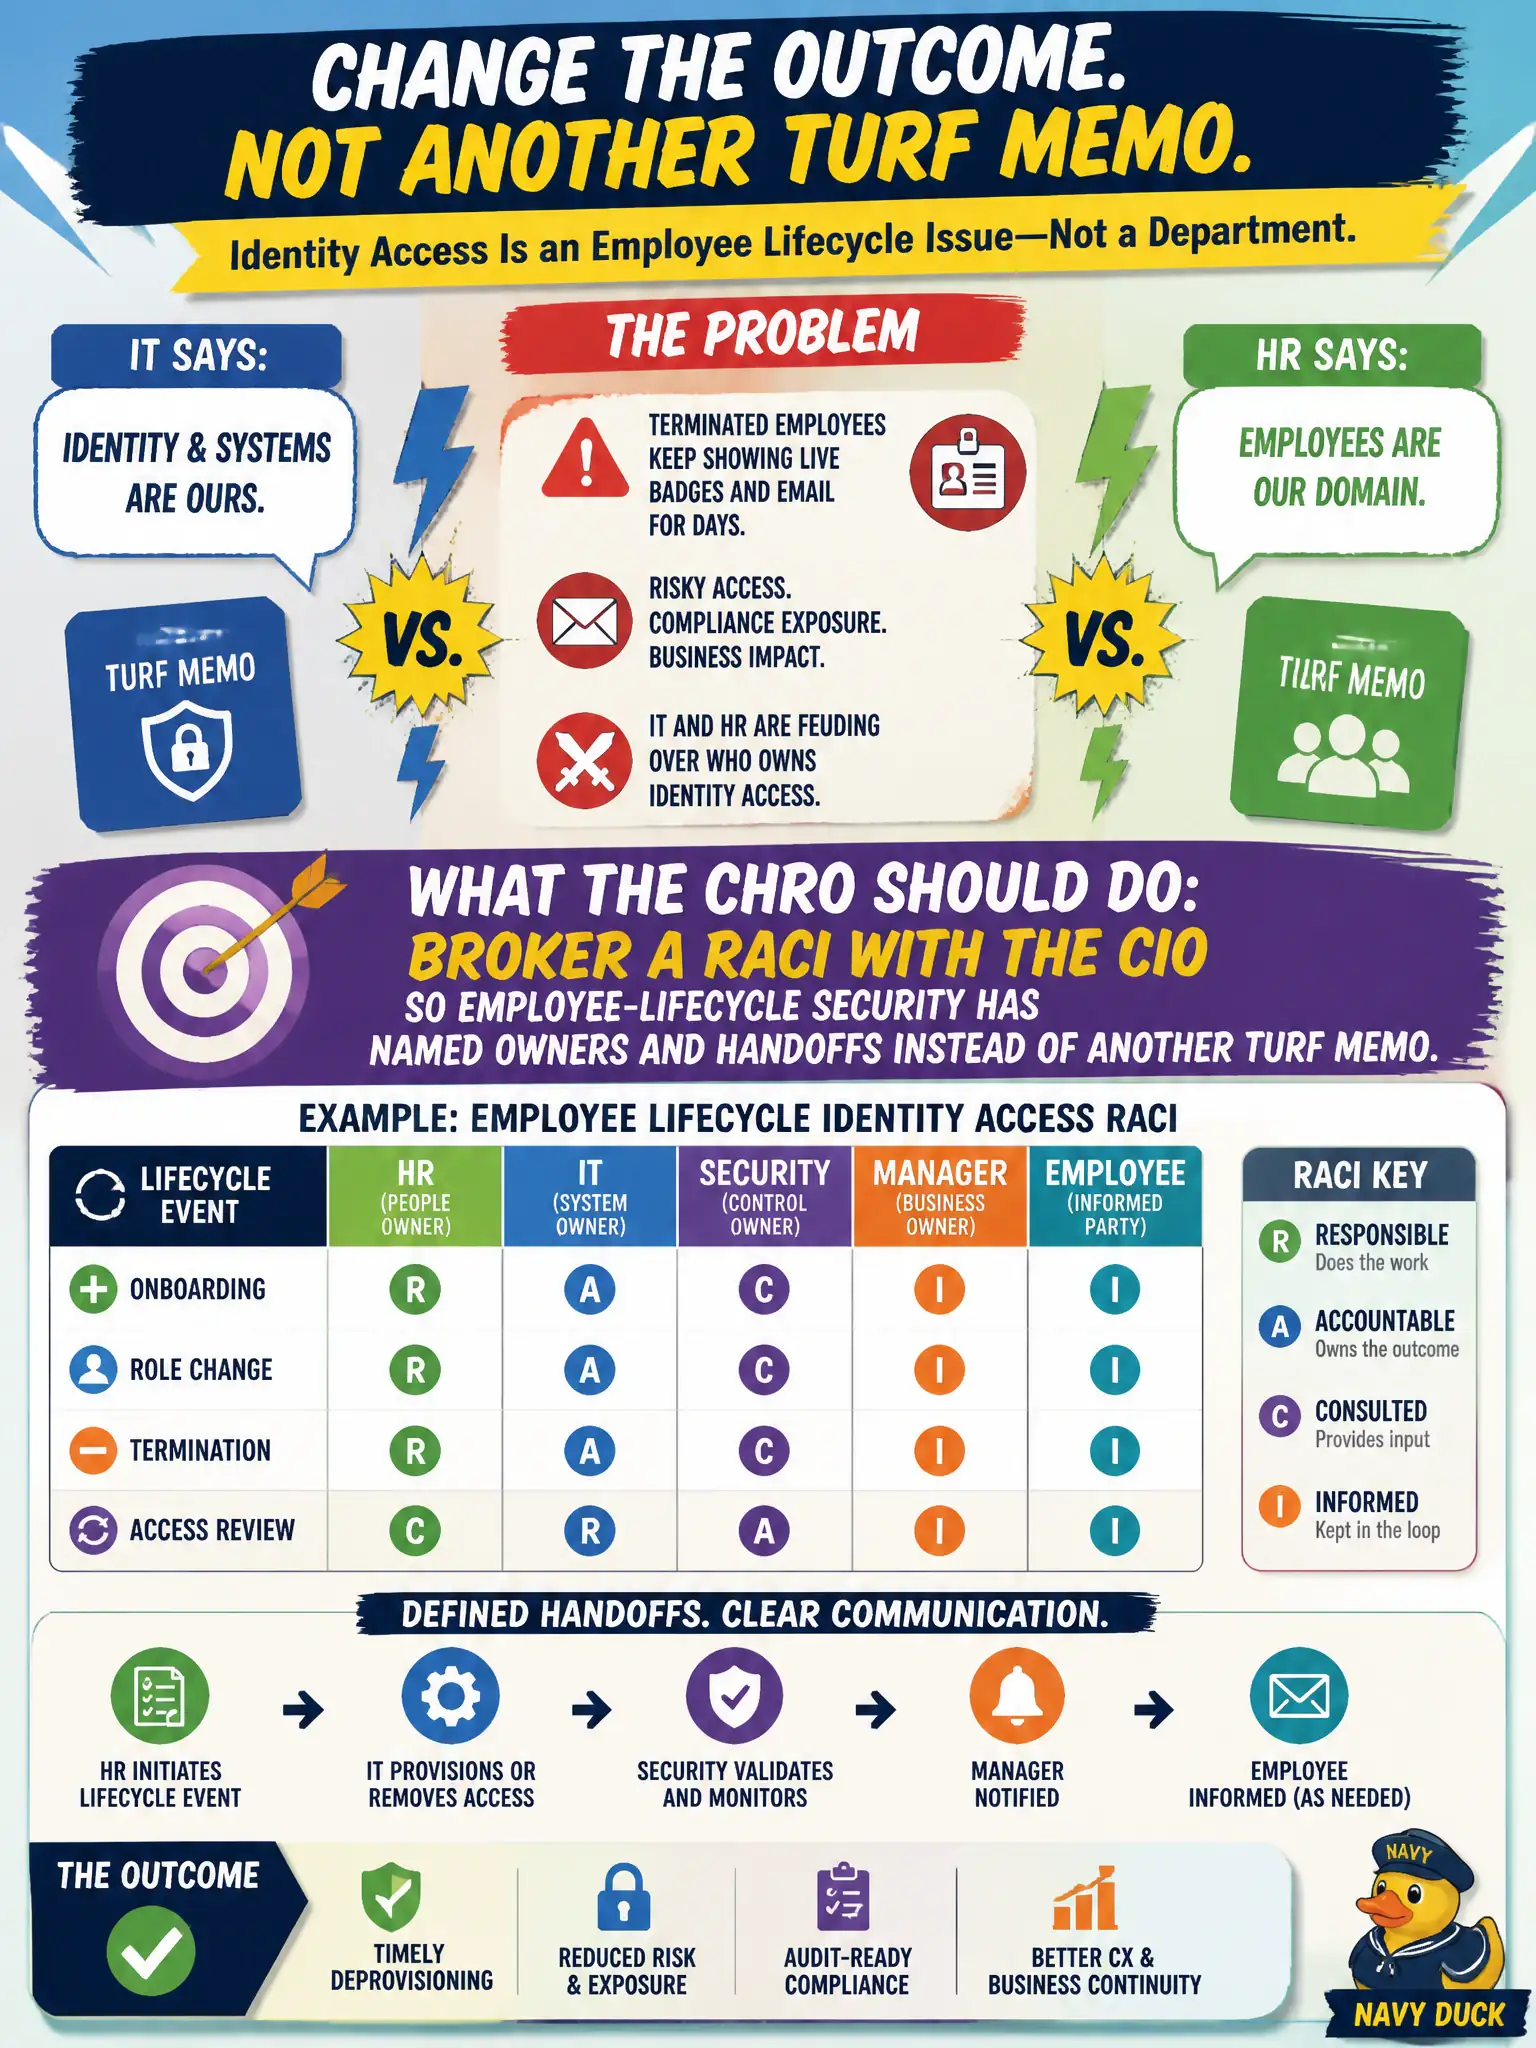
IT and HR are feuding over who owns identity access. Terminated employees keep showing live badges and email for days. Each side has already sent turf memos. What should the CHRO do to change the outcome?
Select an answer to reveal the explanation.
Short Explanation
If HR and IT are arguing about who owns the badge, the badge is still live after somebody is gone. Turf memos do not lock doors. Sit down with the CIO, write a RACI for hire-to-offboard access, and make the handoff somebody's job.
Full Explanation
Cross-function ownership fights are solved by stakeholder agreements, not serial emails. When IT and HR feud over identity access and terminated employees keep live badges and email for days, the CHRO should broker a RACI with the CIO so employee-lifecycle security has named owners and handoffs. Hire, transfer, leave, and terminate all change access; without named provisioners, revokers, and confirmers, turf memos continue while residual access remains a security and public-trust failure. The outcome that matters is locked doors after separation, not which department won the memo war.
Declaring HR sole owner of all network credentials without IT coordination ignores technical control reality and usually breaks revocation. Another ownership memo waiting for the next failed offboard is proof-by-incident, not design. Moving provisioning to department supervisors dissolves accountability into dozens of untrained owners and worsens orphaned access.
Exam caveat: a RACI is not a suggestion that access risk is only an IT problem or only an HR problem. The tested concept is joint lifecycle ownership with clear handoffs.
Operational check: draft a hire-to-offboard RACI with the CIO covering badge, email, VPN, and system roles; set a same-day revocation SLA for involuntary separations; require a confirmation receipt in the personnel file; audit residual accounts weekly for thirty days after go-live; and report residual-access aging to both executives until the backlog is zero.