
A Chief Compliance Officer is designing a review cycle for the organization's corporate compliance policies and procedures. What is the primary purpose of establishing a process for regular, periodic updates to these documents?
Select an answer to reveal the explanation.
Short Explanation
Think of compliance policies like firmware on core switches: configure once, ignore for years, and you're exposed. You need regular updates because regulations, markets, and risks keep changing. Keep them fresh, relevant, and aligned with current threats.
Full Explanation
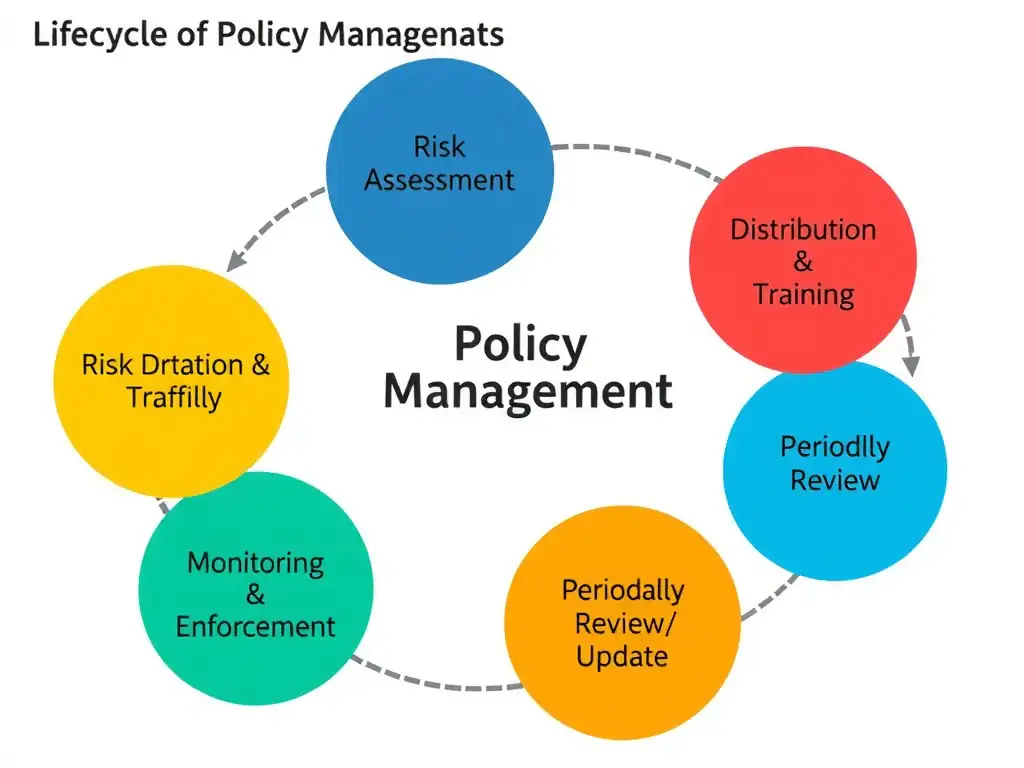
In corporate compliance, policies and procedures serve as operational controls designed to mitigate identified risks. However, the internal and external environments of any business are constantly shifting. External factors such as new legislation, regulatory changes, and evolving industry standards directly affect what constitutes compliant behavior. Internally, mergers, acquisitions, new product launches, and technological adoptions alter the company's operational footprint and risk profile. Therefore, the primary purpose of regularly reviewing and updating policies and procedures is to ensure they remain relevant, aligned with the current regulatory environment, and responsive to new or emerging risks.
The choice focused on proving to external regulators that the organization has achieved a permanent state of compliance is incorrect because compliance is an ongoing operational reality, not a static achievement. Simply updating policies on paper does not prove compliance; the organization must also demonstrate that those policies are actively implemented, monitored, and enforced.
The choice focused on expanding the scope and complexity of guidelines to discourage employees from finding loopholes is incorrect because effective instructional design and compliance principles dictate that policies should be as concise and clear as possible. Making them longer and more complex actually decreases employee comprehension and compliance rates, creating a higher risk of policy violations.
The choice focused on eliminating the need for a dedicated compliance officer by delegating risk ownership to department heads is incorrect because updating policies is a core duty of the compliance function, not a mechanism to replace it. The compliance officer or department is still required to oversee the policy lifecycle, monitor adherence, and manage the broader compliance program.
By implementing a systematic policy review cycle, an organization ensures that its internal rules remain dynamic, legally accurate, and protective against the latest threats.