
When establishing a third-party compliance program, which of the following represents a critical due diligence pitfall that compliance professionals must avoid?
Select an answer to reveal the explanation.
Short Explanation
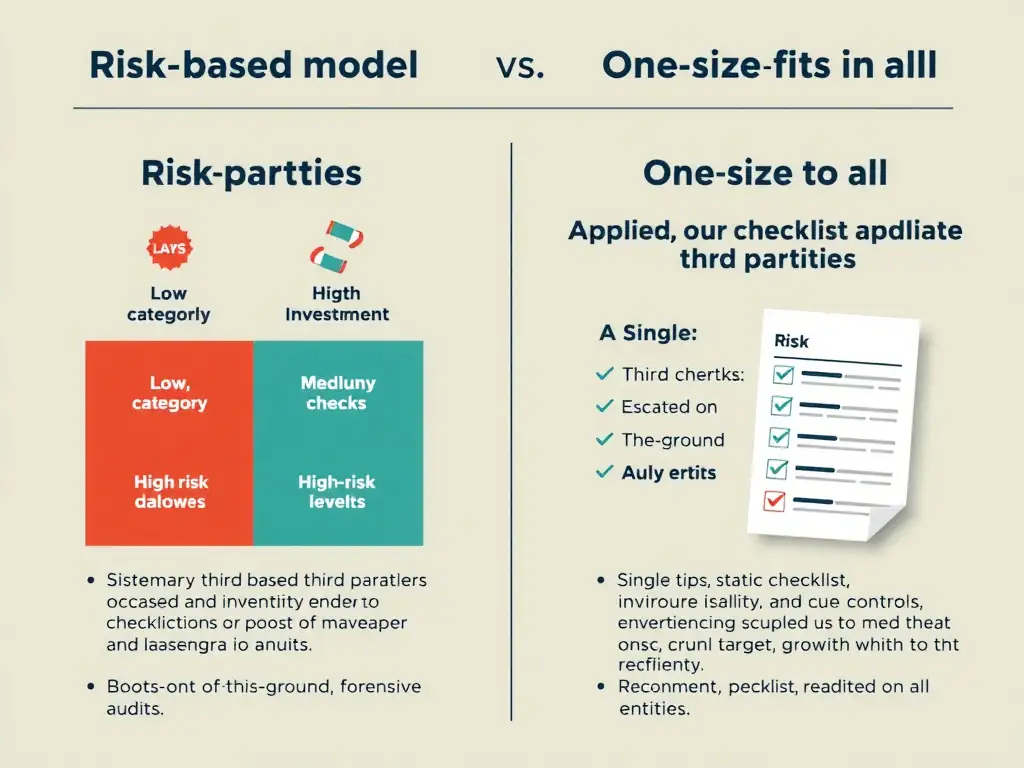
Here's the deal: you can't run the same due diligence on a low-risk office supply vendor and a high-risk offshore partner. A uniform checklist wastes resources and misses red flags where they matter most. Tailor your screening to the vendor's risk, not to a one-size-fits-all box.
Full Explanation
Effective third-party risk management is built on the principle of proportionality. A common and significant pitfall in due diligence processes is adopting a static, standardized approach—often referred to as a "one-size-fits-all" methodology—that applies the same level of scrutiny to every vendor, partner, or agent regardless of risk profile or geographic location. This approach is highly inefficient and dangerous. It fails to distinguish between low-risk suppliers, such as a local office supply company, and high-risk intermediaries, such as a customs clearance agent operating in a high-corruption jurisdiction. Without risk-based tiering, compliance resources are misallocated, and critical red flags associated with high-risk relationships can easily be overlooked.
Let's review the other choices: - Tailoring the depth of the background investigation to the specific risk tier of the vendor is incorrect because adapting the due diligence process to the risk profile of the third party is a recognized best practice, not a pitfall. It ensures that higher-risk entities receive deeper screening, such as beneficial ownership verification and political exposure checks, while lower-risk entities undergo simplified vetting. - Commencing the screening and evaluation process prior to signing a formal contract is incorrect because performing due diligence at the inception of the relationship—before any contracts are executed—is the proper sequencing. Initiating relationships before performing due diligence exposes the company to immediate legal and reputational liability. - Utilizing a multidisciplinary committee of legal, financial, and compliance experts to evaluate third-party risks is incorrect because involving a cross-functional team of experts, such as legal counsel, forensic accountants, and compliance officers, is a strength. It ensures that different dimensions of risk, such as bribery, financial insolvency, and sanctions, are thoroughly evaluated.
Regulators, including the U.S. Department of Justice, explicitly state that effective compliance programs must apply risk-based due diligence. A program that treats all third parties identically is likely to be deemed ineffective during a regulatory review.