
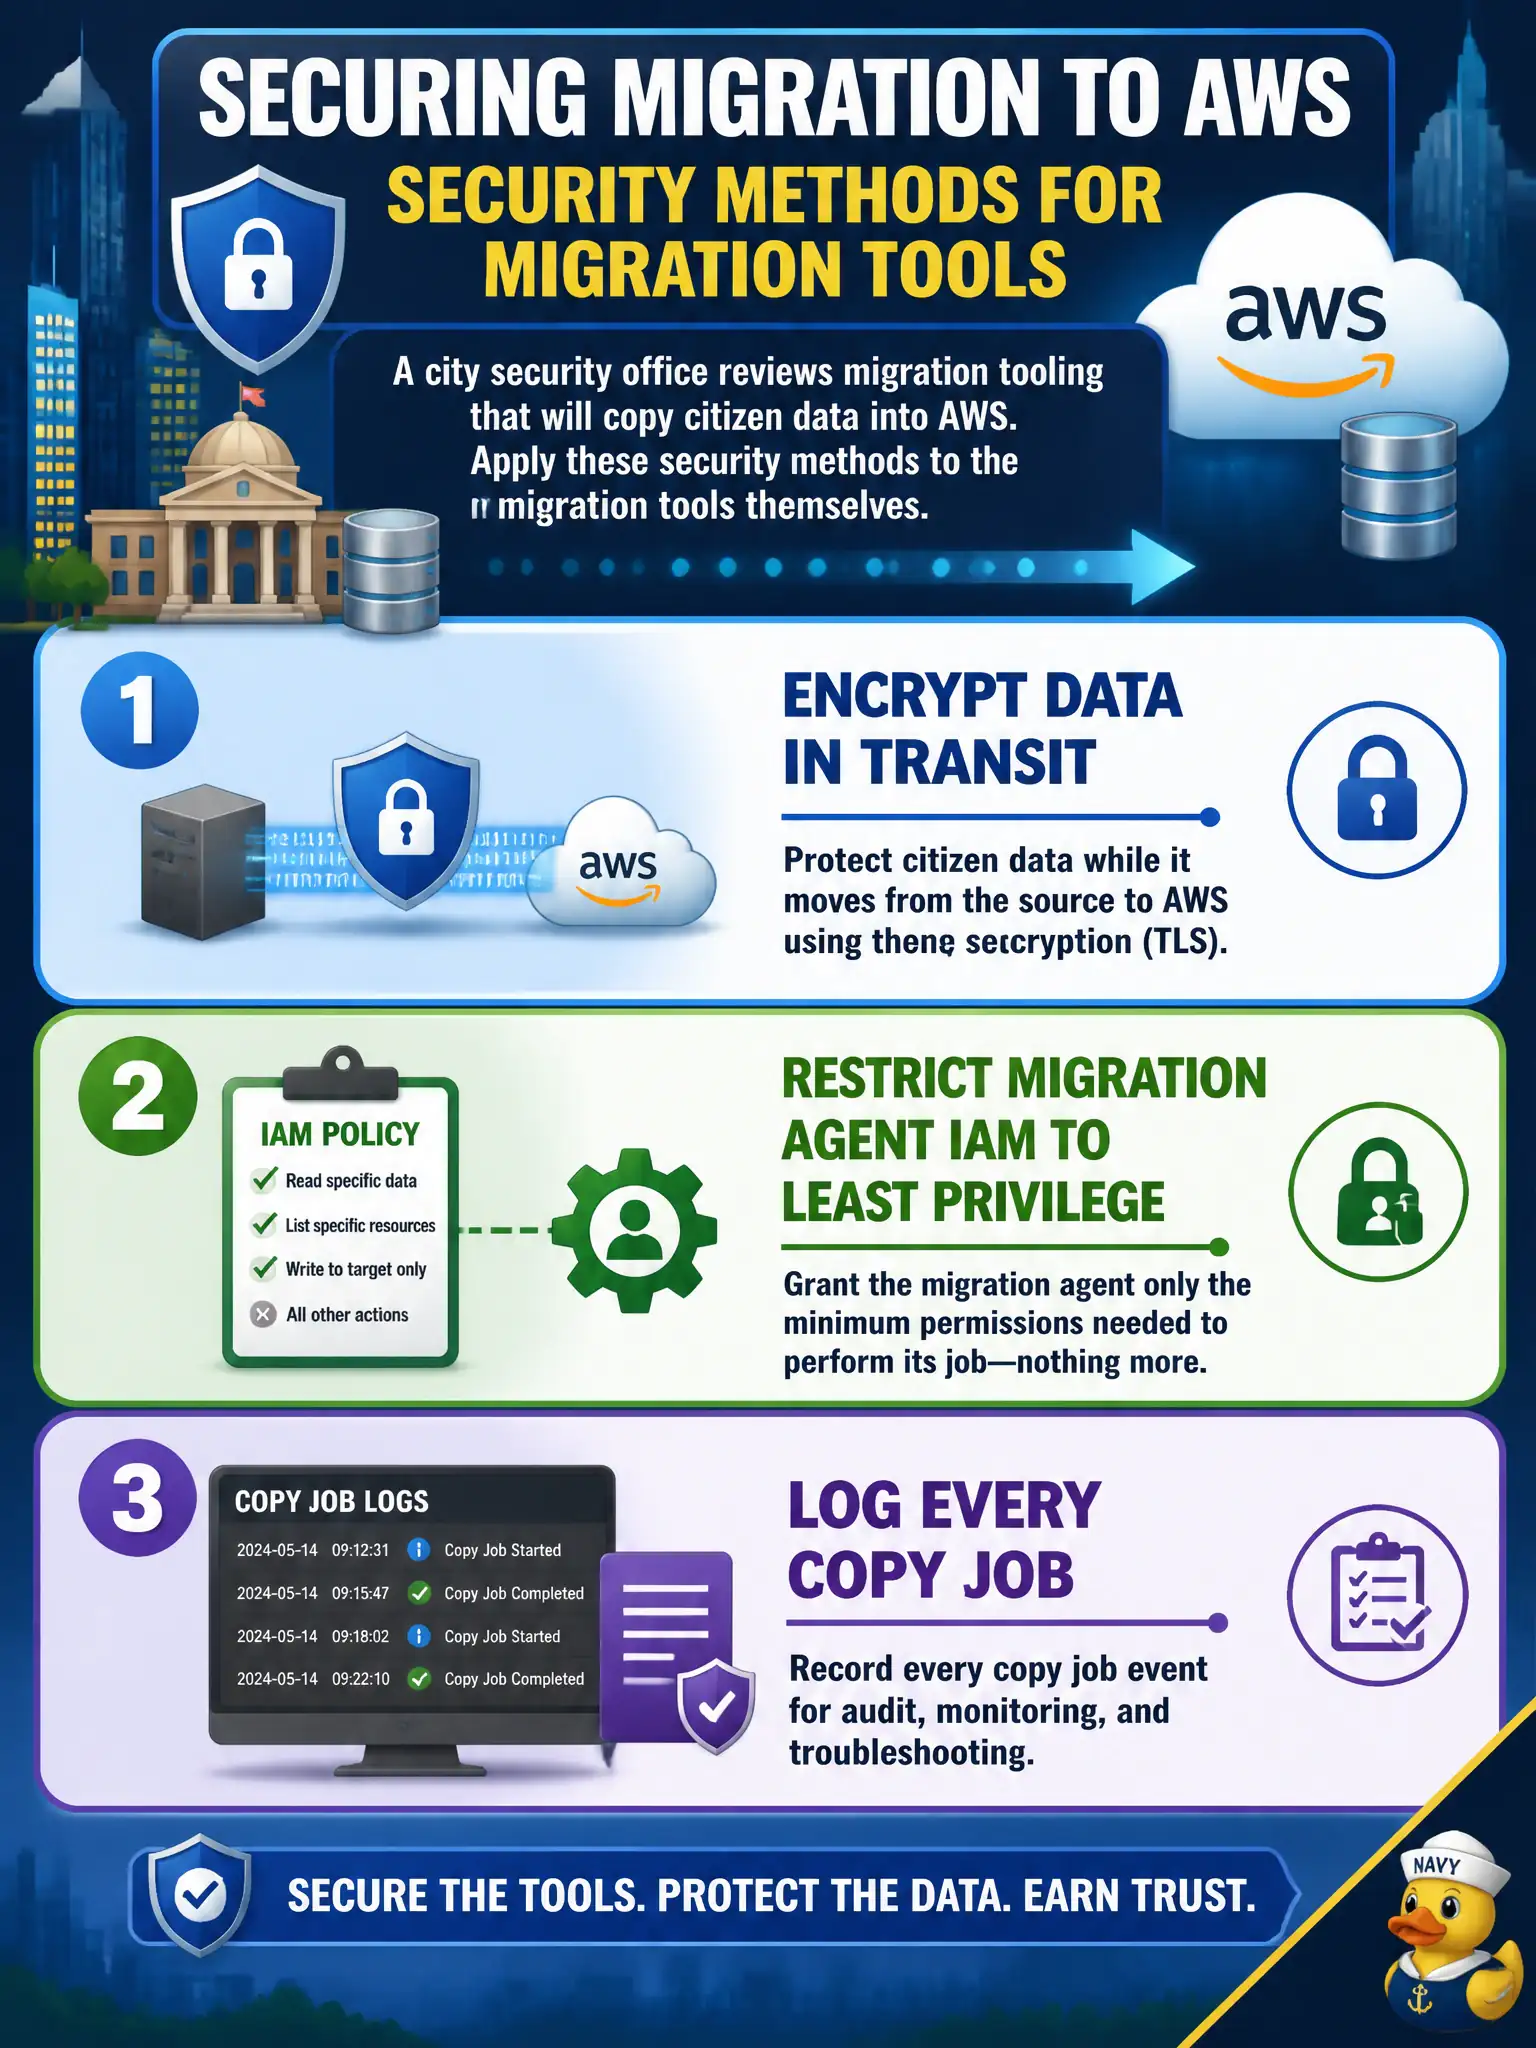
A city security office reviews migration tooling that will copy citizen data into AWS. Which security methods should be applied to the migration tools themselves?
Select an answer to reveal the explanation.
Short Explanation
The moving crew still needs seat belts and a signed inventory. Encrypt the copies, starve agents of extra IAM power, and log every job—speed is no excuse for naked pipes and admin keys.
Full Explanation
A city security office reviewing migration tooling that will copy citizen data into AWS must harden the tools themselves. Encrypt data in transit, restrict migration agent IAM to least privilege, and log every copy job so the migration plane meets the same control expectations as production civic systems. Disabling encryption in transit to maximize agent throughput on untrusted networks fails confidentiality for citizen data. Attaching AdministratorAccess to every migration agent role for convenience fails least privilege and expands blast radius if an agent host is compromised. Turning off CloudTrail for migration accounts so logs do not fill S3 fails detective controls exactly when bulk copy activity needs audit. Exam caveat: migration tools are in scope for encryption, least privilege, and logging—not exempt for speed. Operational check: enforce TLS on agents, scope IAM to required MGN/DataSync actions and target buckets only, enable CloudTrail and agent logs, alert on unusual copy volume, and include migration accounts in the city's security review checklist. Document the decision in the municipal architecture decision record and re-verify controls after the first production wave so auditors see continuous improvement, not one-time tribal knowledge.