
A city directory already runs Active Directory on-premises and wants employees to use existing identities for the AWS Management Console. What should the architect recommend?
Select an answer to reveal the explanation.
Short Explanation
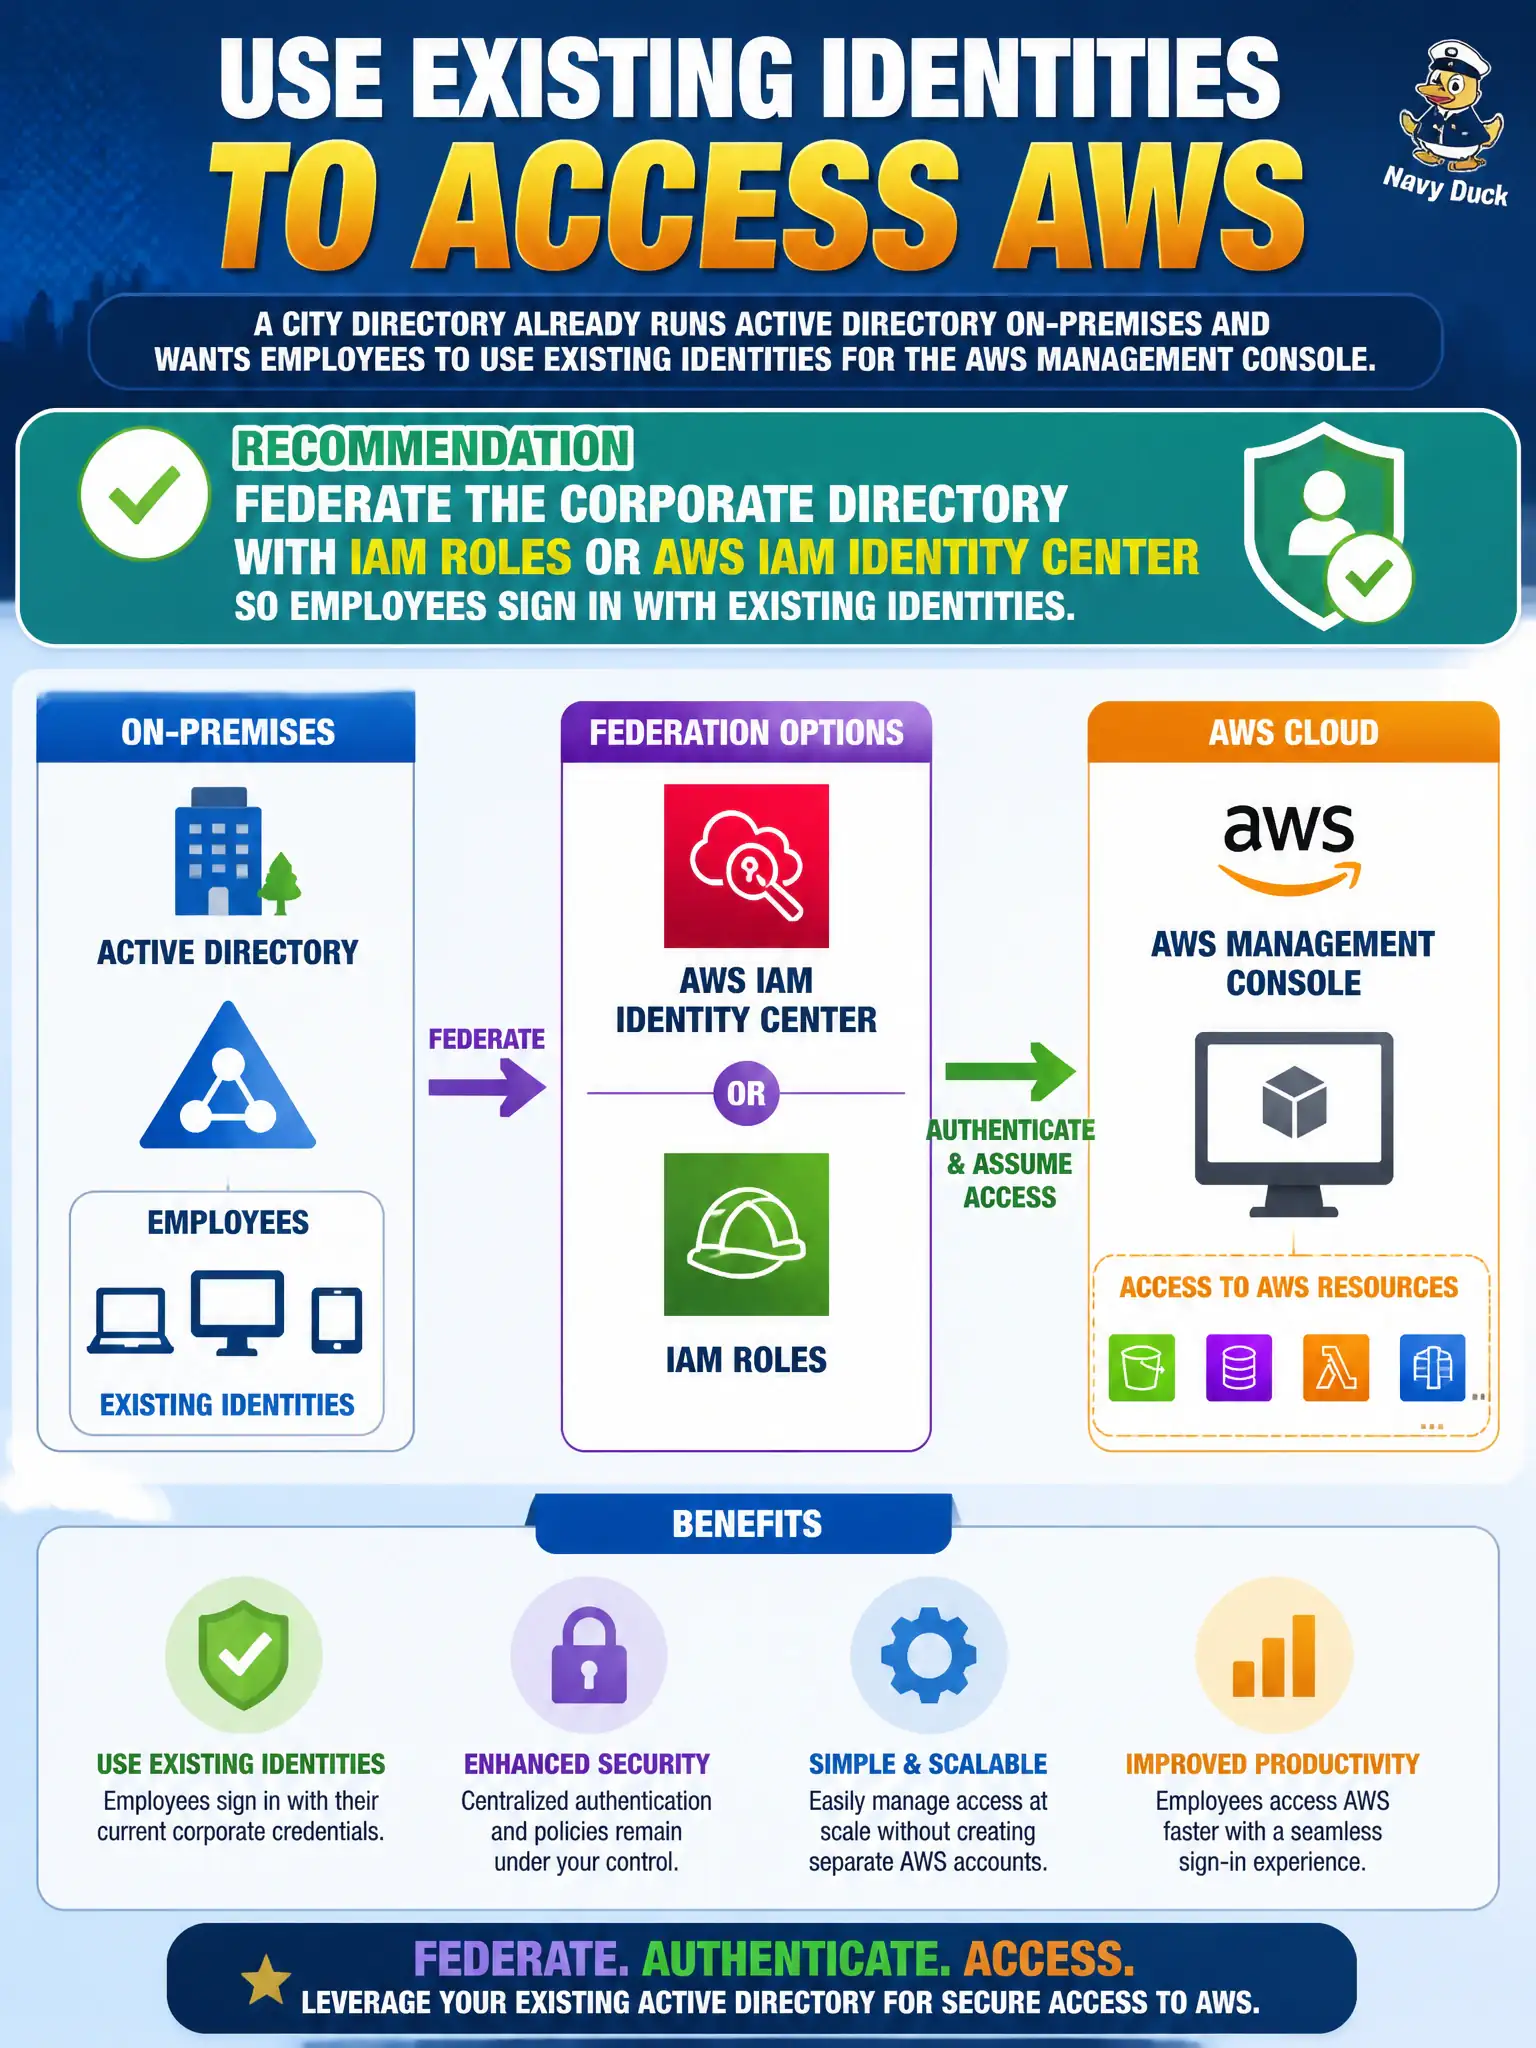
Nobody wants a second password sticky-note for every city worker. Federate Active Directory (or similar) into IAM roles or Identity Center so the same corporate login opens the AWS Console. Duplicating IAM users for the whole workforce is the path to sprawl.
Full Explanation
A city that already runs Active Directory should federate those identities into AWS rather than cloning passwords. AWS IAM Identity Center can use AD or another IdP as the identity source and map groups to permission sets across accounts; alternatively, SAML federation can assert into IAM roles. Employees keep one corporate login for the AWS Management Console, joiners and leavers are handled in the directory, and MFA can be enforced at the IdP or in AWS. That design matches how municipal IT already manages email and VPN access.
Creating a duplicate IAM user with a new password for every employee and syncing passwords weekly doubles the identity store, invites drift when people change roles, and creates orphan accounts. Requiring every employee to share one IAM user named CityStaff destroys accountability and least privilege. Disabling console access and issuing only long-lived access keys to each laptop pushes standing secrets onto endpoints and blocks legitimate console workflows without solving identity lifecycle.
Exam caveat: federation grants temporary credentials via assumed roles or Identity Center sessions—it does not replace the need for least-privilege permission sets, CloudTrail, and MFA. Directory group design should mirror job functions before AWS mapping. Operational check: join a pilot AD group, confirm the user sees the expected Identity Center or SAML role options, access only intended accounts, remove the group membership and confirm access disappears on the next session, and verify no per-employee IAM users were created in member accounts.