
A regional emergency-services consortium needs staff from county A to administer resources in county B’s AWS account for a joint CAD reporting app. Which design provides that access without sharing passwords?
Select an answer to reveal the explanation.
Short Explanation
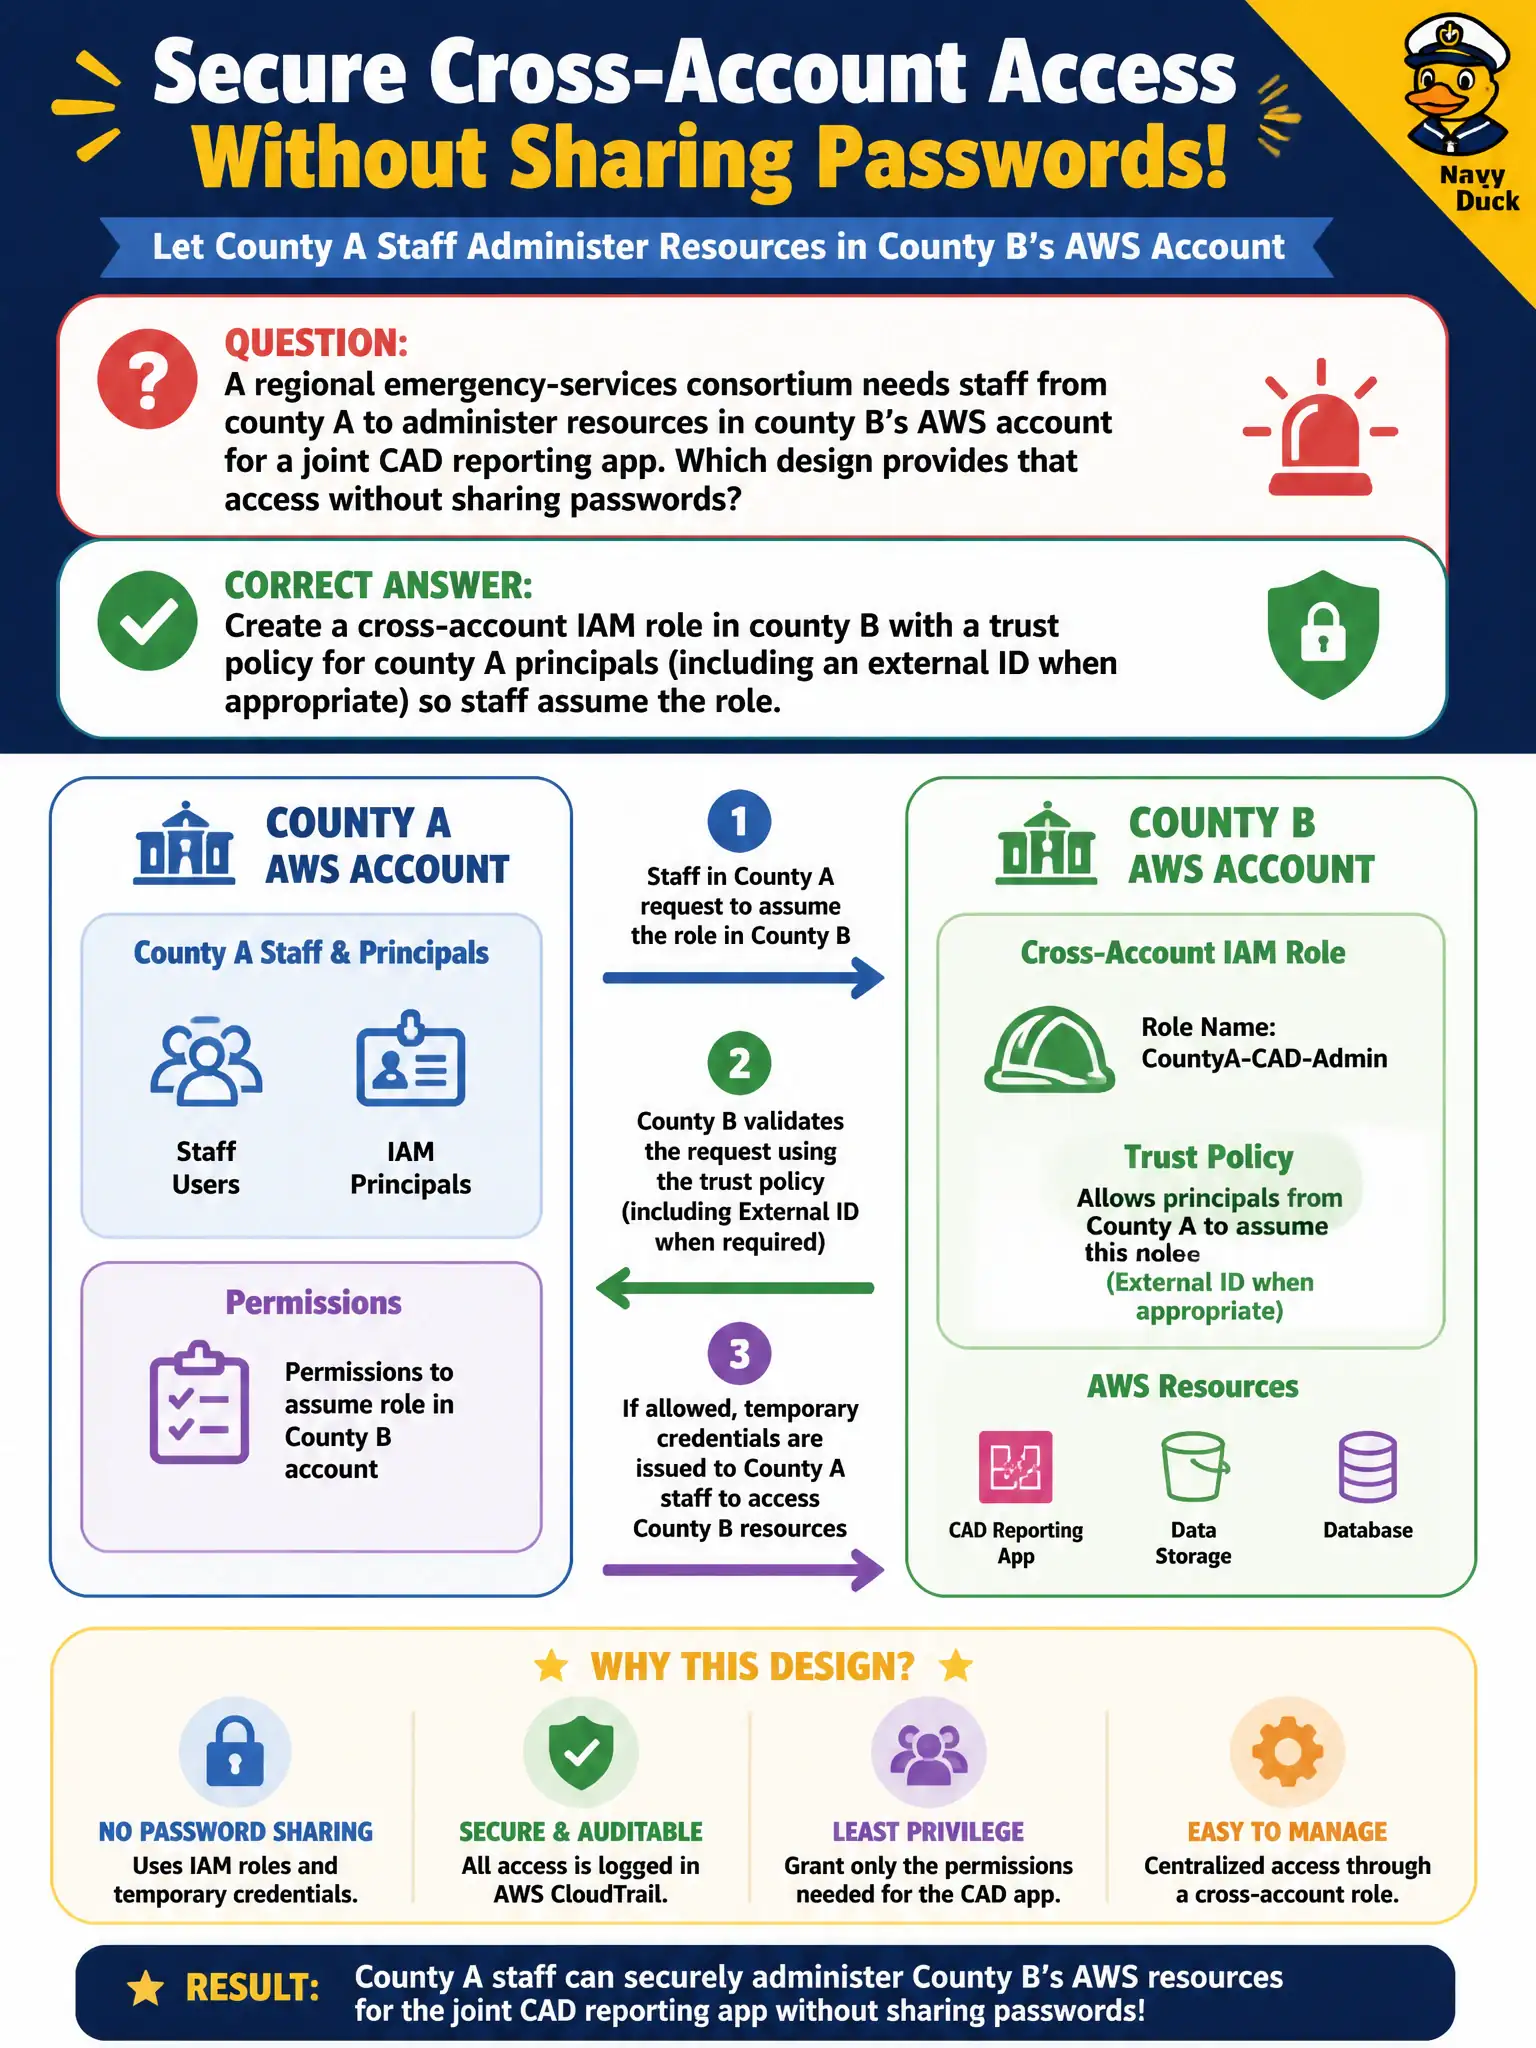
You would not mail the other county the keys to the evidence room. Instead, county B publishes a role that county A’s staff can assume—trust policy, optional external ID, short-lived session. They get admin rights in B without ever sharing a password.
Full Explanation
Cross-county administration for a joint CAD reporting app should use a cross-account IAM role in county B that trusts principals from county A. County B defines a role with the needed administrative permissions and a trust policy allowing specified IAM roles or Identity Center permission sets from county A's account (and an external ID when the relationship involves a third party or confused-deputy risk). County A staff call sts:AssumeRole, receive temporary credentials, and operate in B without ever receiving B's passwords or long-lived keys. Sessions expire, can require MFA, and are logged in both accounts' CloudTrail trails.
Emailing county B's root password to county A administrators shares the most privileged credential over an insecure channel and permanently couples both counties' security postures. Copying IAM user access keys from B into A's source repository embeds standing secrets in version control where they leak and rarely rotate. Opening B's Management Console to the public internet without authentication abandons identity entirely and would expose government systems to anonymous abuse.
Exam caveat: the trust policy Principal must be precise (account or role ARNs), external IDs help when assuming roles across organizational boundaries that could be spoofed, and AdministratorAccess in the role should be narrowed to the CAD reporting resources when possible. SCPs in B's organization can still constrain what the assumed role can do. Operational check: from a county A principal, assume the B role and list or administer only the intended CAD resources; confirm a principal without the trust relationship receives AccessDenied; verify CloudTrail in B shows AssumeRole and subsequent API calls with the role session name identifying the A operator.