
A parks mobile app needs citizen (external) sign-in, while city staff continue to use corporate SSO for the AWS Console. How should the architect separate these identity needs?
Select an answer to reveal the explanation.
Short Explanation
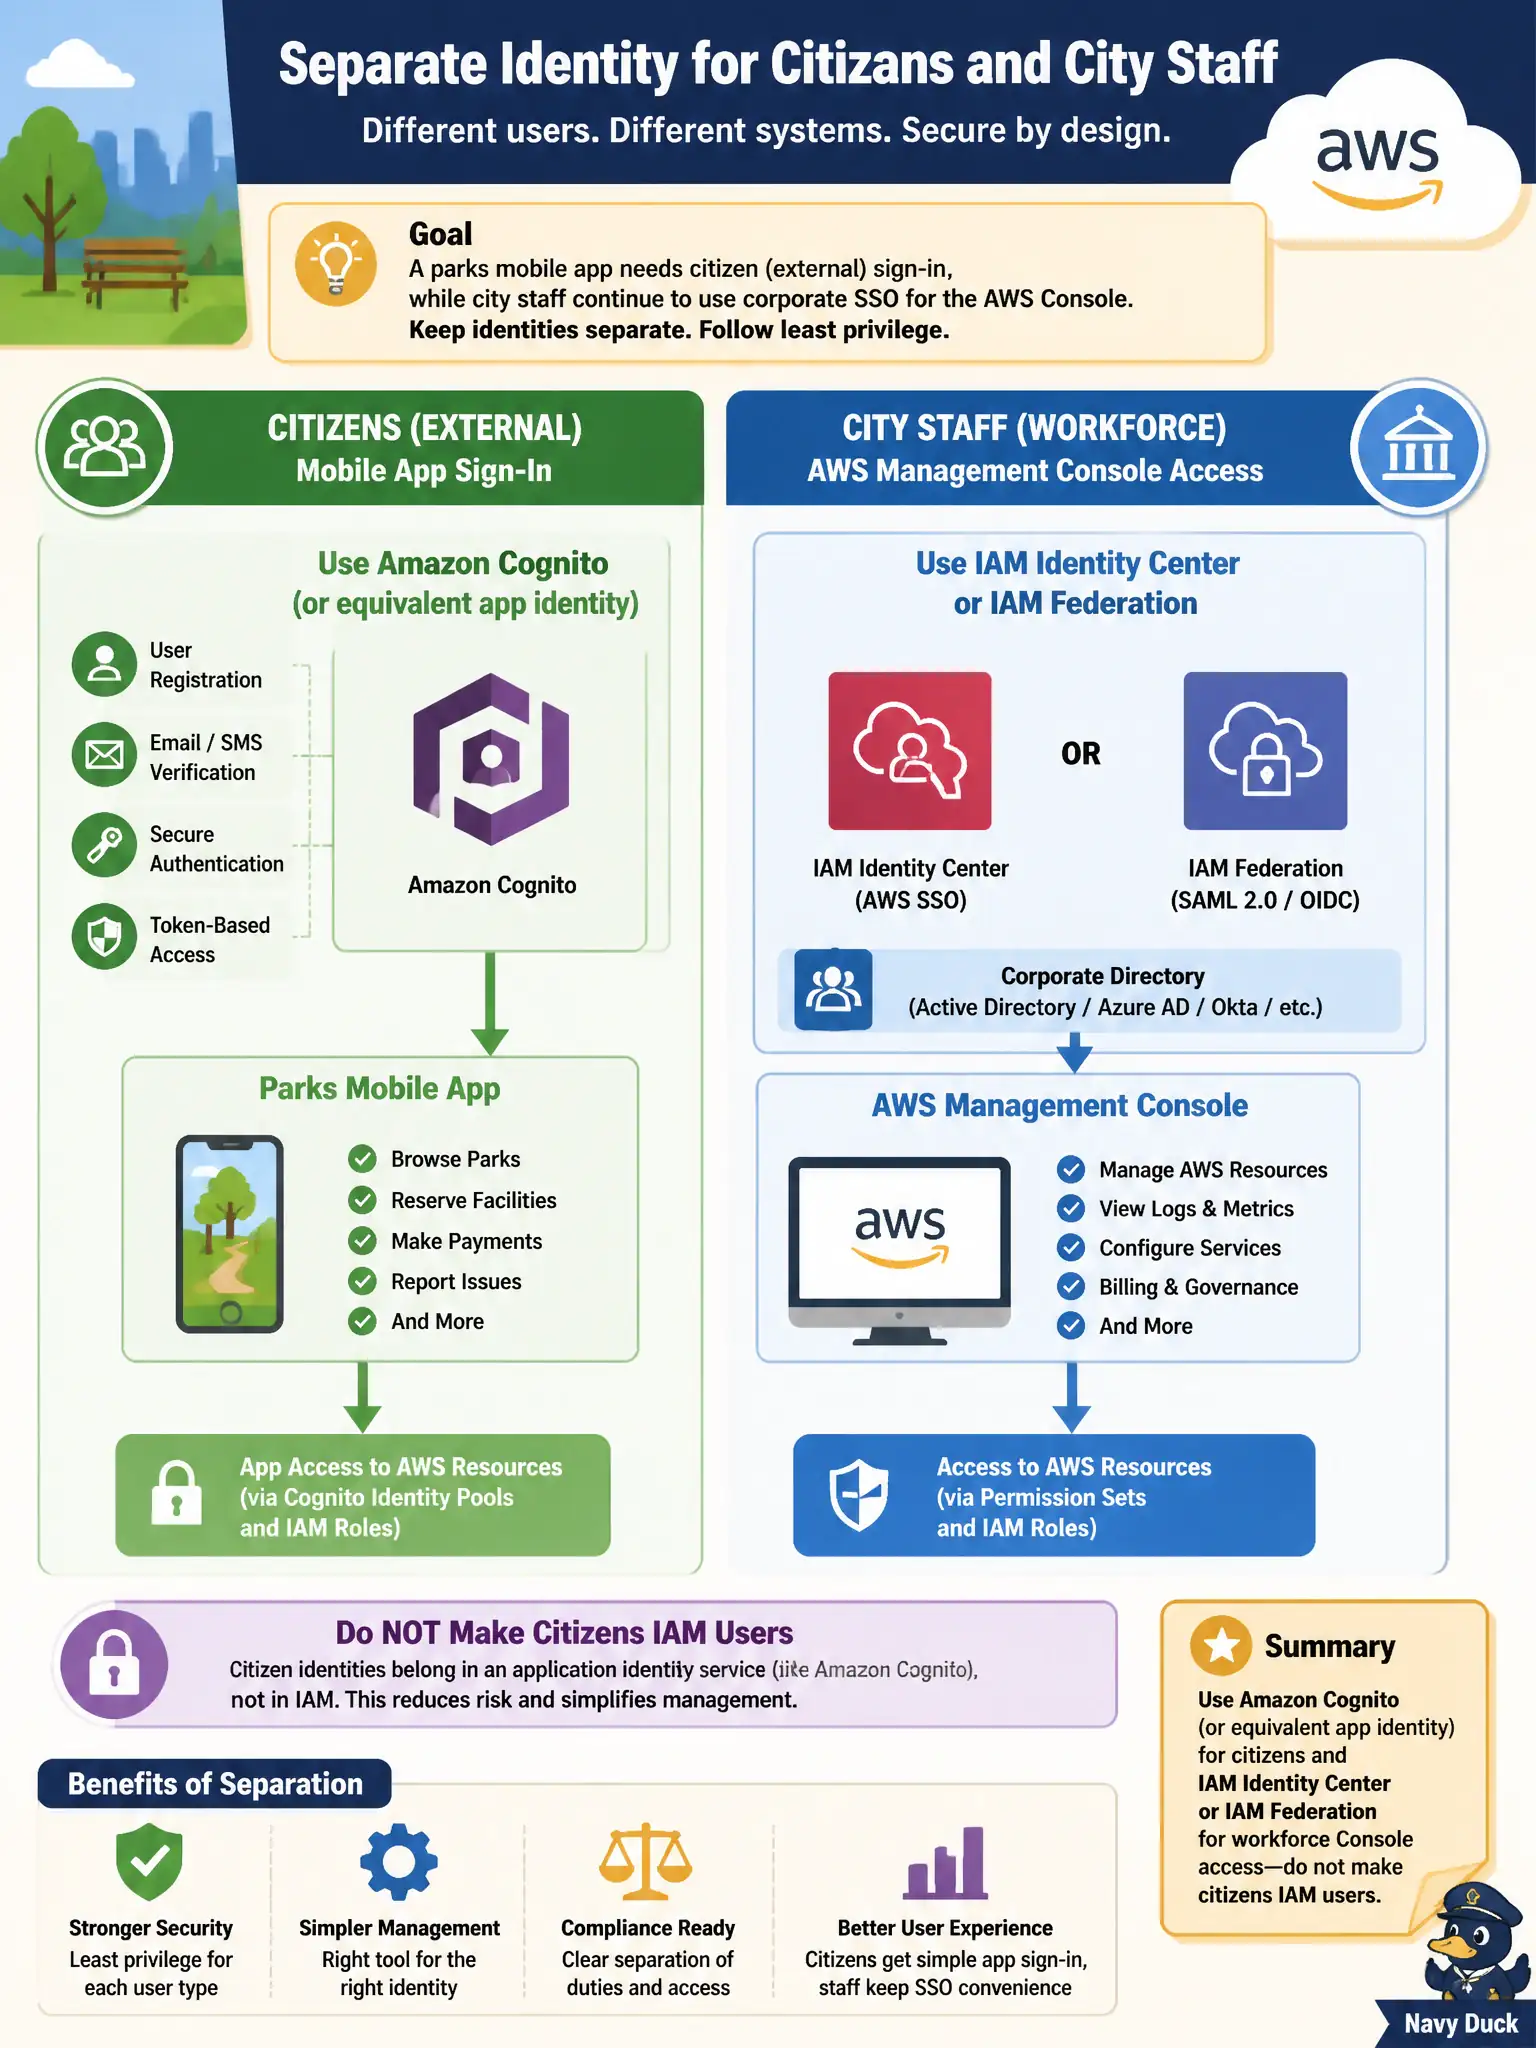
Citizens booking a picnic shelter are not city employees with AWS console badges. Cognito (or similar app identity) handles external sign-in; Identity Center or IAM federation handles staff SSO. Mixing both crowds into IAM users is the wrong crowd for the wrong door.
Full Explanation
Citizen-facing authentication and workforce AWS Console access are different identity planes and must not be collapsed into IAM users. Amazon Cognito user pools (or an equivalent customer identity service) handle external sign-in for a parks mobile app: sign-up, social IdPs, tokens for API Gateway or app backends, and user directory features aimed at consumers. City staff continue to use IAM Identity Center or IAM federation with the corporate IdP for Management Console and AWS API administration. Citizens are not AWS account principals and should never receive IAM users simply because they downloaded a municipal app.
Creating an IAM user for every citizen does not scale, pollutes the account's IAM quota and audit noise, and grants a class of identity meant for administrators and workloads. Putting citizens and staff in the same Identity Center permission set with AdministratorAccess both misuses workforce IAM and massively over-privileges the public. Storing citizen passwords in DynamoDB and embedding table credentials in the mobile app recreates a custom identity store without Cognito's threat protections and ships database secrets to client devices.
Exam caveat: Cognito identity pools can mint temporary AWS credentials for scoped mobile access to AWS resources (for example a citizen uploads to an S3 prefix); that is still application identity, not Console workforce access. Do not confuse Cognito with Identity Center. Operational check: register a test citizen in Cognito and call the app API with the issued tokens; confirm staff SSO via Identity Center cannot be used as a citizen login and vice versa; ensure IAM lists show no citizen IAM users.