
A traveler tweets a screenshot of a municipal airport-authority guest Wi-Fi prompt. What is the correct wireless-OSINT use of that screenshot?
Select an answer to reveal the explanation.
Short Explanation
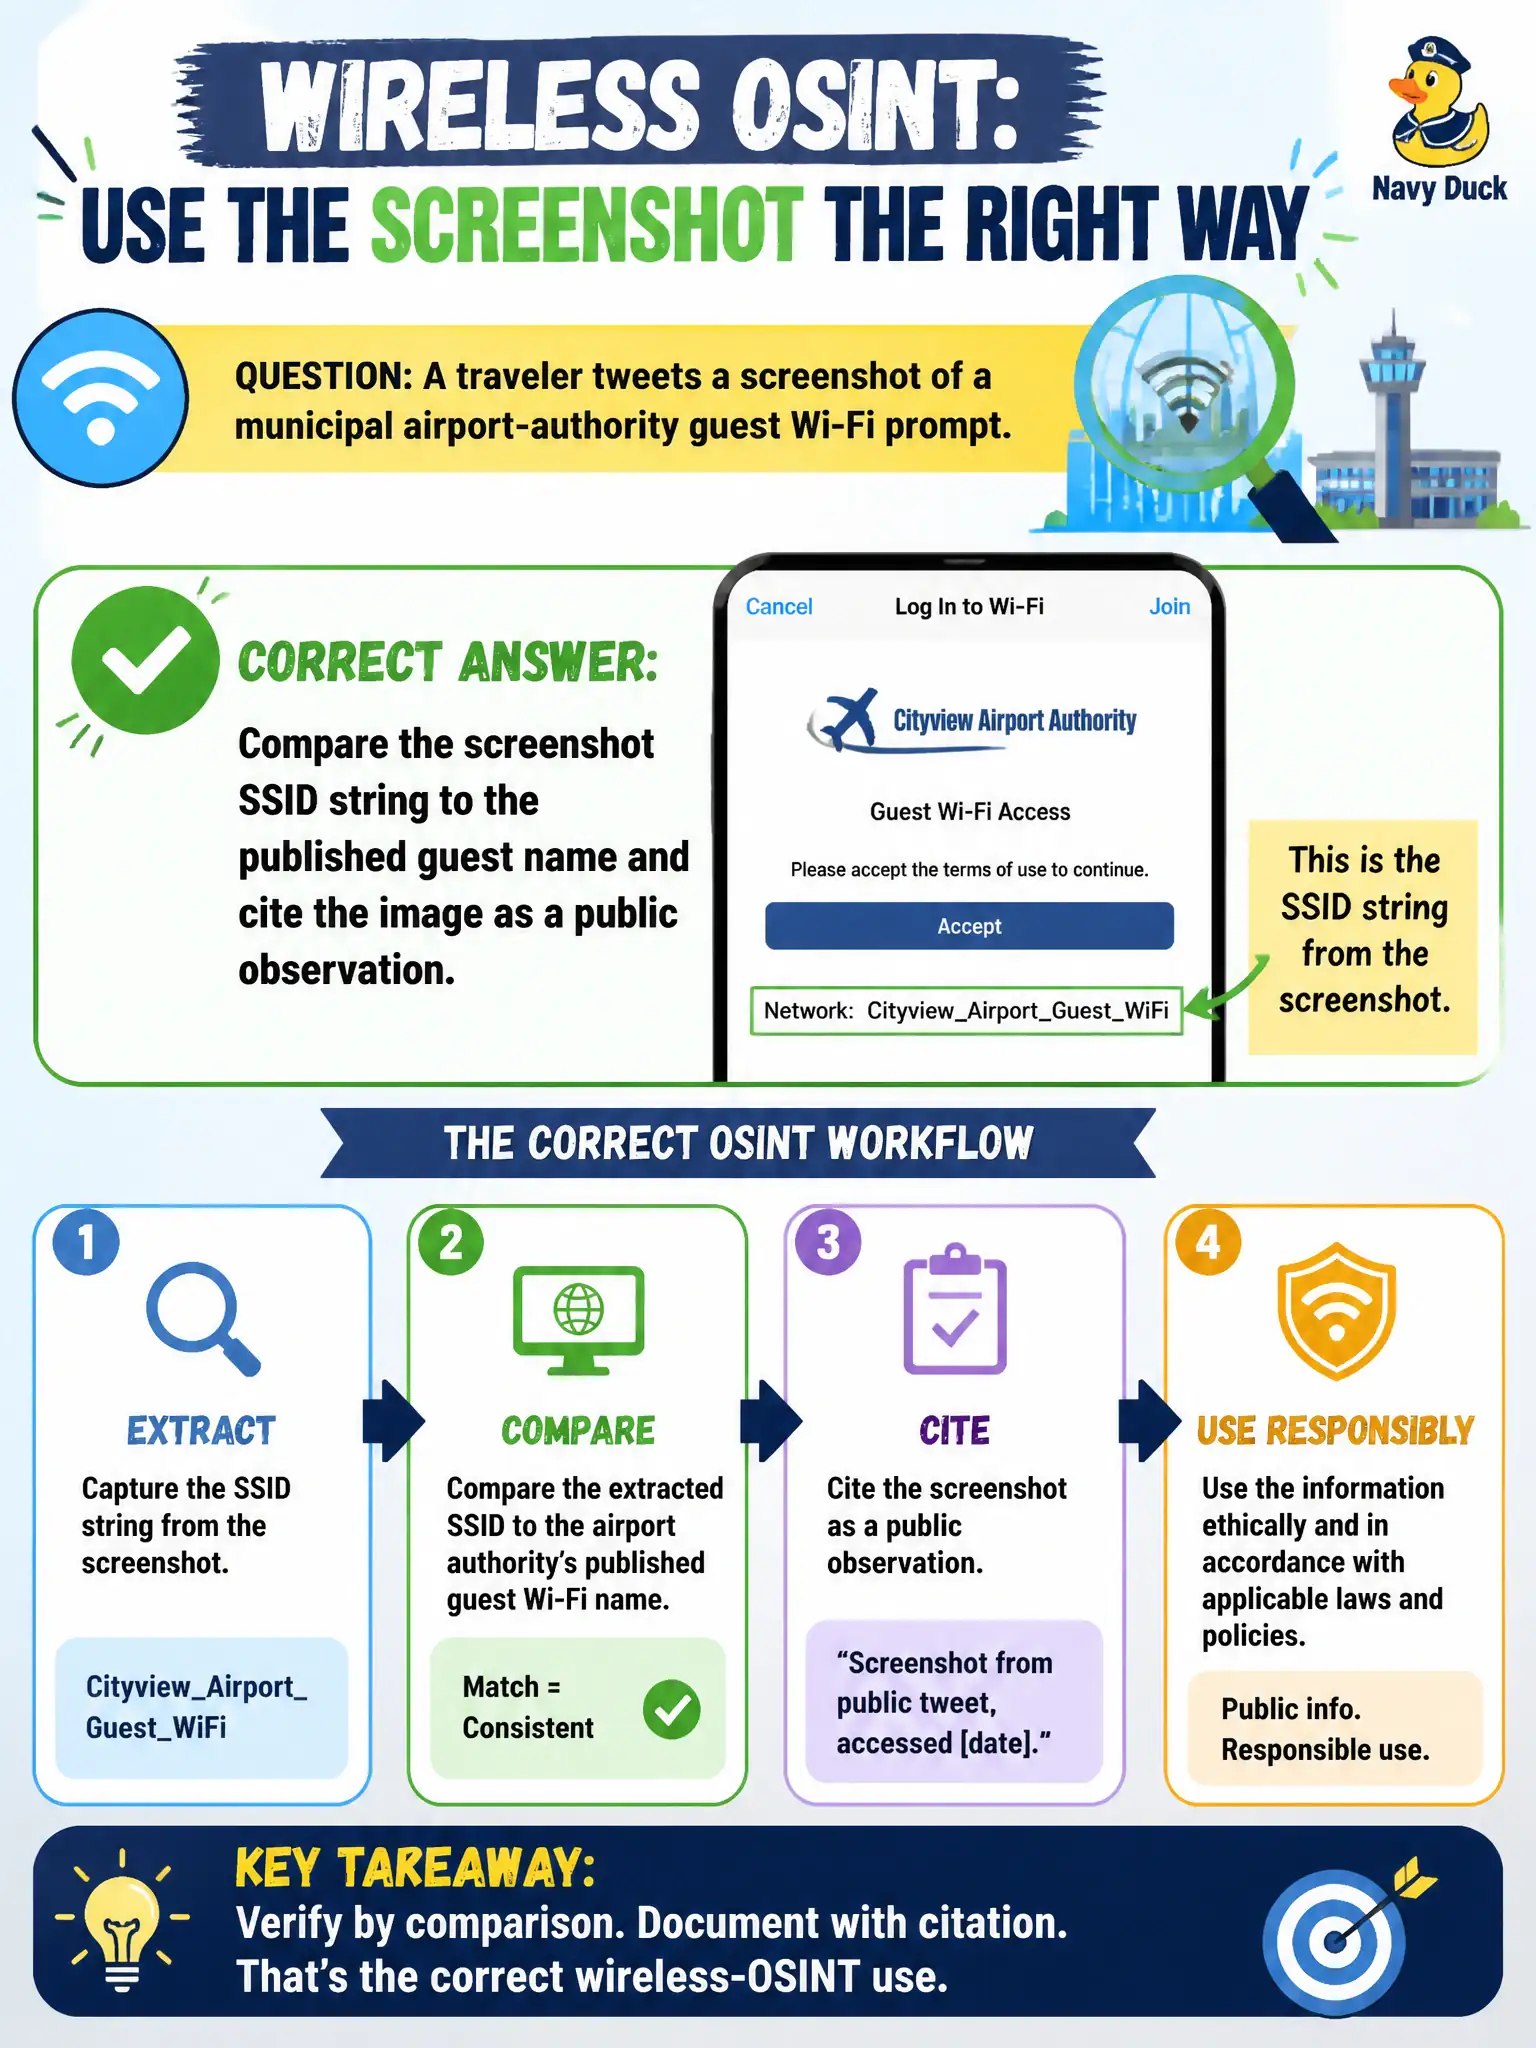
A tweeted login screen already printed the network name. Match that string to the airport authority’s published guest SSID and cite the post. Photos are not handshake files, and DMing a traveler from a real account is sloppy OPSEC.
Full Explanation
Photos and screenshots of network names are valid wireless-OSINT inputs. When a traveler tweets a screenshot of a municipal airport-authority guest Wi-Fi prompt, the correct use is to compare the visible SSID string to the published guest name and cite the public image—including post timestamp—as an observation. That lets airport IT confirm naming consistency without treating the picture as a crackable capture or contacting the traveler for secrets.
Extracting a four-way handshake from the image file is impossible and misunderstands what screenshots contain; seeking key recovery from a photo is offensive framing. Asking the traveler for the passphrase in a DM from a personal account is interactive credential hunting and poor OPSEC. Treating screenshots as unusable because only live RF captures count wrongly excludes a common public artifact class for naming observations.
Exam caveat: a screenshot shows a claimed SSID at a moment in time; captive-portal chrome can be mocked. Corroborate with the authority's published list and, if needed, other public posts rather than demanding live key material.
Operational check: archive the tweet/screenshot, quote the pictured SSID, pull the official guest SSID list with date, document match or mismatch, and avoid personal DMs or handshake fantasies.