
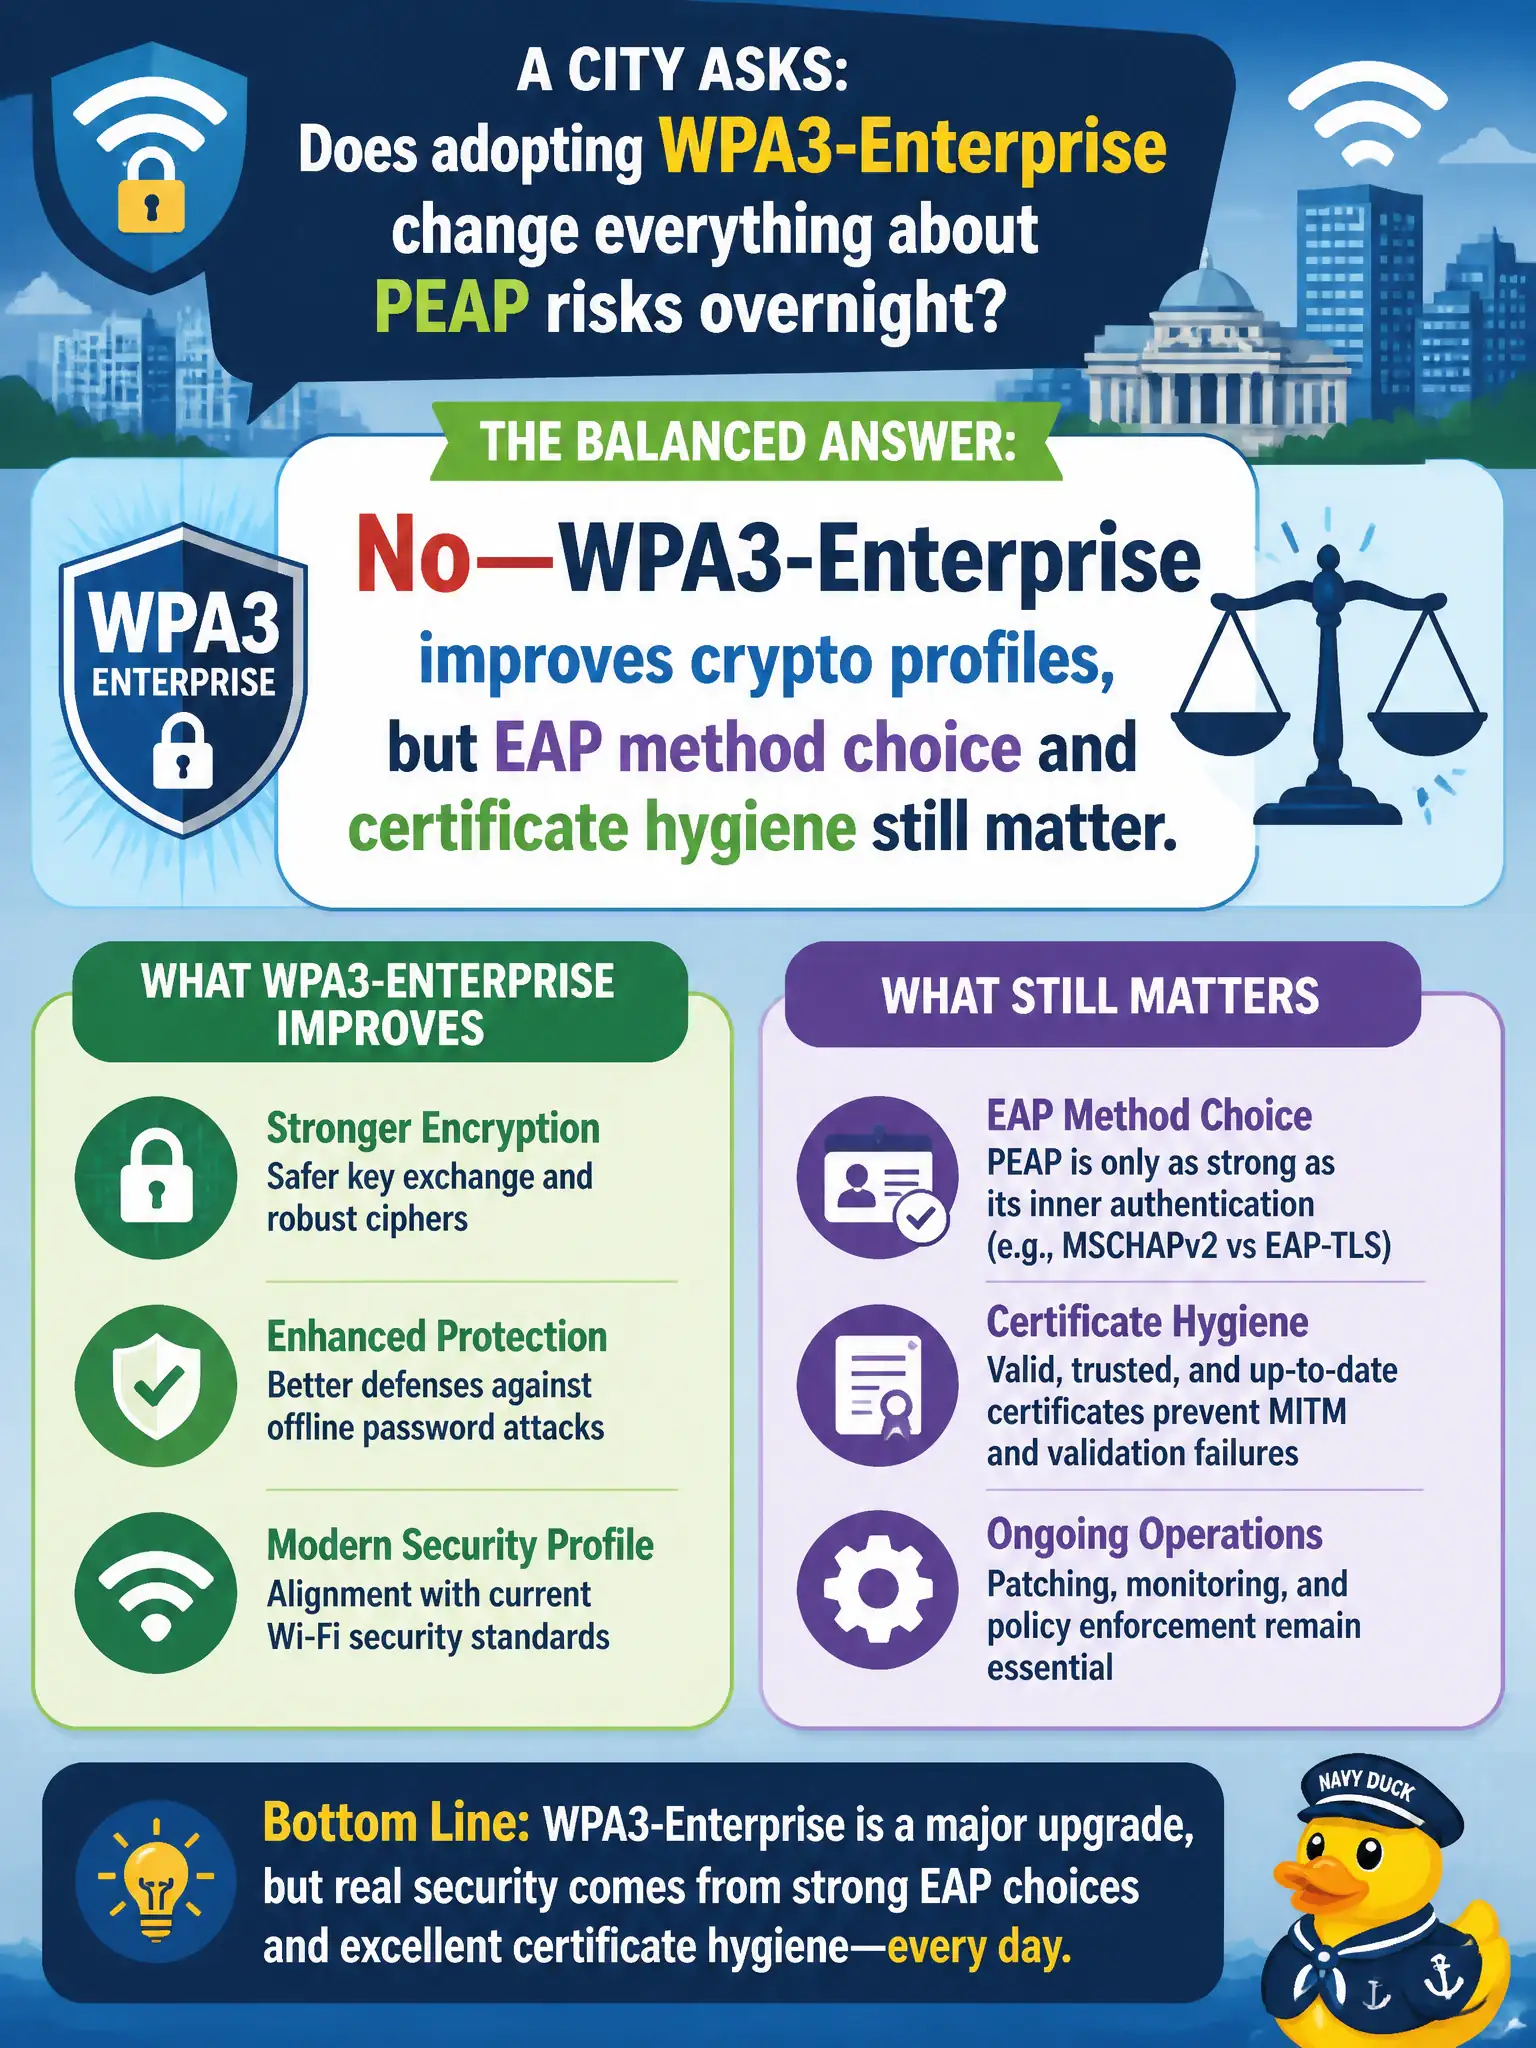
A city asks whether adopting WPA3-Enterprise changes everything about PEAP risks overnight. What balanced answer should advisors give?
Select an answer to reveal the explanation.
Short Explanation
WPA3-Enterprise is a stronger suit of armor, not a spell that erases PEAP mistakes. Method choice and cert hygiene still decide whether twins can trick staff.
Full Explanation
Adopting WPA3-Enterprise does not change everything about PEAP risks overnight. Advisors should say that WPA3-Enterprise improves crypto profiles, but EAP method choice and certificate hygiene still matter. WPA3-Enterprise does not remove the need for any EAP method or RADIUS server. It does not make server certificate validation optional by protocol mandate. It is not limited to open OWE hotspots and never to staff SSIDs; Enterprise modes target authenticated staff networks. Exam caveat: marketing upgrades without profile hygiene leave municipal password-based inner methods exposed to twin classes. Operational check: after a civic WPA3-Enterprise rollout, re-verify EAP methods allowed, enforce certificate validation, and retire legacy PEAP misconfigurations rather than assuming the logo finished the job. For municipal and campus engagements, keep the finding language tied to authorized scope, name the building or SSID class affected, and state the residual risk to residents or staff if the rejected option had been chosen. Re-validate after the next change window that the selected control still matches inventory, monitoring, and RoE abort criteria used by the city wireless program.