
A lab connects with wpa_supplicant using PEAP settings after obtaining authorized credentials. What validation class does a successful join represent?
Select an answer to reveal the explanation.
Short Explanation
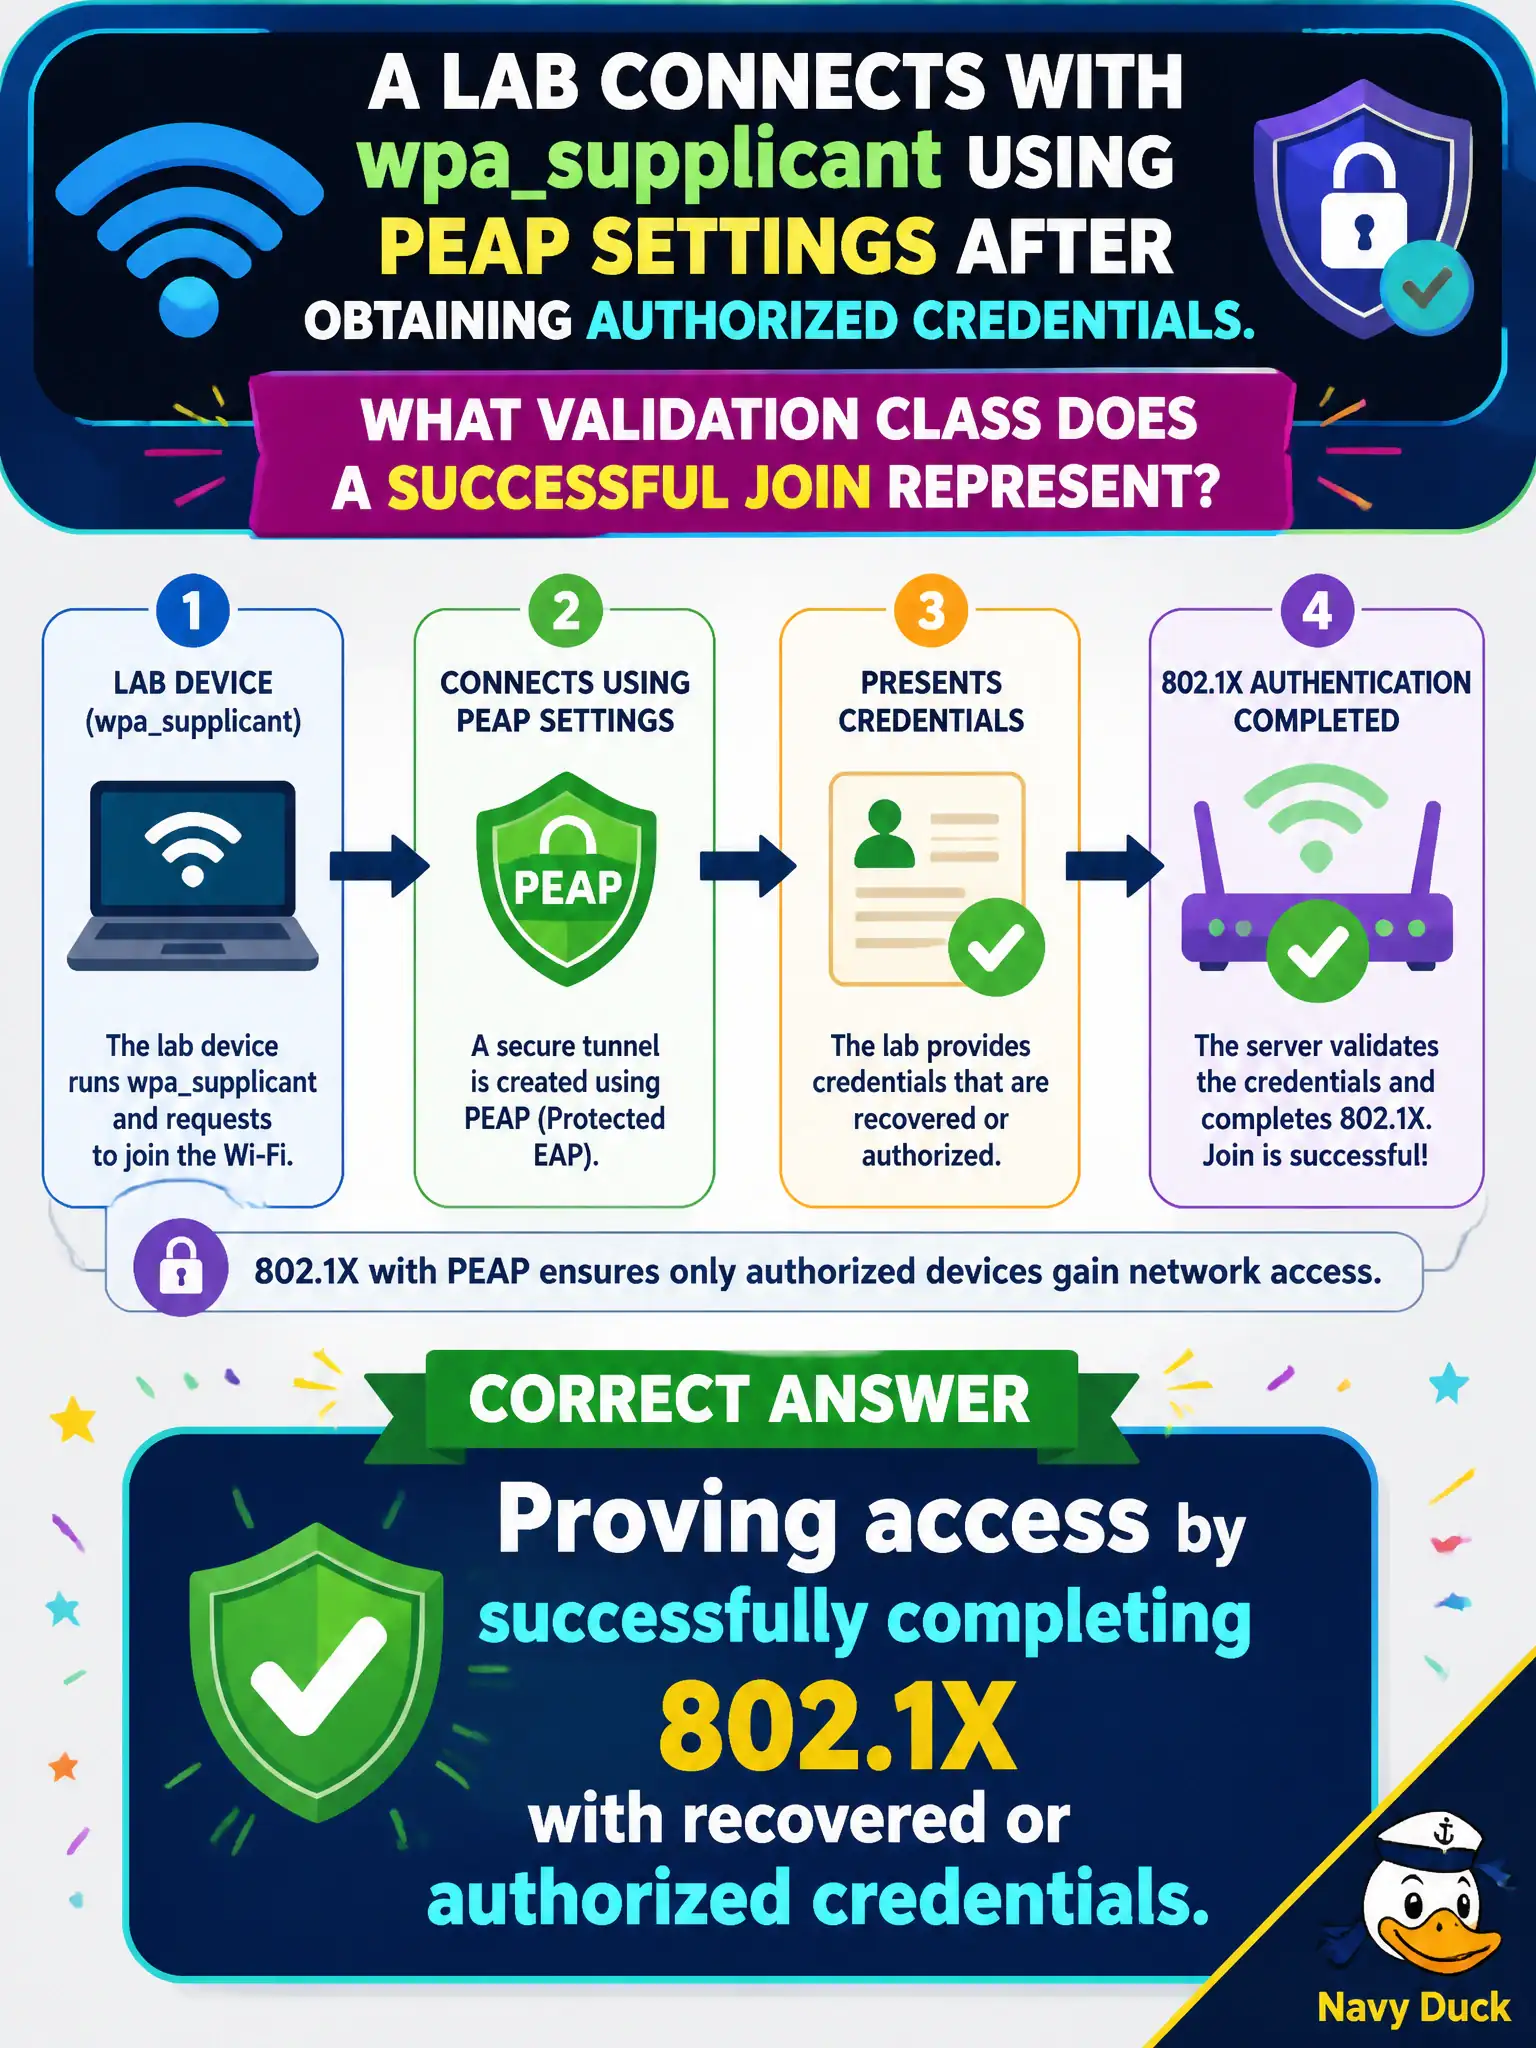
Getting on with wpa_supplicant and PEAP after authorized creds is the 'door opened' check: 802.1X completed for real. Monitor mode alone does not decrypt Enterprise without keys.
Full Explanation
Successfully joining with wpa_supplicant using PEAP settings after obtaining authorized credentials represents proving access by completing 802.1X with recovered or authorized credentials. It does not prove that monitor mode alone decrypts all Enterprise GTK traffic without keys. It does not prove that captive-portal DNS rebinding replaced RADIUS for staff authentication. It does not prove that aircrack-ng converted PEAP into a WPA-Personal PSK file automatically. Exam caveat: validation evidence should show association and authorized network reachability appropriate to scope, not only a partial EAP log. Operational check: in the civic lab or engagement, capture the successful supplicant join evidence, confirm the expected VLAN or resources, and store screenshots as sensitive proof under retention rules. For municipal and campus engagements, keep the finding language tied to authorized scope, name the building or SSID class affected, and state the residual risk to residents or staff if the rejected option had been chosen. Re-validate after the next change window that the selected control still matches inventory, monitoring, and RoE abort criteria used by the city wireless program. Document the decision in the municipal engagement notes so the next assessor inherits both the technical rationale and the civic constraints that shaped it.