
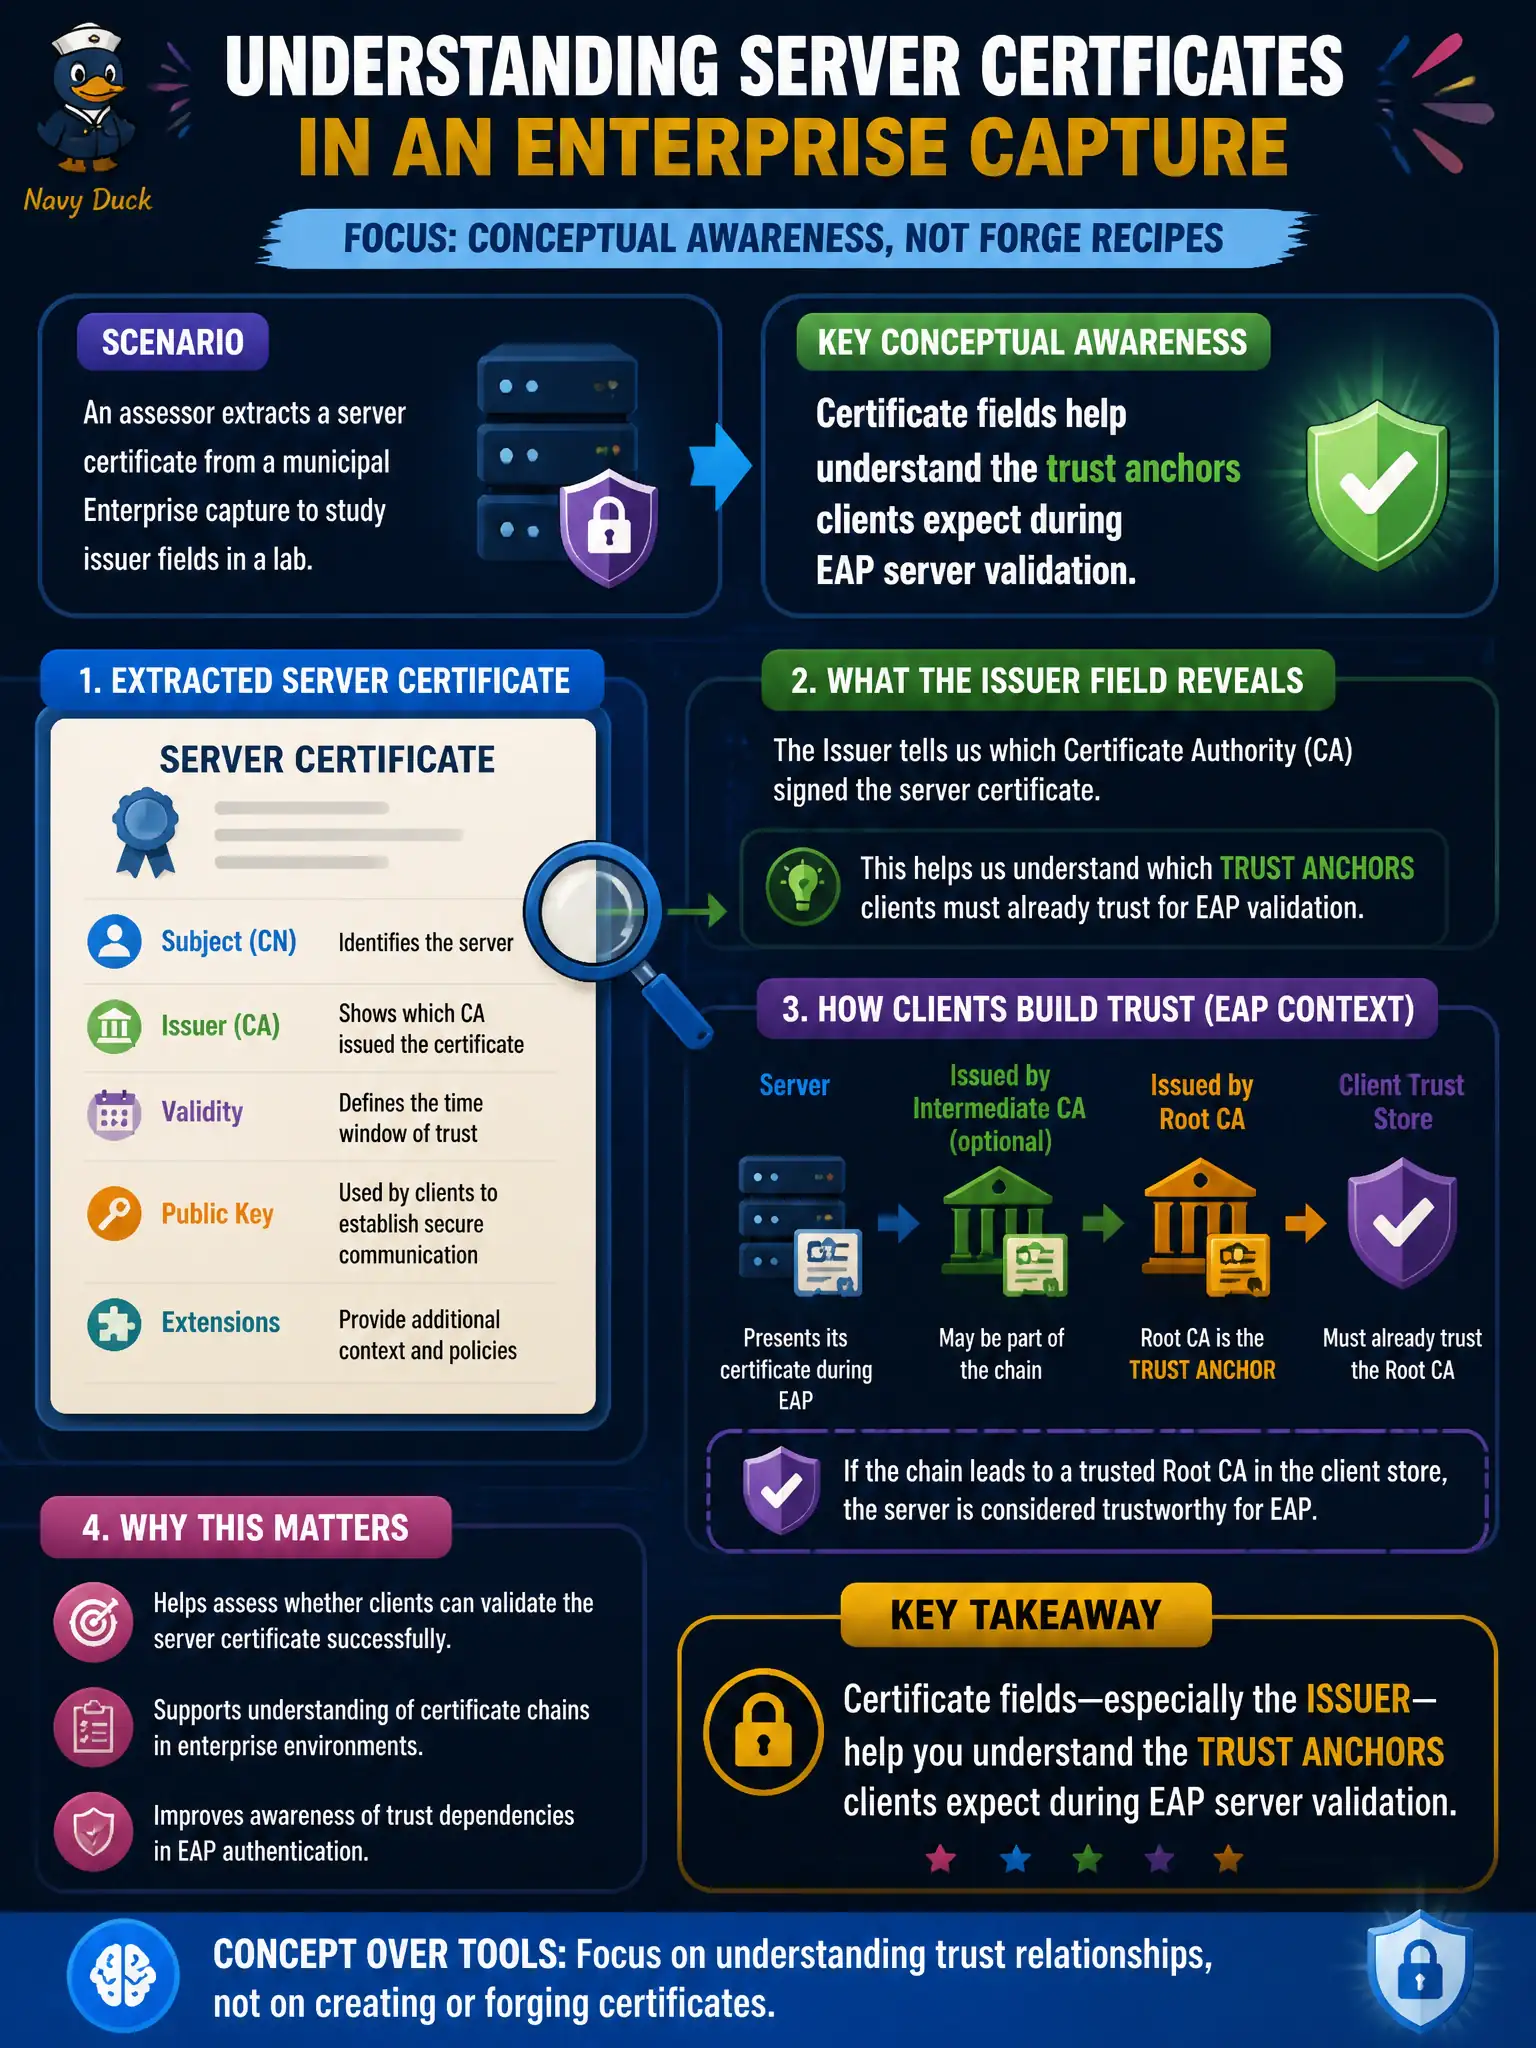
An assessor extracts a server certificate from a municipal Enterprise capture to study issuer fields in a lab. What conceptual awareness is appropriate—without forge recipes?
Select an answer to reveal the explanation.
Short Explanation
Reading issuer and subject fields is map work: you learn which trust anchors clients expect. That is analysis awareness, not a forge cookbook and not a path to PSK recovery.
Full Explanation
Extracting a server certificate from a municipal Enterprise capture to study issuer fields is appropriate conceptual awareness: certificate fields help understand the trust anchors clients expect during EAP server validation. Those fields do not prove the PSK can be recovered directly from the TLS ServerHello. Certificate fields are not irrelevant; Enterprise clients evaluate trust anchors when profiles are configured correctly. Certificate fields do not automatically enable WPS registrar mode on associated stations. Exam caveat: studying certificates in an authorized lab is recon and design review, not permission to forge production trust material or plant rogue CAs. Operational check: compare captured issuer and SAN details to the city's published Wi-Fi trust documentation, confirm endpoint stores match, and note discrepancies as configuration findings for the civic WLAN team. For municipal and campus engagements, keep the finding language tied to authorized scope, name the building or SSID class affected, and state the residual risk to residents or staff if the rejected option had been chosen. Re-validate after the next change window that the selected control still matches inventory, monitoring, and RoE abort criteria used by the city wireless program.