
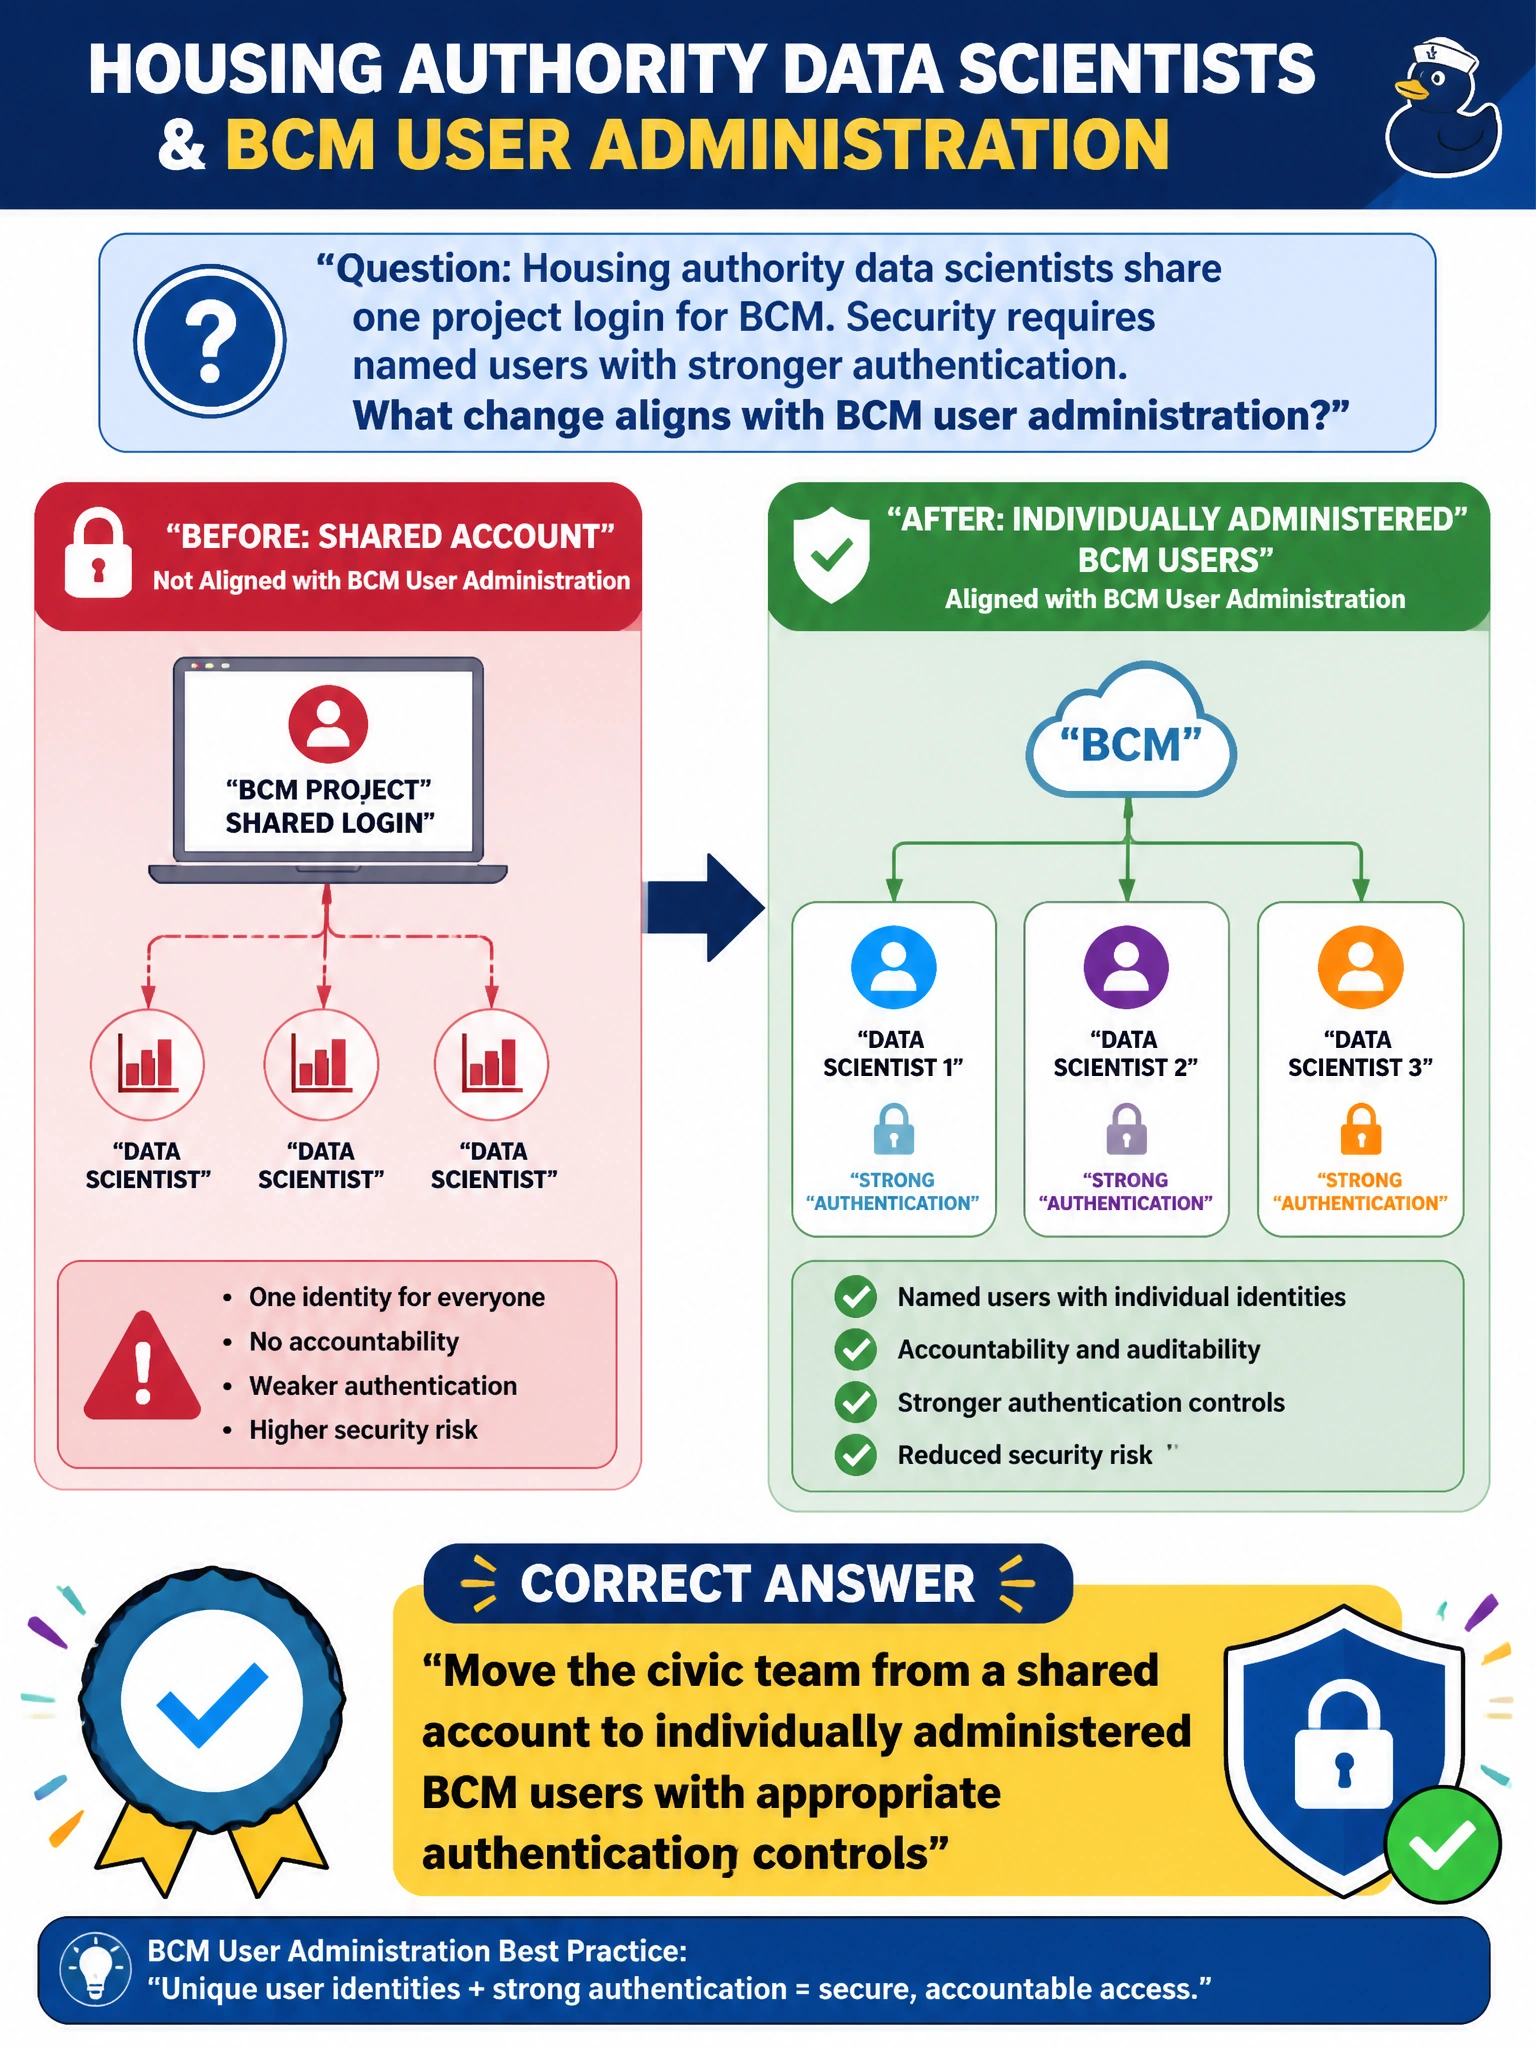
Housing authority data scientists share one project login for BCM. Security requires named users with stronger authentication. What change aligns with BCM user administration?
Select an answer to reveal the explanation.
Short Explanation
One shared housing login is a group house key—nobody knows who opened the door. BCM user administration means named accounts (with the MFA or auth controls security wants) for each data scientist. Wiki passwords and anonymous paths fail that audit conversation.
Full Explanation
Housing authority data scientists sharing one project login conflict with security requirements for named users and stronger authentication. The aligned BCM change is to move the civic team to individually administered BCM users with appropriate authentication controls (such as MFA where mandated). Shared accounts destroy attribution—nobody can prove who submitted a job, changed a setting, or exfiltrated data—and they make credential rotation and offboarding nearly impossible. Keeping the shared login and posting it in the team wiki broadcasts secrets and fails any serious municipal audit. Disabling BCM authentication for housing projects only creates a privileged carve-out attackers will prefer. Switching housing jobs to anonymous FTP for “simpler” access abandons cluster auth entirely and is not a substitute for BCM user administration. Exam caveat: shared service accounts are sometimes debated for automation, but interactive data-scientist access should be named; automation identities still must be unique, secret-managed, and audited. Operational check: create named BCM users for each housing scientist, enforce the required authentication policy, retire the shared login, and confirm job history and admin actions map to individual identities.