
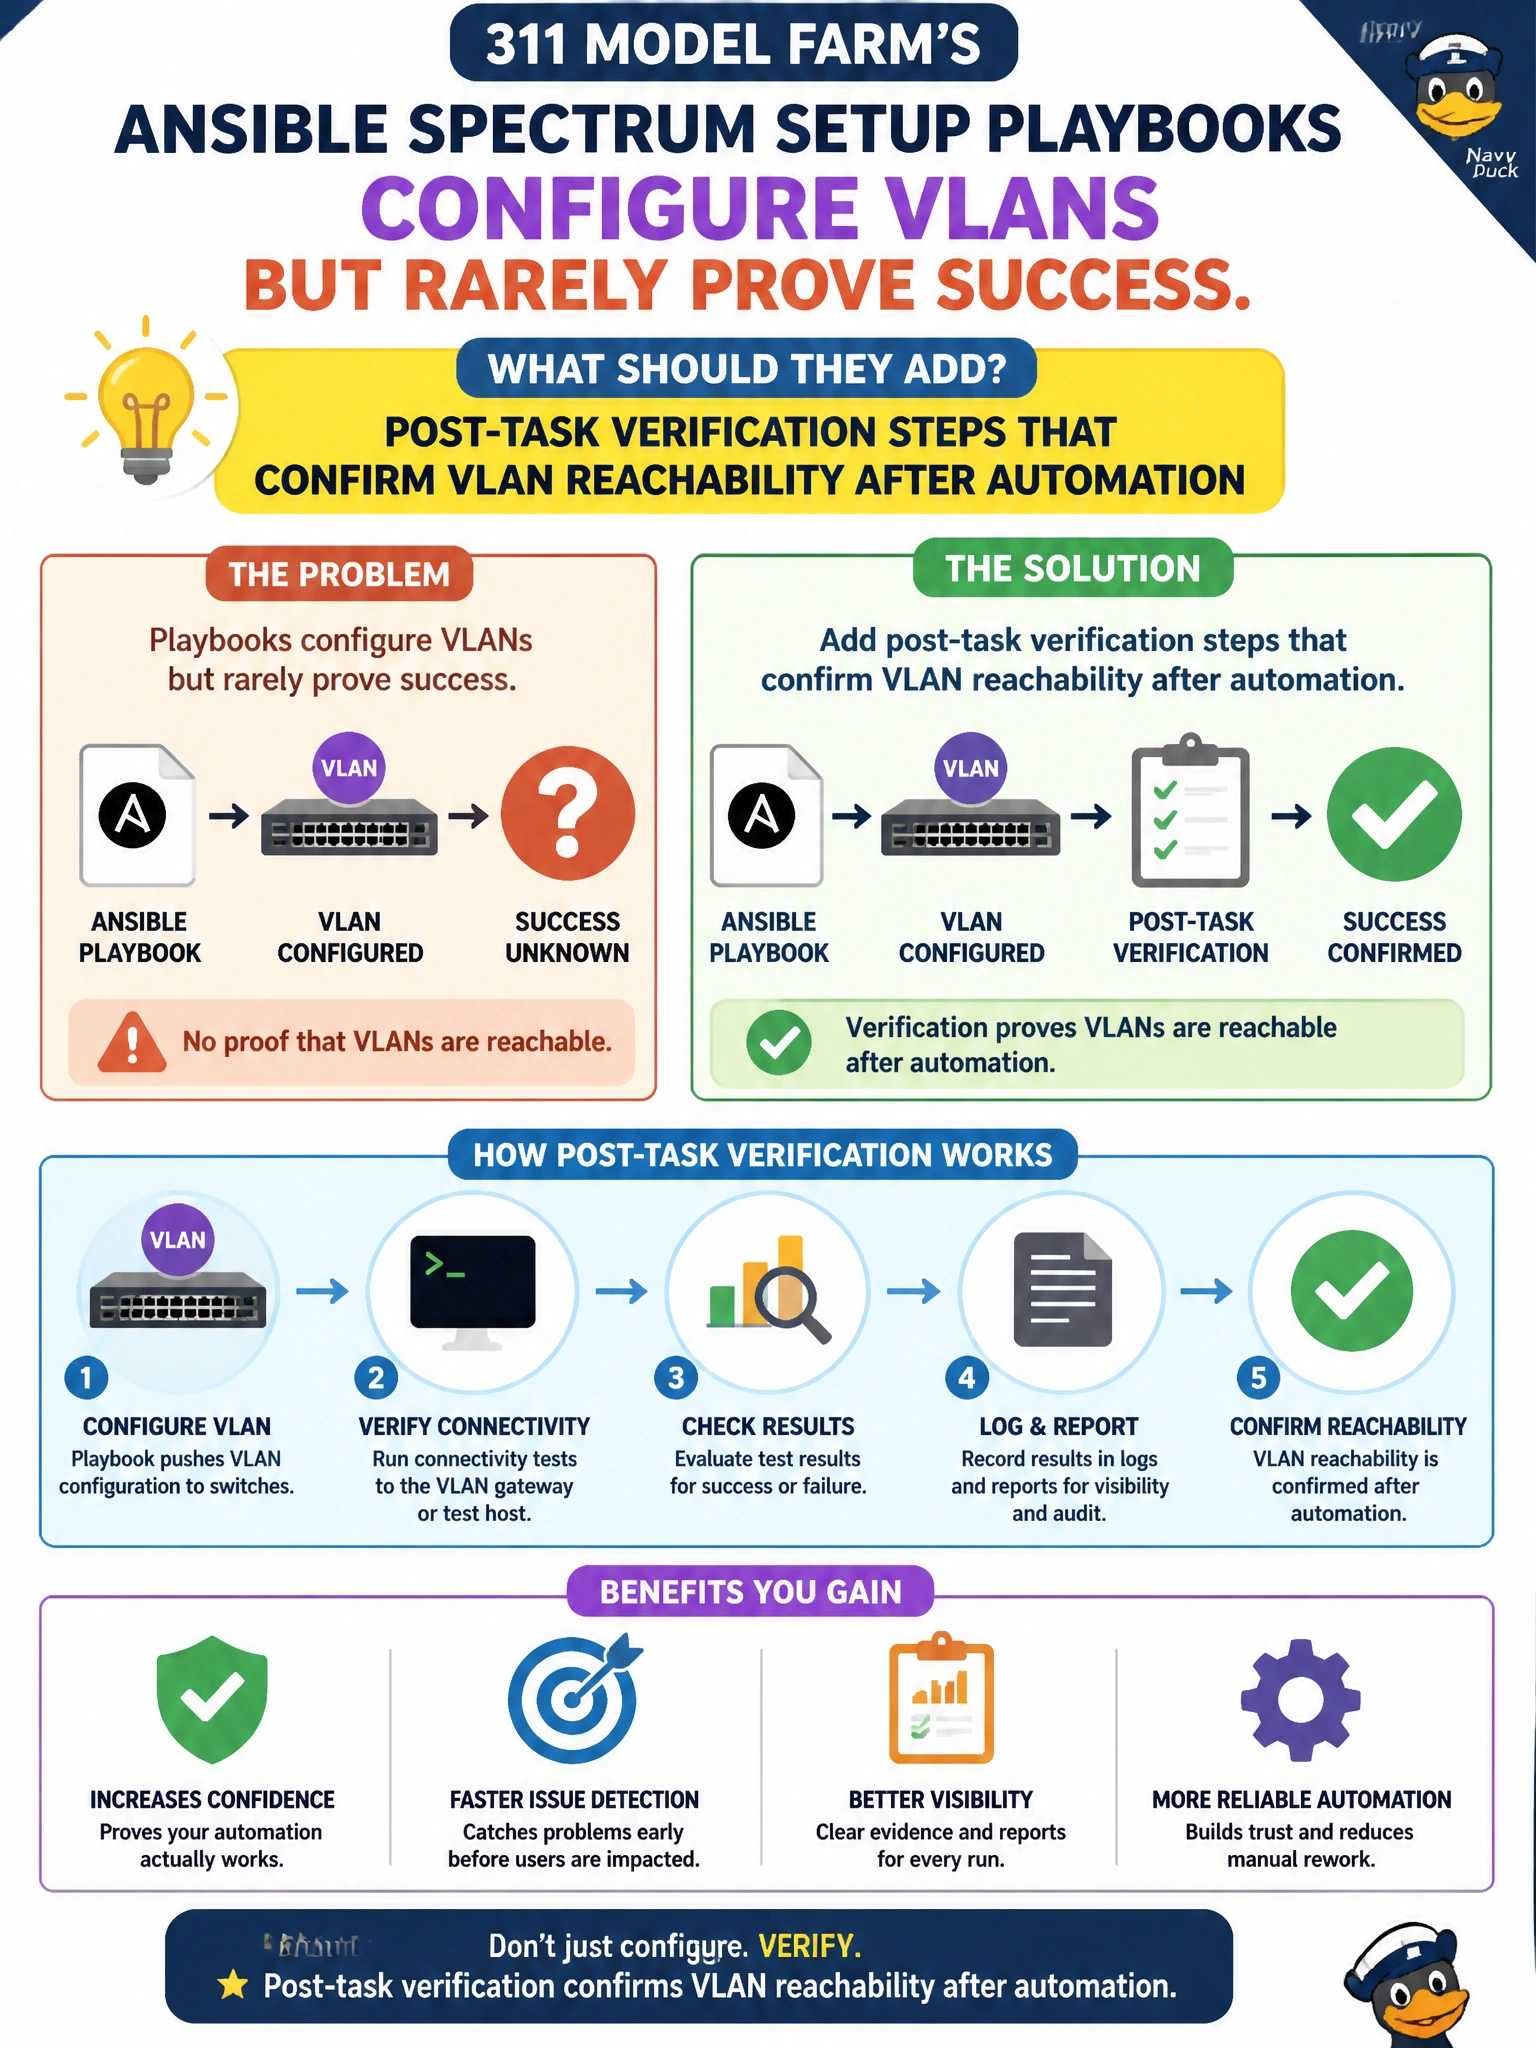
A 311 model farm’s Ansible Spectrum setup playbooks configure VLANs but rarely prove success. What should they add?
Select an answer to reveal the explanation.
Short Explanation
You can't just rerun idempotent playbooks on a schedule and hope the VLANs work. Add post-task verification to the 311 model farm’s Ansible playbooks so VLAN reachability is proven after Spectrum setup.
Full Explanation
A 311 model farm whose Ansible Spectrum setup playbooks configure VLANs but rarely prove success needs explicit verification. Post-task verification steps that confirm VLAN reachability after automation turn playbooks into closed-loop municipal procedures: create or update VLANs on Spectrum-X, then prove hosts or SVIs can reach as intended before declaring the change done for civic AI jobs. Idempotent playbook reruns that reapply desired VLAN state on schedule only converge configuration; they do not prove that the VLAN actually passes traffic on Spectrum Ethernet. Pre-change switch configuration backups paired with VLAN inventory capture preserve state before a change but do not prove post-change data-plane reachability, so they cannot replace verification after automation. Centralized forwarding of Ansible playbook output to a log archive for auditing preserves a record of what ran, but logs alone do not verify VLAN reachability or confirm the change worked. Exam caveat: verification should assert the specific VLAN/SVI/EVPN outcome the playbook intended; overly generic pings can pass while the wrong VLAN remains misconfigured. Operational check: add Ansible post-tasks or handlers that ping or otherwise test VLAN reachability for the 311 model farm, fail the play on verification failure, and alert operators instead of reporting false success. Log verification results with the 311 change ID so scheduled idempotent reruns without reachability proof cannot close the ticket.