
County health must pull NGC containers under a municipal organization account. What should operators configure before the first pull?
Select an answer to reveal the explanation.
Short Explanation
Log NGC CLI in with the county org account before the first pull—anonymous hope is not an enterprise plan. Keep keys out of the public wiki.
Full Explanation
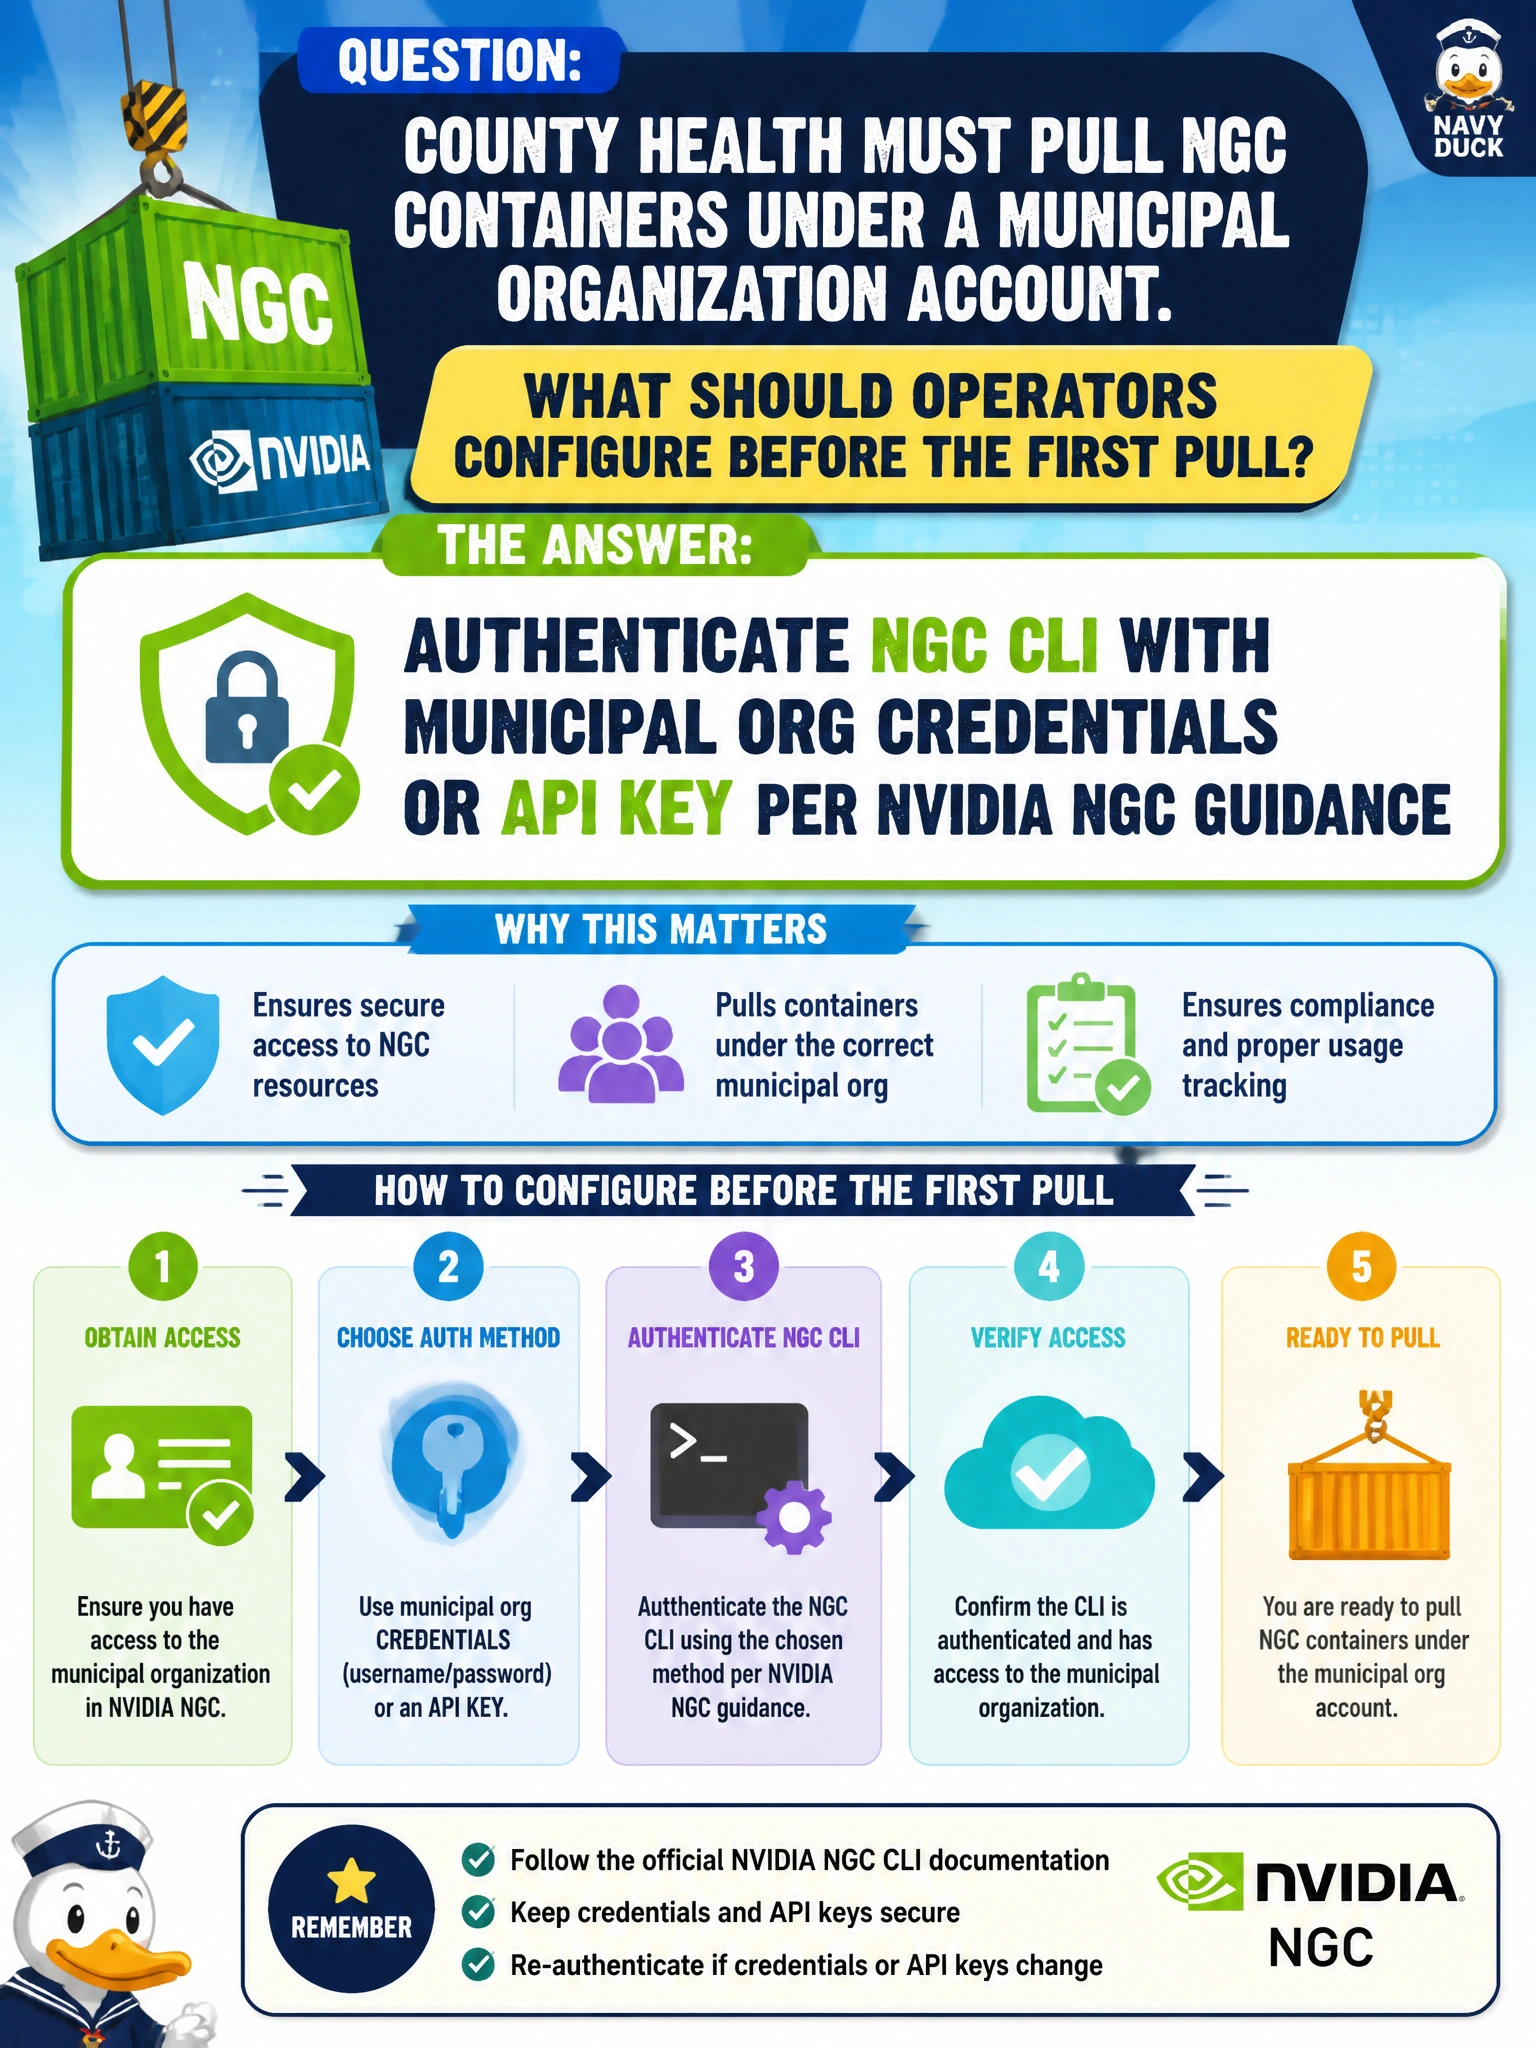
County health pulling NGC containers under a municipal organization account must authenticate NGC CLI with municipal org credentials or an API key per NVIDIA NGC guidance before the first pull. Enterprise and organization-scoped assets are gated; authentication is the onboarding step that binds pulls to the city’s sanctioned NGC tenancy and entitlements.
Disabling TLS for all NGC transfers fails by concept because clearing encryption to “speed downloads” violates security baselines and does not replace authentication—many enterprise assets still require login even on TLS paths. Sharing a single personal API key in a public wiki fails because personal keys are not a municipal org credential strategy, and publishing secrets destroys accountability and invites abuse. Skipping authentication because “NGC is always anonymous for enterprise images” fails because anonymous access is insufficient for many sanctioned enterprise/org assets the county intends to use.
Exam caveat: NCP-AII expects NGC CLI authentication as part of using NGC for containers/models. Distractors often attack security hygiene (TLS off, shared secrets) or claim anonymous enterprise access.
Operational check: on the approved health login host, run NGC CLI login with the municipal org API key/credentials, confirm identity/org context, pull a known entitled verification or inference image, and store the key in an approved secret store—not a wiki.