
A municipal case-management agent calls tools that open resident case files. What security and audit design is required?
Select an answer to reveal the explanation.
Short Explanation
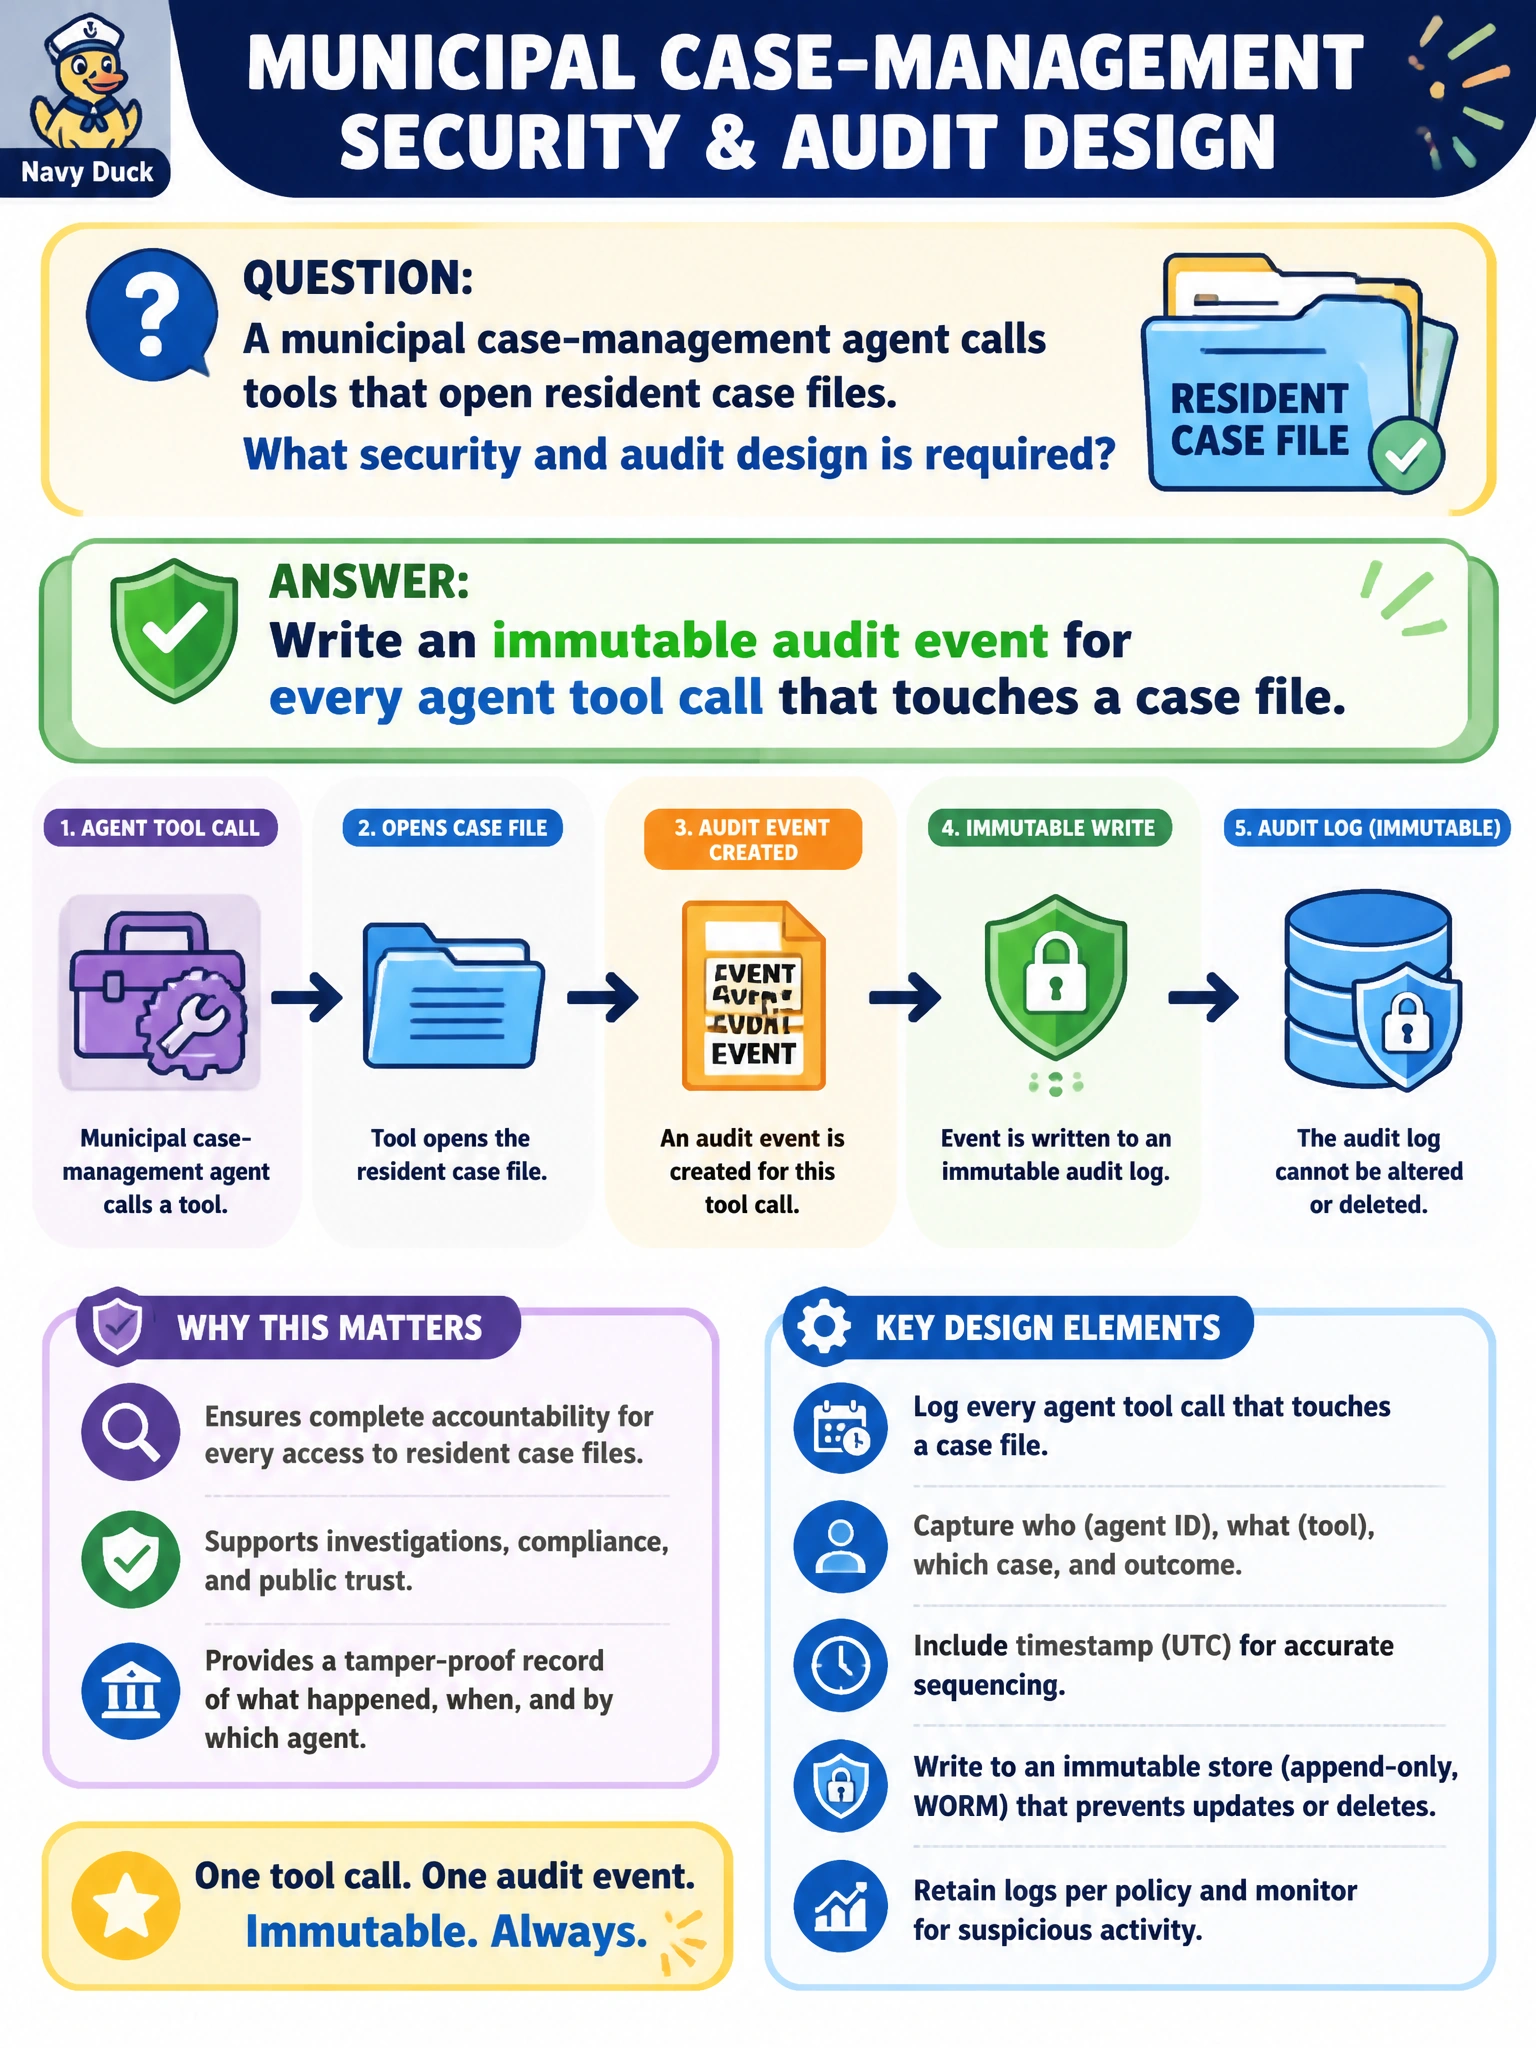
If the agent opens a case file, that touch needs a paper trail. Immutable audit events on every such tool call keep municipal security and accountability honest.
Full Explanation
When a municipal case-management agent invokes tools that open resident case files, security and accountability require an immutable audit event for every such tool call. Each open, read, or update against a case file should produce a non-repudiable record of actor (agent identity/service principal), tool name, case identifier, timestamp, and outcome. Immutable audit trails support investigations, least-privilege reviews, and compliance with municipal records and privacy expectations whenever automated agents touch sensitive resident case data.
Allowing silent tool access to case files with no recorded events fails by concept because invisible access cannot be reviewed, attributed, or disputed after a privacy incident. Logging only successful answers and never tool invocations fails because the harmful or sensitive action is often the tool call itself—answer-only logs miss failed attempts, over-broad fetches, and intermediate case opens. Storing audit trails in editable chat notes clerks can rewrite later fails because mutable notes are not an audit control; they can be altered after the fact and do not meet immutability requirements for security evidence.
Exam caveat: NCP-AAI security/audit questions emphasize logging the privileged action (tool calls that touch case files), not merely the final natural-language reply. Prefer immutable, tool-level audit events over silence, answer-only logs, or editable notes.
Operational check: enable append-only audit logging on every case-file tool; sample a live agent session and confirm each case open appears with agent identity and case ID; verify clerks cannot edit or delete those events; run an access review that reconciles tool audits to authorized workflows.