
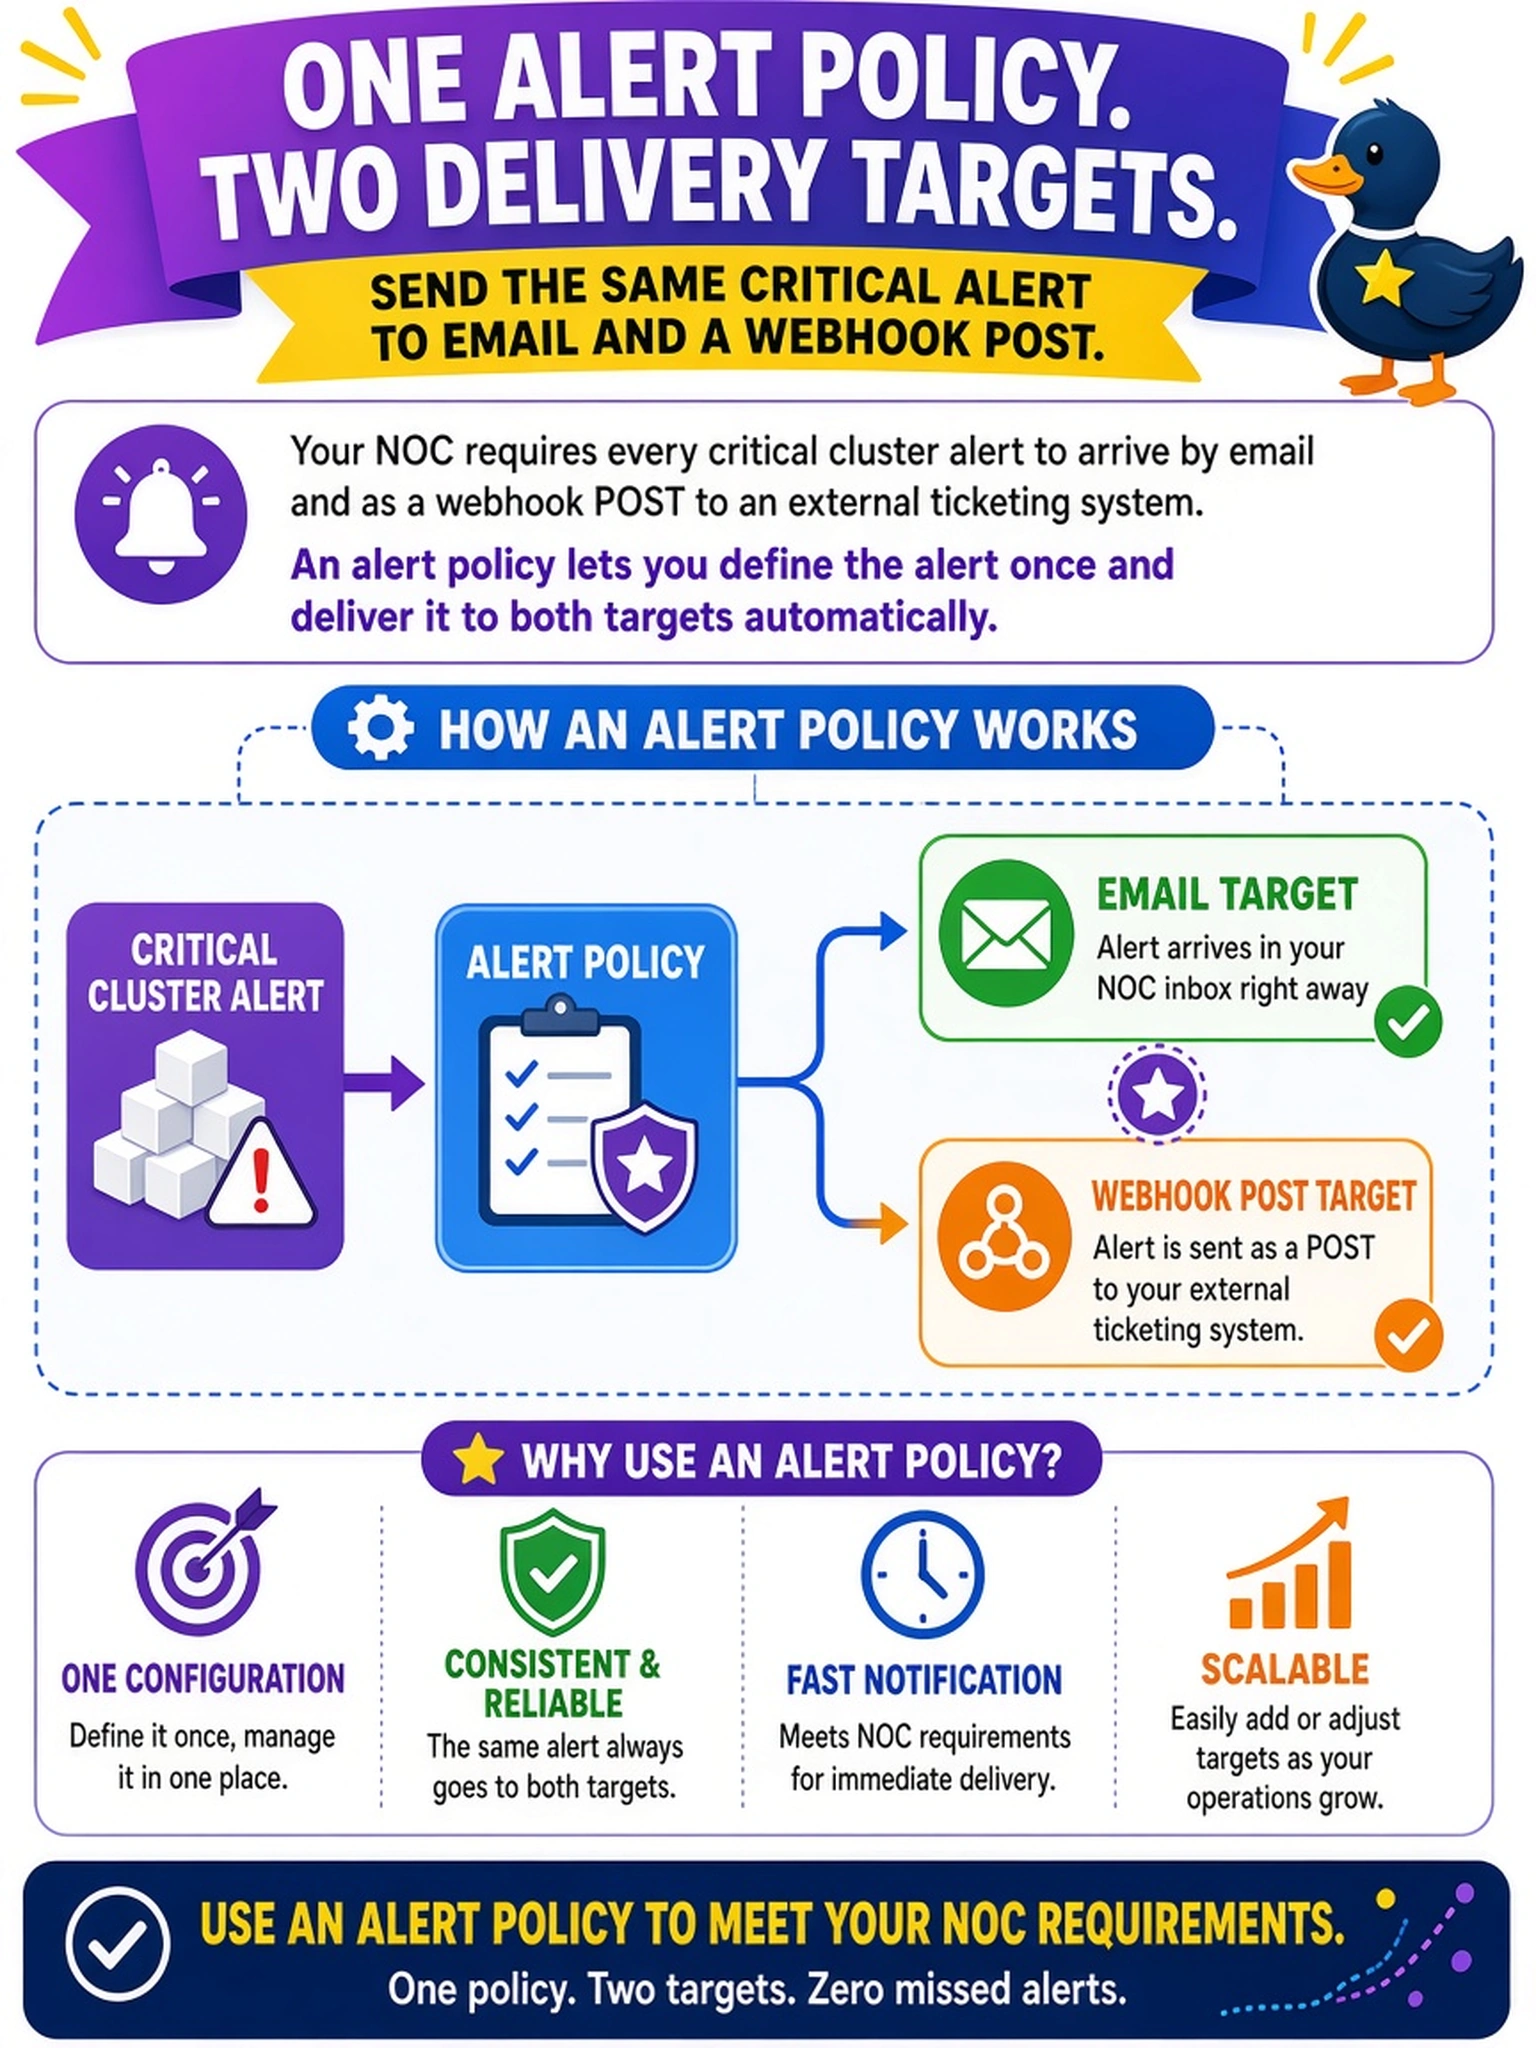
Your NOC requires every critical cluster alert from Prism to arrive by email and as a webhook POST to an external ticketing system. You need one configuration that can send the same alert to both targets. Which method should you use?
Select an answer to reveal the explanation.
Short Explanation
Think of an alert policy like a broadcast rule: one trigger, multiple loudspeakers. You attach email and webhook to the same policy instead of trying to force SNMP or syslog to do a webhook's job. That keeps the alert path simple and verifiable.
Full Explanation
An alert policy is the configuration object that binds an alert condition to one or more notification methods. When the policy is triggered, the alert engine evaluates the condition once and dispatches the resulting notification through every method attached to the policy, so email and webhook can both receive the same critical alert without duplicate rules. SMTP relay configuration addresses only the transport for outbound mail; it does not create an alert condition or a webhook delivery path. SNMP trap forwarding sends trap-formatted events to a SNMP manager or collector, which is not an email message and is not parsed as an HTTP webhook payload. Syslog forwarding is useful for log aggregation, but it forwards log records rather than executing an alert-notification policy with multiple notification channels. Exam caveat: the exact menu labels may vary across Prism Element and Prism Central, but the concept to recognize is a policy-based alert definition with multiple notification methods. Operational check: create a test alert policy, trigger a test alert, then confirm both the mailbox and the webhook endpoint received matching alert details.