
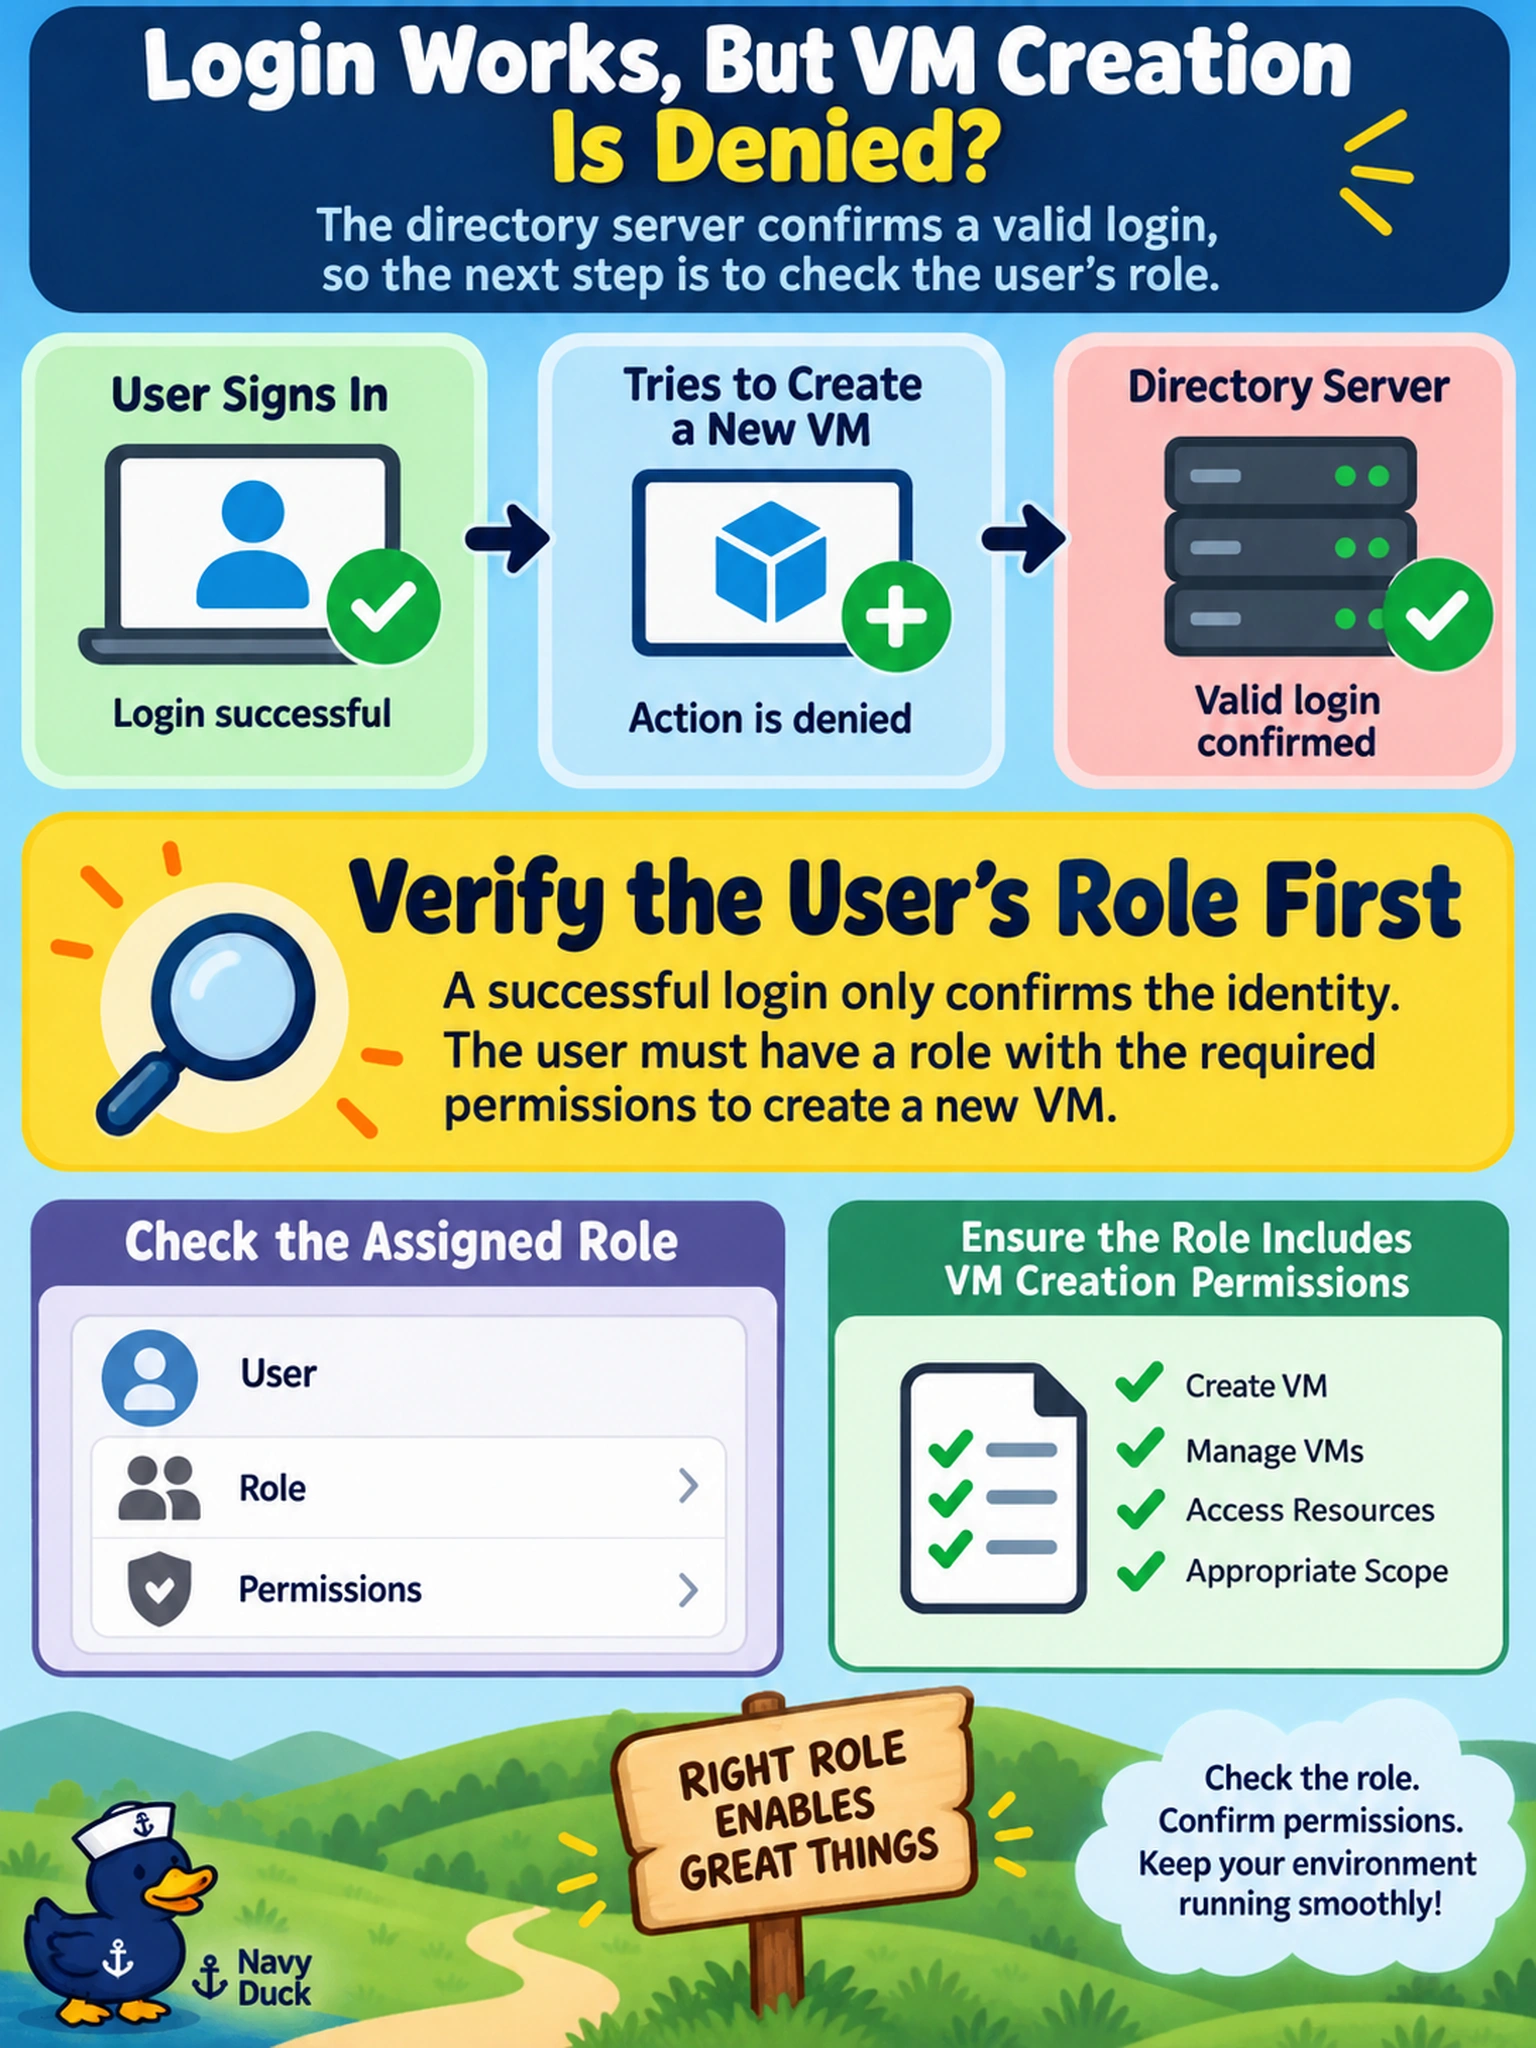
A user signs in to Prism Central successfully, but when they try to create a new VM, the action is denied. The directory server reports a valid login. What should the administrator verify first?
Select an answer to reveal the explanation.
Short Explanation
Think of it like this: a badge can get you through the front door, but it doesn't let you into every room. If the user signs in, authentication worked; the denied action points to authorization. Check your Prism Central role assignment, not another login check.
Full Explanation
In Nutanix administration, authentication proves an identity, while authorization determines what that identity may do. Prism Central can authenticate a user through local accounts or a configured directory, then enforce access through RBAC roles and permissions. A successful login with a denied operation therefore points to insufficient permissions, scope, or role assignment for the requested action. The engineer should inspect the role bound to the user or group, the role's permissions, and any scope constraints before changing credentials or network settings. Authentication failures would typically prevent login or produce directory bind errors, not allow sign-in and then block an action. Password complexity and expiration affect credential acceptance, not post-login entitlements. Multi-factor authentication adds a second verification step during login; if the user has already authenticated, MFA status is not the reason the operation is denied. Directory connectivity problems also prevent or interrupt sign-in rather than selectively deny a VM creation. Exam caveat: do not confuse successful directory authentication with sufficient RBAC authorization, especially when groups or role scopes are involved. Operational check: review the user's effective role and permission set in Prism Central, then test the denied action after granting the minimum required permission.